Use the Upgrade page to upgrade the Endpoint Security (HX) appliance. To open the Upgrade page, click the About tab and then click Upgrade. (If the About tab is not visible, select Appliance Settings from the Admin menu.)
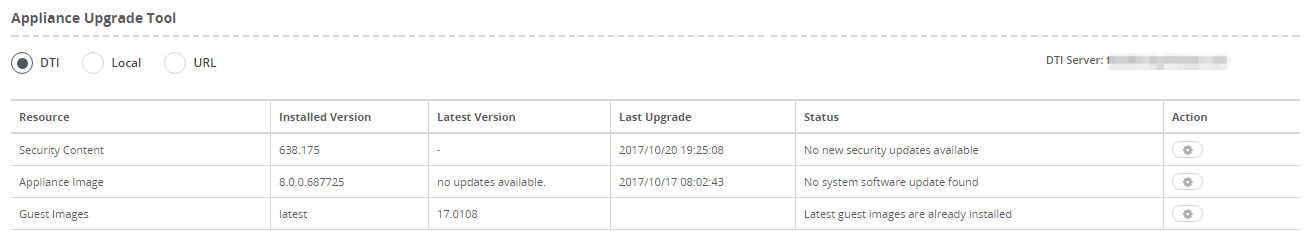
The following is an example of the Upgrade page for a standalone Endpoint Security (HX) appliance.
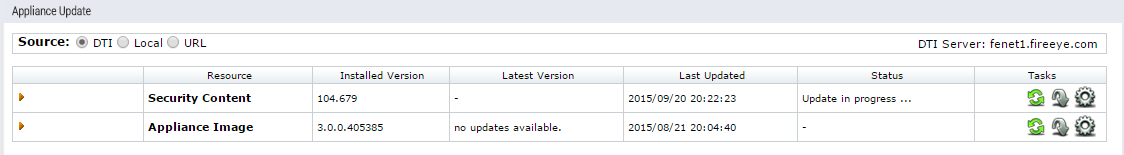
The following is an example of the Update page for a standalone Endpoint Security (HX) server
The following is an example of the Upgrade page for an appliance that is managed by the Central Management System appliance.
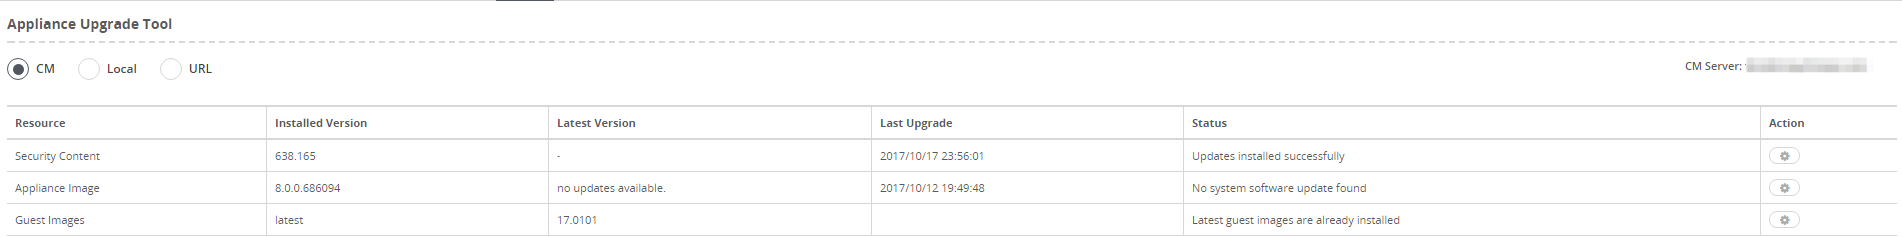
The timestamp shown in the Last Updated column is the timestamp when the Endpoint Security (HX) image was last built. It does not indicate when the server image on the hardware was last updated.
The following is an example of the Update page for an Endpoint Security (HX) server that is managed by the Central Management System appliance.
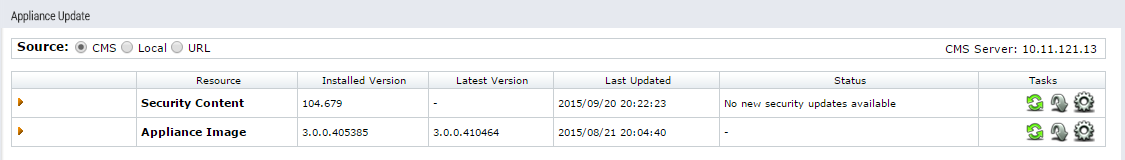
Task list for upgrades
Perform the following steps (detailed in the sections that follow) to upgrade the Endpoint Security (HX) appliance.
Note
If your appliance is offline and cannot download updates from the DTI network, perform Select an Update Source on the facing page and then refer to the Trellix DTI Offline Update Portal User Guide for additional instructions.
Export your agent certificates
Before upgrading the Endpoint Security or DMZ server, Trellix recommends that you export (back up) any existing Endpoint Security certificates (the PKI keys needed to communicate with the agent population.
This is a precautionary step. Ordinarily, software upgrades do not affect the PKI keys, but if a problem occurs during the upgrade that forces you to reinstall the software or reimage the server, the backup of the PKI keys is critical. Without these certificates, you will also need to reinstall all of your agents. However, if you can import the saved agent certificates, you will not need to reinstall the agents.
Go to CLI configuration mode:
hostname > enable hostname # configure terminal
Export the certificates to the file identified by
<fileURL>:hostname (config) # hx pki export file <fileURL> passphrase <passphrase>For example:
hostname (config) # hx pki export file scp://user@host/path/to/file passphrase abc123
Select an upgrade source
The upgrade source is the location from which the software updates will be downloaded.
Online options
DTI—The software is downloaded from the Dynamic Threat Intelligence (DTI) server or a Content Delivery Network (CDN) server. The server address is displayed at the top right of the page. See Changing the active setting for a DTI service for details about these options.
CM—This option is displayed instead of DTI if the appliance is being managed by the Central Management System appliance. The default source server is the Central Management System appliance, but it can be overridden by the three DTI options specified above.
Offline options
The following options can be used if your appliance cannot download updates from a DTI source server. For details and upgrade instructions, see the Trellix DTI Offline Update Portal User Guide.
Local—Upload a local file that was obtained from the Trellix DTI Update Portal for offline appliances. Click Local to specify a path to the locally stored update software, and then click Save.
URL—Upload a local file that was obtained from Trellix via the DTI Update Portal for offline appliances and hosted on a local site identified by a URL. Click URL to specify a URL to the update software, and then click Save.
If neither offline option is feasible, contact Trellix Technical Support.
Check for available update software
Click the action icon ( ) in the Action column, and then click Check for a resource row to determine if update software is available.
The status is displayed in the expanded Status area.
Note
If the Check option does not appear in the Action column, then the software is already available for download or an update has recently taken place. The Check option also does not appear during software downloads.
Download the software
If a software update is available for a software image or security content update, the Download icon in the Tasks column is enabled (green).
Click the action icon () in the Action column, and then click Download to begin the software download.
The download status is displayed in the expanded Status area.
Install the software update
Installation status is displayed in the expanded Status area. After you download a software update, click the action icon () in the Action column, and then click Install to install it.
Installation status is displayed in the expanded Status area. If prompted, read the End User License Agreement (EULA), and then accept it if you agree to its terms. If you do not accept it, the appliance will not function.
Note
If an upgrade process is interrupted or fails, the appliance software automatically falls back to the currently installed image.
Reboot or refresh the appliance
When installation of security content is complete, click the action icon () in the Action column, and then click Refresh. When installation of the software image is complete, click the action icon () in the Action column, and then click Reboot to complete the update process.
Note
You must access the appliance through the serial port if you want to monitor appliance boot activities. You can enter CLI commands through direct keyboard and monitor connection only before the boot loader begins loading the kernel, for example, to post output, and after the boot is completed.
Validate the software updates
After software updates are installed, verify the installations:
Click the About tab. The current software image and security content version information is displayed on the Summary page. If the About tab is not visible, select Appliance Settings from the Admin menu.)
Click the Settings tab, and then click Appliance Licenses on the sidebar to verify and view installed licenses. (If the Settings tabs are not visible, select Appliance Settings from the Admin menu, or click the Appliance Settings tab at the top of the page.) Valid and active licenses display the attribute “True.” If the licenses are not valid and active, the updates are not functional.
Import your agent certificates
If the Endpoint Security (HX) server upgrade went smoothly, you can skip this step.
If there were any problems upgrading your server that required you to reimage it or to fully reinstall the Endpoint Security (HX) software, import the Endpoint Security certificates you exported earlier so you do not have to reinstall all of your agents.
Caution
Importing certificates automatically detaches any DMZ server from the Endpoint Security (HX) server. You need to reattach them after the certificates are imported. See the Endpoint Security (HX) Server Deployment Guide.
Go to CLI configuration mode:
hostname > enable hostname # configure terminal
Import the certificates from the file containing your exported certificates, identified by
<fileURL>:hostname (config) # hx pki import file <fileURL> passphrase <passphrase>For example:
hostname (config) # hx pki import file scp://user@host/path/to/file passphrase abc123
(Optional) reenable Endpoint Security (HX) server relay mode
If the Endpoint Security (HX) server is in relay mode when it is upgraded, relay mode must be reenabled after the upgrade completes.
Log in to the Endpoint Security (HX) server as an administrator.
Enable CLI configuration mode on the Endpoint Security (HX) server.
hostname > enable hostname # configure terminal
Reenable relay mode.
hostname (config) hx rproxy relay <hostname-or-IPaddress>where
<hostname-or-IPaddress>is the host name or IP address of the Endpoint Security (HX) appliance.Save your settings.
hostname (config) # write memory