IPv6 Network is not supported for Quarantine. Also, only one IPv4 Network item per Rule Object is allowed for quarantine zone.
The steps to add IPv4 Network and IPv6 Network rule objects are identical. Follow these steps to add IPv4 Network or IPv6 Network rule objects:
Upon specifying the options in the Properties tab and selecting IPv4 Network or IPv6 Network from the rule object Type drop-down, click Next.
Create an IPv4 Network or IPv6 Network rule object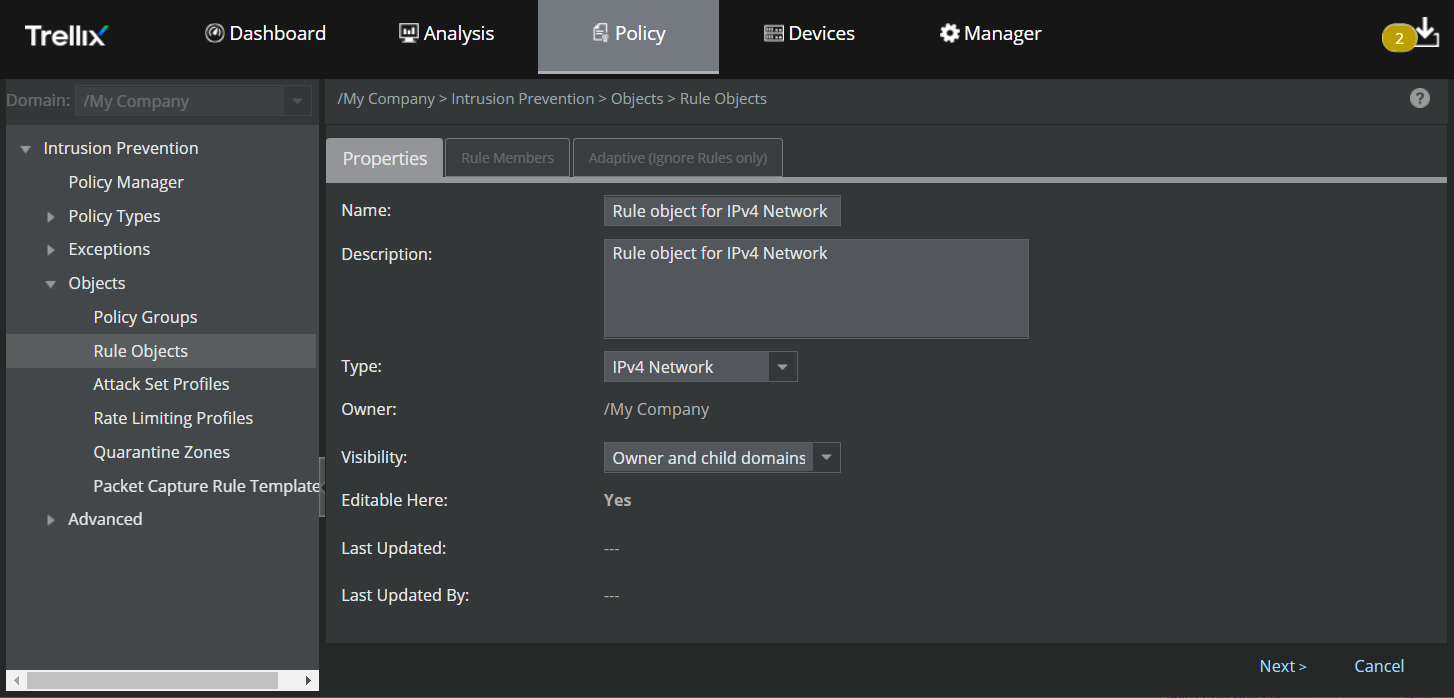
The Rule Members tab is displayed.
Add Rule Members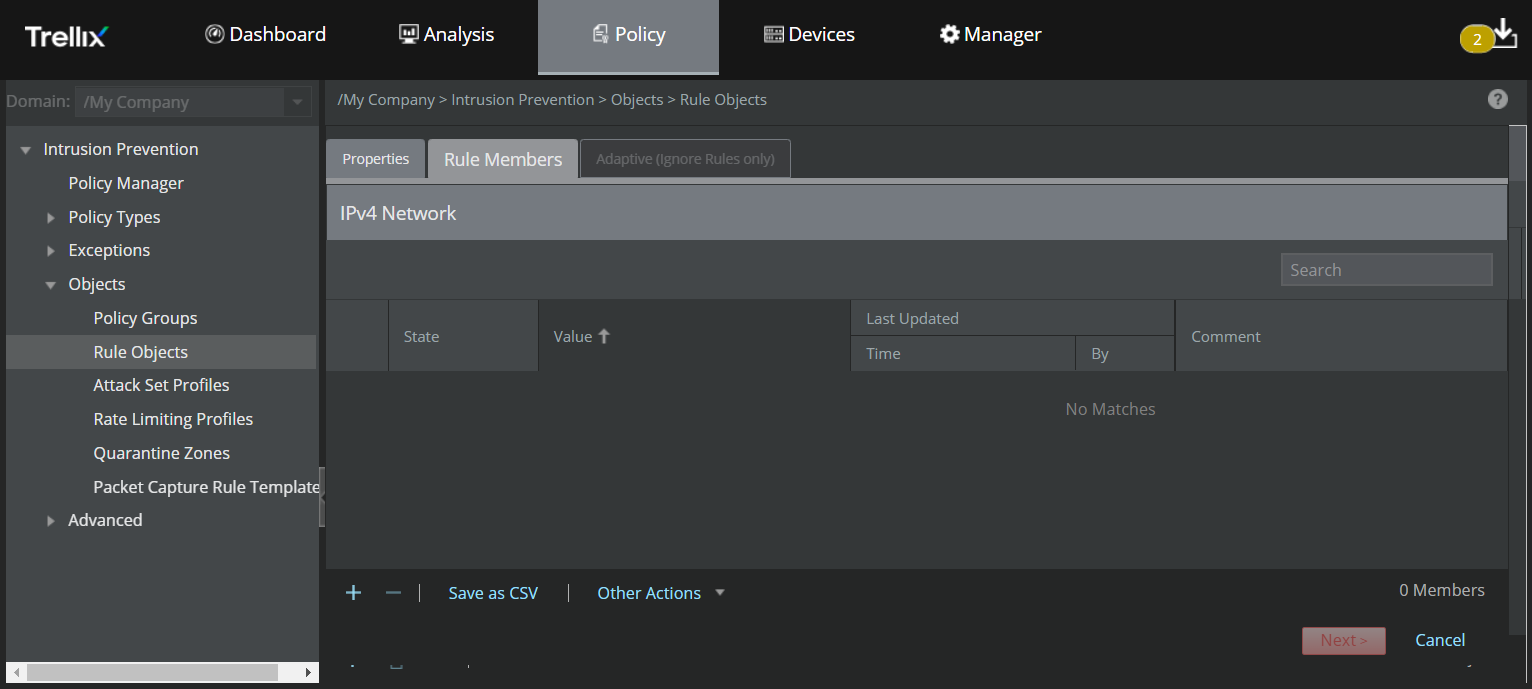
Following are the details of the columns displayed in the Rule Members tab:
Column details in the Rule Members tab - IP Network rule objectColumn
Description
State
Specifies whether a rule member (in this case, IPv4 or IPv6 CIDR block based on the rule object selected) is Enabled or Disabled
Value
Displays the IPv4 or IPv6 CIDR blocks
Last Updated
Time — Specifies the time when the rule member was last modified
By — Displays the user who modified the rule member
Comment
Displays any additional comment specified for the rule member
You can rearrange/resize the columns to view the details according to your preference.
The following table explains the options in the Rule Members tab.
Option
Definition

Click this icon to add a valid IPv4 or IPv6 CIDR block. For example, enter 172.16.200.0/24 for IPv4 Network, or 3003:0AB8::/48 for IPv6.

Click this icon to delete single or multiple IPv4 or IPv6 CIDR blocks
Save as CSV
Click this icon to remove a rule object from the list
Other Actions
Import — Allows you to import a file containing a list of IPv4 or IPv6 CIDRs
Export All — Allows you to export all the CIDRs from the Manager to the local system
There are two ways to add the IP CIDR blocks — add individual IP CIDR block using the
icon or import a list of IP CIDR blocks from a CSV file using the Other Actions → Import option.To add an individual IPv4 or IPv6 CIDR block:
Click the
icon.A Details window is displayed on the right-hand side of the Rule Members tab.
For details of the options displayed in the window, refer the table Column details in the Rule Members tab - IP Network rule object.
Select the State, enter the IPv4 or IPv6 CIDR block in the Value field, enter a Comment if required and click Add.
Note
You can enter up to 140000 IPv4 or 140000 IPv6 CIDRs in a single rule object.
The above rule member count is applicable only for Firewall policy. For QoS policy, Ignore Rules, SSL Decryption Exclusions, Quarantine Zones and NTBA Communication Rules, the maximum rule member count applicable for each rule object type is 10. For Quarantine Zones, only one rule member should be assigned per rule object. So, you need to add rule members to a rule object accordingly.
If the Manager is on or before version 10.1.7.55 and the Sensor is on or before 10.1.5.153, you can add a maximum of 10 IPv4/IPv6 CIDRs in any rule object.
Add individual IP CIDR block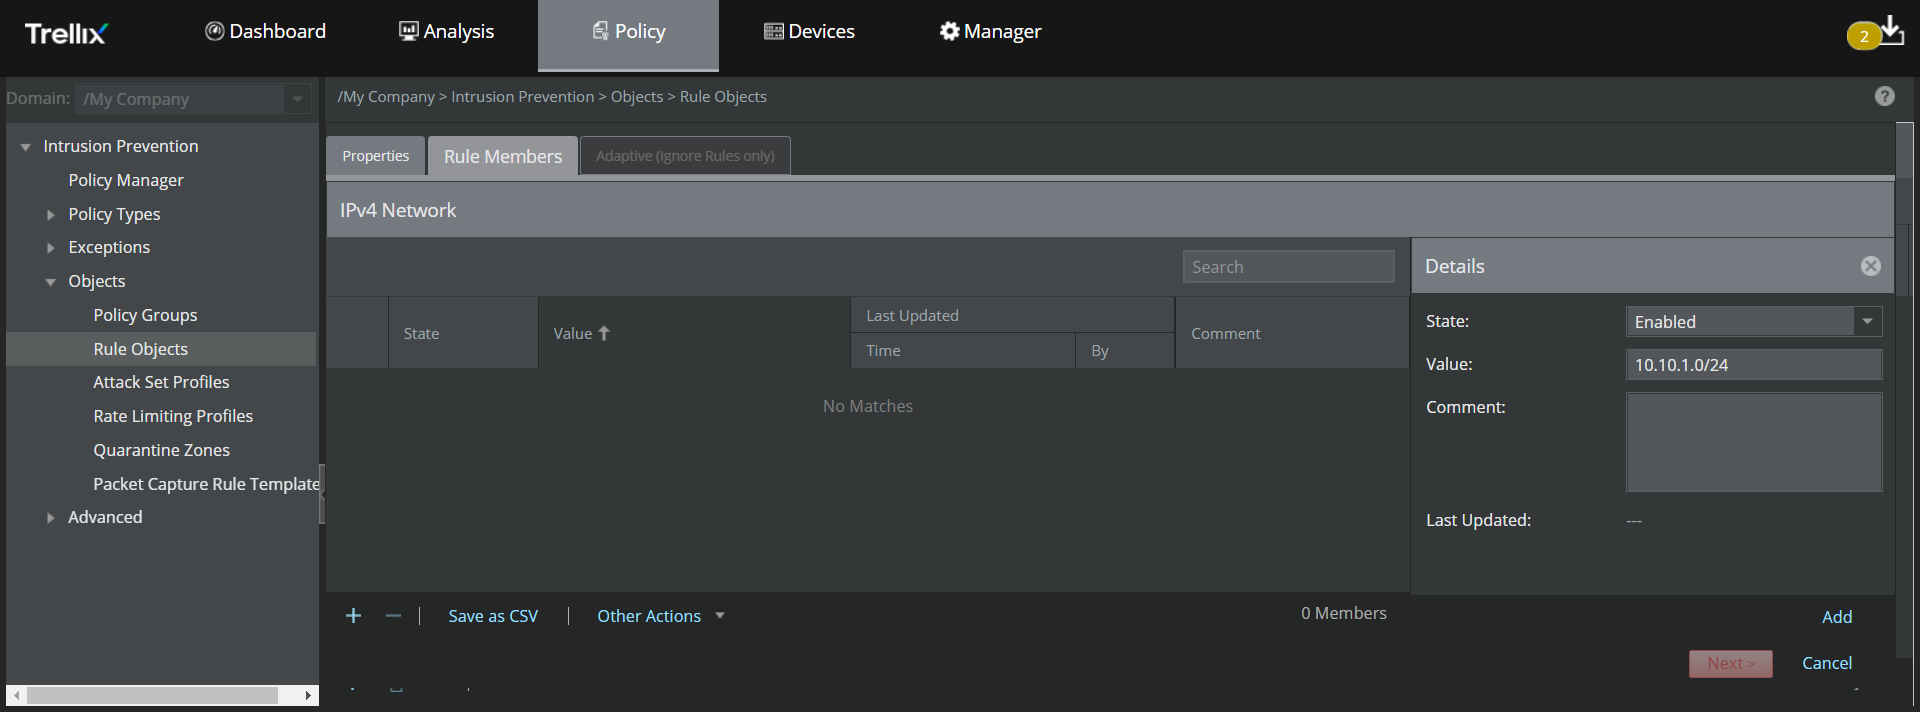
Upon adding all the required IP CIDR blocks, click Next.
Adaptive (Ignore Rules only) tab is displayed. This is an optional tab.
The following table explains the options in the Adaptive (Ignore Rules only) tab.
Option
Definition
Customization
Select Disabled to disable customization or select Use custom values per resource to customize values
Resource to Customize
Select the resource to customize from the drop-down list
Note
This option is displayed only if you select the customization option as Use custom values per resource
Add
Click this button to add a CIDR block to the Customizations list
Search
Type the search criteria to search for a resource

Click this icon to remove a CIDR block from the list
Based on the above options, make any configuration changes if required, and click Save. The rule object will be created.
To import a list of CIDR blocks from a CSV file using the Import option:
Click Other Actions → Import.
Note
You cannot import the file while adding individual entries. In case you plan to import a file along with the individual entries, add the entries first, save the rule object and re-open the rule object to import the file. Make sure that total rule member count (sum of CSV file entries and individual entries) does not exceed 140000.
Note
If you are assigning the rule object to QoS policy, Ignore Rules, SSL Decryption Exclusions, and NTBA Communication Rules, make sure that total rule member count (sum of CSV file entries and individual entries) does not exceed 10.
Import IP CIDRs from a CSV file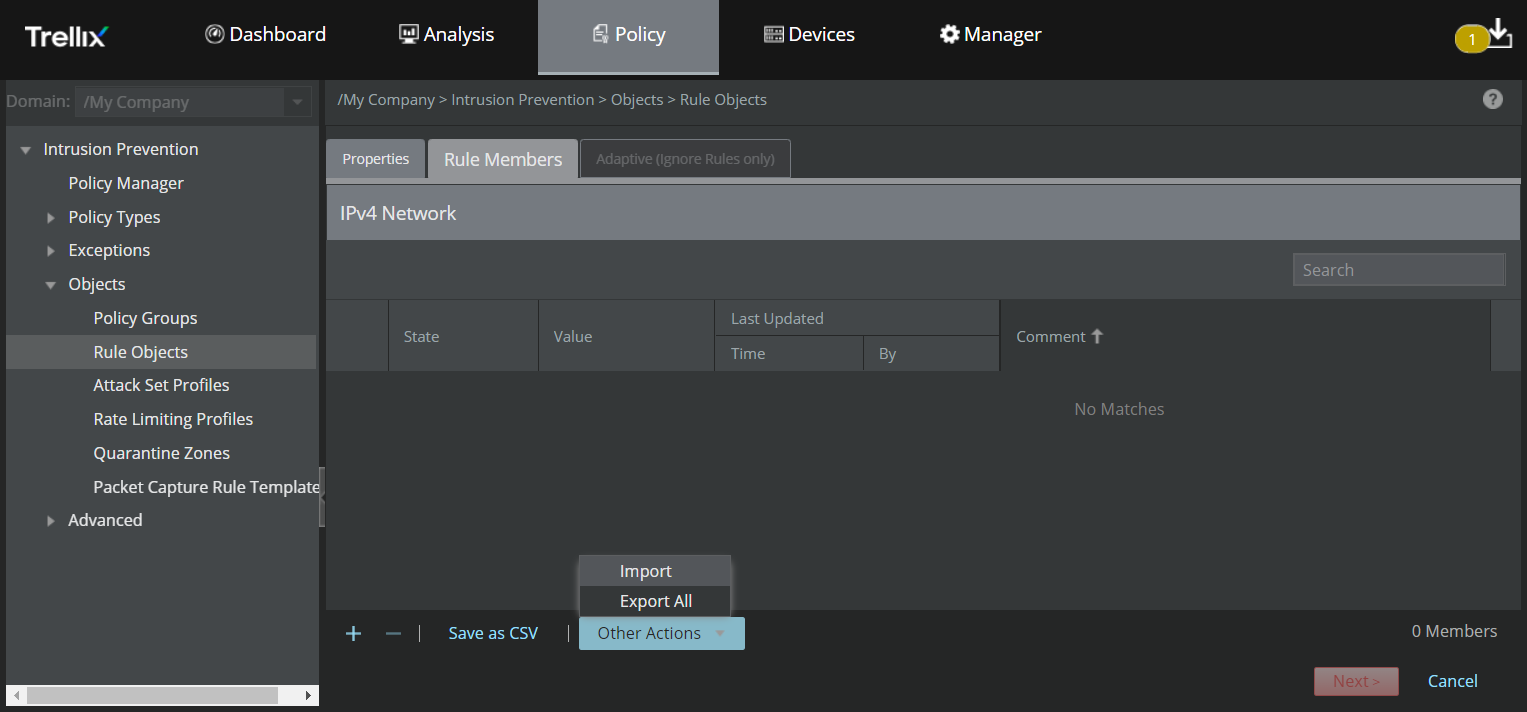
Import from CSV window appears. Use the Append option to add a new list of CIDR blocks or to append a list of CIDR block to an existing list. Use the Replace option to replace an existing list of CIDRs with a new list.
Note
If any duplicate entries exist while appending, the Manager replaces the existing entries with the entries being imported.
Click Browse to locate the CSV file that contains the list of IPv4 or IPv6 CIDRs that you plan to import.
Import IP CIDRs from a CSV file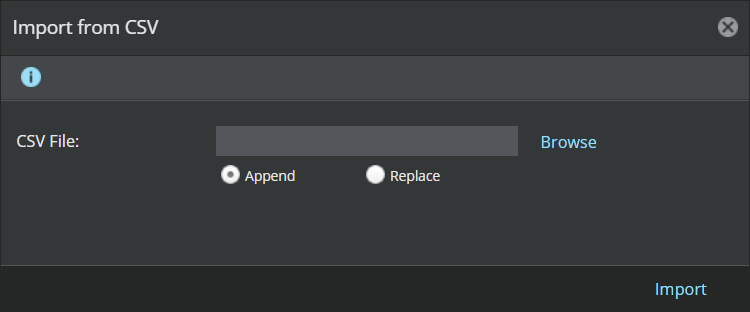
The file to be imported should be in the following CSV format: <IPv4 or IPv6 CIDR>,<Comment>
Example file format: 10.10.1.0/24,textual description.
The following is a sample for a CSV file with multiple IPv4 CIDRs:
CSV file format for IPv4 or IPv6 Networks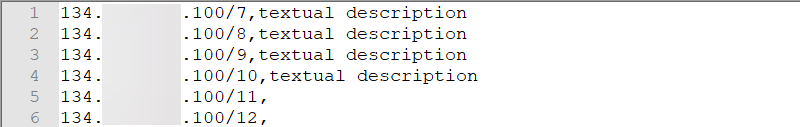
The following table describes the details of the IP CIDR blocks to be imported in the CSV file format.
Format
Description
<IPv4 or IPv6 CIDR>
Specifies the IPv4 or IPv6 CIDR to be imported
<Comment>
Specifies the description of the IP address to be imported. If you do not want to specify a comment for an entry, add comma (
,) next to the entry and leave it.Click Import upon selecting the CSV file.
All the entries in the CSV file will be imported and the rule object will be saved automatically.
Note
The State of the rule members will be set to Enabled by default. You may change the state of a rule member by accessing the rule object.
Rule object for IPv4/IPv6 network successfully created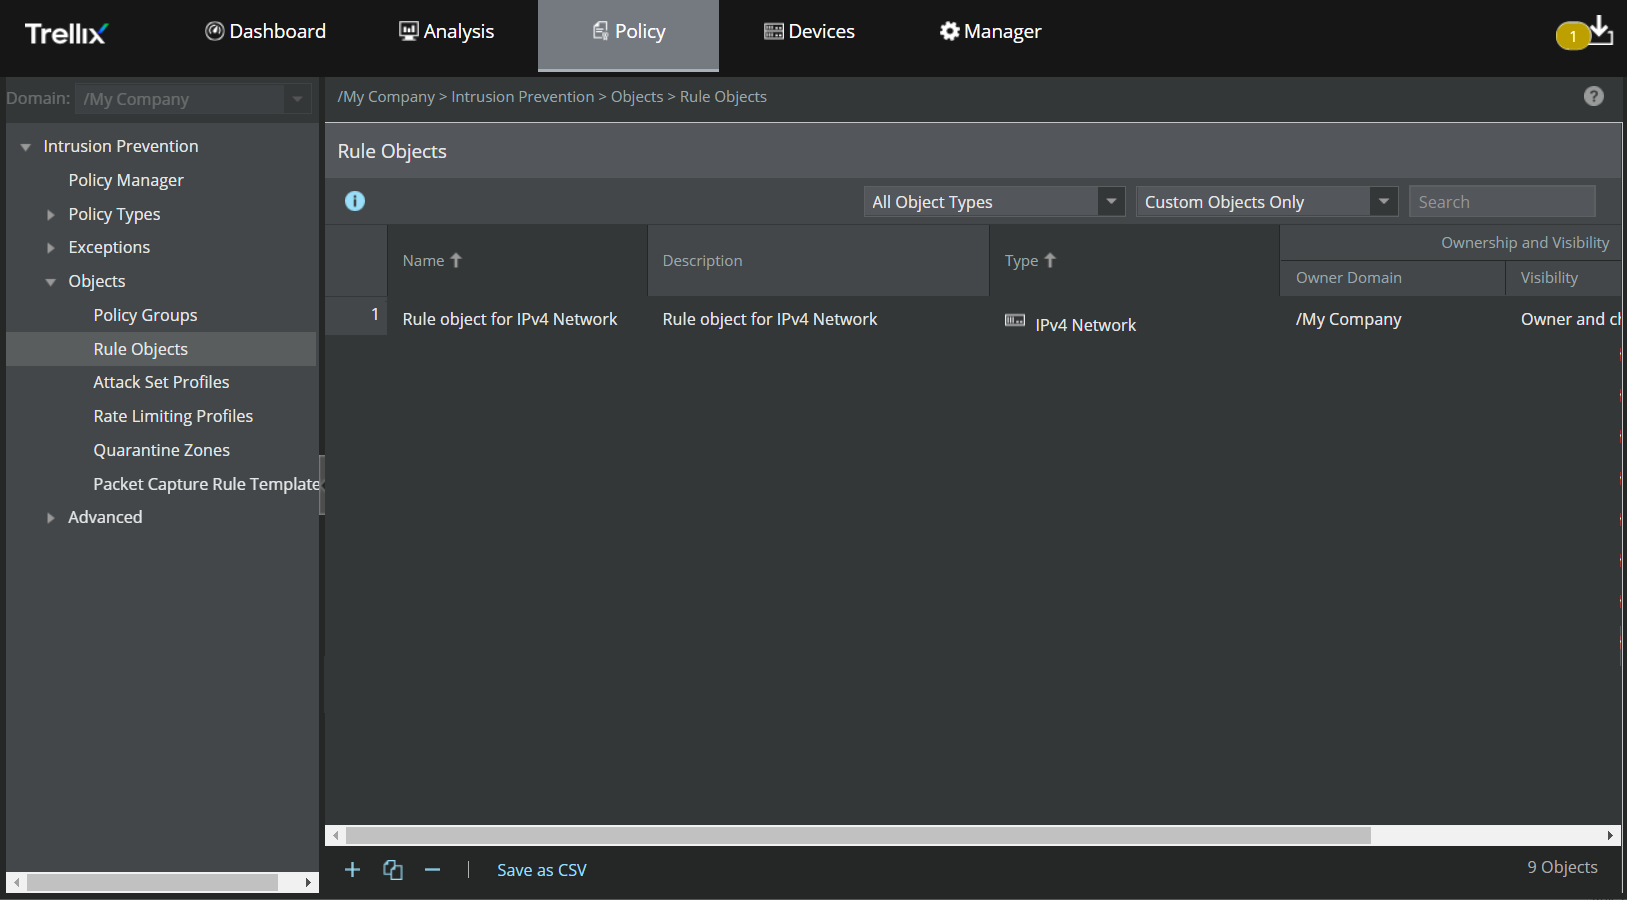
Note
If there are any invalid entries in the CSV file, the Manager displays an Informational dialog-box stating about the invalid entries. All such entries will also be collected to a CSV file. This file will either download onto the local machine automatically or require you to choose a download location, based on your web browser's download settings. Upon downloading the file, click OK to close the Informational dialog-box. In this case, the rule object will be created upon closing the dialog-box.
Information dialog-box for invalid entries