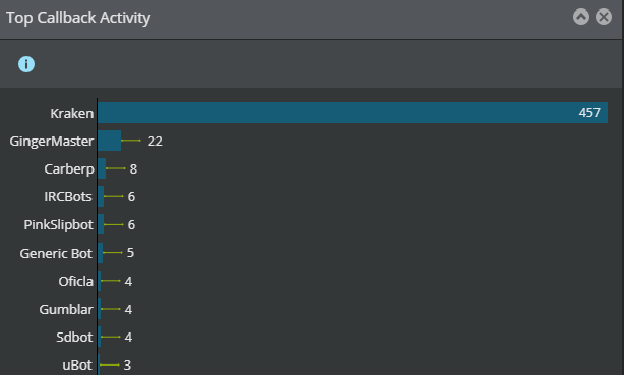
You can leverage the analysis technique provided by the Trellix IPS to perform an in-depth analysis of the callback activity in your network. The Manager provides you with a complete view of the bot events and threats on your network for further analysis and actions, thus providing a comprehensive view of the threat landscape in your network. You can view the Top Callback Activity dashboard. This dashboard is populated when bot activity is detected in your network. The dashboards display the callback activity name and the number of bots (zombies) in your network for the corresponding callback activity. The Dashboard page security monitors are displayed as bar charts.
If you want to drill down further on a specific bot activity, click the bar, and you'll be redirected to the Analysis → Callback Activity page, which displays additional details on that activity. This page provides you with the flexibility of filtering and sorting the information displayed based on your choices. In addition to these filtering/sorting options, you can also view the alerts that match the filter criteria by opening the Attack Log page. You can view the callback activities specific to admin domains by selecting the required admin domain from the Domain drop-down list. Summarized data for callback activities, which includes data from the child domains, also can be viewed. If you have integrated the Manager with products like ePolicy Orchestrator - On-premises, Intelligent Sandbox, or Trellix Virtual Execution, you can view the host name, operating system, open ports, known vulnerabilities.
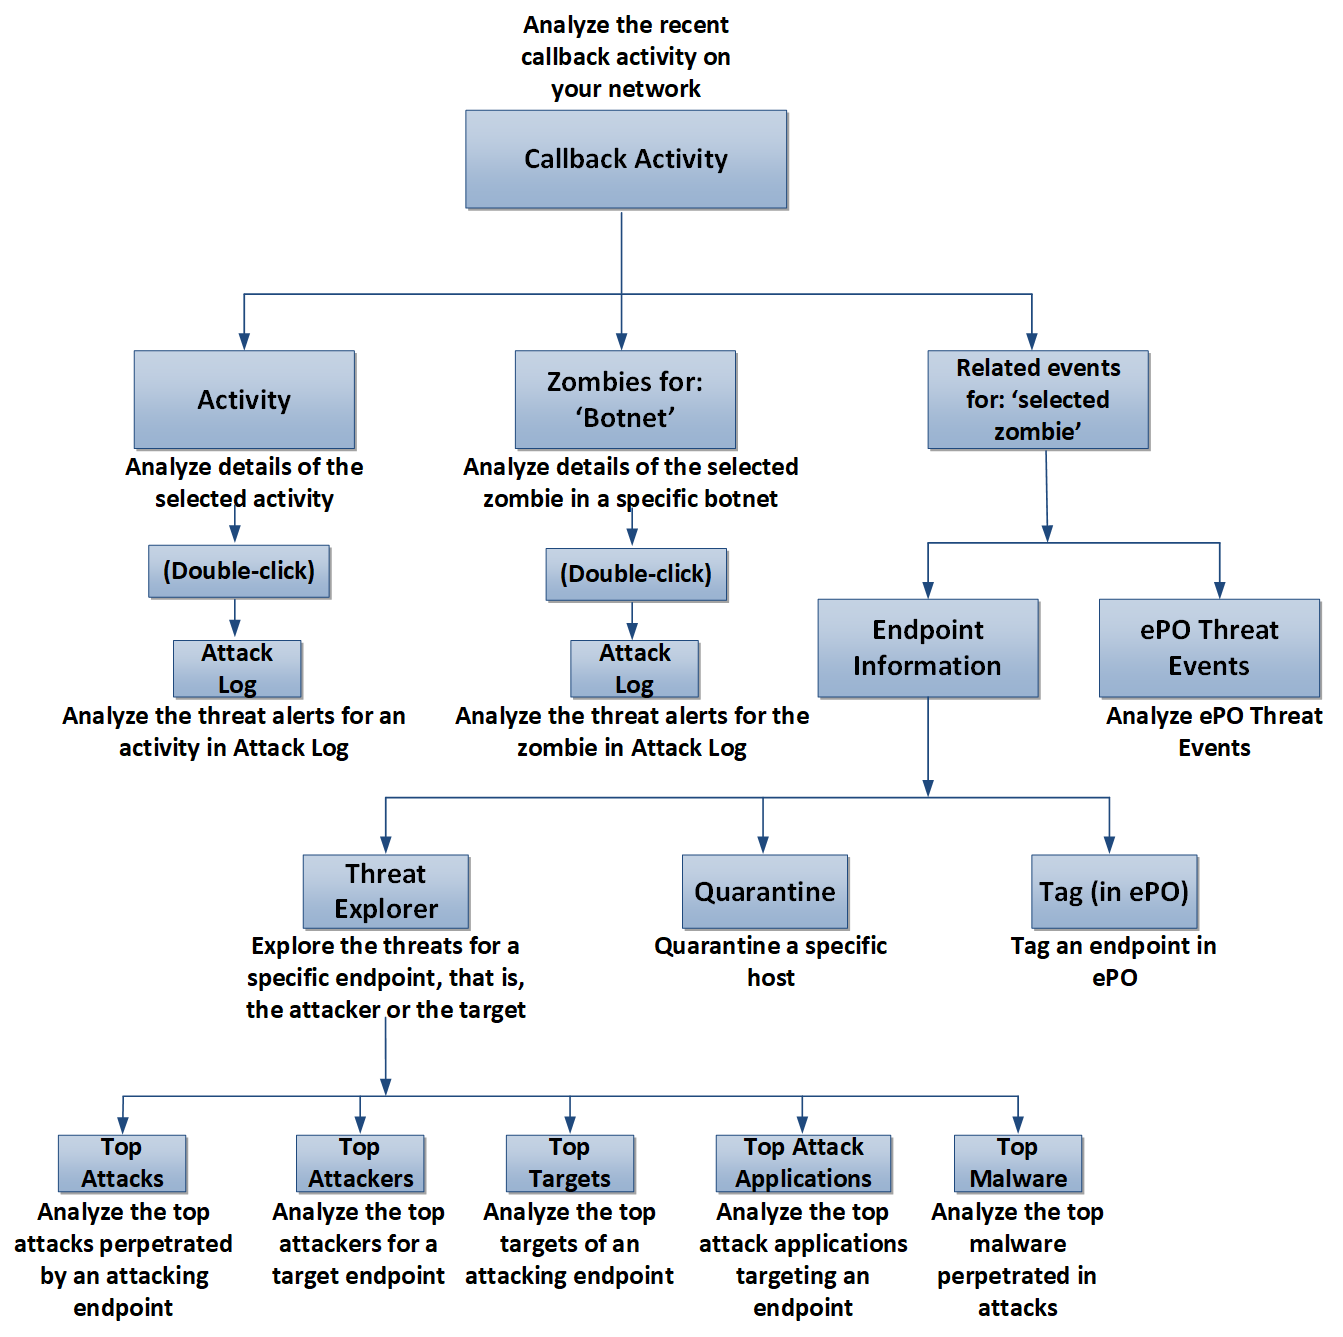
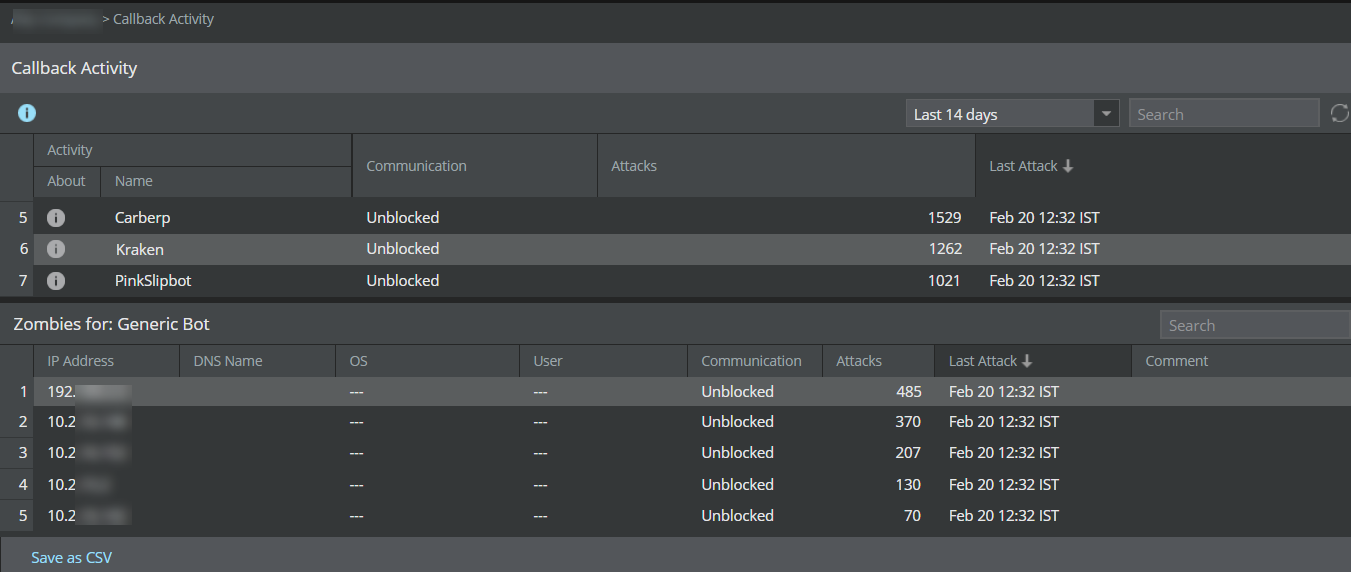
You can analyze details of the callback activities, such as the callback activity name, status of the Command and Control Server communication, number of events and the details of the last event occurrence.
You can further analyze the details of all the zombies in the activity. For each zombie you can view its IP address, DNS name, operating system, user details, status of the Command and Control Server communication, number of events and the details of the last event occurrence.
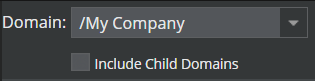
Filters can be applied at the admin domain levels which provide bot data for the selected admin domains. Data from the child domains are included in the data provided. The Include child domains checkbox is selected by default. Deselect the checkbox to view data only for the selected admin domain.
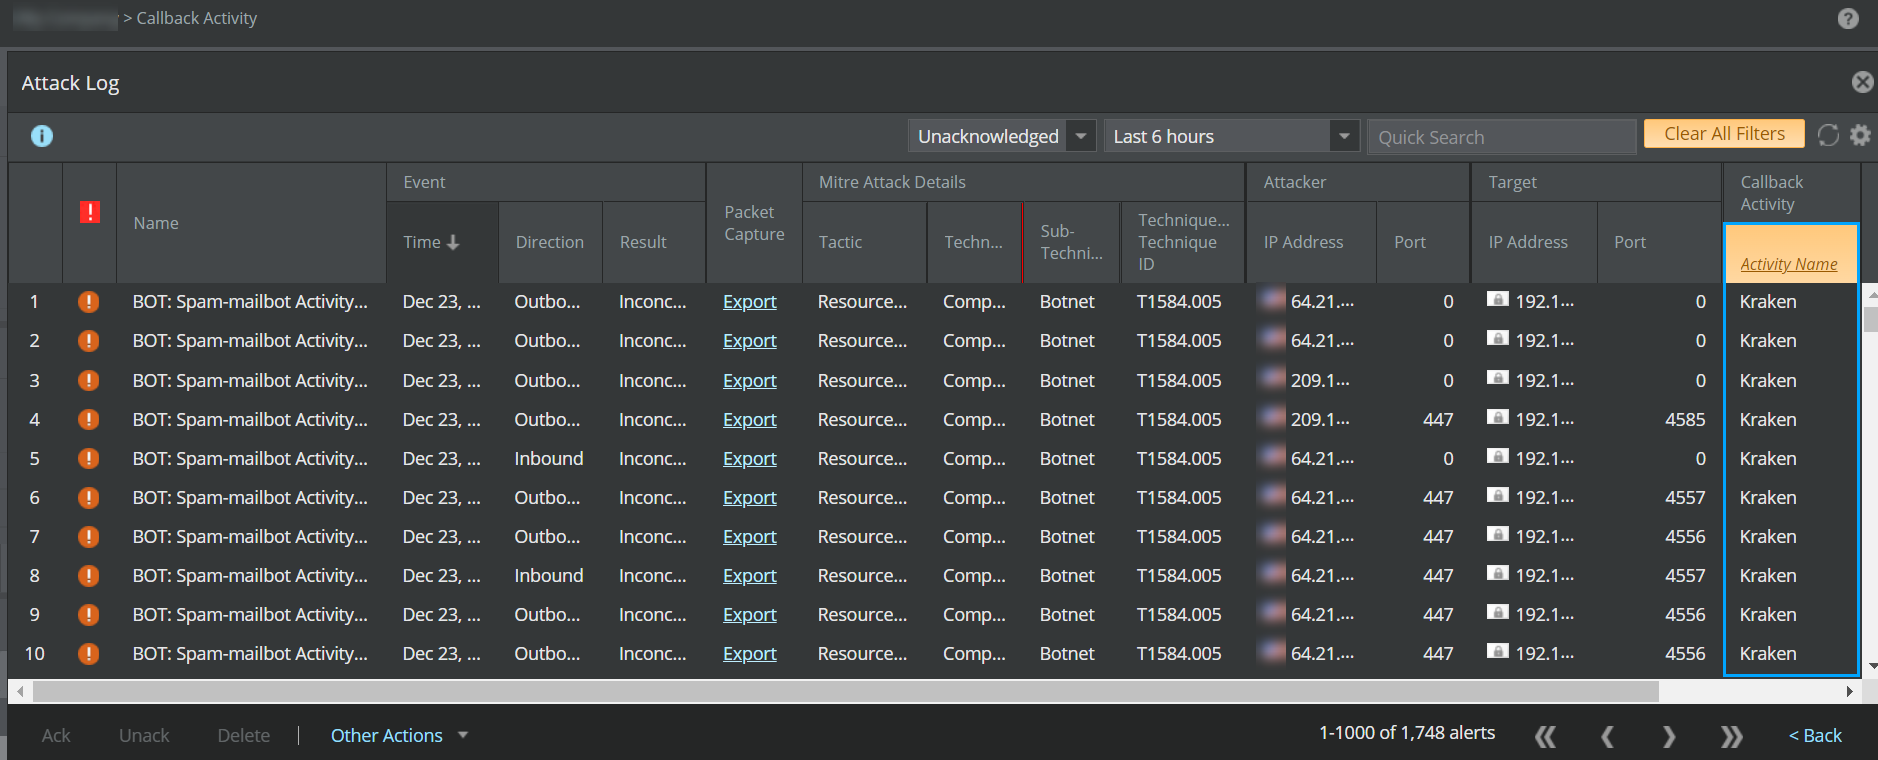
Attack Log
Upon double-clicking any callback activity under the Activity section, the Attack Log opens where you can view and analyze the alerts related to the callback activity.
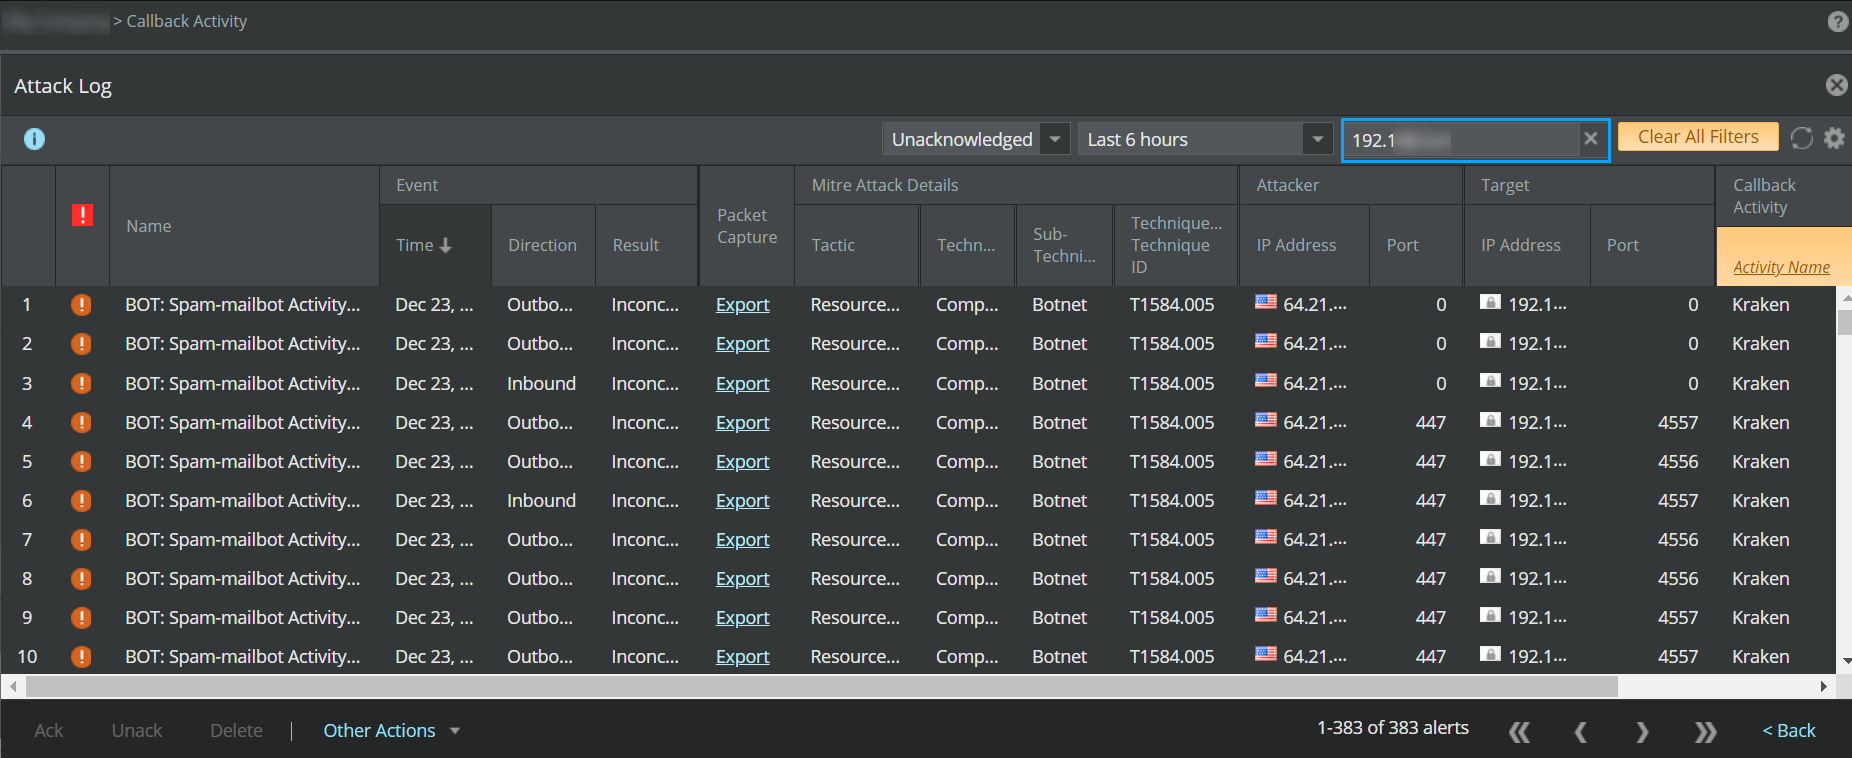
Double-click the IP address under the Zombies for: <Activity> section to view alerts related to the IP address and callback activity.
To close the attack log, click Back or  icon.
Activity
This tab displays the following details of the selected activity.
Option | Definitions |
|---|---|
About | Click to view the detailed Activity Description. This comprehensive activity report provides information, such as the activity description, symptoms of the bot, bot prevention methods, and bot removal tips. |
Name | The name of the callback activity family |
Communication | The status of the bot's communication with the Command and Control server, whether blocked or unblocked |
Attacks | The number of attacks executed by all the bots listed under the callback activity family |
Last Attack | The date and time of occurrence of the last attack |
Zombies for: <activity>
This tab displays the details of the selected zombie for a particular activity.
Option | Definitions |
|---|---|
IP address | IP address of the attacker |
DNS name | DNS name of the endpoint to resolve the names to IP addresses |
OS | Operating system platform of the endpoint |
User | Operating system user name of the endpoint. |
Communication | The status of the bot's communication with the Command and Control server, whether blocked or unblocked |
Attacks | The number of attacks executed by a selected bot/IP address |
Last Attack | The date and time of occurrence of the last attack |
Comment | Additional comments on the activity can be added |
'Zombie IP address'
This tab displays various events related to a specific zombie.
Endpoint Information
The Endpoint Information sub-tab shows the following details specific to the endpoint.
Analyze Endpoint Information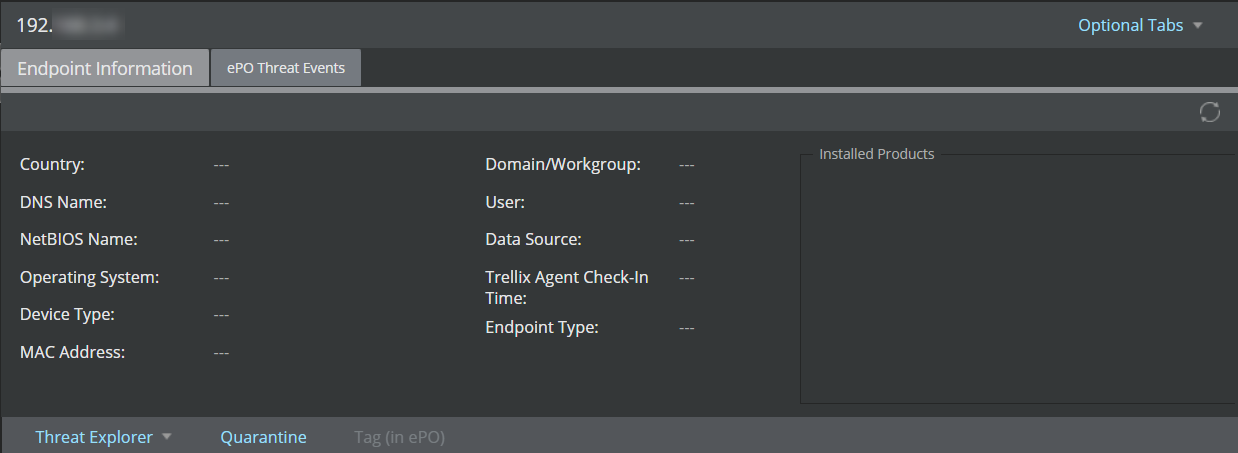
Option
Definitions
Country
Country of the endpoint
DNS Name
DNS name of the endpoint to resolve the names to IP addresses
NetBIOS Name
NetBIOS name of the endpoint to access the endpoint machines
Operating System
Operating system platform of the endpoint
Device Type
Device type of the attacker/target
MAC Address
MAC address of the endpoint
Domain/Workgroup
Domain or workgroup of the endpoint
User
Operating system user name of the endpoint
Data Source
Point product (ePO - On-prem) from where information is retrieved
Trellix Agent Check-In Time
Check-in time of the Trellix Agent that communicates with the same ePO - On-prem server integrated with the admin domain
Endpoint Type
Type of the endpoints:
UNMANAGED (No Agent) — This indicates that there is no Trellix Agent installed on the endpoint.
UNMANAGED (MANAGED) — This indicates that the endpoint has a Trellix Agent but there is no active communication channel between the Agent and ePO - On-prem server integrated with the admin domain.
MANAGED — This indicates that the endpoint has a Trellix Agent and there is active communication channel between the Agent and ePO - On-prem server integrated with the admin domain. The endpoint is managed by the agent.
Installed products
List of the installed products
Threat Explorer
Explore as attacker IP — Explore the threats where the endpoint is the source IP address.
Explore as target IP — Explore the threats where the endpoint is the destination IP address.
Quarantine — Use this option to block all the traffic originating from the specified IP address seen on the selected device for the selected time.
Quarantine Endpoint dialog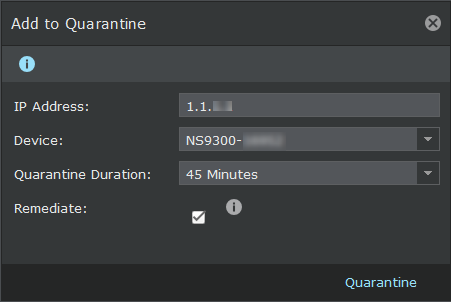
To quarantine endpoints to block all the traffic originating from the specified IP address:
Option
Definition
IP Address
Enter the IP address of the endpoint.
Device
Select the specific device of the endpoint whose traffic originating from the IP address you want to block.
Quarantine Duration
Select the quarantine duration from the drop-down list.
Remediate
Select the checkbox to redirect the configured endpoint to the configured remediation portal.
Note
You can configure the remediation portal settings in Devices → Global → IPS Device Settings → Quarantine → Remediation Portal.
Remediation cannot be configured for IPv6 address. The checkbox and the information icon for remediation are not displayed if you enter an IPv6 address in the IP Address field.
Click Quarantine. The endpoint is added and displayed in the Quarantine page.
Tag (in ePO) — Use this option to assign a tag to the selected endpoint in ePO - On-prem.
You are able to assign tags only to endpoints whose Endpoint Type denotes MANAGED. This means that the endpoint runs a suitable version of Trellix Agent and is managed by ePO - On-prem.
To assign a tag:
Select a tag from the drop-down list. If the tag you are looking for does not appear in the list, click the refresh button.
Click Tag.
If the tagging is successful, you receive a message stating its success. If not, you receive a failure notification.
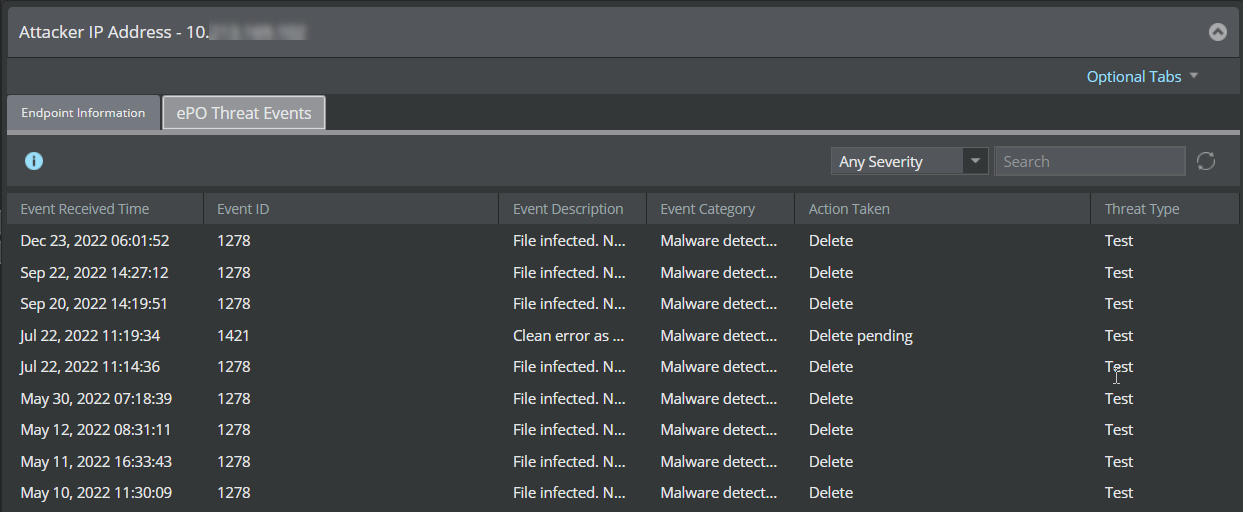
ePO Threat Events
The ePO Threat Events sub-tab displays the latest 50 Threat Events listed in the ePolicy Orchestrator - On-premises for a selected endpoint. The information displayed under this sub-tab includes the date and time at which the threat event was generated, the ID associated with the event, the event description, event category, action taken on the event, and the type of the threat that triggered the event.
You can click the
 icon to refresh the list and view the latest 50 Threat Events listed in the ePolicy Orchestrator - On-premises for the selected endpoint. The Search text field allows you to search for a specific event based on the Event Received Time, Event ID, Event Category and Threat Type. For example, to view all events associated with the Event ID 1095, type
1095in the Search field.Note
The sub-tab has Any Severity filter selected by default. With this filter selected, the sub-tab displays all types of events including those which are informational and/or of low-severity. Such events act as noise and impede one's ability to find true threats. To exclude these events, select the Warning+ Severity Only filter from the drop-down menu. This displays only those events with Critical, Alert and Warning severity.
Note
Ensure that the ePO server has the latest Trellix IPS Extension file installed. For information on how to download and install the Trellix IPSExtension, see section Install Trellix IPS extension file in ePO - On-prem in Trellix Intrusion Prevention System Integration Guide.
ePO Threat Events sub-tab