A Sensor has a specialized heuristic engine to detect DGA-generated domains. Sensors perform the following tasks as part of DGA detection:
Sensors identify the bots as they attempt to resolve C&C domains.
When a bot successfully resolves a DGA-generated domain, Sensors attempt to identify and expose the C&C infrastructure of that DGA-based botnet.
Post-detection of the C&C infrastructure, Sensors look for any subsequent communication between the C&C server and hosts on your network. This identifies the other bots on your network.
Note
For interfaces in SPAN and tap mode, you must enable DGA detection in both inbound and outbound direction.
At a high-level, Trellix IPS detects DGA-related information as described in this section.
For the sake of explanation, assume the following:
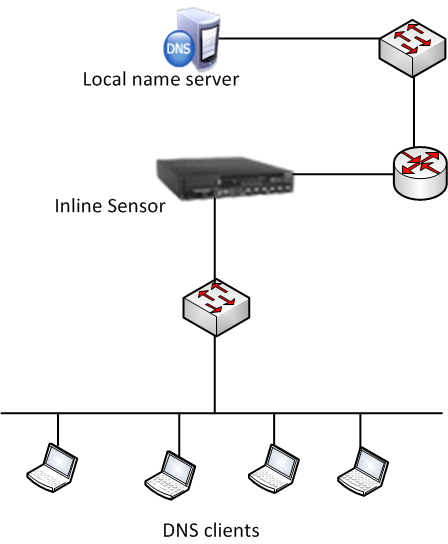
Sensor monitoring ports are inline between the protected hosts (DNS clients) and the local (recursive) name server. Therefore, all DNS requests and responses pass through the Sensor.
You have configured the DNS clients as the inside network. That is, the name server is in the outside network. The Sensor inspects DNS response packets for DGA. So, you must enable Domain Generation Algorithm Detection for outbound in the inspection option policy. This enables the Sensor to track the DNS response with the corresponding request.
Note
For DGA, a Sensor does not inspect AAAA records.
The Sensor first detects an infected host.
The Sensor starts its DGA heuristic analysis, if it suspects DGA involvement in the monitored DNS traffic.
The Sensor filters out DNS packets, which need not be inspected for DGA. The Sensor excludes the suspicious DNS traffic from DGA analysis, if any of the following conditions are met. The Sensor checks the DNS response packets in the following sequence.
The source or destination IP address in the DNS response packet belongs to CIDRs Excluded from Advanced Callback Detection list.
The domain is exempted according to the user-defined domain name exceptions. Assume that you have imported the domain name exceptions in the Manager and enabled Domain Name Exclusion List Processing in the inspection option policy.
The domain is blocked according to the callback detectors. Assume that you enabled Callback Detectors and Heuristic Callback Discovery in the inspection option policy. Then, the Sensor sends a crafted DNS response packet to sinkhole the corresponding callback traffic.
If you disabled Callback Detectors and Heuristic Callback Discovery, the Sensor inspects the DNS traffic for DGA even for C&C server domains.
Note
If a requested domain name resolves to an IP address of a reserved CIDR, such as the private network CIDRs in RFC 1918, the Sensor does not consider that IP address for DGA C&C suspect processing.
The Sensor mines the information in the DNS packets and runs them through its heuristic engine. If the heuristic analysis indicates that the domains are DGA-generated, the Sensor does the following.
The Sensor raises the Botnet: DGA Heuristic Detection of Botnet Zombie alert.
The possible Sensor actions for this alert are to quarantine and remediate the victim host and send an alert to the Manager. Capturing the packets is not applicable.
For a specific time period, the Sensor tracks the subsequent DNS traffic to and from the bot to detect the C&C domain.
Note
If the same host is infected by different malware family using a different DGA, the Sensor raises an alert separately for each unique DGA.
After detecting a bot, the Sensor attempts to identify the C&C domain and the corresponding IP addresses.
The Sensor monitors the DNS traffic for all bots detected for a specific time period to discover the current C&C domain name.
Some DGA deliberately query for legitimate domain names to mislead security products. Also, the user logged on to the bot might query for a legitimate domain name. So, the Sensor performs a detailed analysis to accurately identify the C&C domain.
When the C&C domain is detected, the Sensor raises the Botnet: DGA Heuristic Detection of C&C Server in DNS Response alert.
If any of the monitored hosts in your network attempt to communicate with the C&C IP addresses, the Sensor raises the Botnet: DGA Heuristic Detection of Connection to C&C Server alert. This alert enables you to identify all hosts in your network, which are part of the botnet.