Prerequisite: Make sure you have created a Firewall policy with the required access rules.
A Firewall policy is useful for maximizing a Sensor's detection and prevention capabilities by denying specified traffic without requiring full inspection, while also permitting certain traffic to pass without inspection.
At the Sensor level, you can assign a Firewall policy for the entire Sensor as well as those for specific ports/port pairs of the Sensor. Policy assigned at the Sensor level for a specific port/port pair are inherited by all the ports/interfaces/subinterfaces, while policy assigned is inherited by the corresponding interface and, if applicable, subinterfaces. In the case of Firewall policies, an interface is a subset of the corresponding port or port pair. That is, access rules configured for a port/port pair at the Sensor level are inherited by the corresponding interface as well as any subinterfaces. However, rules created at the interface level are not inherited by corresponding subinterfaces due to the rule of separating interface traffic flows from subinterface traffic flows based on the following policy application rule:
If you configure multiple access rules, note the order as access rules are executed in top-down sequence: the rule at the top of the list is checked first, followed by subsequent rules down to the bottom-most rule. Trellix IPS employs a first-match process; the first rule matched in sequence is enforced.
If you apply a policy to a subinterface that is different than the inherited policy, the policy enforced at the interface level protects all traffic not specific to the subinterface. Thus, for access rules, the rule of inheritance requires you to create global rules at the Sensor or physical port/port pair level: interface rules only apply to interfaces, and subinterface rules only apply to subinterfaces.
Access rules applied at the Sensor level are inherited by all interfaces and subinterfaces of the Sensor. You can add more rules at the interface and subinterface levels; however, you cannot delete inherited rules at the child levels. Even if no rules have been assigned at the Sensor level, you can assign rules at the interface and subinterface levels.
In a Firewall policy, you can create unique access rules for inbound and outbound traffic, respectively. Inbound refers to any traffic destined for the internal network from an external source. Outbound refers to any traffic that originated from your internal network.
You assign rules to a Sensor/port/interfaces or subinterfaces using the Policy Manager panel and view the order of the rules at the ports, interfaces, or subinterfaces by clicking Inbound or Outbound in the Effective Rules field of the corresponding Policy Manager panel.
For a Sensor, ports, and interfaces, or subinterfaces, you can choose rules created at admin domain and apply them to the entity.
Select Intrusion Prevention → Policy Types → Firewall Policies.
Click the Assignments value of the policy that you want to assign.
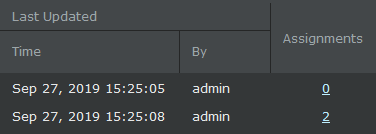
The Assignments window displays. It lists the available resources for the admin domain.
Assign the policy to the required Sensor resources.
Assignments window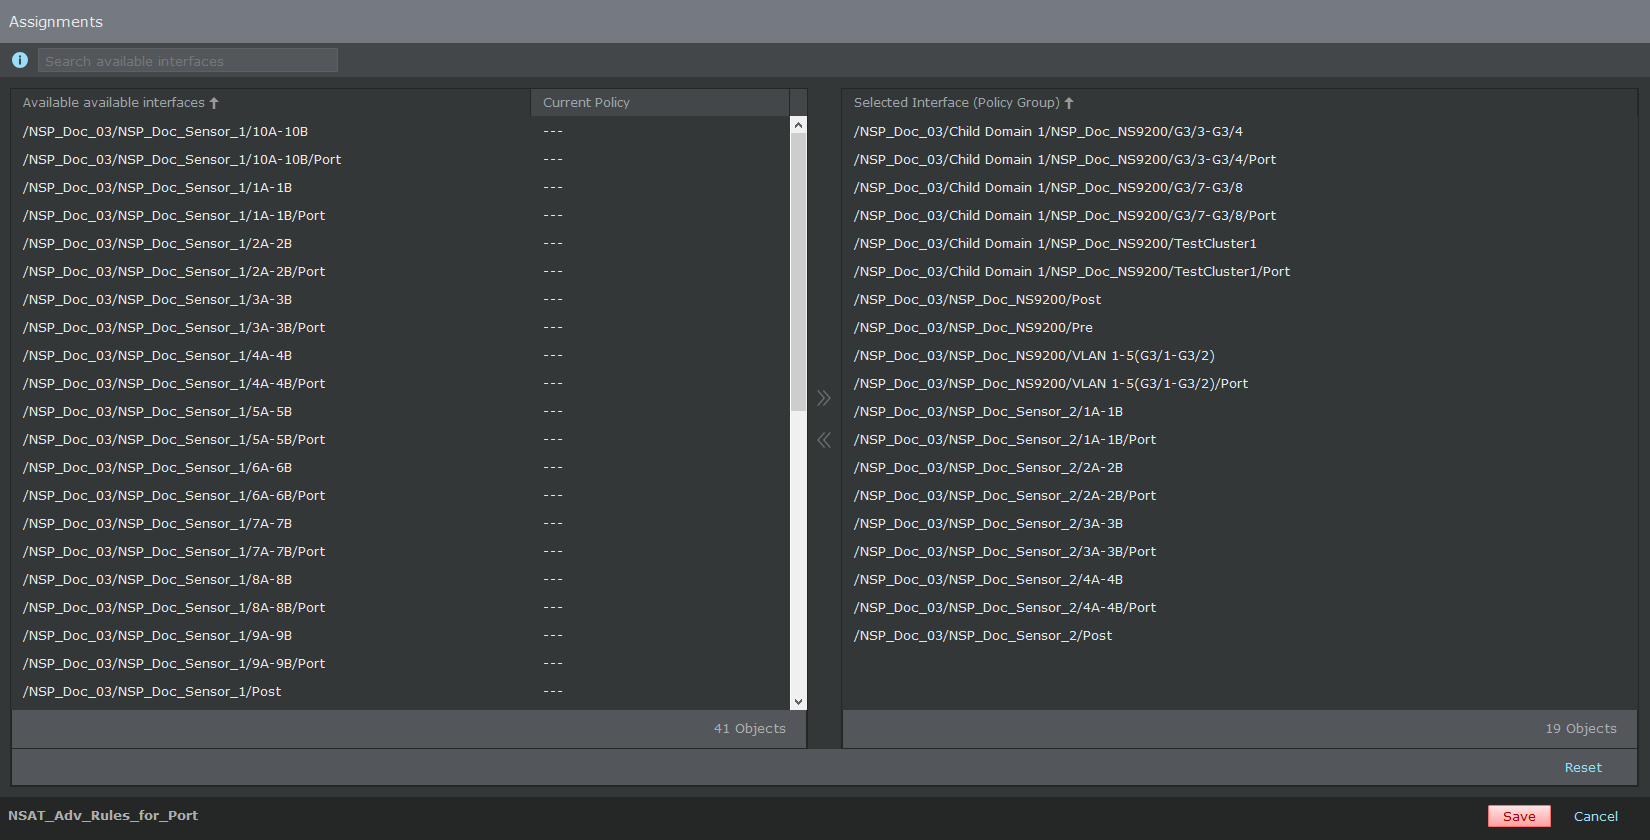
Option
Definition
Search Interfaces
To filter the list of available resources and selected resources, enter a string that is part of the Available Interfaces or Selected Interface.
Available Interfaces
Lists the Sensor resources for the admin domain. For example, if an admin domain has only Sensor ports allocated from the parent domain but no Sensor of its own, then no device-level resource is listed. Also, the items in this list are filtered based on your filter criteria.
Note
In case of Sensors in failover, the ports used for interconnection of the Sensors are not displayed. If you have assigned the Firewall policy to an interconnect port, the assignment is automatically removed when you create the failover.
Select a resource and click
 to move it to Selected Interface.
Current Policy
The Firewall policy that is currently assigned to a resource. To replace that policy with the policy that you are currently assigning, move the resource to Selected Interface.
Selected Interface (Policy Group)
Lists the Sensor resources to which you have assigned the policy.
Reset
Reverts to last saved configuration.
Save
Saves the changes to the Manager database.
Cancel
Closes the Assignments window without saving the changes.
Verify the list of effective inbound and outbound rules at the corresponding ports, interfaces, or subinterfaces.
Note that the Sensor checks the traffic against the effective rules in a top-down fashion.
You can view the Effective Rules in the Policy Manager panel at the interface and sub-interface levels.
Do a configuration update for the Sensor to enforce the policy.
There are many options to assign Firewall policies to Sensor resources. You can also go to the Policy Manager page of a specific Sensor resource and select a Firewall policy for that resource. These options are described here. Ensure you do not assign the same Firewall policy to more than one resource of a Sensor.
To assign a Pre-device or Post-device Firewall policy:
Click the Policy tab.
Select the domain from the Domain drop-down list.
Navigate to Intrusion Prevention → Policy Manager.
Select the Devices tab and double-click the Sensor to which you would like to assign the Firewall policy.
The <Sensor Name> panel opens.
Under the Firewall-Device First and Firewall-Device Last sections, select the policy to be assigned from their respective Policy drop down lists.
To create a new policy, click the
 icon or click the
 icon to edit an already assigned policy.
If you are creating a new policy, proceed to step 7. If you are editing an existing policy, proceed to step 8.
The Properties page opens. Enter the Name and Description. Select the Visibility and Type. Click Next.
The Access Rules page opens.
Assigning Firewall policy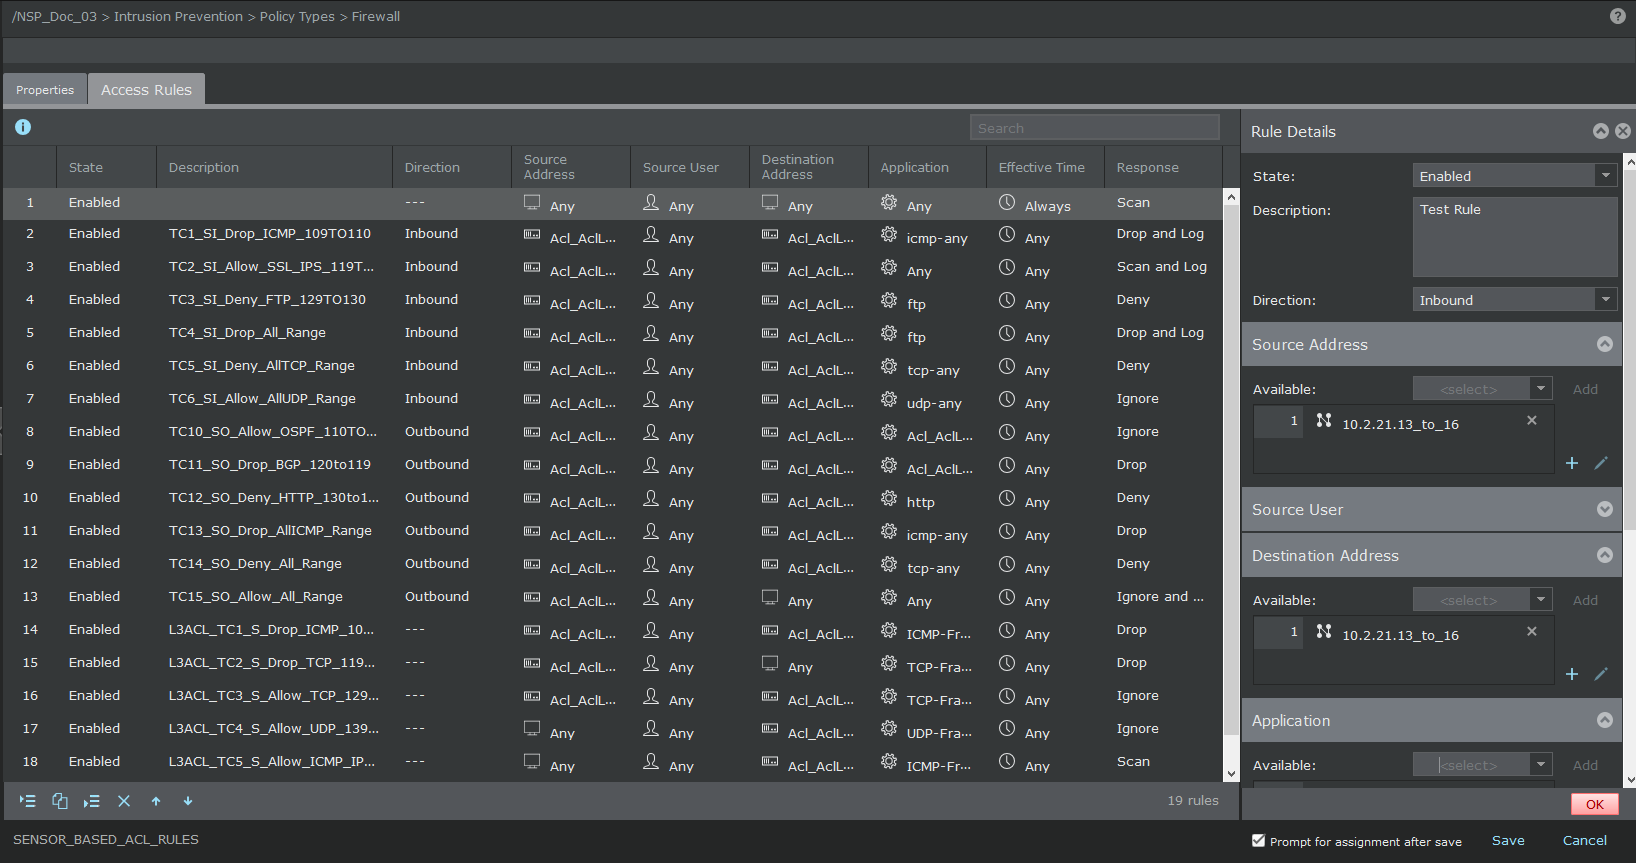
Click the
 icon to insert a new rule or double-click the existing rule to edit.
In both cases the Rule Details panel opens.
Select the necessary rules under the Source Address, Source User, Destination Address, Application, Effective Time, and Response sections.
Click OK and then Save the changes.
Do a configuration update for the Sensor to enforce the policy.
To assign a Firewall policy to port or interface and sub-interfaces:
Navigate to Policy → Intrusion Prevention → Policy Manager.
In the Interface tab, double-click the interface/sub-interface to assign the firewall policy.
The <Device name/Interface> panel opens.
In the Firewall section, select the policy from the Interface Policy drop down list.
To create a new policy, click the
icon or click the icon to edit an already assigned policy.If you are creating a new policy, proceed to step 6. If you are editing an existing policy, proceed to step 7.
The Properties page opens. Enter the Name and Description. Select the Visibility and Type. Click Next.
The Access Rules page opens.
Click the
icon to insert a new rule or double-click the existing rule to edit.In both cases the Rule Details panel opens.
Select the necessary rules under the Source Address, Source User, Destination Address, Application, Effective Time, and Response sections.
Click OK and then Save the changes.
Click Save to save the configuration changes updated.