Prerequisite: You can create rule objects when creating the Firewall access rules. However, a systematic approach is to create the required rule objects before you create the Firewall access rules. You create a Firewall policy using access rules as the building blocks.
Be sure whether you need a classic or advanced Firewall policy. Review the Differences between Advanced and Classic Firewall policies section. To use advanced features such as require-authentication access rules, user-based access rules, and application-based access rules you need advanced Firewall policies.
When you create the access rules, be aware that for a given traffic, the Sensor executes the rules in a top-down fashion and stops the execution when a rule matches. The following are some recommendations that you can consider:
As a precaution, create a rule that allows traffic to the basic network infrastructure servers such as AD, DHCP, and ePO - On-prem. Make sure this is the first rule in the list. This is to ensure that your Firewall policy does not prevent the hosts from receiving an IP address or your users from authenticating against the AD.
If you require, create all the required authentication access rules right after the rule that allows traffic to the infrastructure servers.
Define the specific rules above the broader rules. For example, rules for Facebook, Google, Yahoo and so on must be above the HTTP rule.
To create user-based access rules, you use user and user group rule objects. Note the following:
You can create these rules only in Advanced Firewall policies.
To create these rules, you must first integrate Trellix Logon Collector 3.0.11 with the Manager.
Before you create these rules, make sure the AD server is able to authenticate the users and these details are reflected correctly in Trellix Logon Collector.
If Kerberos snooping is required, you must configure the Active Directory server details and Trusted Domain Controllers in the respective pages of the Manager.
For the require-authentication rules to work, the Guest Portal on the Sensor must be up, and you must configure the IP address settings for the corresponding monitoring ports as well.
Click the Policy tab.
From the Domain drop-down list, select the domain you want to work in.
Select Intrusion Prevention → Policy Types → Firewall.
Click
 .
Specify the details on the Properties tab.
Option
Definition
Name
Enter a unique name to easily identify the policy.
Description
Optionally describe the policy for other users to identify its purpose.
Owner
Displays the admin domain to which the policy belongs
Visibility
When selected, it makes the policy available to the corresponding child admin domains.
Note
However, the policy cannot be edited or deleted from the child admin domains.
Editable here
The status Yes indicates that the policy is owned by the current admin domain.
Type
Select the type — Advanced or Classic. After you save the properties, you cannot change advanced to classic.
Statistics
Lasted Updated
Displays the time stamp when the quarantine zone was last modified
Last Updated By
Displays the user who last modified the quarantine zone
Assignments
Indicates the number of Sensor resources to which the policy is assigned
Inbound Rules
Displays the number of access rules currently defined for inbound traffic
Outbound Rules
Displays the number of access rules currently defined for outbound traffic
Prompt for assignment after save
When selected, you are automatically prompted to select the Sensor resources to which you want to assign the policy.
Next
Click Next to save the changes made on the Properties tab and access the Access Rules tab.
Important
After you click Next you cannot change the type from advanced to classic.
Save
Saves the changes made on the Access Rules tab. This is also visible when you open an existing policy.
Cancel
Reverts to the last saved configuration
On the Access Rules tab, click the appropriate button to insert a new rule.
Button
Definition

Inserts a new rule above the currently selected rule

Inserts a new rule below the currently selected rule

Clones the currently selected rule

Deletes the currently selected rule

Moves the currently selected rule one row up

Moves the currently selected rule one row down
Select the section of an access rule and specify your choices.
Adding Firewall access rules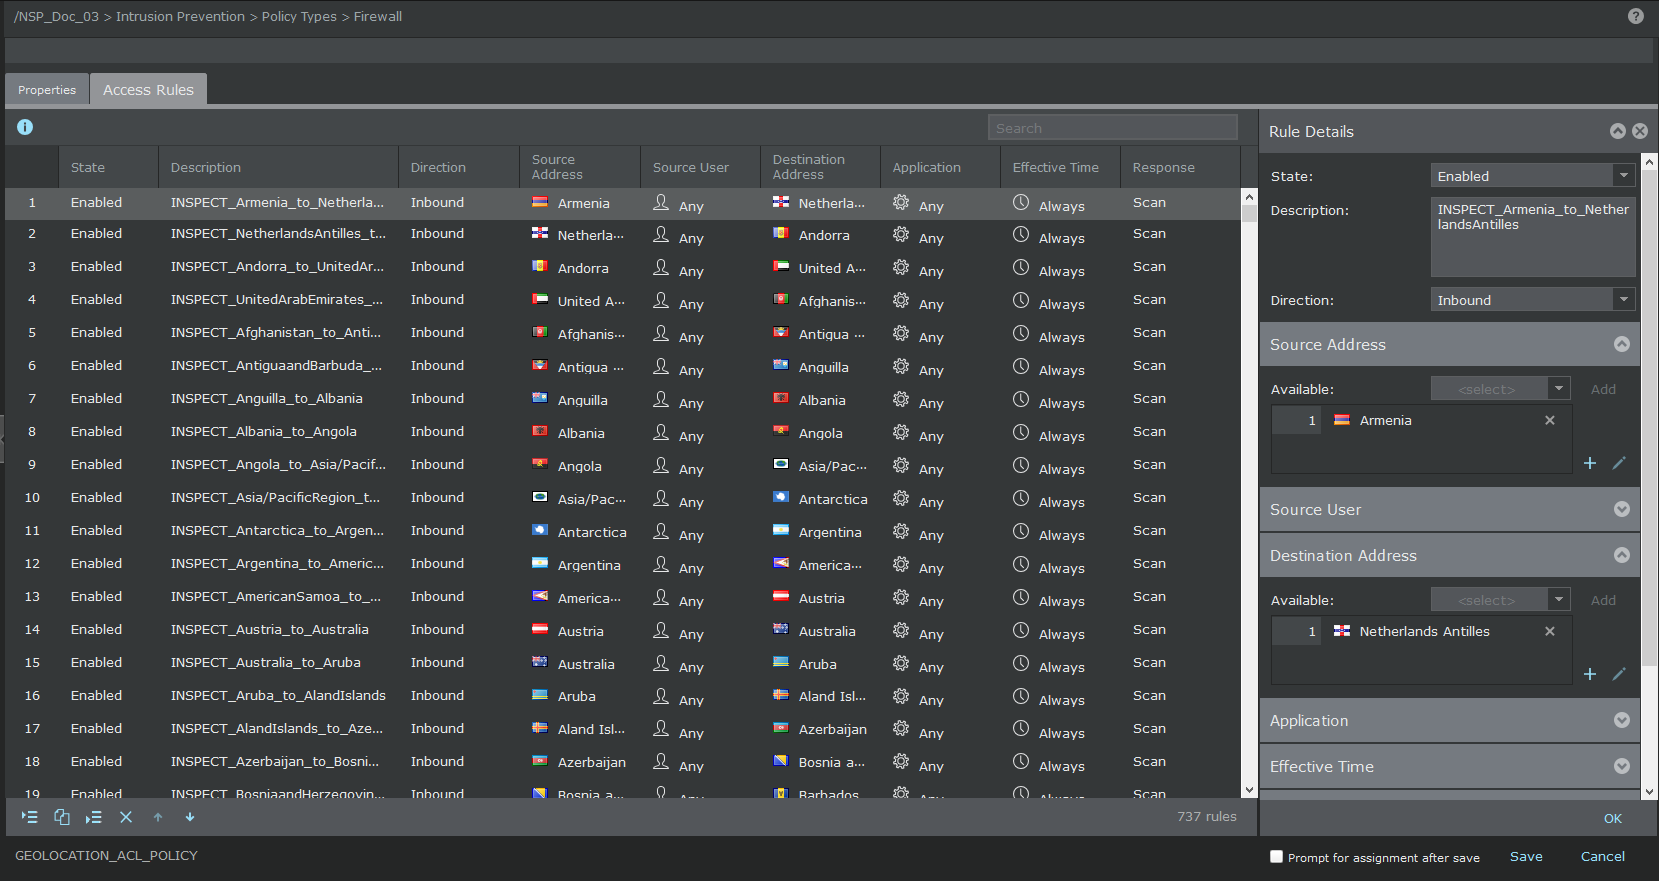
For advanced Firewall policies, change the values of Source Address, Direction, Source User, Destination Address, Application, Effective Time and Response. For classic Firewall policies, change the values of Source Address, Destination Address, Service, Direction and Response.
Option
Definition
#
Displays the serial number of the rule
State
Displays whether a rule is enabled or disabled. Sensor does not apply disabled rules. This option might help you during troubleshooting.
Description
Optionally enter additional information about the rule. This might help you to easily understand the logs forwarded to the syslog server. You can enter a description up to 64 characters long and click OK.
Direction
Inbound — To apply this rule only to traffic seen at the outside port
Outbound — To apply this rule only to traffic seen at the inside port
Any — To apply this rule at both the ports
Source Address
Select the rule objects corresponding to the source of the traffic from the Available list.
Click Add to add a rule object.
Click
to create a new rule object.Click
 to edit or view a rule object.
Click
 to remove the rule object from the list.
Destination Address
Select the rule objects corresponding to the destination of the traffic from the Available list.
Click Add to add a rule object.
Click
to create a new rule object.Click
to edit or view a rule object.Click
to remove the rule object from the list.Application
Select the rule objects corresponding to the application from the Available list.
Click Add to add a rule object.
Click
to create a new rule object.Click
to edit or view a rule object.Click
to remove the rule object from the list.Source User
This option is for user-based rules. Recall that the Manager receives users and user groups from Logon Server and automatically displays them as rule objects. User groups are listed by default.
User groups are listed by default. Select the user group from the Available drop-down list. Click Add to add the selected user group to the list.
Click
to remove the user group from the list.To select the user:
Select User from the Type drop-down list.
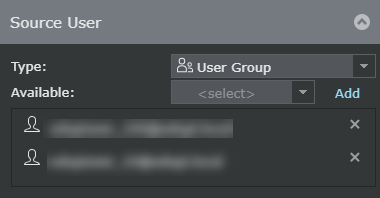
In the Search User text field, type the fist few letters of the name you want to find and click the Find button. The list of users with the searched criteria is listed in the Available drop-down list.
Click Add to add the selected user to the list.
Click
to delete user from the list.
Service
Select the Application or Service-related rule objects from the Available list.
Click Add to add the selected service.
Note
This option is available only for classic firewall policies.
Click
to create a new rule object.Click
to edit or view a rule object.Click
to remove the rule object from the list.You can have Service or Application-related rule objects in a rule but not both.
Effective Time
Select the time-based rule objects to specify the time when the Sensor should implement the rule, from the Available list.
Click Add to add the selected service.
Click
to create a new rule object.Click
to edit or view a rule object.Click
to remove the rule object from the list.Note
Time-based rules are implemented using the local time zone of the corresponding Sensor.
Response
Specify the response action the Sensor should take on the traffic that matched the rule.
Primary Action:
Note
To configure stateful access rules, use the response actions Deny, Drop, Ignore, Scan, Scan with Priority, or Require Authentication.
Deny — Discards the traffic and resets the connection with the source of the traffic.
Drop — Discards the traffic.
Ignore — Allows the traffic to pass through without any further inspection.
Scan — Allows the traffic but inspect it for attacks.
Scan with Priority — Allows you to prioritize critical network traffic. The prioritization increases the usable bandwidth for high priority packets to optimize performance. Consider you have a traffic comprising of HTTP, SMTP, FTP, POP, and so on and you have configured a priority access rule for HTTP traffic. In this case, during heavy network load conditions, the HTTP traffic is always put in the priority queue and processed and non-HTTP traffic is dropped.
In case of a heavy network load condition comprising of HTTP traffic only, some HTTP packets might be forwarded or dropped.
In case of High priority traffic is latency sensitive, that is, it has lower latency compared to other traffic.
Note
This option is available only for advanced Firewall policies.
For information on Require Authentication, see the following step.
For information on Stateless Drop and Stateless Ignore, see Using stateless access rules.
Log to Syslog — Select if you want to log the details of the traffic that matched the rule.
Prompt for assignment after save
If you clear this option you can save the policy now and assign it to the Sensor resources as explained in the following section. If you select this option, the Assignments window opens automatically when you save the policy and you can assign the policy to the required Sensor resources.
Save
Saves the access rules in the Manager database. The Firewall policy is listed in the Firewall list.
To create a require-authentication rule, do the following:
In the Description field, enter a description.
In the Response field of a rule, select Require Authentication, and click OK.
In the Application field, select only the default HTTP Service rule object.
Even the HTTP Application rule object or a custom HTTP Service rule object are not valid in a require-authentication rule.
Specify the values for Source Address, Destination Address, Effective Time, and Direction.
You must leave the Source User as Any.
Repeat the steps to add more access rules.
Following these steps, you can clone and edit Firewall policies.