Every attack definition provided by Trellix includes an attack description. The information in this description is designed to give reference to what the attack does and how to defend against the attack in the future.
Attack descriptions can be accessed from a number of areas:
Policy — during policy viewing/creation. Includes all Exploit, DoS, and Reconnaissance attacks.
Attack Log — within the details of a detected attack.
Threat Explorer — within the Top Attacks section by accessing any attack's hyperlink.
Trellix IPS KnowledgeBase — all entries within the Attack Encyclopedia.
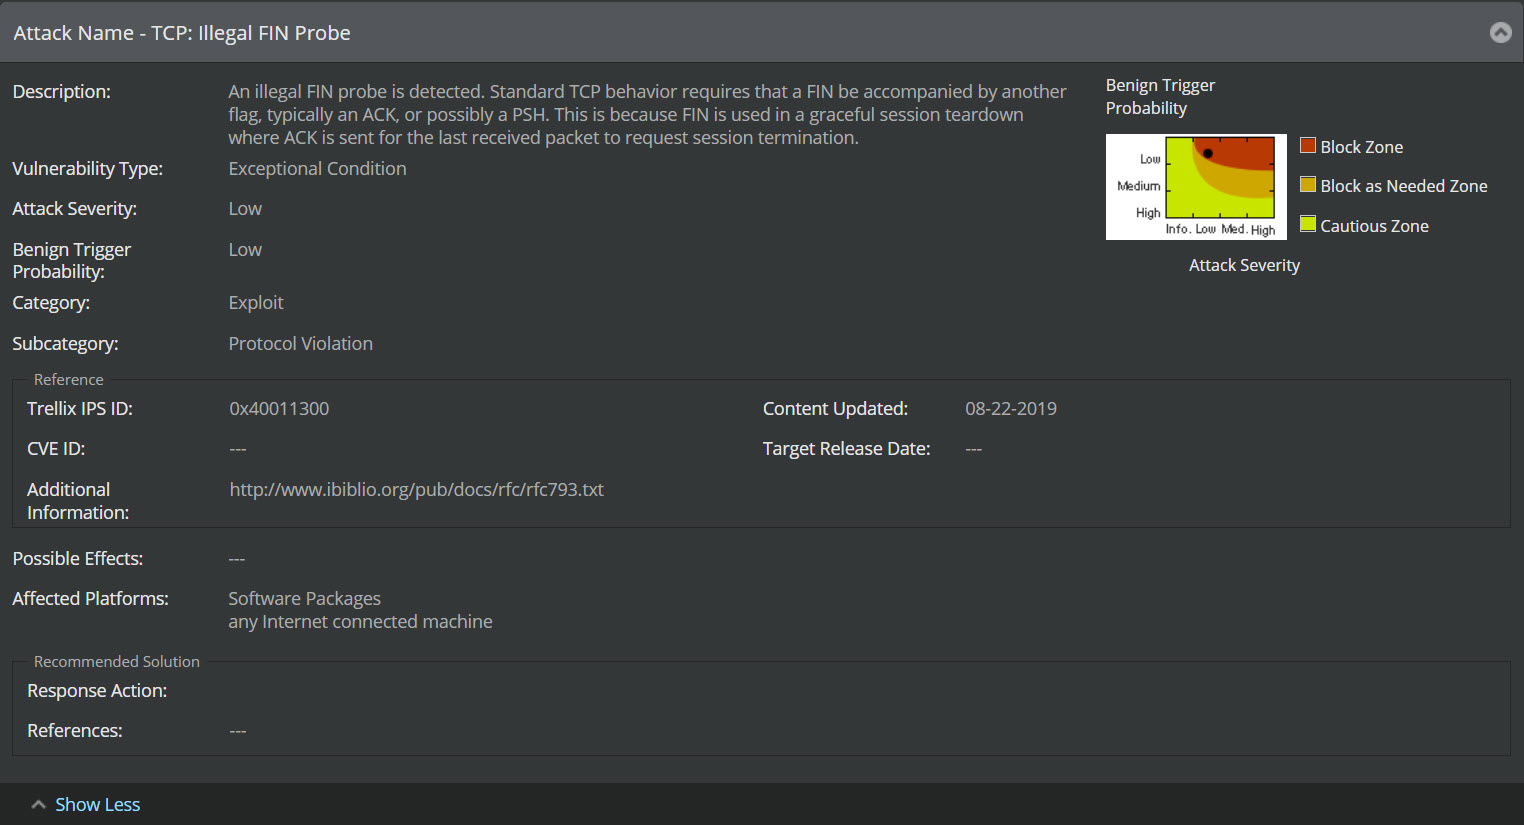
The Attack Information & Description fields are as follows:
Fields | Description |
|---|---|
Name | Trellix IPS-designated name for an attack. |
Vulnerability Type | Type of inherent system flaw that can be exploited by attackers. |
Impact Category | Type of impact that it can have on a system. |
Impact Subcategory | Type of inherent system flaw that can be exploited by attackers. |
Severity | Malicious impact potential of the attack. The values are high, medium, and low. |
Benign Trigger Probability | The benign trigger probability is the chance that the signatures for an attack may trigger a false positive. |
Description | Attack definition and conditions |
Possible Effects | The impact if the attack is successful. |
Recommended Solution | Available workarounds and patches |
Platforms Affected | Systems and/or software directly affected by the attack. |
Reference | Trellix IPS supports multiple standards and sources for finding information on known attacks. Cross-referencing a Trellix IPS attack name with a CVE name, BugTraq ID, or other link can assist your analysis of known attacks and vulnerabilities. Trellix IPS ID — globally unique attack ID within the Trellix IPS. Last Rev Date — last date attack information was updated. CVE — The Common Vulnerabilities and Exposures (CVE) name related to an attack. CVE maintains a list of standardized names related to publicly known vulnerabilities and security exposures. Refer to www.cve.mitre.org. A CVE name such as "CVE-1999-0001" is called an entry, denoted by "CVE" at the beginning of the name. An entry is a vulnerability or exposure that has been accepted by the CVE Editorial Board. A CVE name such as "CAN-2001-0002" is called a candidate, denoted by "CAN" at the beginning of the name. A candidate is a vulnerability or exposure that is "under consideration for acceptance into CVE." A CVE name has three fields — entry status, year of entry, and entry number during the year. Thus, if a CVE name reads "CVE-2000-0005," the vulnerability/exposure was the fifth accepted entry in the year 2000. Between candidacy and entry, a CVE entry will most likely change numeric ID along with the change from CAN to CVE-. Thus, CAN-2001-0023 may be accepted in the year 2002 and thus read — "CVE-2002-0002.". BugTraq: ID of attack as listed in the BugTraq database. Refer to http://online.securityfocus.com/. Microsoft — ID of attack as listed in the Microsoft Security Bulletin. Links — additional information sources. |
User Comments | Any comments that you have entered for the attack description. |