The Attack Compilation page enables you to specify the type of attack definitions to be included in the IPS Policies for a specific Sensor.
To access the Attack Compilation page, go to Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → Attack Compilation.
The Attack Compilation page opens.
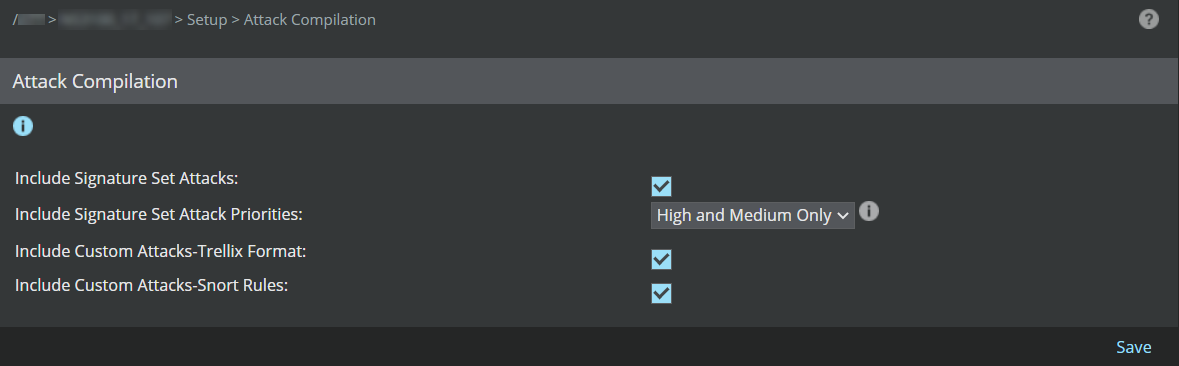
You can select the following types of attack definitions for the Sensor:
Signature Set Attacks - These are the attacks from Trellixsignature set.
When the Signature Set Attacks option is selected, the Manager allows you to choose Signature Set Attack Priorities for the Sensor. This allows the Manager to dynamically compile only critical attacks from the standard signature set for Sensors that do not have enough resources to support all attacks.
The signature set attack priorities available are as follows:
All: Includes all attack definitions in the signature set. This is the default signature set attack priority selected for NS-series and Virtual IPS Sensors and provides complete attack coverage.
High and Medium only: It comprises of high and medium priority attacks in the signature set.
High only: It comprises of high priority signature set attacks. You can use this option to optimize Sensor resources on Sensor models running older Sensor software versions to support the latest signatures against most critical attacks.
Warning
The High Only signature set attack priority provides an attack coverage only against the most critical attacks.
Custom Attacks – Trellix Format — These are the Trellix Custom Attacks that are defined or received from Trellix.
Custom Attacks–Imported Snort Rules — These are the Snort Custom Attacks that are imported or created in the Manager.