To launch the Virtual IPS Sensor as a virtual machine in the Azure environment, perform the following steps:
Go to Dashboard and type the Virtual IPS Sensor image name in the search field.
The Virtual IPS Sensor image page opens.
Click Create VM.
The Create virtual machine window along with the Basics tab opens.
On the Basics tab, enter the following details:
Option
Definition
Project details
Subscription - The subscription linked with your Azure account is selected by default. If you have multiple subscription accounts, select the subscription account in which you would like to launch the Virtual IPS Sensor virtual machine.
Resource group
Create new - You can create a new resource group to be protected.
Use existing - Select the resource group to be protected.
Instance details
Virtual machine name - Type a name for the Virtual IPS Sensor virtual machine.
Note
The Virtual IPS Sensor name should not exceed 25 characters.
Region - Select the region where the Virtual IPS Sensor virtual machine must be created.
Availability options - [Optional] Select the availability sets for providing high availability to the Virtual IPS Sensors. It is recommended to deploy one VM scale set for Sensors in one availability set and the other VM scale set for Sensors in another availability set. This way when there is a downtime, one of the Sensors is available.
Image - By default, Trellix Virtual IPS Sensor is selected as the image for the virtual machine.
Size - Select F4s_v2 for the Virtual IPS Sensors.
Administrator account
Authentication type - Select SSH authentication type.
Note
Only the SSH Public Key authentication type is supported for Sensors.
Username - Enter the user name for the Virtual IPS Sensor virtual machine.
Note
Trellix recommends using the Username created in Azure UI to access the Sensor CLI through SSH.
SSH public key store
Generate new key pair - You can create a new key pair in Azure for SSH login to the Sensor.
Use existing key stored in Azure - You can use a previously stored key pair in Azure for SSH login to the Sensor.
Use existing public key – You can a key pair generated using an external tool.
Note
The private key file for the SSH public key must be in .pem format.
Inbound port rules
Public inbound ports - Select the ports in the Virtual IPS Sensor to be accessible from the public internet. Trellix recommends you to select None.
Note
Azure validates the information you enter and a green tick appears against the fields where you enter details.
Click Next: Disks >.
The Disks tab opens. Enter the following details:
Option
Definition
Disk options
OS disk type - The SSD type is selected by default. Trellix recommends you use Premium SSD disk type for Virtual IPS Sensor for improved performance.
Data disks
You can attach a new disk or an existing disk for your virtual machine.
Advanced
Use Managed disks - Select Yes for Azure to manage the disk availability automatically.
Click Next: Networking >.
The Networking tab opens. Enter the following details:
Option
Definition
Network interface
Virtual network - Select the virtual network in which the Virtual IPS Sensor must be deployed.
Subnet - Select the subnet in which the Virtual IPS Sensor must be deployed.
Public IP address - Trellix recommends you to not assign public IP address to the Virtual IPS Sensor virtual machine.
NIC Network security group (firewall) - Select Advanced and assign pre-configured network security group rules.
Configure network security group - Select the security group created for the Virtual IPS Sensor.
Accelerated networking - By default, Off is selected as the selected image does not support accelerated networking.
Click Next: Management >.
The Management tab opens. Enter the following details:
Option
Definition
Monitoring
Boot diagnostics - Trellix recommends you to select Disbale.
OS guest diagnostice - Trellix recommends you to select Off.
Identity
By default, the system assigned managed identity is Off.
Auto-shutdown
Trellix recommends you to select Off as the Virtual IPS Sensor should not be shutdown on a daily basis.
Click Next: Advanced >.
The Advanced tab opens. Enter the following details:
Option
Definition
Extensions
Installing external extensions is not supported on vIPS components.
Custom Data
Enter the Custom Data for the Virtual IPS Sensor in the following format:
{ "Primary Manager IP" : "IPS_PRIMARY_MANAGER_PRIVATE_IP", "Secondary Manager IP" : "IPS_SECONDARY_MANAGER_PRIVATE_IP", "Cluster Name" : "CLUSTER_NAME", "Sensor Shared Key" : "SHARED_KEY", "Traffic Source" : "GWLB" }Custom data parametersParameters
Description
Primary Manager IPPrivate IP address of the primary Manager
Secondary Manager IPPrivate IP address of the secondary Manager
Cluster NameName of the Cluster in the Manager
Sensor Shared KeyShared secret key to establish trust with the Sensor.
Traffic SourceType of traffic source used for traffic inspection.
Click Next: Tags >.
The Tags tab opens. On this tab, you can categorize resources by applying a tag name and value to multiple resources and resource groups.
Click Next: Review + create >.
The Review + create tab opens. Validate the summary details which contain all the parameters selected. Make sure the validation is successful.
Click Create.
The Virtual IPS Sensor virtual machine is created.
Tip
To view the Virtual IPS Sensor virtual machine, go to All services, under the Compute section, and click Virtual machines. You are directed to the Virtual machines page where you can view or delete the Virtual IPS Sensor virtual machine.
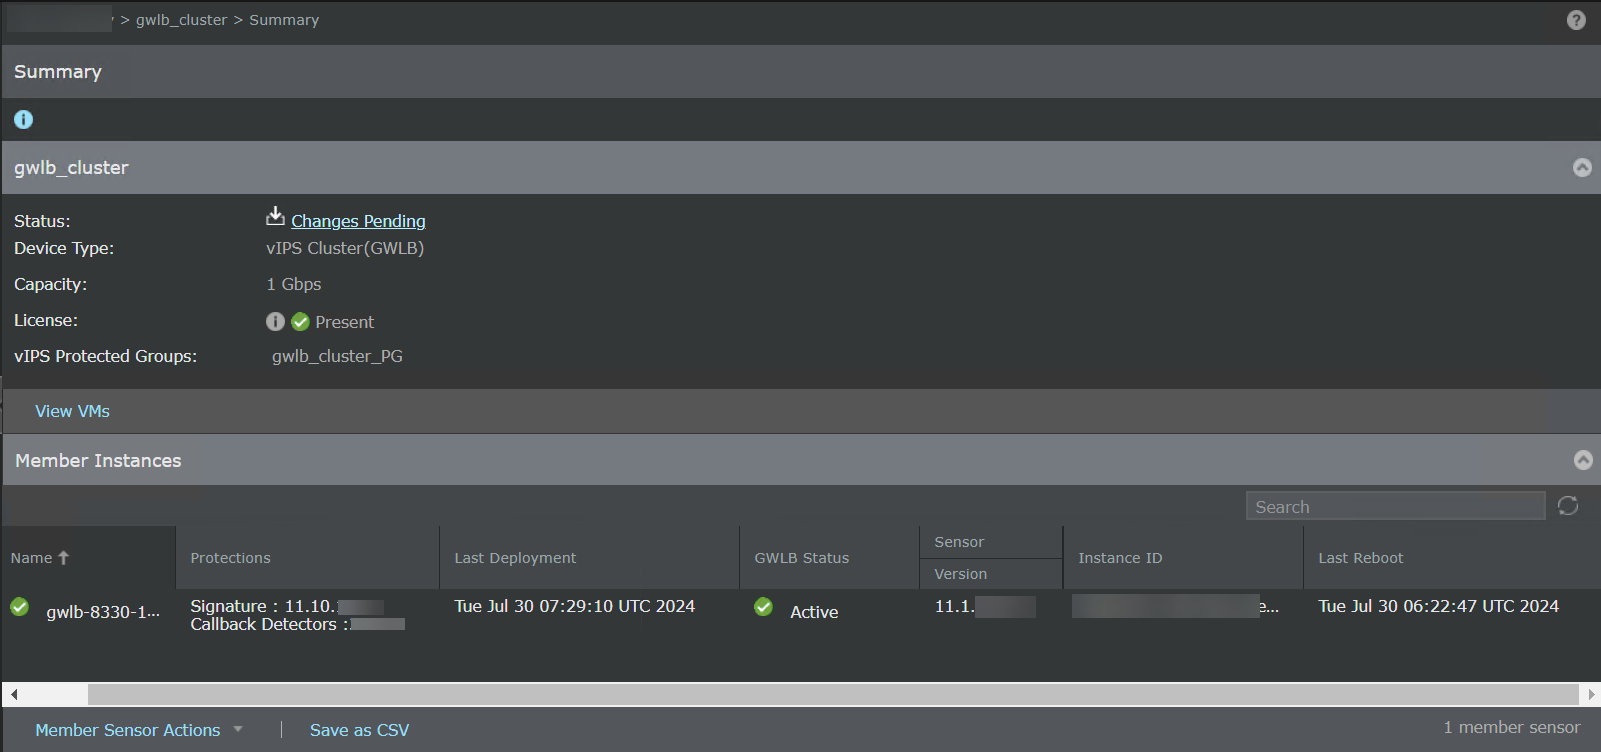
After the Virtual IPS Sensor is deployed, go to Devices → <Admin Domain Name> → Devices → <Device Name> → Summary page in the Manager to validate the successful deployment of the Virtual IPS Sensor.
If the Virtual IPS Sensor is deployed successfully, a green icon appears next to the Virtual IPS Sensor name.