When you create a Snort rule in the Custom Attack Editor or when you import Snort rules, the Custom Attack Editor checks if there is an equivalent Trellix IPS attack signature based on the CVE IDs. If a Trellix IPS attack signature exists, the corresponding Snort rule is referred to as a duplicate Snort custom attack or duplicate Snort rule. Such rules are imported into the Custom Attack Editor but staged in the policies by default when you save them. You can manually change the State of such rules to Published.
Alternatively, you can specify your preference in the Custom Attack Editor so that, going forward, the duplicate Snort custom attacks are published in the corresponding policies by default.
When you publish duplicate Snort custom attacks and enable alerting for the corresponding Trellix IPS signature as well, two alerts might be raised for the same attack traffic — one triggered by the Snort custom attack and the other by the Trellix IPS attack.
Steps:
In the Custom Attack Editor, click
 .
Select Check for Overlap with Trellix IPS Attacks.
Publish duplicate Snort custom attacks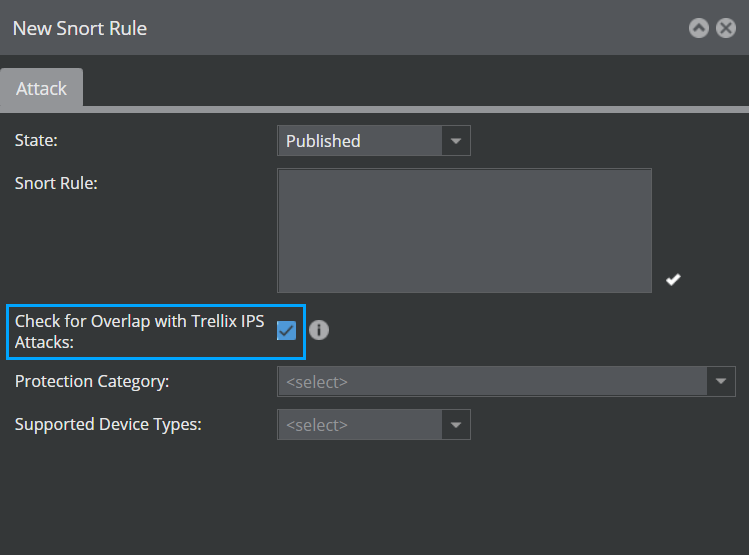
This selection applies only to the Snort custom attacks that you will create or import from now on and not to the already staged duplicate Snort custom attacks. You can only manually publish the previously staged duplicate Snort custom attacks by changing the State of the corresponding attack.
This feature compares only the CVE IDs in Snort rules with the CVE IDs in the Trellix IPS attack signatures.
The CVE ID that you mention in the Snort rule must be of the universal format for this feature to work.
Correct
Incorrect
reference:cve, 2010-0249;reference:cve, CVE-2010-0249;The rule is published even though there is an equivalent Trellix IPS signature because the Custom Attack Editor looked for CVE-2010-0249 instead of just 2010-0249.