Prerequisites:
Make sure of the following before you begin importing the conf file:
You have all the rules files containing the rules that you want to import.
The conf file has references to each rules file that you want to import. That is, the rules files are called from the config file using the include keyword and the absolute or relative path to the files. You can also use a variable to denote the path.
All the variables, classifications, and references used in the rules are either defined in the conf, or the rules files up front, or available already in the Manager.
Depending on how the rules have been constructed, the conf file may be referencing some files in addition to the rules files. Make sure all the files called by the conf file are in place.
Each rule must have a globally unique Snort rule ID (SID) for it to be converted and saved in the Manager database. A rule is not considered for import, if the SID and revision number are same as that of a rule imported earlier. If the SID is same but not the revision number, then the rule with the highest revision number is retained.
This section provides the steps for importing Snort rules into the Manager using a conf file.
Steps:
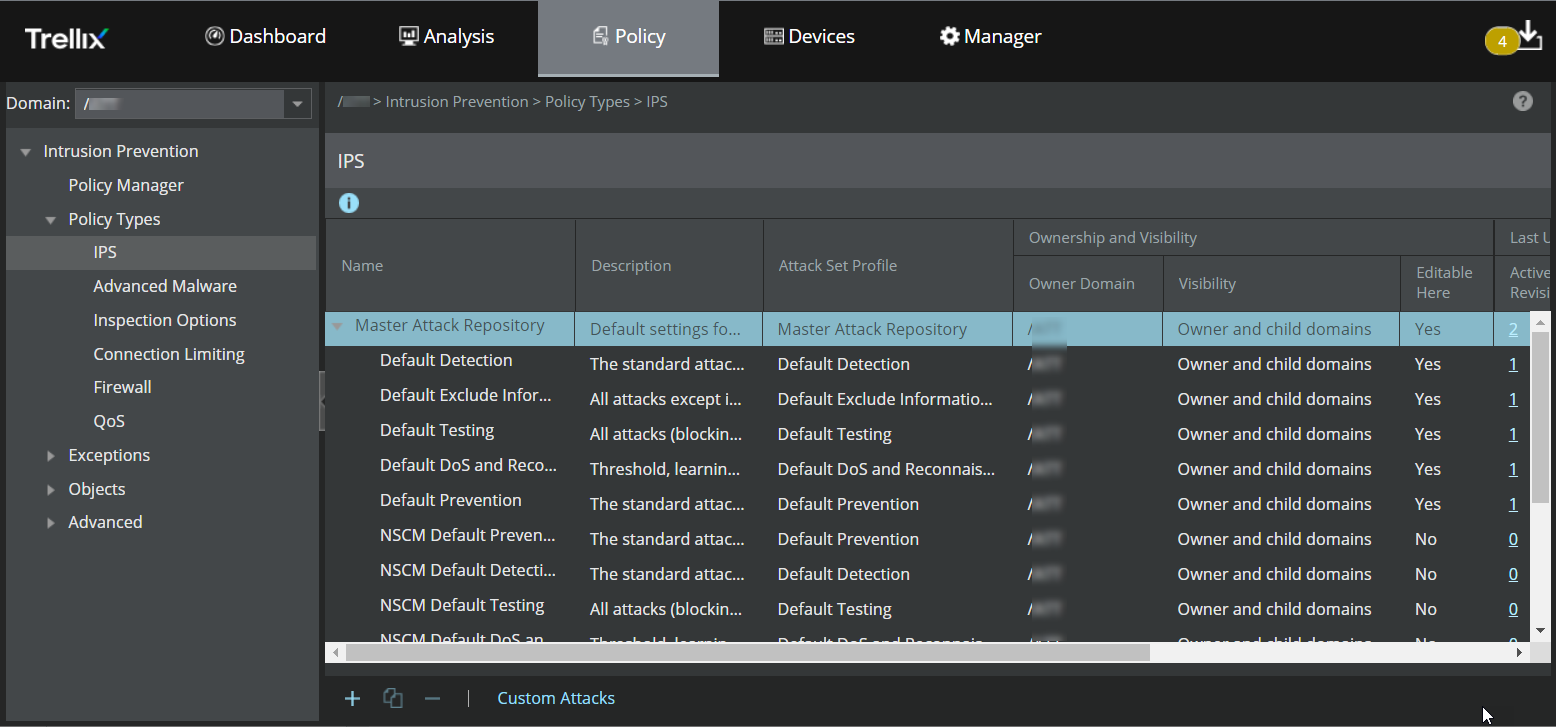
Select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS. Click Custom Attacks.
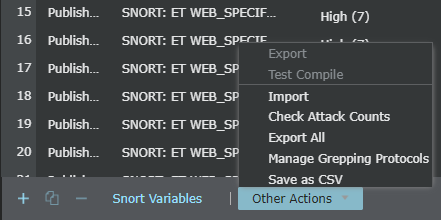
In the Custom Attack Editor of the Snort Format tab, click Other Actions → Import .
Navigate to the .conf file to be imported.
Click Open.
All the rules are imported into the Manager and the valid ones are converted to Trellix IPS's format. There could be some rules that were successfully converted to Trellix IPS's format, some converted with warnings, and some that failed to convert.
Select a Protection Category value.
Import rules window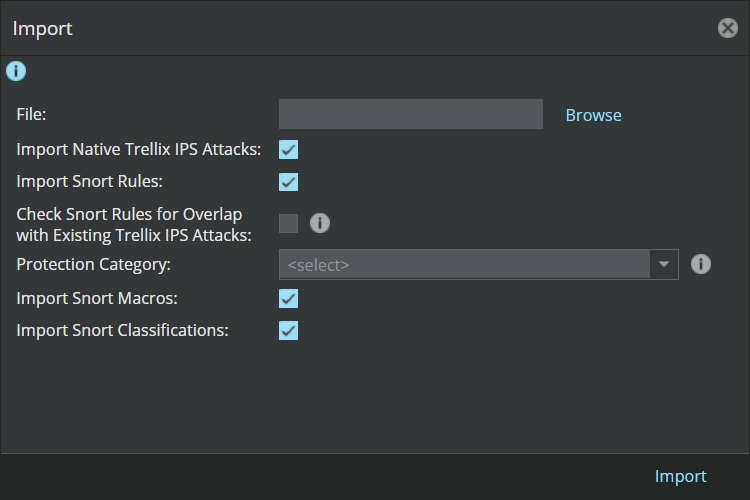
Click Import.
You can refer to the section Managing Snort rules to:
View the details of the imported Snort rules
Know which rules converted successfully, which converted with warnings, and which failed to convert