In the Custom Attack Editor (formerly UDS Editor), you create custom recon attacks using both user-defined exploit attacks and Trellix IPS-defined exploit attacks (in sigset) as component attack. You can also define correlated attacks using these individual attack definitions. For example, UDS attacks that check for URI can be further correlated to test for multiple occurrences in a defined time interval to raise a correlated alert.
To configure Custom Reconnaissance Attack Definition:
Steps:
Select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS. Click Custom Attacks.
The Custom Attack Editor opens with the existing Custom Attacks listed on the Native Trellix IPS Format tab.
Click
 .
The New Custom Attack interface opens.
In the Name field, type the new custom reconnaissance attack.
Note
The Trellix IPS ID is provided by the Manager when you save it in the Manager server.
Optionally, type a Description for your attack.
This area can be used for your notes or other specific information pertinent to your new attack.
Select a severity for your attack by toggling the drop-down list. Choices are High (9, 8, 7), Medium (6, 5, 4), Low (3, 2, 1), and Informational (0).
Select the most appropriate Protection Category for the attack.
Select Custom Reconnaissance Attack (Correlation-Based) from the Detection Type drop-down menu for the attack.
New Custom Attack window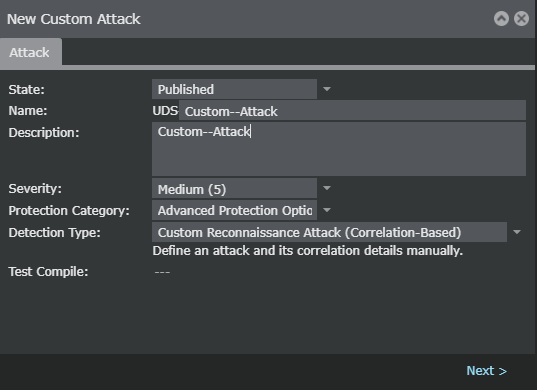
Click Next.
Set the Benign Trigger Probability (BTP) for the reconnaissance attack.
Set the Attack Subcategory from Correlation Logic for the attack.
The following subcategories are available:
brute-force
fingerprinting
host-sweep
port-scan
service-sweep
You can select the above options using a single component attack for correlation. Select fingerprinting option if you wish to use multiple component attacks for correlation.
In the Attack field, type the attack name and select the relevant attack from the list.
You can select either a Trellix IPS-defined exploit attack or a user-defined custom attack as a component attack.
Set the Threshold value between 1 and 255.
Set the Interval in seconds between 1 and 65535.
Select the Generate Individual Conponent Alerts check box.
Select either Protocol or Software Package (OS), and click Add.
You can add more than one matching criteria to your custom reconnaissance attack.
Add Protocols Packages page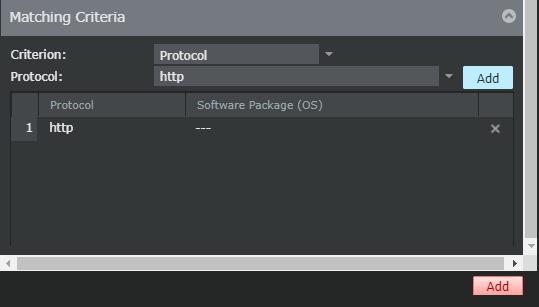
Click Add.
Review all the settings, and click Save.
When traffic passing through the Sensor exceeds the threshold count set for the custom reconnaissance attack within a configured Interval, the Sensor raises an alert to the Manager. You can view the alert in the Attack Log page. The alerts Summary shows the type of attack as either a Trellix IPS Exploit or Trellix IPS Reconnaissance.
Note
The custom reconnaissance attacks are staged by the IPS engine when:
One or more of its component attacks is deleted.
One or more of its component attacks is marked as Staged.