Create one or more signatures to detect an attack. This section assumes that you are adding signatures to the attack that you just created in the previous section. That is, the Add Trellix IPS Attack interface is open and the attack you created is yet to be saved in the Manager server. If you are adding signatures to a previously saved attack, double-click on the attack in a tabbed region to open the Edit Trellix IPS Attack interface.
Note
You can create up to 15 signatures per attack definition.
Steps:
In the New Custom Attack interface, click on the Signature-<signature name> tab.
The signature tab appears.
Optionally clear the Signature Name and type a new one.
Select a Benign Trigger Probability value.
New Signature window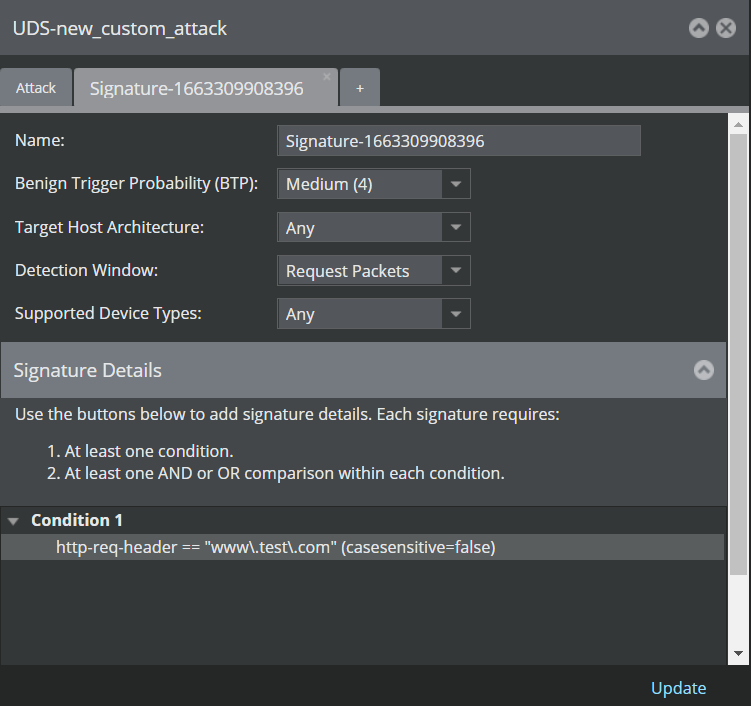
Select a Target Host Architecture. The default is Any.
Select a Detection Window. The choices are as follows:
Single Packet
Request Packets
Response Packets
Entire Flow
Based on the Sensor model that you plan to use you can select any of the following options:
NS-series Only
VM-series Only
Any
Under Signature Details panel, Condition 1 is added and selected by default.
To add another condition, do the following:
Click
 under Signature Details. [AND THEN] Condition 2 appears in the blank white field.
Click Condition 1 or [AND THEN] Condition 2 so that it is highlighted.
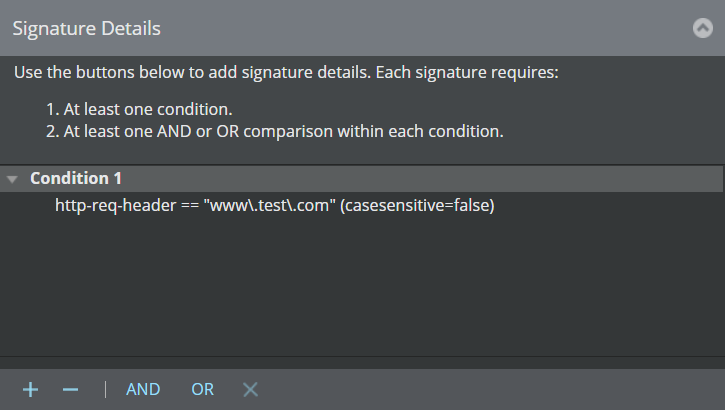
Do one of the following:
Click
 under Comparisons to add an AND comparison.
Click
 under Comparison to add OR comparisons.
Select a comparison type from the Comparison Type list. The choices are as follows:
String Pattern Match: The pattern contains a sequence of characters which will be used for detections. It can contain alphanumeric and hexadecimal sequence.
Numeric Value Match: The pattern contains only numeric values.
Numeric Range Match: The pattern contains only numeric values. You can configure a minimum and maximum value. These are used to detect numeric values which falls between minimum and maximum value.
Numeric Enumeration Match: The pattern contains only numeric values. The values may not be in any order but a sequence of numbers against which detection occurs.
Single Fixed Field Match: This contains mixed values. The input type varies based on the protocol and protocol field selected.
Packet Grep Protocol Match: This contains alphanumeric or hexadecimal as input and does not contain any regular expression. This will detect patterns in the selected protocol for either request or response. Select this option, only if the protocols are not listed in the String Pattern Match or if the requested Protocol field is missing from the String Pattern Match list.
Your selection affects what appears in the subsequent dialogs. The String Pattern Match option requires knowledge of the Regular Expression Language.
From the Protocol Details box, select a protocol from the Protocol list.
The subsequent options are based on the selected protocol.
Note
If you selected Packet Grep Protocol from the Comparison Type drop-down menu, the available protocols are those packet grep instances created/provided within the Protocol drop-down menu.
Configure the fields for the comparison(s) you have chosen.
Note
If selection fields (drop-down menus) are blank, then the protocol and comparison you have chosen cannot be used to create a signature condition; select another protocol and/or comparison combination.
For example, if you want to configure a string match in the URI path of an HTTP GET request:
Select http for the Protocol, req-uri-path for the Protocol Field and select get as the http-req-method.
Configure Comparison window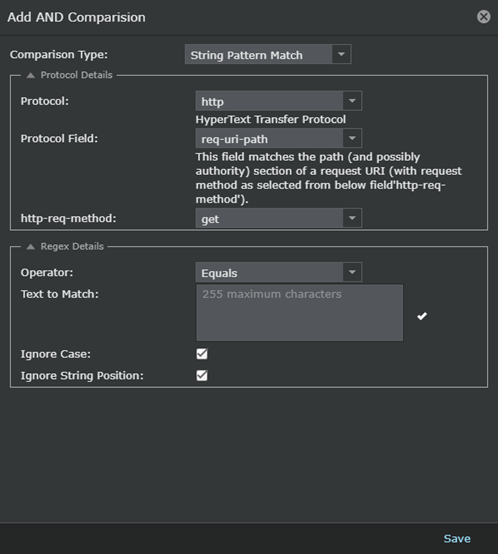
From the Operator drop-down list in the Regex Details section, select the matching criteria as Equals.
If you are configuring a string pattern match, type your pattern in Text to Match.
Optionally, click the Ignore Case check box if you want the pattern to be matched regardless of [letter] case.
Optionally, click the Ignore String Position check box if you want the pattern to be matched regardless of string position.
Click
 to verify that your pattern is valid.
Click Save when done with the Configure Comparison fields. Your comparison appears under Condition 1.
Do one of the following:
Click
to add another condition.Select Condition 1 and click AND under Comparisons to add another AND comparison.
Select Condition 1 and click OR under Comparisons to add multiple OR comparisons to your condition. Note that the first of the OR comparison appears under [AND](One Of).
(Optional) Do one of the following if you have created multiple conditions:
Select a condition and click
 under to delete a condition, or select a comparison and click to delete a comparison.
Optionally, you can add more signatures to your attack by clicking
next to the signature tab.Click Save in the Custom Attack interface.
The created Attack and its signatures are saved in the Manager client that you are logged on to.
Caution
If you close the Custom Attack Editor without saving the attack, the attack that you created (along with any unsaved changes to other attacks) is lost.