You can use the predefined template to create a Trellix IPS custom attack to detect TCP connection attempts from specific IP addresses.
Steps:
Select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS. Click Custom Attacks.
The Custom Attack Editor opens with the existing Custom Attacks listed on the Native Trellix IPS Format tab.
Click
 .
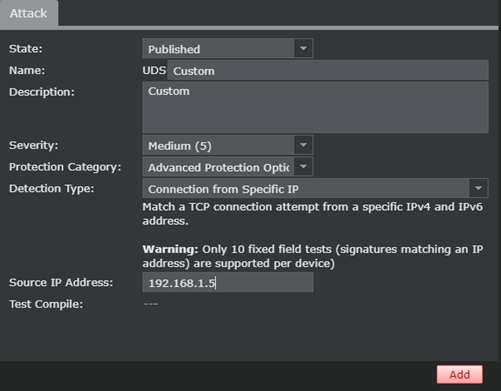
The New Custom Attack interface opens.
In the Name field, type a new name for your attack. UDS (User-Defined Signature) is appended at the front automatically when you save the attack. For example, if you name the new attack "HTTP Attack XYZ", it appears as "UDS-HTTP Attack XYZ" in the Custom Attack Editor as well as in the attack database when you save the attack.
Note
The Trellix IPS ID is provided by the Manager when you save it in the Manager server.
Type a Description for your attack.
This area can be used for your notes or other specific information pertinent to your new attack.
Select a severity for your attack by toggling the drop-down list. Choices are High (9, 8, 7), Medium (6, 5, 4), Low (3, 2, 1), and Informational (0).
Severity is set to Medium (5) by default.
Select the most appropriate Protection Category for the attack.
Select Connection from Specific IP from the Detection Type drop-down menu for the attack.
Enter the IPv4 or IPv6 Source IP Address from which TCP connection attempts are to be detected and click Add.
The attack is listed on the Native Trellix IPS Format tab.
Double-click on the attack that you created on the Native Trellix IPS Format tab.
In the Matching Criteria section, the Software Package (OS) is selected as tcpip-machine.
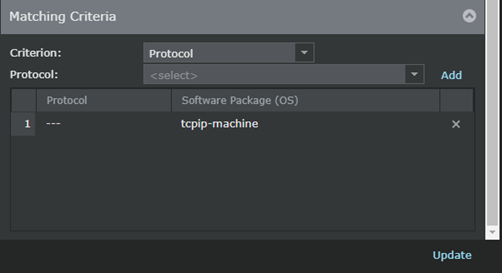
You can modify the values of the signature on the Signature-<signature name> tab. You can also add more conditions to the signature. For example, do the following to add conditions based on TCP flags:
Add a signature or edit a signature.
In the corresponding signature, click
.Add a condition by clicking
 or
 .
From Comparison Type list, select Single Fixed Field Match.
Select tcp from the Protocol drop-down menu.
Select the required flag from the Protocol Field.
Select the Operator.
Enter the value to match in the Integer or IP to Match field.
Select Ignore Bitmask if you want to ignore the bitmask.
Click Save.
Click Save in the Custom Attack interface.
Until you save the attack in the database, value for the Trellix IPS ID column is not generated. The Sensor detects this attack after you deploy pending changes to the corresponding Sensor (Devices → <Admin Domain Name> → Global → Device Manager. Select the Sensors tab. Then, select the required Sensor from list and click Sync).