This section explains how to create Trellix IPS Exploit Attacks and the constituent signatures.
To create a Trellix IPS Exploit Attack instance, you start by first adding a new attack. Attacks are configured first because signatures logically relate to attacks as one particular means of detection.
Attack creation includes impact categorization for proper policy integration and enforcement. Each policy — those provided with Trellix IPS and those you create — consists of rule sets, which contain multiple categories of attacks. Attacks are categorized by the protocols, operating systems, and applications they impact. Within the Custom Attack Editor, you define the impact categories wherein your attack definition best fits, so that when you save it in the Manager, it will be published in one or more rule sets.
Steps:
Select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS. Click Custom Attacks.
The Custom Attack Editor opens with the existing Custom Attacks listed on the Native Trellix IPS Format tab.
Click
 .
The New Custom Attack interface opens.
Add Exploit Attack window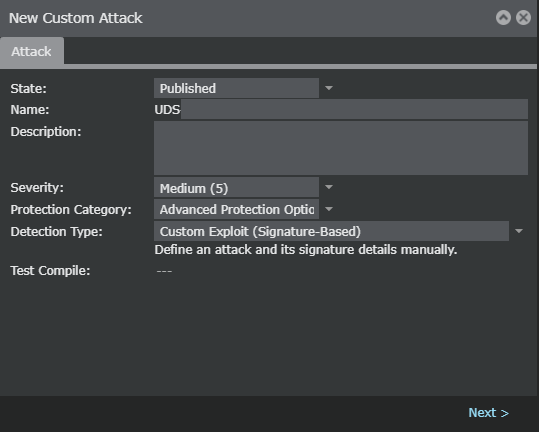
In the Name field, type a new name for your attack. UDS (User-Defined Signature) is appended at the front automatically when you save the attack. For example, if you name the new attack "HTTP Attack XYZ", it appears as "UDS-HTTP Attack XYZ" in the Custom Attack Editor as well as in the attack database when you save the attack.
Note
The Trellix IPS ID is provided by the Manager when you save it in the Manager server.
Type a Description for your attack.
This area can be used for your notes or other specific information pertinent to your new attack.
Select a severity for your attack by toggling the drop-down list. Choices are High (9, 8, 7), Medium (6, 5, 4), Low (3, 2, 1), and Informational (0).
Select the most appropriate Protection Category for the attack.
Select Custom Exploit (Signature-Based) from the Detection Type drop-down menu for the attack.
Click Next.
Select an appropriate Attack Target.
Select an appropriate Blocking type.
On the Matching Criteria tab:
Complete at least one of the following:
Categorize the attack definition by protocol. For example: HTTP, FTP, DNS. In the Criterion dialog box, select Protocol and then select a protocol from the Protocol list.
Categorize by software package (that is, application and operating system). For example: Internet Explorer on Windows 2003. In the Criterion dialog, select Software Package (OS) and then select one package from the list. Optionally, select an Operating System.
Click Add.
Repeat steps to specify more protocols or packages.
Note
It is mandatory that you specify at least one impact package or protocol. If you are not sure about the impact package or protocol, select tcpip-machine as the impact package.
Tip
Check the rule sets (Inbound and Outbound) of the policy you plan to enforce to determine whether your attack will be selected. You also have the option of creating a new rule set in order to enforce your Custom Attack.
Once your attack configuration is complete, continue to Creating a Signature.