At the interface and subinterface levels, the DoS attack definitions are inherited from the IPS policy applied at the Sensor level. This includes the DoS learning attack definitions as well as the DoS threshold attack definitions. Any customization in the assigned IPS policy applies automatically at the interface and subinterface levels. You can further customize these attack definitions in the Interface-Specific Customization section exclusively for the interface or subinterface. Just like any other customization in an IPS policy, these are applicable only to that interface or subinterface. Also, note that the customization done at an interface is not inherited by the corresponding subinterfaces, unlike the customization at the Sensor, which are inherited at the interfaces and subinterfaces.
The process of customizing attack definitions at interfaces and subinterfaces are similar.
Click the Policy tab.
Select the domain from the Domain drop-down list.
Navigate to Intrusion Prevention → Policy Manager
Double-click the interface to which you would like to customize the DoS learning attack.
The <Device Name/Interface> panel opens on the right side.
Under the IPS section, you can view the applied IPS policy.
The applied IPS policy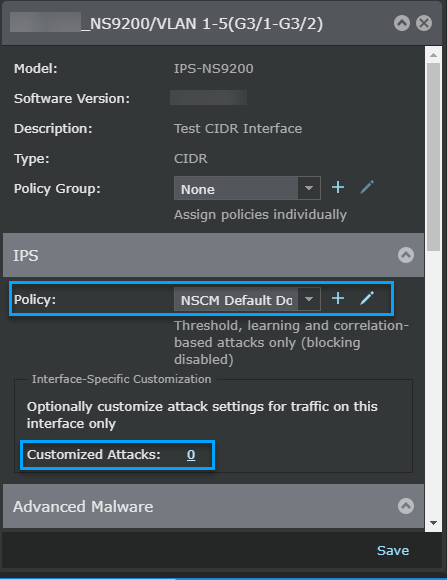
Click on "0" next to the Customized Attacks field under Interface-Specific Customization.
The Attack Definitions window opens.
Select the filter from the Attack Category column to view the DOS Learning Attack or DOS Threshold Attack based on the DoS attacks that you want to customize.
Number of attack definitions by Attack Categories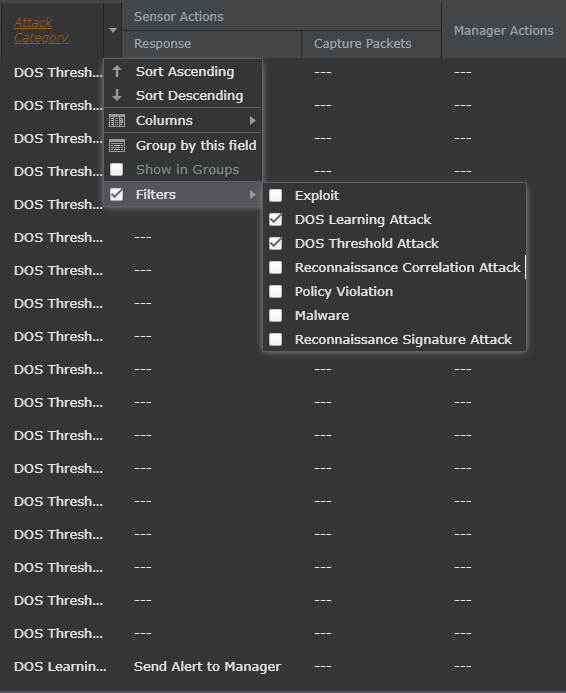
The attack definitions belonging to the DoS attack category you selected are listed. This includes inbound, outbound, and bidirectional attack definitions.
Note
DOS Learning Attack and DOS Threshold Attack are the categories that correspond to DoS attack definitions.
Double-click on the attack that you want to customize. The <Attack Name> panel opens on the right side.
You can also select multiple attacks by using the Ctrl key to select multiple attacks. For the sake of explanation, assume that you are customizing a single attack.
Customize the DoS attack definition on the Settings tab of the <Attack Name> panel.
Click Update.
After you have customized all the required attack definitions, click Save.
A Save Confirmation dialog opens. Click Confirm to save the changes. Click the "x" icon to exit the window without saving the changes.
Click the Save button in the <Device Name/Interface> panel to save all the changes.
The Customized Attacks field shows the integer value of the number of attacks customized for that policy.
In the <Device Name/Interface> panel, you have the following options:
 (merge) — Merges the customized policy with the assigned IPS policy. After a successful merge, the Customized Attacks field shows the integer value as "0".
 (delete) — Deletes any customized attacks before it is merged with the assigned IPS policy.
Customized attacks merge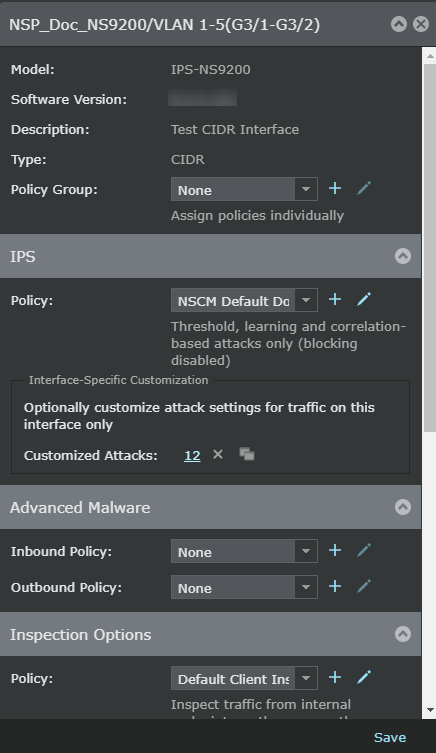
Deploy the configuration changes to the required Sensors for the changes to take effect.