This section lists issues related to DoS alerts.
Applicable to Sensor models: NS-series
Problem scenario
DoS alerts raised in Trellix IPS Manager.
Data/Information Collection
Execute
show dospreventionprofile <dos-measure-name> <inbound/outbound>in the Sensor.Trace the Sensor files.
Troubleshooting Steps
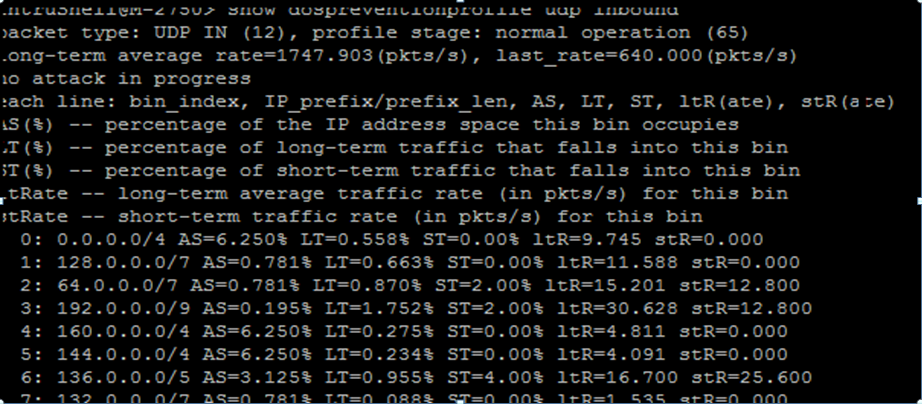
Check for the source IP of the profile learning each of the packet types. Execute the following commands:
show dospreventionprofile tcp-syn inbound/outboundshow dospreventionprofile tcp-syn-ack inbound/outboundshow dospreventionprofile tcp-rst inbound/outboundshow dospreventionprofile udp inbound/outboundshow dospreventionprofile icmp-echo inbound/outboundshow dospreventionprofile icmp-echo-reply inbound/outboundshow dospreventionprofile icmp-non-echo-echoreply inbound/outboundshow dospreventionprofile ip-fragment inbound/outboundshow dospreventionprofile non-tcp-udp-icmp inbound/outbound
Check the bins for long-term average traffic rate and short-term average traffic rate values. An alert is raised when the short-term traffic rate is higher than the long-term traffic rate.
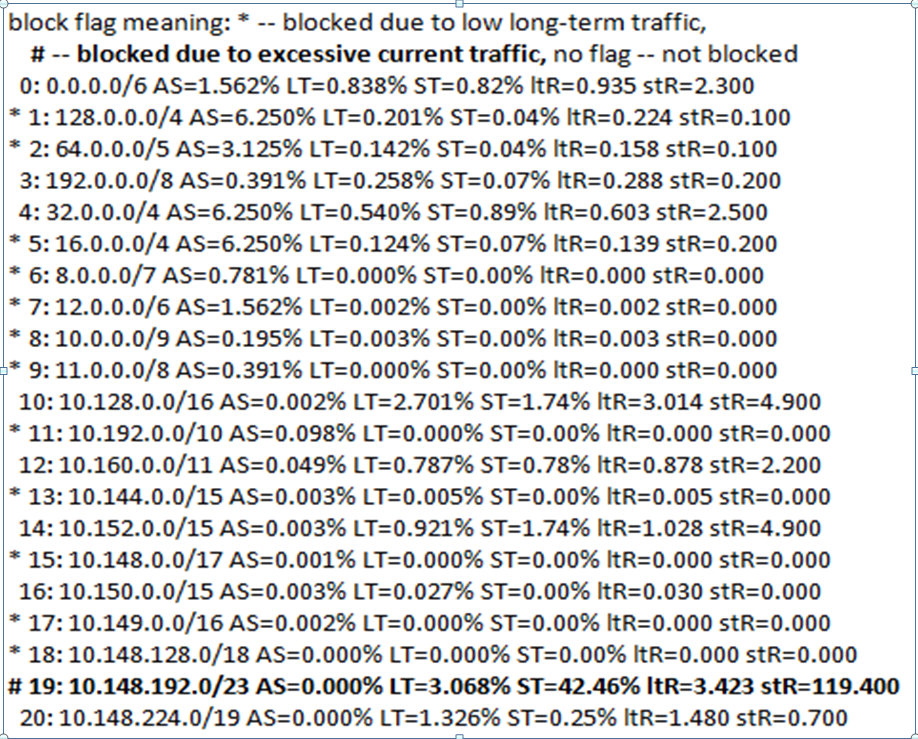
Check bins that are blocked. A sample of the source IP profile during the detection stage which indicates the blocked bins is shown in the figure.
If many DoS alerts are raised frequently for a particular IP, it could be false positive. The reason could be due to the profile of that IP not studied properly.
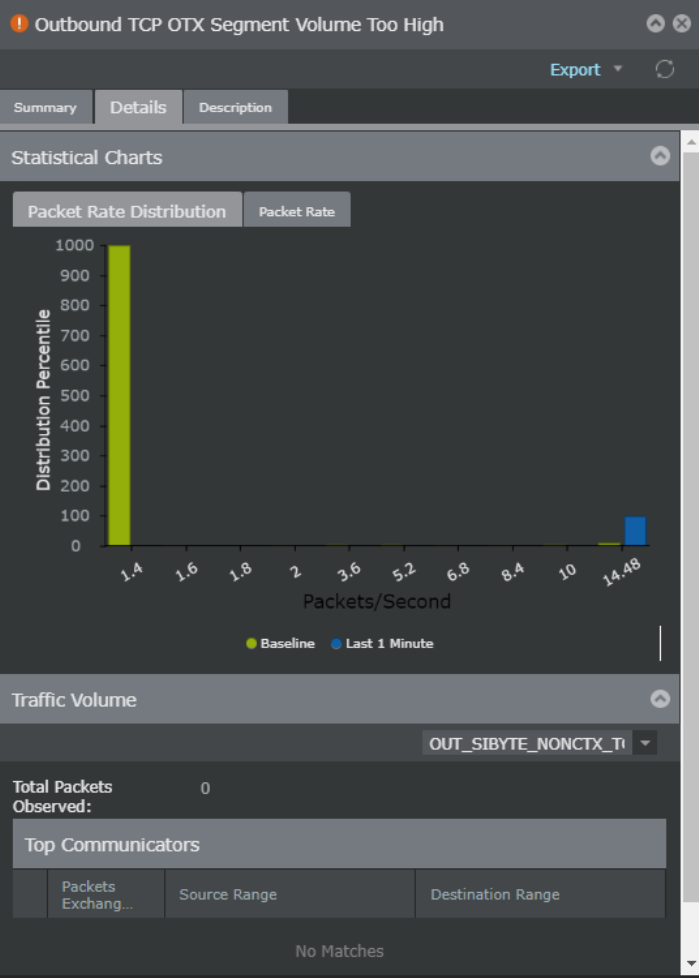
For volume related alerts (for example, if the inbound UDP volume is too high), check if the IP is missing in the alert details. To check the alert details, navigate to Analysis → <Admin Domain Name> → Attack Log and select the alert by clicking on it twice.
Solution
Rebuild the DoS profile to resolve the issue. To rebuild the DoS profile, perform the following steps:
Click Devices → <Domain Name> → Devices → <Device Name> → Troubleshooting → Denial of Service → Data Management.
In the DoS Profile Learning section, select Rebuild the DoS Profiles.
Click Update.