Validation errors while importing the CA-signed certificate chain
This section lists the validation errors that may appear while importing the CA-signed certificate chain.
Error | Description | Solution |
|---|---|---|
Invalid CA Certificate Chain with Client Certificate | Client certificate is invalid in the certificate chain. | Request for a certificate chain from the CA with a valid client certificate. |
Validity Expired for the certificate provided | Validity period for the certificate has expired. | Request for a certificate chain from the CA with the validity period set to a future date. |
Signature Algo NOT SHA256withRSA | Signature algorithm used in the certificate chain is not SHA256 with RSA 2048 bit encryption. | Request for a certificate chain from the CA sine with SHA256 with RSA 2048 bit encryption. |
Invalid Serial Number in Certificate | Invalid serial number present in the certificate chain. | Request for a certificate chain from the CA with a valid serial number. |
Certificate Issuer Not Present | Certificate issuer name is not present in the certificate chain. | Request for a certificate chain from the CA with a valid issuer name. |
Some Certificate or Key file missing in import | Files missing in the certificate chain. | Request for the complete certificate chain from the CA. |
Signing issue. Verification failed for root with leaf certs | Signature issue with the root and leaf certificates. | Request for a certificate chain from the CA with a valid signature. |
Certificate Algorithm is not RSA or more | Signature algorithm used in the certificate chain is not using RSA encryption. | Request for a certificate chain encrypted using RSA from the CA. |
Certificate Key size is not 2048 or more | Certificate public key size is not 2048 bit. | Request for a certificate chain with public key having 2048 bit from the CA. |
Total certificates in chain should be at least 2 and maximum 6 | Total number of certificates in the chain is not between 2 and 6. | Request for a certificate chain from the CA with correct number of certificates. |
Certificate basic constraints are missing | Basic Constraints flag is missing in the certificate chain. | Request for a certificate chain from the CA with valid Basic Constraints flags. |
Leaf Certificate Extended Keys are either invalid or missing | Extended Keys parameters are invalid or missing in the certificate. | Request for a certificate chain from the CA with valid Extended Keys parameters. |
Leaf Certificate Extended keys are not valid for client | Extended Keys parameters are invalid in the certificate for the client. | Request for a certificate chain from the CA with valid Extended Keys parameters. |
Leaf Certificate Extended keys are not valid for server | Extended Keys parameters are invalid in the certificate for the server. | Request for a certificate chain from the CA with valid Extended Keys parameters. |
Certificate Chain Root CA not present | Root certificate is missing in the certificate chain. | Request for the complete certificate chain from the CA. |
Troubleshooting scenarios
This section lists some troubleshooting tips for migrating Manager and Sensor from self-signed to CA-signed certificate.
Remove Manager CA-signed certificate when the Sensor is offline indefinitely
If a Sensor is offline indefinitely, remove the device from the Manager. Once the device is removed successfully, ensure that all the devices connected to the Manager are using self-signed certificate. You can then remove the CA-signed certificate chain from the Manager.
For steps to remove the CA-signed certificate chain from the Manager, see the Manager Administration section.
Remove Manager CA-signed certificate when the Sensor is offline temporarily
If a Sensor is offline temporarily, wait for the device to come online. Once the device is online, change the active certificate to self-signed. Ensure that all the devices connected to the Manager are using self-signed certificate. You can then remove the CA-signed certificate chain from the Manager.
For steps to remove the CA-signed certificate chain from the Manager, see the Manager Administration section.
Import CA-signed certificate to a Manager
To import a new CA-signed certificate to the Manager which already has a CA-signed certificate, change the active certificate of all the Sensors connected to the Manager to self-signed certificate. You can then import the new CA-signed certificate to the Manager.
For steps to import the CA-signed certificate chain to the Manager, see the Manager Administration section.
Import a new CA-signed certificate to a Sensor
To import a new CA-signed certificate to the Sensor which already has a CA-signed certificate, first you have to change the active certificate of the Sensor to self-signed. You can then import the new CA-signed certificate to the Sensor.
For steps to import the CA-signed certificate chain to the Manager, see the Manager Administration section.
Manager CA-signed certificate validation fails during Sensor trust establishment
Check the system faults in the Manager to see the reason for failure. Go to Manager → <Admin Domain Name> → Troubleshooting → Logs to see the system faults.
If it is a certificate error, correct the error in the certificate and replace the certificate in the Manager.
Establish trust with Manager using one of the methods:
If self-signed certificate is present in the Sensor:
Change the active to the self-signed certificate for the Sensor from the Manager.
For steps to change active certificate, see the Manager Administration section.
Run the
deinstallcommand while retaining the CA-signed certificate.Run the
set sensor sharedsecretkeycommand to establish trust with the Manager.
If the trust is not established, run the
set sensor sharedsecretkeycommand to establish trust with the Manager using a self-signed certificate.
Sensor CA-signed certificate validation fails during trust establishment with the Manager
Check the system faults in the Manager to see the reason for failure. Go to Manager → <Admin Domain Name> → Troubleshooting → Logs to see the system faults.
If a self-signed certificate is present in the Sensor, run the
deinstallcommand without retaining the CA-signed certificate.If the trust is still not established, run the
resetconfigcommand without retaining the CA-signed certificate.Run the
set sensor sharedsecretkeycommand to reestablish trust with the Manager using self-signed certificate.Import the corrected CA-signed certificate from the Manager to Sensor.
Change the active certificate for the Sensor in the Manager from self-signed to CA signed.
For steps to change the active certificate, see the Manager Administration section.
Sensor certificate import fails due to unavailability of Manager CA certificates
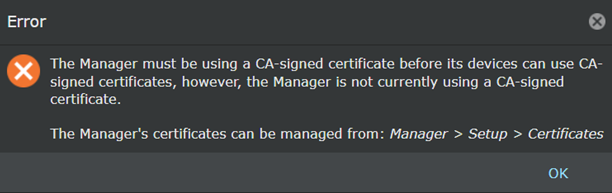
Error: The Manager must be using a CA-signed certificate before its devices can use CA-signed certificates, however, the Manager is not currently using a CA-signed certificate.
The Manager's certificates can be managed from Manager → Setup → Certificates.
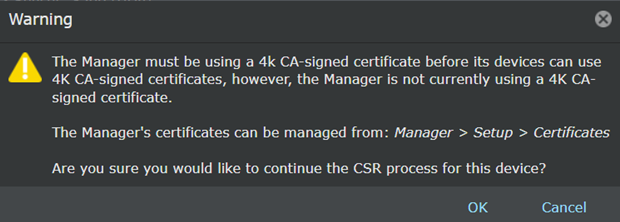
Warning: The Manager must be using a 4k CA-signed certificate before its devices can use 4K CA-signed certificates, however, the Manager is not currently using a 4K CA-signed certificate.
The Manager's certificates can be managed from Manager → Setup → Certificates.
Are you sure you would like to continue the CSR process for this device?
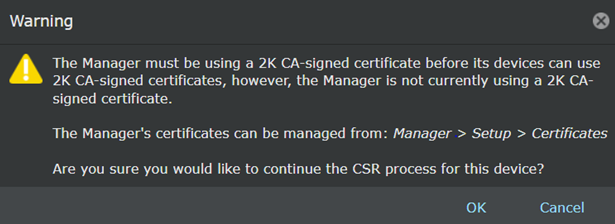
Warning: The Manager must be using a 2K CA-signed certificate before its devices can use 2K CA-signed certificates, however, the Manager is not currently using a 2K CA-signed certificate
The Manager's certificates can be managed from Manager → Setup → Certificates.
Are you sure you would like to continue the CSR process for this device?
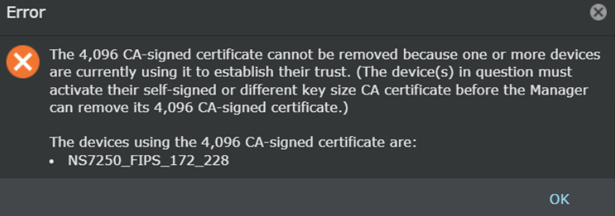
Error: The 4,096 CA-signed certificate cannot be removed because one or more devices are currently using it to establish their trust. (The device(s) in question must activate their self-signed or different key size CA certificate before the Manager can remove its 4,096 CA-signed certificate.)
The devices using the 4,096 CA-signed certificate are:
<Certificate_Name>
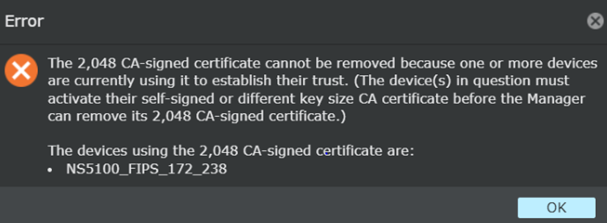
Error: The 2,048 CA-signed certificate cannot be removed because one or more devices are currently using it to establish their trust. (The device(s) in question must activate their self-signed or different key size CA certificate before the Manager can remove its 2,048 CA-signed certificate.)
The devices using the 2,048 CA-signed certificate are:
<Certificate_Name>
Trust establishment fails due to Sensor errors
Migration of Manager-Sensor trust establishment from self-signed to CA-signed certificate may be caused due to one of the following issues:
Control channel process restarts
Sensor reboots or autorecovers
Sensor loses connectivity with the Manager
Network connectivity issue
In case of any issue, perform the following steps:
Initiate Manager-Sensor trust once the Sensor autorecovery is complete.
If the self-signed certificate is present in the Sensor, change the active certificate to self-signed certificate for the Sensor from the Manager.
For steps to change the active certificate, see the Manager Administration section.
Run the
deinstallcommand while retaining the CA-signed certificate.Run the
set sensor sharedsecretkeycommand to reestablish trust with the Manager.If the trust is not established, run the
set sensor sharedsecretkeycommand to reestablish trust with the Manager using the self-signed certificate.