Prerequisite: Make sure that for the port-pairs for which you need to enable Anti-spoofing feature, their Mode is set to inline and their Interface Type is set to CIDR.
Click the Devices tab.
Select the domain from the Domain drop-down list.
On the left pane, click the Devices tab.
Select the device from the Device drop-down list.
Select Setup → Advanced → Anti-Spoofing.
The Anti-Spoofing page displays. Note that the tabs relate to the interfaces on the Sensor.
For the required port-pairs, enable Anti-Spoofing in the required directions - inbound, outbound, or both.
You can only enable IP spoofing detection for port-pairs in inline mode with CIDR interface types. CIDR entries must be previously configured for IP spoofing detection to function properly. You can enable Anti-spoofing at the interface level; you cannot enable it for specific CIDR subinterfaces.
Note
You can click an interface name to view the CIDRs configured for that interface.
Configuring Anti-spoofing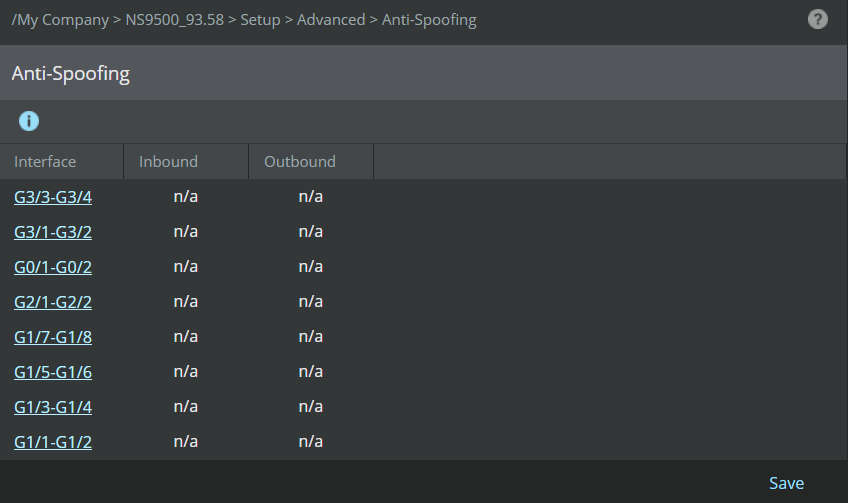
Click Save to enable IP spoofing detection.
Once you click Save, the configuration is sent through SNMP to the Sensor; thus, you do not have to update the configuration changes to the Sensor.
Note
When you enable Anti-spoofing, a Sensor drops any IP-spoofed packets but raises no alert. You can view a list of dropped packets by clicking on the Dropped Packets tab in Devices → <Admin Domain Name> → Devices → <Device Name> → Troubleshooting → Traffic Statistics. Once in the tab, select the port for which you want to see the list and count of dropped packets.
Alternatively, you can use the
show inlinepktdropstatSensor CLI command to view the number of IP-spoofed packets dropped by a Sensor. For information on using this CLI, refer to the CLI commands section.