Attackers sometimes attempt to modify the extension of the file in order to avoid detection. Certain file types which are subject to a more thorough analysis, because of the nature of the content that they hold, have their extensions changed in order to mislead firewalls or conventional security systems from analyzing or blocking them. Once such a file is in the network, it can perform various actions such as contacting a bot server or attaching itself to documents in order to proliferate across a network. A common example is when an executable file is sent with an extension of .sys, but when analyzed, contains a content type value as plain text.
The Sensor is equipped with a specific signature and an underlying mechanism to be able to detect such evasion attempts. When a file appears, the Sensor first extracts the magic number for the file type. Every file type has a magic number that is unique to itself. The Sensor extracts this data and does not rely only on the extension provided in the file name. This method of detection also works when no file extension is provided. The Sensor check the magic number and content type.
Note
Magic numbers are not extracted for JAR, APK, and ZIP files since the Sensor cannot differentiate among these three files.
When the Sensor has extracted the magic number, it is able to distinguish between files whose extensions are genuine and those of which have been tampered. If the extension has been tampered with, the Sensor raises a MALWARE: File Mismatch Detected alert in the Attack Log. To use this feature, you must confirm that the attack definition, MALWARE: File Mismatch Detected, is enabled. It is enabled by default.
Note
This feature is separate from advanced malware policies and requires no additional configuration for a fresh installation. It is available by default.
File types scanned
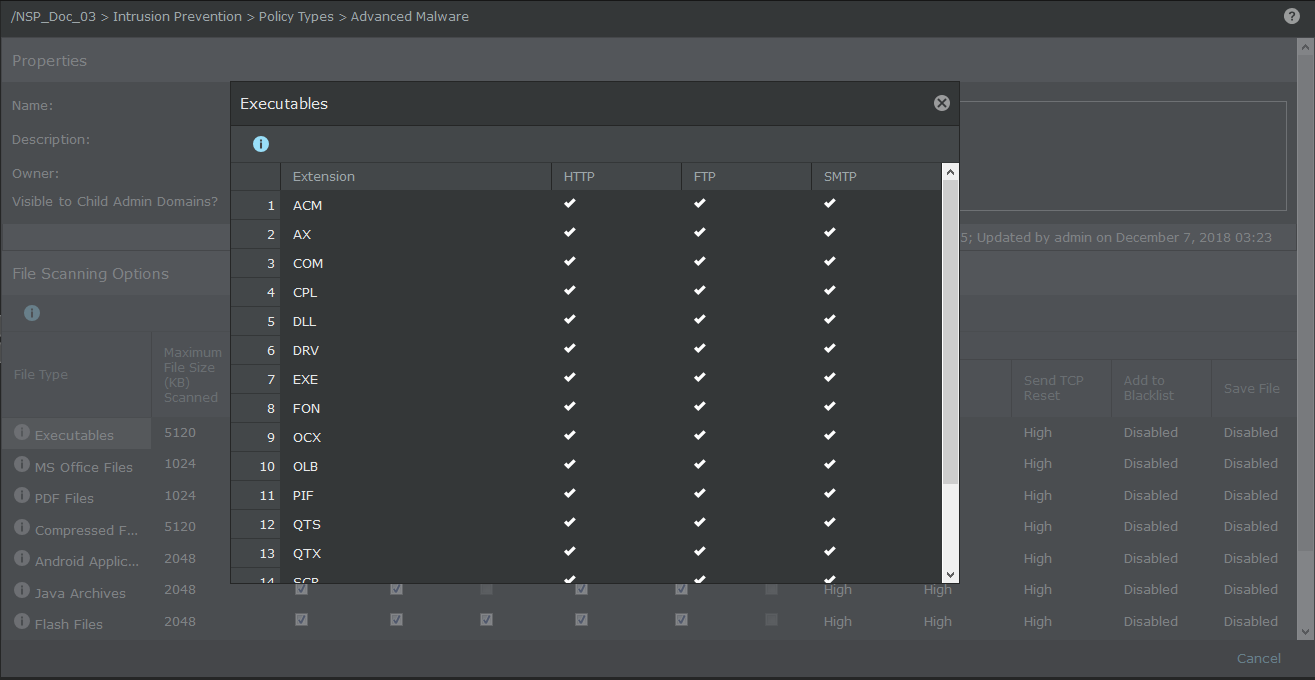
You can view the file types scanned by clicking on the info icon for a given file type under Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → Advanced Malware.
The following image shows the file types scanned for the Executables file type.