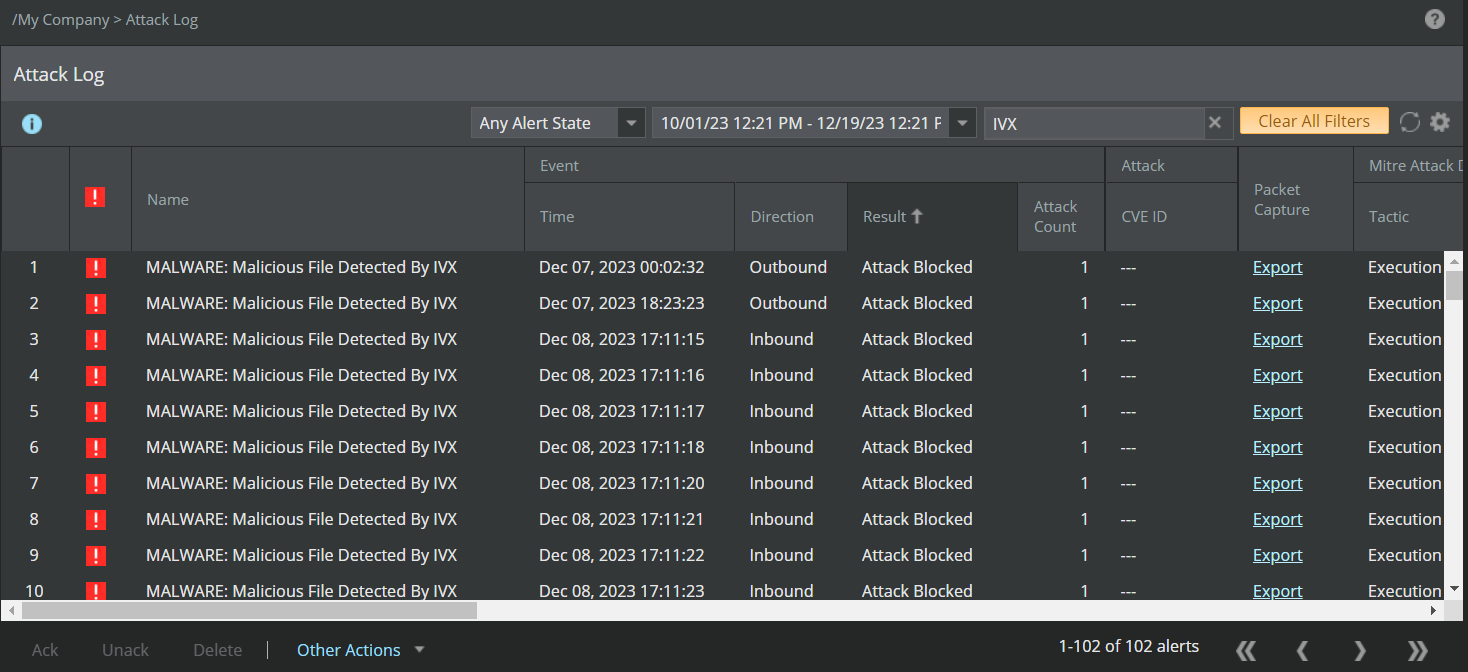
The volume of alerts generated in the Attack Log makes it difficult for the analysis of alerts. The different sorting and filtering options provided in the Attack Log helps drill-down only the necessary alerts for further analysis. Use the arrow keys at the bottom of the page to navigate back and forth between the alert pages.
Sort alerts
Alerts when generated are in unacknowledged state. Once an alert is acknowledged, a tick mark appears next to the alert in the acknowledged and unacknowledged column. You can sort the alerts by selecting any one of the three options, Unacknowledged, Acknowledged and Any Alert State. You can also sort the alerts based on the period in which the alerts were generated. The Custom Time Period option lets you customize the time period.
When the time period option is selected, the display shows the alert, attack counts, and other parameters for the chosen time period. The alert count displays the number of times each attack has been reported within the parameters. For example, for a query, there are two reported alerts (number of alerts = 2) and two reported attacks (attack count = 2) for the "ARP: ARP Spoofing Detected" attack. Thus, the "ARP: ARP Spoofing Detected" attack was detected and reported exactly twice during the queried period. Also, the number of alerts and attack count for the "Samba Trans2Open Buffer Overflow" attack: 74 alerts have been generated for this attack; however, there were 2133 attack instances. One or more attack instances was suppressed according to the configuration set.
When looking for a particular alert, you can enter the keyword for the alert in the Quick Search field and the results are automatically displayed in the log. Click Clear All Filters to undo all the filters applied.
The Clear All Filters button color changes to orange which indicates that a filter is active, and that the attack log is not displaying all the alerts. For example, if you want to filter the alerts detected by IVX engine, type ivx or IVX in the Quick Search field. The Clear All Filters button color changes to orange and the Manager filters IVX specific alerts.
Filter alerts
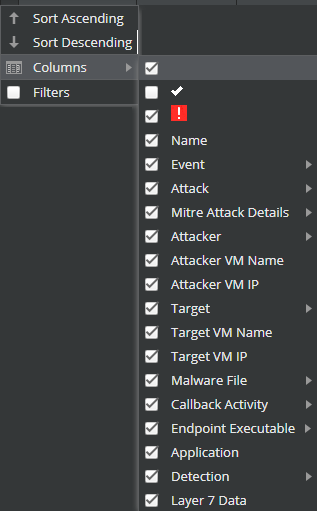
You can customize the columns in the Attack Log to view only the necessary details about the alert. You can rearrange/resize the columns to view the details according to your preference. Following are the column options for the alerts:
Column header | Description |
|---|
Acknowledged/unacknowledged alerts | The tick mark indicates that the alert is acknowledged. |
Attack Severity | Indicates different colors based on the attack severity, high/medium/low/informational |
Name | Name of the attack |
Event | Displays various information about the attack Time — Time at which the attack occurred Direction — Transmission destination with regard to internal network (inbound or outbound) Result — Result of the alerted attack The Result categories for alerted attacks are as follows: Attack Successful — The attack was successful. Inconclusive — The result of the attack is not known. This is most likely due to a generic policy, such as the Default or All-Inclusive policy where the policy rules are not environment specific. For example, this may be the result if an attack occurs against an irrelevant node. Attack Failed — The attack had no impact. n/a — The alert was raised for suspicious, but not necessarily malicious, traffic. This result is common for Reconnaissance attacks due to the nature of port scanning and endpoint sweeping. Attack Blocked — Attacks blocked by a "Drop packets" Sensor response Attack SmartBlocked — Attacks blocked by a "Drop packets" Sensor response as per GTI reputation response DoS Blocking Activated — Applies to DoS traffic and indicates that the Sensor has identified traffic that is suspicious in nature that is exceeding its learned threshold or is not recognized based on its profile. The Sensor has started blocking unknown traffic, while attempting (on a packet-by-packet basis) to block only DoS traffic from a trusted source. The Sensor attempts to allow legitimate traffic to flow from the trusted source. Because of the nature of DoS attacks, one cannot be certain that 100% of bad traffic was blocked nor that 100% of 'good' traffic was permitted. For more in-depth description of Trellix IPS's DoS handling, see Denial-of-Service attacks.
The following is the alert result status when Simulated Blocking is enabled. Blocking Simulated (Attack Failed) — The attack had no impact. Blocking Simulated (Attack Blocked) — An alert is raised for the attack that had potential impact. Blocking Simulated (Attack Successful) — The attack was successful. Blocking Simulated (Inconclusive) — The result of the attack is not known. This is most likely due to a generic policy, such as the Default or All-Inclusive policy where the policy rules are not environment specific. For example, this may be the result if an attack occurs against an irrelevant node. Blocking Simulated (n/a) — The alert was raised for suspicious, but not necessarily malicious, traffic. This result is common for Reconnaissance attacks due to the nature of port scanning and endpoint sweeping. Blocking Simulated (Attack SmartBlocked) — An alert is raised for the attack that had potential impact as per GTI reputation response.
Attack Count — Number of instances of the same attack Relevance — Indicates if the endpoint is vulnerable to this particular attack Matched Threat Feed — The name of the threat feed which includes the matching IoC detected in the alert. Alert ID — ID assigned to the alert Assigned to — Displays the name of the user if the attack is assigned
|
Attack | Displays specific information about the attack Trellix IPS ID — ID of the Sensor from where the alert was generated CVE ID — CVE ID of an attack that has been identified in the network and captured by the Sensor The CVE ID is displayed only for those attacks present in the signature set that have a valid CVE ID assigned to them.
In case you are performing a fresh installation of Trellix IPS Manager, the CVE ID column in the Attack Log page displays CVE IDs for all the alerts that have valid CVE IDs assigned to them in the signature set. In case you are upgrading the Manager to version 10.1.7.44 from versions prior to 10.1.7.29, the CVE ID column in the Attack Log page displays CVE IDs for all the alerts that have valid CVE IDs assigned to them in the signature set. In case you are upgrading the Manager to version 10.1.7.44 from version 10.1.7.29, 10.1.7.35, or 10.1.7.40, the CVE ID column in the Attack Log page displays CVE IDs only for the alerts (that have valid CVE IDs assigned to them in the signature set) generated post upgrade. You will not be able to view the CVE IDs for old alerts. In order to view CVE IDs for such alerts: Double-click on the old alert for which you want to view the details. The <Attack Name> panel opens on the right hand side. Click on the Description tab in the panel and scroll down to the Reference section. You can view the CVE ID in this section, provided the alert has a valid CVE ID assigned to it in the signature set.
BTP — Displays the BTP level as either High, Medium or Low Attack Category — General attack type Last Updated — Recent version of the signature set in which the attack was updated
|
Packet Capture | You can export the packet capture for that alert. |
Mitre Attack Details | Displays key components of the Mitre matrix table for an attack or alert: Tactic — Name of the adversarial tactic matching with the attack or alert Technique — Name of the corresponding adversarial technique matching with the attack or alert Sub-Technique — Name of the corresponding adversarial sub-technique matching with the attack or alert Technique/Sub-Technique ID — ID of the specific technique/sub-technique in the <techniqueID.sub-techniqueID> format. For example, in the ID T1595.001, T1595 represents the technique Active Scanning and 001 represents the corresponding sub-technique named Scanning IP Blocks.
Mitre Attack Details column option is available in both Trellix IPS Manager and Central Manager.
If an attack matches with multiple tactics, techniques, and/or sub-techniques, their names along with applicable technique/sub-technique IDs are shown in the respective fields under the Mitre Attack Details column. When an attack is mapped to multiple tactics, techniques, and/or sub-techniques, there is one-to-one correspondence among the tactics, techniques, sub-techniques, and technique/sub-technique IDs. For example, the first tactic corresponds to the first technique, sub-technique, technique/sub-technique ID, and so on.
If the Tactic, Technique, Sub-Technique, or Technique/Sub-Technique ID is not available for any alert or attack, that particular field is displayed as ---.
Mitre attack related details in the Attack Log are not shown for older alerts.
|
Attacker | Displays details about the attacker endpoint IP Address — IP address of the attacker endpoint Port — Port on which the attack was detected Risk — Displays the risk level as High Risk, Medium Risk or Low Risk Hostname — Name of the host from where the attack was generated Country — Country of the attacker host Proxy IP — IP address of the proxy server
|
Target | Displays details about the target endpoint IP Address — IP address of the target endpoint Port — Port to which the attack is directed Risk — Displays the risk level as High Risk, Medium Risk or Low Risk Hostname — Name of the host to which the attack is directed Country — Country of the target host Proxy IP — IP address of the proxy server
|
Malware File | Displays details about the attack in case of malware attacks File Name — Name of the malware file File Hash MD5 — Displays the MD5 hash of the file SHA1 — Displays the SHA1 hash of the file SHA256 — Displays the SHA256 hash of the file
Malware Name — Name of the malware Malware Confidence — Malware confidence level returned by the configured malware scanning engines Engine — The configured scanning engine that detected the malware
|
Callback Activity | Displays details about the callback activity for BOT attacks |
Endpoint Executable | Displays details about the endpoints running the executables Manager — Name of the Manager. This field is applicable for Central Manager only. Name — Binary name of the executable Hash — File hash of the executable Malware Confidence — Displays the malware confidence level returned by the configured McAfee EIA. The malware confidence values are very high, high, medium, low, very low, and unknown.
|
Application | Displays the Layer7 applications involved |
Detection | Displays details about the Sensor that detected the attack Domain — Name of the domain to which the Sensor belongs Device — Name of the device that detected the attack Interface — Interface at which the attack was detected
|
Layer 7 Data | Displays the following layer 7 data field details: NetBIOS Action NetBIOS File Name Relevant fields of command SMB CMD NEGOTIATE in the request direction only Relevant fields of the command SMB CMD TREE-CONNECT-ANDX in the request direction only Relevant fields of the command SMB CMD Trans in the request direction only Relevant fields of the command SMB CMD Trans2 in the request direction only Relevant fields of the command SMB Header in both request and response directions Relevant fields of the command SMBv2 Create in both request and response directions Relevant fields of the command SMBv2 Find in the request direction only Relevant fields of the command SMBv2 Header in both request and response directions Relevant fields of the command SMBv2 IOCTL in the request direction only Relevant fields of the command SMBv2 NEGOTIATE in both request and response directions Relevant fields of the command SMBv2 Read in the request direction only Relevant fields of the command SMBv2 Session Setup in both request and response directions Relevant fields of the command SMBv2 Tree Connect in both request and response directions Relevant fields of the command SMBv2 Write in the request direction only FTP Action FTP Banner FTP File Name FTP Return Code FTP User Name SMTP Attachments SMTP Banner SMTP Recipients SMTP Sender TELNET User Name Relevant fields of the command DCERPC Bind Relevant fields of the DCERPC Header in both request and response directions Relevant fields of the command DCERPC Request DNS OPCode DNS RRName DNS RRType Relevant fields of the command DNS RSP Answer Relevant fields of the command DNS RSP Answer Rdata Relevant fields of the command DNS RSP Authority Relevant fields of the command DNS RSP Authority Rdata DNS RSP Header Flags DNS TXID DNS Type HTTP CLSID HTTP Host HTTP Request Content Type HTTP Request Filename HTTP Request Method HTTP Request Referer HTTP Request URL HTTP Response Content Type HTTP Return Code HTTP Server Type HTTP URI HTTP User-Agent HTTP2 STREAM ID HTTP2 Settings Enable Push (Client) HTTP2/3 HTTP VERSION SSL Certificate Common Name SSL Server Name Indication
You can view the protocols that are enabled on the Protocols tab of the L7 Data Collection page under Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → Advanced. You can also customize the settings for the protocols in the L7 Data Collection page. For more information, see Enable Layer 7 Data Collection for an interface or subinterface. |
In addition to the column filters, there are specific sub-filters for each column. These sub-filters are based on specific values for that column. For example, the Direction column will have Inbound, Outbound, Unknown, and Bi-directional as the sub-filters. The alerts are filtered based on the selected option. Further, the Sort Ascending and Sort Descending options for each column toggles the alerts either in ascending order or descending order.
Alerts cannot sorted using the Mitre Attack Details column.
Automatic refresh of alerts
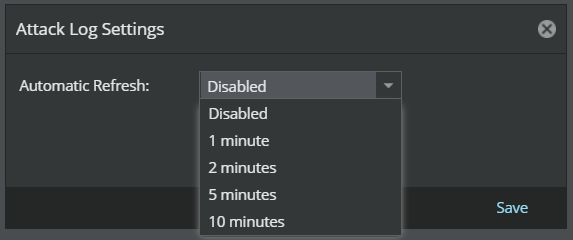
Alerts in the Attack Log page can be refreshed automatically. Refer the following steps to enable or disable automatic refresh:
Alerts can be refreshed manually by clicking  .
Click  .
The Attack Log Settings dialog box is displayed.
Make sure that the set time period to fetch alerts is greater than the automatic refresh interval to not lose any alert data.
From the Automatic Refresh drop-down, select the refresh interval based on your requirement.
To disable automatic refresh select Disabled from the drop-down.
Click Save.
When Automatic Refresh is enabled, the Attack Log page refreshes automatically every time you visit the page from some other location, such as the Dashboard tab or Threat Explorer.
When you select an alert in the Attack Log page, with auto refresh enabled, the alert remains selected with the details panel still displaying the alert data though new alerts are added to the page.