The following are the requirements for implementing user-based rules for Firewall and QoS:
Manager version 10.1.7.65 or above
NS-series Sensors running on version 10.1 or above
Trellix Logon Collector version 3.0.11
Your AD server is configured correctly and that your users are able to logon to the domain.
You have deployed the required Sensor monitoring ports in SPAN, tap, or inline mode (for QoS, only inline mode applies). Your Trellix IPS deployment is functioning as expected. For example, in the segment where you have deployed the monitoring ports, legitimate traffic is able to reach the destined hosts.
Optionally, you can log the results of each rule that the Sensor applied. For this you need a syslog server.
Note
To be able to configure and use Firewall policies, you must have administrator permissions for the IPS environment of the Manager. If you are not sure, contact the administrator of the Manager server.
The following are the high-level steps involved in implementing user-based access rules:
Install or upgrade Trellix Logon Collector to software version 3.0.11. You can install Trellix Logon Collector on your AD server or on a different one. If you are installing it on a different server, make sure the Trellix Logon Collectorand the AD server are reachable to each other over the network. Refer to Trellix Logon Collector 3.0 Administration Guide for information on installation and upgrade.
Add the relevant domains in Trellix Logon Collector. After you have added the domains, the Status in Trellix Logon Collector must be in green. If not, refer to Trellix Logon Collector documentation to troubleshoot and fix the problems.
The status in Trellix Logon Collector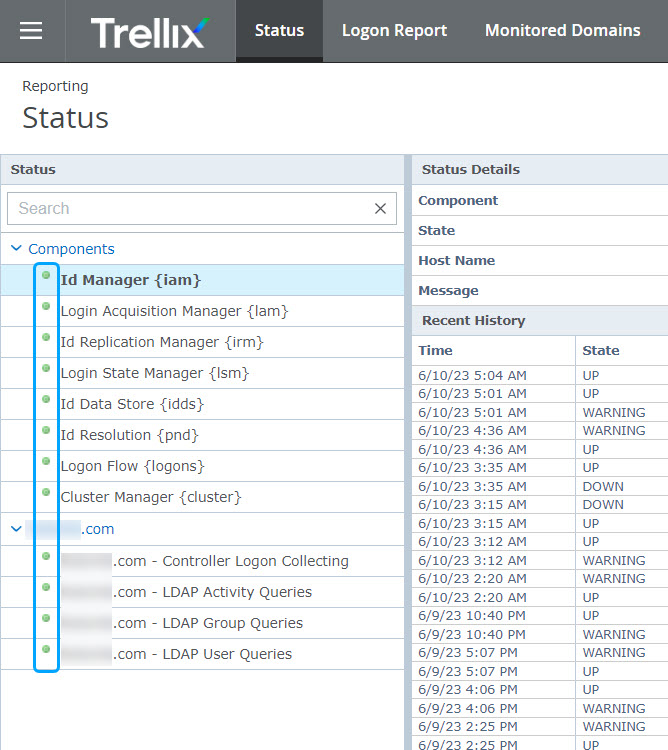
Make sure the IP, users, and computer details displayed in the Logon Report of the Trellix Logon Collector are accurate.
Integrate Trellix Logon Collector with the Manager. You can integrate only one Trellix Logon Collectorwith the Manager. See Trellix Intrusion Prevention System Integration Guide for more information.
Note
If you implement Manager Disaster Recovery (MDR), then you must manually integrate the secondary Manager with Trellix Logon Collector.
Optionally, configure the syslog details in the Manager to log the details related to Firewall access rules.
As explained in the subsequent sections, the Manager receives the user details from Trellix Logon Collector. Additionally, the Sensor also uses the Kerberos traffic to detect user details. For this method to work, you must configure the details of the AD and Trusted Domain Controllers in the Manager.
Configure user-based access rules in the Manager and apply it to the required Sensor resources. In an access rule, you can specify the following as the criteria:
Up to 10 AD user names
Up to 10 AD user groups
A combination of AD user names and user groups not exceeding 10 in a rule in advanced policy.
View the access-rule related details in the Manager configuration report and in the syslog server.