Similar to application identification, the information in this section applies to advanced Firewall policies and advanced QoS policies.
For example, you can create access rules to allow a specific AD group of users to access social-networking applications while blocking the same for some other group during business hours. Such access rules where user data is also a criteria are referred to as user-based access rules. Creating rules that are based on users and user groups is a better option than IP address based rules, especially when the IP address are likely to change dynamically.
Note
You cannot specify country and user name or user group in the same rule.
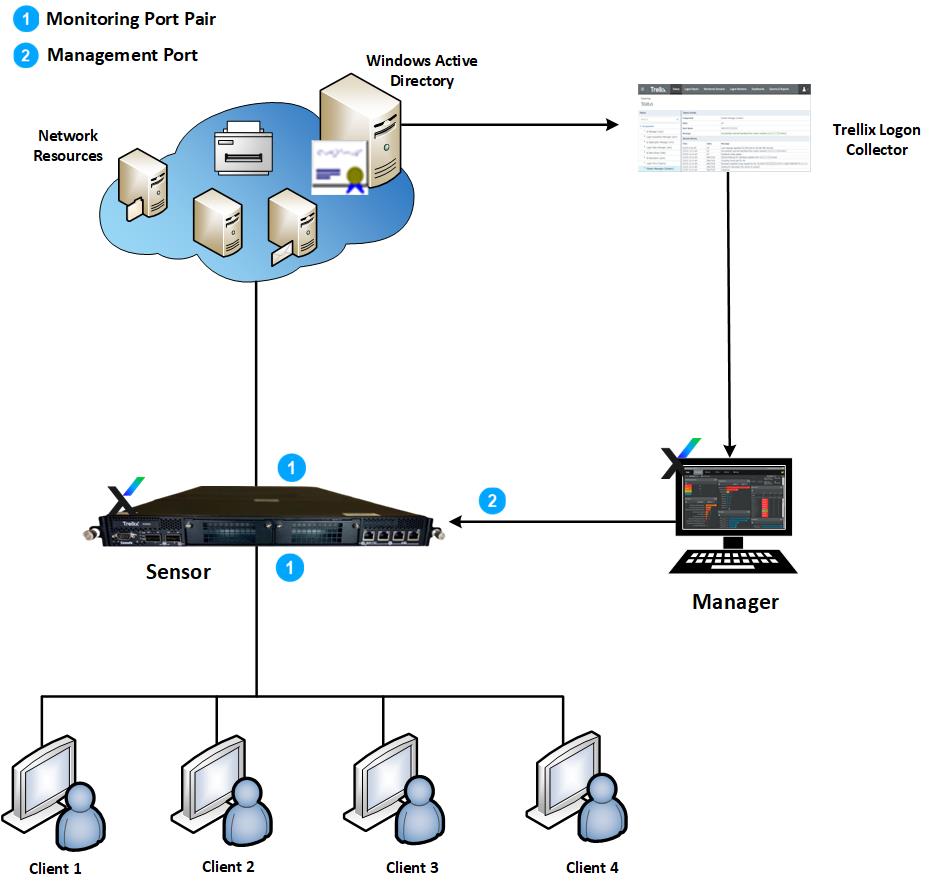
To use user-based rules in your Firewall or QoS policies, you must install Trellix Logon Collector on your network and integrate it with the Manager. Trellix Logon Collector gathers the details of the currently logged on users from the domain controllers. It then regularly updates these details to the Manager. The Manager processes these details and passes them to the relevant Sensors, which use them to evaluate the traffic and take the configured response action.
Note
You can configure user-based access rules only in advanced Firewall and QoS policies.
You can create an advanced Firewall access rule with the Response set as Require Authentication. This option indicates that you want the Sensor to ensure AD authentication of users if the traffic is HTTP. If the Sensor does not have the AD details for a user, it mandates the user to provide the AD logon credentials. The Manager then verifies these credentials with the AD server. So, the Sensor is aware that the user has valid AD credentials and also has the AD user name to apply the correct rule.
Advantages
User-based rules enable you to effectively identify and regulate traffic originating in your network. So, you can now control what your users can or cannot access regardless of the other criteria. In case of QoS, you can apply traffic management techniques based on user groups.
Consider organizations where users work in shifts or where users log on from any available host; that is, a host is not dedicated to any particular user. For such cases, user-based access rules can provide the required control.
Bring Your Own Device (BYOD) environment is another scenario where user-based access rules can be very useful. Using the Require Authentication option, you enforce your users to make their host to be part of your corporate domain.