For a botnet to be active, the bots must be able to communicate with the C&C server. For example, bots transfer the results of previous operations as well as seek further instructions. As a counter-measure, security applications find ways to break this communication channel between the bots and the C&C server. One of the ways of breaking a botnet is to identify the IP addresses and domains of C&C servers based on signatures to block them, or use a central reputation system to identify known C&C server domains and IP addresses. So, for a botnet, it is critical that the C&C server details are concealed so that they are highly available for the bots and avoid any legal action.
Some hackers use DGA to keep the C&C infrastructure concealed but available to the bots. DGA uses a seed, such as date or time, and generates random C&C server domain names. The bot contacts the local name server to resolve these domain names. DGA generates a high number of such domain names over a short period.
The attacker registers one of the random domain names generated by the DGA. So, the bot is now able to access the C&C server. Attackers register DGA domains for short periods. This just-in-time registration makes it difficult for security applications and reputation systems to block the domain.
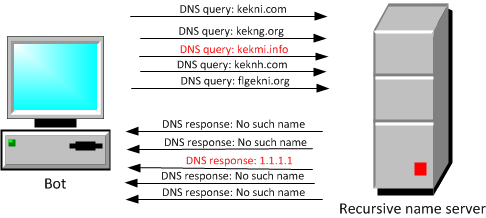
Malware might use DGA as the primary or secondary method to contact the C&C domain. For example, some malware such as Conficker use DGA as the mechanism to contact its C&C domain. Some Zeus variants employ DGA as a secondary mechanism. That is, the DGA code is triggered only when a bot is unable to reach the hardcoded C&C domains.