While creating or editing an attack set profile, you can create one or more rules with the categories, subcategories and minimum severity level of attacks that you want to be blocked by the Sensor as per the blocking strategy that suits your network environment and use the same profile during any IPS policy configuration. You can then enforce the IPS policy at the interface and sub-interface level for the required Sensor(s) and deploy these configuration changes to the required devices in the admin domain level or at a device level. When the policy and rule updates are applied to the required Sensor(s), those automatically block all attacks that match your blocking criteria as set in the attack set profile and send an alert to the Manager.
Automating the process of blocking attacks in the Manager and Sensor involves the following steps:
Creating or editing an attack set profile that includes rules for blocking attacks specific to any network environment
Creating or editing an IPS Policy that uses the attack set profile created for blocking specific attacks.
Assigning the IPS policy to specific interfaces and sub-interfaces of the required Sensor(s)
Deploying the configuration changes to the required Sensors
Configuring attack set profile that include user-defined rules for blocking attacks
Perform the following steps to include the rules for blocking specific attacks as per your network requirements while creating or editing an attack set profile.
In the Manager, click Policy and select the required Domain.
Navigate to Intrusion Prevention → Objects → Attack Set Profiles page.
The Attack Set Profiles page is displayed that includes all pre-configured and user-configured attack set profiles.
Click
 icon if you want to create a new attack set profile with your specific blocking strategy. If you want to add your blocking criteria to an existing attack set profile, you may do so by double-clicking that specific profile.
Note
You can create rule for blocking in custom attack set profiles only, as the default or preconfigured attack set profiles are read-only.
Enter appropriate details on the Properties tab and configure Include and Exclude rules on the Attacks to Include/Exclude tab as per your network requirement.
Once the rules to include and exclude attacks have been added, click Next to save the changes made on the Attacks to Include/Exclude tab and go to the Attacks to Block tab. This tab helps you define rules that determine whether the attack definitions, that are to be included in the IPS policy as per the configured Include rules on the Attacks to Include/Exclude tab, are automatically set to be blocked in the corresponding IPS policy.
Attacks to Block tab as displayed during attack set profile configuration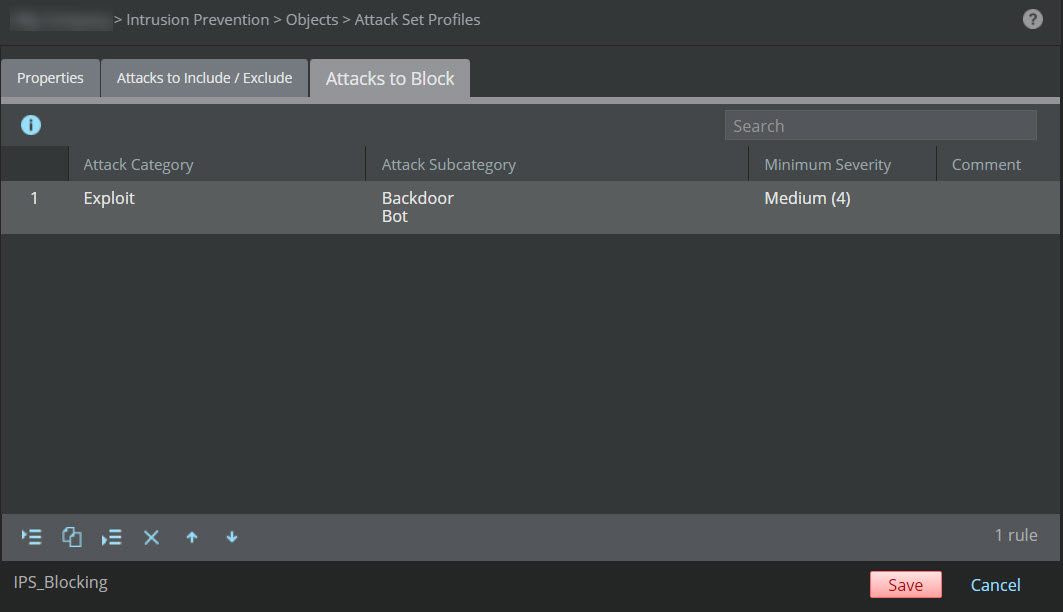
On the Attacks to Block tab, click the appropriate button to insert a new rule. You can insert a new rule by clicking either
 or
 icon. The Details panel is displayed.Details panel on Attacks to Block tab
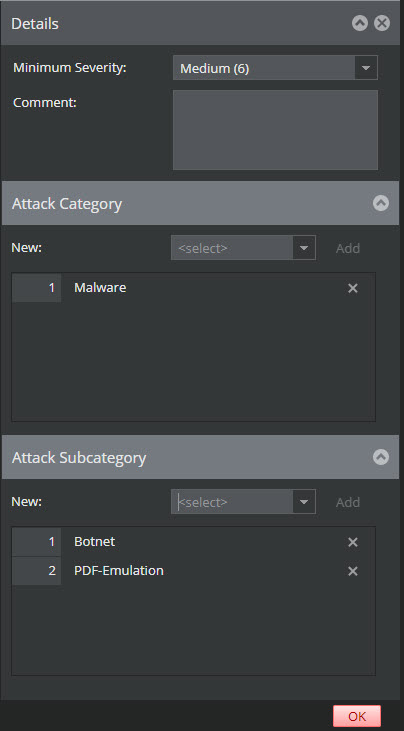
Select the appropriate options in the Details panel:
Option
Definition
Minimum Severity
Select the minimum severity level from the drop-down list. The default value selected while creating a rule is set to High (9).
Important
Rules created for automatic blocking of attacks are not applicable to Informational and Low severity attacks.
Comment
Enter additional comments, if any.
Attack Category
Select one or more attack categories as per your requirement from the drop-down-list.
Click the Add button to add the attack category to the list. Click
 to remove the item from the list.
Attack Subcategory
Select one or more attack subcategories for the attack category selected.
Click the Add button to add any subcategory to the list. Click
to remove the item from the list.Note
For more information on the configuration options available on the above-mentioned tabs during attack set profile creation, refer to the section Create an attack set profile.
Click OK to confirm the configuration changes and Save to save the attack set profile configuration. Your new attack set profile is listed in the Attack Set Profiles page.
Attack set profile configured with the user-defined blocking criteria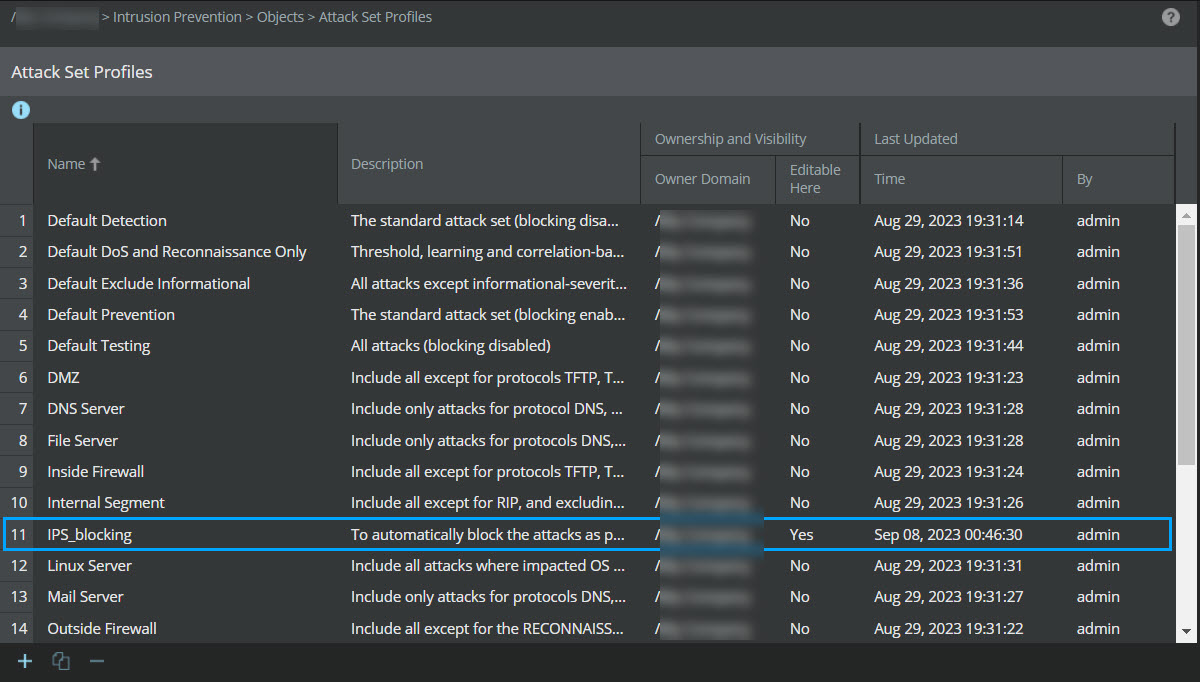
Configuring an IPS Policy that uses the attack set profile created for automatic blocking of specific attacks
Once the attack set profile, which includes rules for automatic blocking of specific attacks, is configured, you can use that profile during the IPS policy configuration. To do so, perform the following steps.
In the Manager, click Policy and select the required Domain.
Navigate to the Intrusion Prevention → Policy Types → IPS page.
Click
icon, if you want to add a new IPS policy. If you want to edit an existing IPS policy, you may do so by double-clicking it.On the Properties tab that opens, choose the Policy Direction as per your requirements and map the attack set profile that contains the rules defining your blocking criteria in the Attack Set Profile field.
Using the selected attack set profile in the IPS policy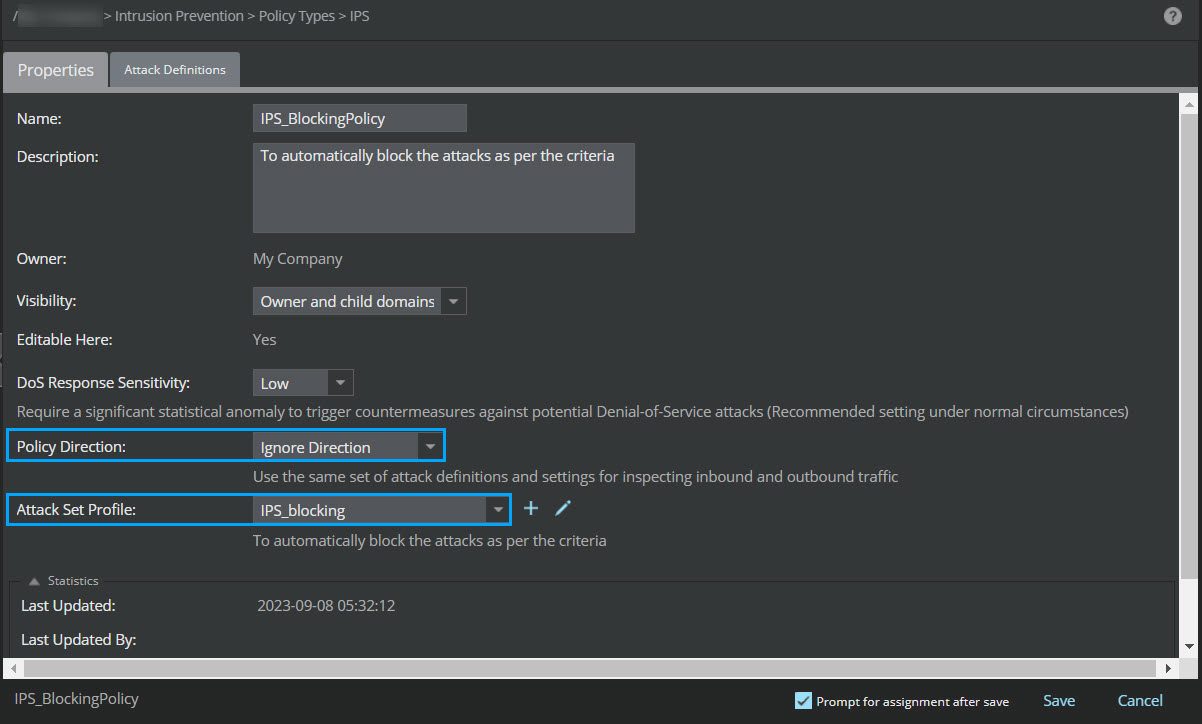
Note
When you select the Policy Direction option as Consider Direction, you can select one attack set profile for inbound traffic and another for outbound traffic. Separate attack set profiles for inbound and outbound can be applied to Sensors in SPAN or tap mode. If the Sensor is unable to determine the direction of the traffic, it enforces the rules and configuration updates of the inbound attack set profile.
Click Evaluate Attack Set Profiles. This redirects you to the Attack Definitions tab which displays all attack definitions that match the Include rule criteria in the attack set profile. For attacks that fall under the blocking criteria in the attack set profile and are set to be automatically blocked, you would notice the Response column under Sensor Actions showing the alert messages Send Alert to Manager Enable Blocking.
Attack Definitions tab showing the attacks automatically set to blocking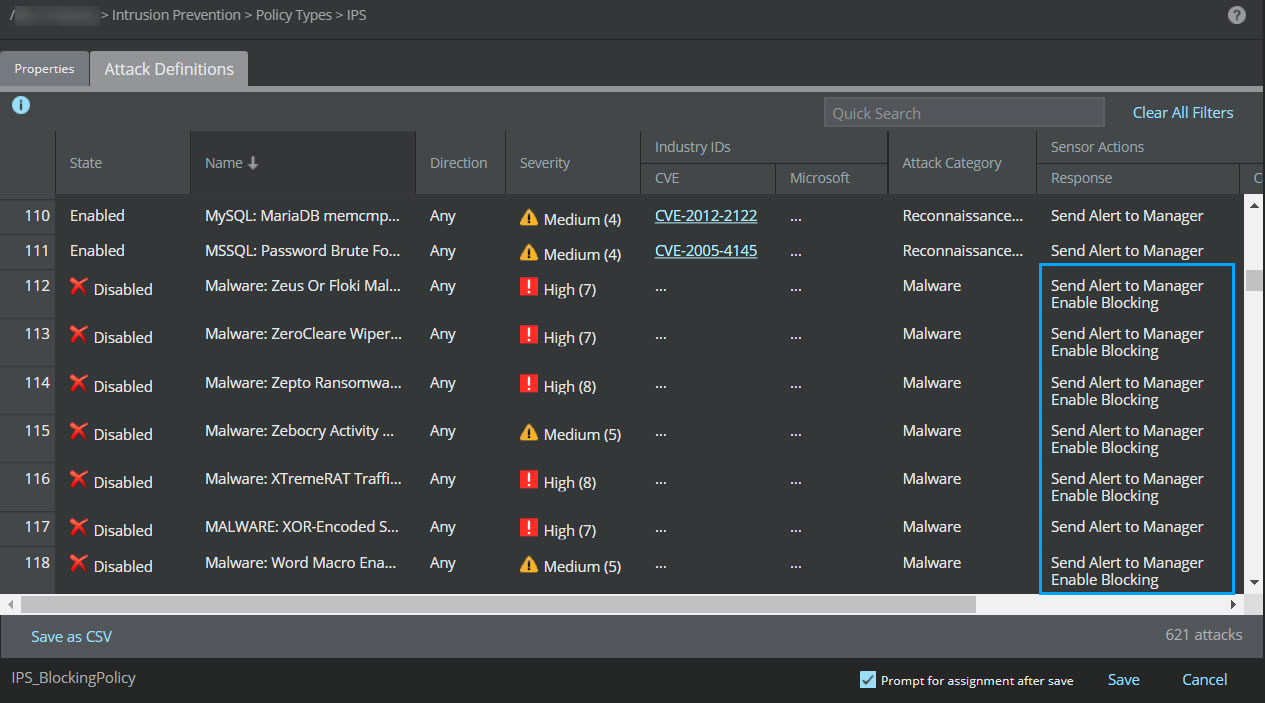
Double-clicking any attack definition marked to be automatically blocked as per the attack set profile configuration shows the Block field under Sensor Actions - Response to be Inherit (Enable Blocking). This Sensor response action is only visible for attacks that are set to be automatically blocked in the selected attack set profile.
Sensor response action for block is shown as Inherit (Enable Blocking)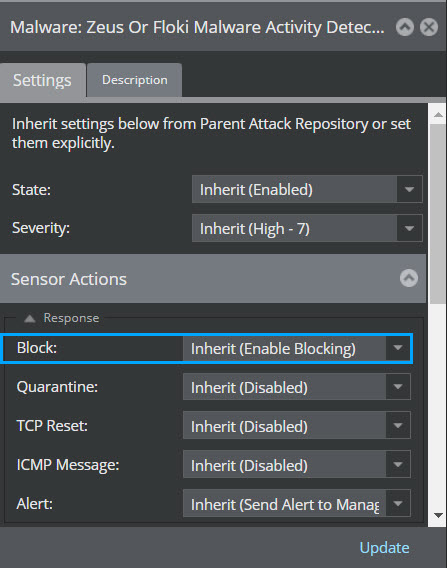
Important
If you wish, you can override the automatic blocking behavior of any attack by manually setting the Sensor blocking action during IPS policy configuration. Sensor response actions customized in the IPS policy always takes precedence over automatic blocking of attacks criteria set in the Attack Set Profiles page.
Review the attack details as shown on the Attack Definitions tab and click Save to save the IPS policy.
For more information on how to add/edit an IPS policy or customize it, refer to the section Manage IPS policies.
Assigning the IPS policy to interfaces and subinterfaces
Once the desired IPS policy is mapped to the attack set profile that includes the rules for attack blocking, you can assign that policy to the specific interfaces and subinterfaces of the required Sensors. For more information, refer to the section Assign IPS policy to interfaces and subinterfaces.
Deploying configuration changes to the required Sensors
Post the assignment of the policy to the required interfaces and subinterfaces, perform a configuration update for the corresponding Sensors to enforce the policy. For more information, refer to the section Deploy pending changes to a device.
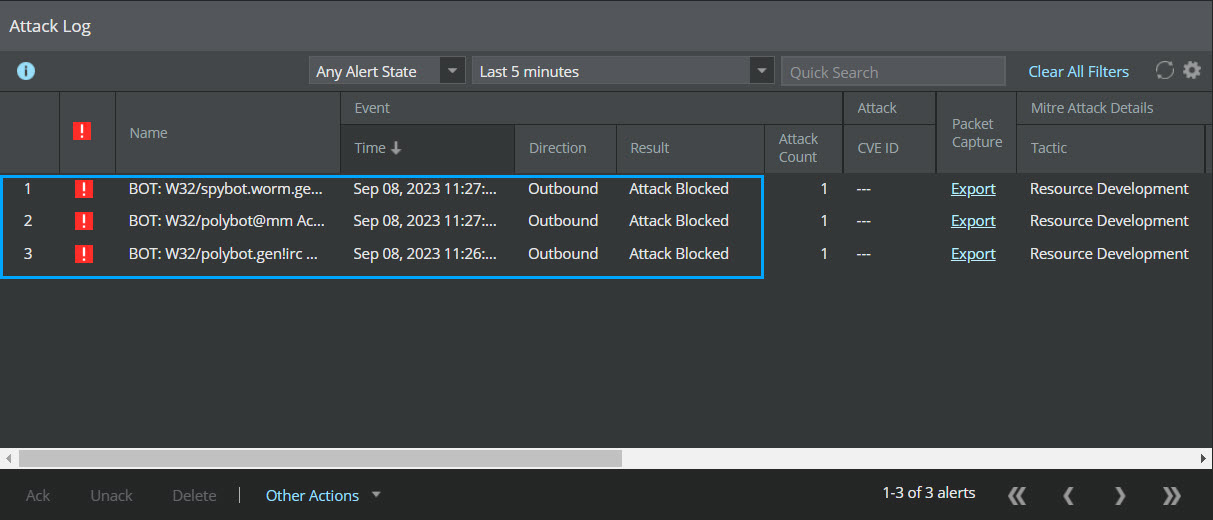
Post the successful assignment of the IPS policy, the concerned Sensor detects attacks and blocks them if it matches the blocking criteria of the attack set profile. Along with the blocking action, it also generates an alert which is sent to the Manager and can be viewed using the Analysis → <Admin Domain Name> → Attack Log page.