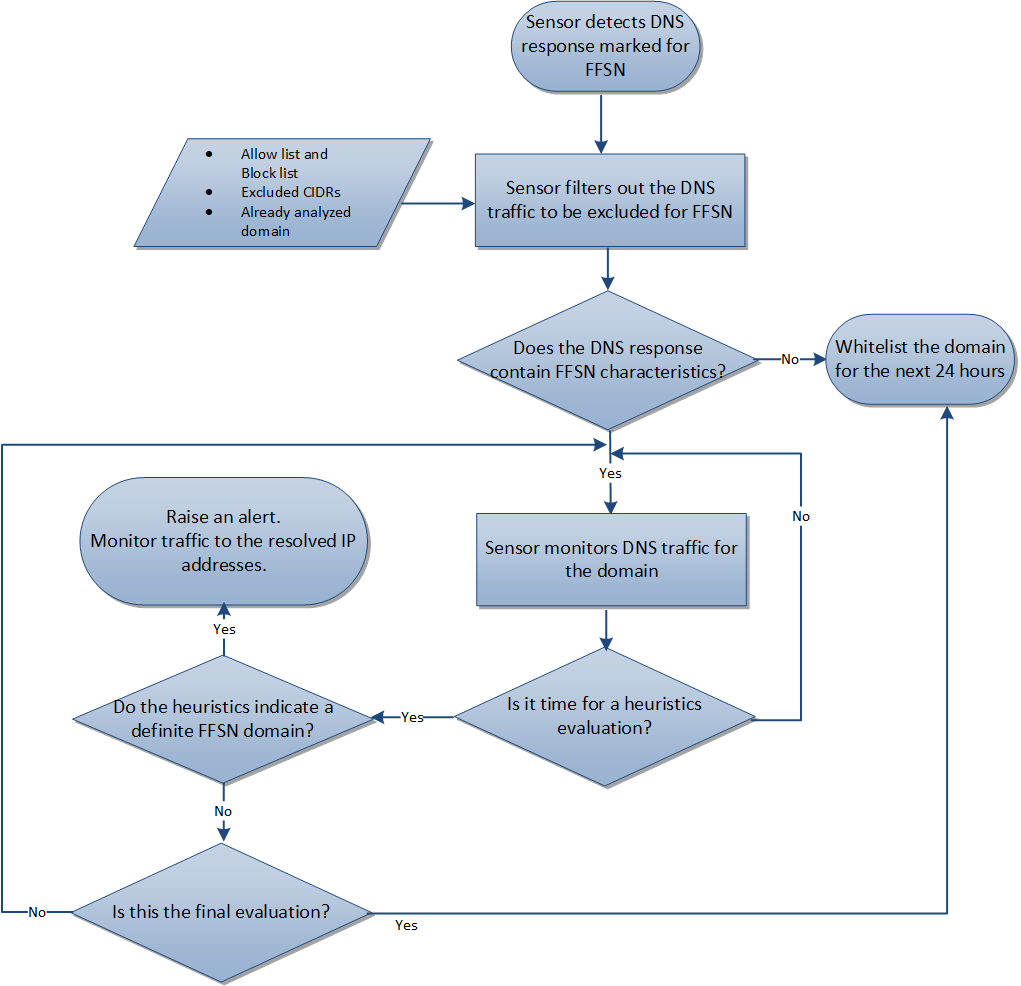
At a high-level, Trellix IPS detects FFSN as described in this section.
For the sake of explanation, assume the following:
Sensor monitoring ports are inline between the protected hosts (DNS clients) and the local (recursive) name server. Therefore, all DNS requests and responses pass through the Sensor.
You have configured the DNS clients as the inside network. That is, the name server is in the outside network. The Sensor inspects DNS response packets for FFSN. So, you must enable Fast Flux Detection in the outbound direction. Enabling Fast Flux Detection in the outbound enables the Sensor to track the DNS response with the corresponding request.
The Sensor filters out the DNS traffic, which need not be inspected for FFSN. The DNS traffic is exempted from FFSN inspection, if any of the following conditions are met. The Sensor checks the DNS response packets in the following sequence.
The source or destination IP address in the DNS response packet belongs to CIDRs Excluded from Advanced Callback Detection list.
The domain is exempted according to the user-defined domain name exceptions. Assume that you have imported the domain name exceptions in the Manager and enabled Domain Name Exclusion List Processing in the inspection option policy.
The domain is blocked according to the callback detectors. Assume that you enabled Callback Detectors and Heuristic Callback Discovery in the inspection option policy. Then, the Sensor sends a crafted DNS response packet to sinkhole the corresponding callback traffic.
If you disabled Callback Detectors and Heurisitc Callback Discovery, the Sensor inspects the DNS traffic for FFSN even for C&C server domains.
The domain is already analyzed for FFSN and found to be benign.
Note
If a requested domain name resolves to an IP address of a reserved CIDR, such as the private network CIDRs in RFC 1918, the Sensor does not consider that IP address for FFSN suspect processing.
The Sensor identifies the domains to be monitored for FFSN. For each domain, it checks the DNS response packets for any FFSN characteristics.
If the Sensor finds any FFSN characteristics in the DNS responses, it considers the domain for heuristics-based inspection for FFSN.
The Sensor might take anywhere between 10 seconds to 12 hours to complete this heuristic analysis for a suspected domain.
If the heuristics parameters indicate that the domain belongs to an FFSN, the Sensor raises the Botnet: Heuristic Detection of Fast Flux DNS alert. Because Botnet: Heuristic Detection of Fast Flux DNS is a component attack, quarantining the host is not applicable.
The Sensor adds all IP addresses which resolved for this domain in its watch list for the next 12 hours. When any hosts communicate with any of these IP addresses, the Sensor raises the Botnet: Connection to Fast Flux Agent Detected alert. This alert enables you to identify other victim hosts in your network.
Sensor does not consider DNS responses for FFSN, if they contain IPv6 addresses.
When the Sensor detects an FFSN domain, it includes the following information in the alert:
The IP addresses in the A records
Reverse DNS result for the IP addresses
Monitor interval
Number of IP addresses in the A records
Geo-diversity of the IP addresses
IP address of the last victim host to query for the FFSN domain
Note
For interfaces in SPAN and tap mode, you must enable FFSN detection in both inbound and outbound direction.