Generally, a Fast Flux Service Network consists of hundreds of compromised hosts commanded and controlled by a server (C&C server). The C&C server acts as the mother ship for the network. The compromised hosts are referred to as flux agents. These flux agents are hosts with public IP addresses, such as home computers. When a host in your network is infected, it attempts to access the malicious content on the C&C server. For this purpose, the FFSN has a registered domain name.
The main objective of an FFSN is to ensure high-availability of the malicious content on the C&C server as well as to prevent the C&C server from being identified and subsequently blocked. To achieve this goal, attackers exploit the way DNS functions. The FFSN strategy has dual approaches to it.
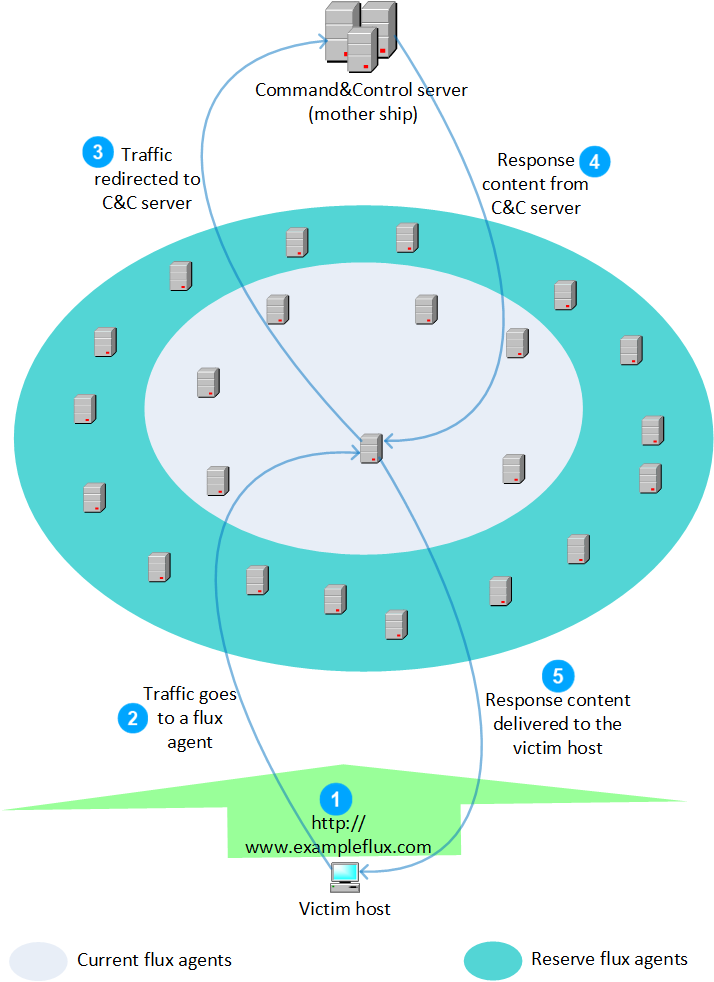
Firstly, the DNS records for the FFSN domain are configured such that it resolves to the IP addresses of the flux agents. That is, the flux agents act as the front end for the FFSN domain. So, a flux agent acts as a reverse proxy between the victim host and the C&C server. This prevents the C&C server from being exposed to security applications and law-enforcement agencies.
Secondly, attackers make sure that the IP addresses resolving to the FFSN domain continually change. That is, the IP addresses associated with the domain are in a flux. This is achieved by configuring a very low time to live (TTL) for the DNS A records. At one point in time, only a batch of the flux agents are advertised. Attackers keep rotating the pool of flux agents that are currently in use.
This technique of keeping the IP addresses in a flux, ensures high availability of the FFSN domain. Even if some of the flux agents are not available (probably powered off by the legitimate owners) or if the domain IP addresses are blocked by a security application, the domain is still available.
Typical characteristics of an FFSN
The number of A records is high.
The TTL of FFSN IP addresses is very low.
With each DNS query, the FFSN domain is likely to resolve to newer IP addresses. Therefore, the DNS results reaching your local name server is different from the previous.
The flux agents belong to different networks and usually are from different geographical locations.
The IP addresses in the A records do not belong to the same Autonomous System Number (ASN).
The traffic between an victim host and the C&C server is typically HTTP. As this traffic is redirected through a flux agent, there is a relative delay observable at the victim host for this HTTP traffic.
The C&C server rotates the flux agents based on round-robin to distribute the load and for high-availability. There could also be factors such as availability of the flux agents.
Analyzing a flux agent usually does not provide much information on the served malicious content or the C&C server.
Differentiating benign DNS traffic and FFSN traffic
There are some similarities between how an FFSN functions and certain cases of normal DNS traffic.
For example, to load-balance Web service requests, name servers resolve domains to servers based on round-robin.
In the case of Content Delivery Networks (CDNs), the domain resolves to servers based on their availability and proximity to the client. So, the domain might resolve to IP addresses belonging to different networks and geographical locations.
For the purpose of load-balancing, such benign DNS results also have a low TTL.
Though FFSNs can exhibit similar behavior as some benign DNS traffic, the Sensor is capable of differentiating these traffic from FFSN traffic.
DNS traffic flow
Because FFSN is based on DNS, the Sensor inspects the DNS response traffic to detect FFSN domains and flux agents. To understand how the Sensor detects FFSNs, review how DNS traffic flows when an victim host attempts to access an FFSN domain.
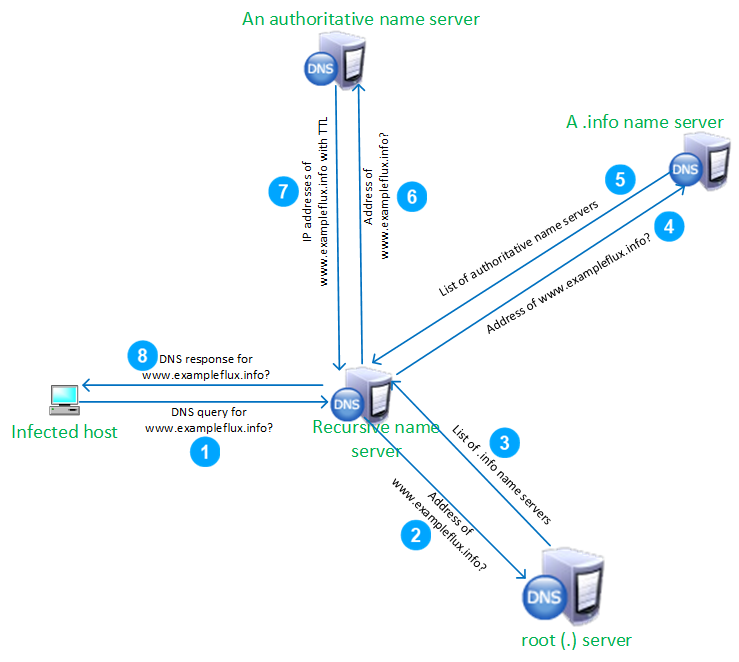
Consider a victim host in your network attempts to access an FFSN domain, for example
www.exampleflux.info.The host sends the DNS request to the recursive (local) name server.Assume that name resolution details are not available in the recursive name server's cache. So, it sends a request to the root name server.
The root name server responds with the list of name servers for the .info top-level domain (TLD).
The recursive name server queries a .info name server for
www.exampleflux.info.The .info name server provides the list of authoritative name servers for
www.exampleflux.info.The recursive name server queries one of the authoritative name servers for
www.exampleflux.info.The authoritative name server responds with the IP addresses of the current flux agents.
The recursive name server passes on this list of flux agents to the victim host.