Trellix Intrusion Prevention System offers multi-gigabit performance, flexible deployment, robust scalability, and easy-to-use intrusion detection and prevention. Trellix IPS goes beyond the simple string matching. Sensors analyze and validate the traffic to its basic protocol elements and inspect specific protocol fields to improve accuracy, while maintaining full flow and application state. The Sensors perform IP fragment reassembly and TCP stream reassembly, and perform thorough protocol analysis all way up to the Application Layer. The signature engine searches in a flow for multiple triggers (that is, sub-signatures) in multiple fields of a protocol using Trellix IPS embedded signature files to increase the precision by which an attack can be unambiguously detected.
Once the packet is captured, it is analyzed into its corresponding protocol fields. The Sensor analyzes a frame completely and thoroughly from Layers two through seven, and understands the semantics of the protocol fields even at the Application Layer. After it analyzes the protocols, it verifies that the packet conforms to the protocol specification. Trellix IPS then passes the parsed packet through its other engines, such as the DoS, Signature and Anomaly detection engines, Malware engine, and internal Firewall engine. This enables Trellix IPS to be very efficient in terms of packet processing because the packet is "peeled" only once and then fed to the corresponding detection engines. All these processes are designed to provide the required wire-speed performance.
If the detection engines detect something abnormal, they pass an alert and corresponding data to the management process that is running on the Sensor. The management process can then trigger the appropriate response, based on policy, and send alerts to the Manager. This response can include blocking the corresponding traffic entirely and even quarantining the attacking host.
In addition to dropping malicious traffic, Trellix IPS provides "packet scrubbing" functionality to remove protocol inconsistencies resulting from varying interpretations of the TCP/IP specification, which can be used by hackers to evade IDS/IPS and other security devices.
The accuracy level of Trellix IPS is exceptionally high due to the following factors:
Full protocol analysis and state tracking
Multi-trigger, multi-field pattern matching
Trellix IPS's ability to see all the traffic in a variety of deployment modes, including active/active, active/passive, and asymmetrically routed traffic environments.
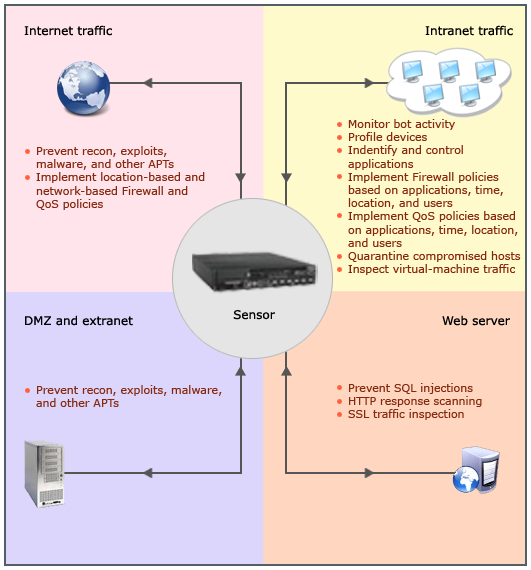
Protection against APTs: Trellix IPS performs deeper inspection of traffic to detect malicious file downloads and bots. It uses various malware scanning options for advanced malware protection. This includes an embedded PDF emulator that detects zero day java script threats in PDF downloads. It also runs the gateway anti malware engine on the NTBA appliance.
For bot-detection, Trellix IPS correlates multiple attacks across different flows by observing a host over a given period of time. It also forwards the attack information to the NTBA appliance for similar correlation.
Trellix IPS detects DoS and DDoS through threshold-based and self- learnt profile‑based detection techniques. In addition, it provides a connection-limiting feature that limits the number of connections a host can establish.
Protection for web applications: Trellix IPS provides various features to protect your web application servers. For example, it employs a heuristic engine to detect SQL injections. Trellix IPS can inspect HTTP responses to ensure your servers are not compromised.
For inbound SSL traffic, in case of Known-Key method, the Sensor decrypts and analyses the SSL traffic based on the server's private key. In case of Agent-based method, the Sensor decrypts traffic based on the key exchanged by the agent installed on the web server with the Sensor. Based on the result of the inspection, the traffic is either allowed to go the client or blocked.
In case of outbound SSL traffic, the Sensor decrypts the traffic by matching with the trusted CA certificates in the Manager. After the Sensor inspects the traffic, the traffic is encrypted using the re-signing certificate.
Application Identification: Trellix IPS can identify the applications traversing your network and act on them as configured. So, you can allow or block specific applications or application features on your network. For example, you can block the connections to Facebook from your network while allowing all other HTTP traffic.
Identifying users and user groups: Trellix IPS integrates with Trellix Logon Collector to identify the Windows AD users on your network and also the user groups to which they belong. This means that you can now control based on users rather than their IP addresses, which are not always reliable. For example, a dynamic IP address might differ based on whether the user connects from office or outside office.
Next-generation IPS features: Trellix IPS provides next-generation IPS features, such as internal Firewall and QoS.
You can create different Firewall rules for different segments of your network. You can base these rules on the traditional 5-tupple with support for IPv6. In addition, you can base them on the applications, application features, Windows AD user data, geographical location, and time. This enables you to control the privileges of your network users regardless of whether they log on from home, airport, or office.
The Sensor evaluates the traffic against the Firewall rules before checking it for attacks. So, you can use this feature to filter the traffic that must be inspected for attacks.
You can create QoS rules based on similar criteria as for Firewall. These rules ensure that the required network bandwidth is always available for your business applications and not consumed by other applications, such as social-network or video-streaming applications.
Identifying the host type: Trellix IPS profiles devices to address risks due to BYOD. It integrates with ePO - On-prem and NTBA to identify the device type and the operating system for each host on your network. You are now aware of the types of devices on your network. If a specific host is targeted for an attack, you can also assess if that attack is relevant based on the device type and OS.
Protection for virtual machines: Virtual instances of Sensors enable you to monitor peer-to-peer traffic between virtual machines even within the same virtual host. Trellix Virtual Intrusion Prevention System Sensors are called as Virtual IPS Sensors or Virtual Sensors. You can deploy a Virtual IPS Sensor as a virtual appliance in a virtualization platform such as VMware ESXi server. Then, you can configure the Virtual IPS Sensor to protect the virtual network within the virtualization platform or even outside. Based on the network design and security requirements, you can configure a Virtual IPS Sensor to be inline between virtual machines or configure it in the IDS mode. It is also possible to use a Virtual IPS Sensor to inspect traffic between physical hosts.
Cloud-based IP and file reputation: To protect your network from known and near zero-day malware, Trellix IPS integrates with Trellix GTI. It can check if an email, URL, or a file is known malware. It can also check the reputation of IP address and port combination when an external host attempts to communicate with a host on your network.
Quarantine host and enforce remediation: If an internal host generates attack traffic, it could be that it is compromised. You can use Trellix IPS to manually or automatically quarantine such hosts until they are remediated.
Analyzing your network traffic: The IPS Sensor integrates with the NTBA appliance to proactively provide visibility into any anomalous behavior on your network. They passively monitor your network to help identify threats from APTs and to even troubleshoot network issues. NTBA collects a vast amount of data, which is converted to meaningful and relevant information, and presented to you in an easy-to-understand graphical format.
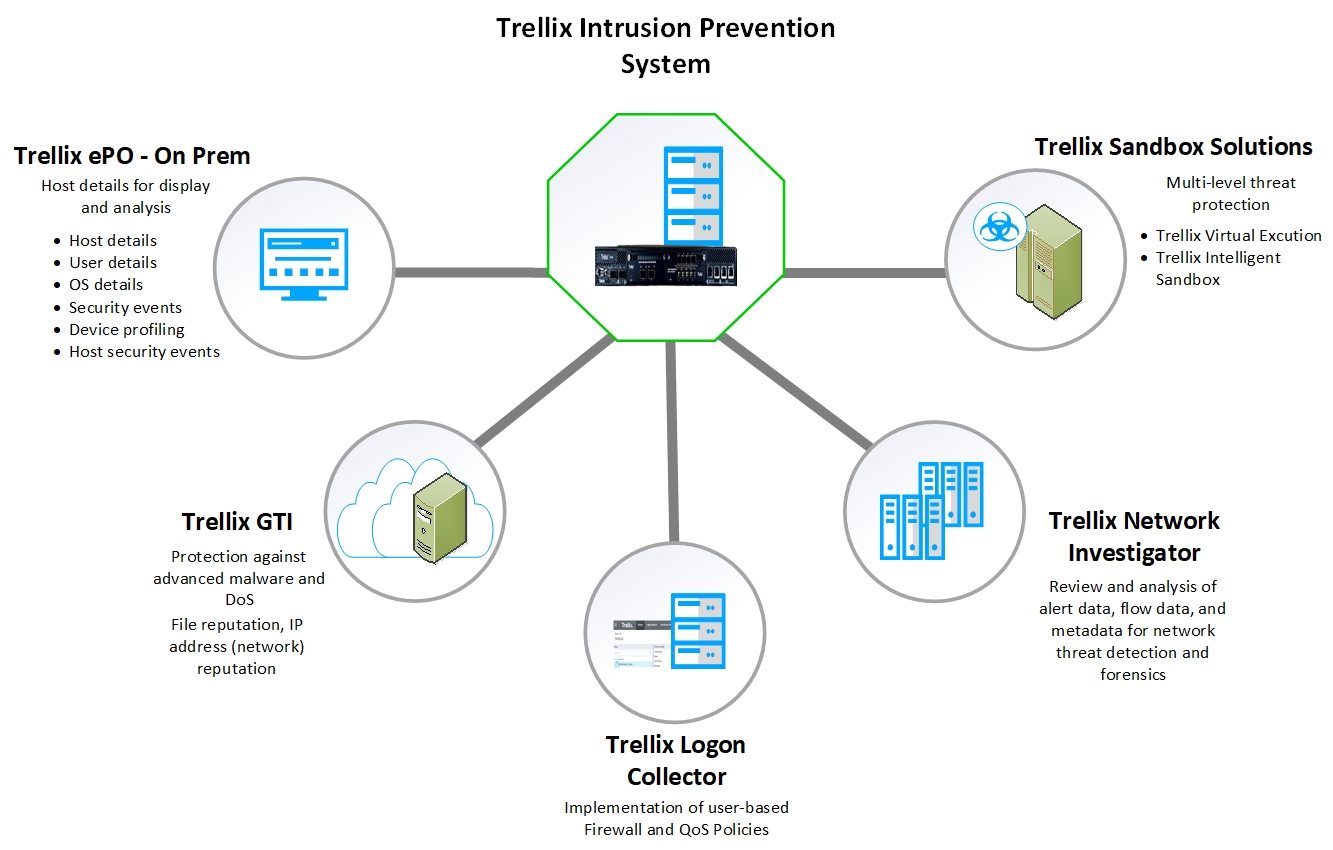
Integrating with other Trellix products: One of the biggest advantage that Trellix IPS provides is the ability to integrate with other Trellix products. A few of the Trellix products that Trellix IPS integrates with are given below:
Integration with Trellix ePolicy Orchestrator - On-premises: As mentioned earlier, this integration enables Trellix IPS in identifying the devices on your network. You can also query for the complete details of any ePO-managed host on your network.
Integration with Trellix GTI: As explained previously, this integration facilitates Trellix IPS to check the reputation of a file, URL, email, IP, and network.
Integration with Sandbox Solutions: Trellix enables integration with Trellix Intelligent Sandbox and Trellix Virtual Execution. Both these solutions facilitate detection and prevention of malware. They provide protection from known, near-zero day, and zero-day malware without compromising on the quality of service to your network users.
Integration with Trellix Network Investigator: With integration enabled with Trellix Network Investigator (NI), Trellix IPS exports netflows and Layer 7 metadata from IPS Sensors, and alert data from IPS Manager to Network Investigator, as per the configuration and filter parameters set by the user. The alert data, L7 metadata information, and net flow records exported by Trellix IPS are displayed on the Dashboard of NI's web-based UI which users can review and utilize further for the detection and analysis of network threats.
Integration with Trellix Logon Collector: This integration enables Trellix IPS to identify the Windows AD users and their hosts to apply the security policies accordingly.
Flexible deployment options: Trellix IPS provides devices of various throughput capacities to meet today's higher speed network segments. The throughput of these devices range from 100 Mbps to 100 Gbps that are designed to provide comprehensive protection without compromising on network performance. Trellix IPS provides wire-speed monitoring and analysis up to multi-Gbps network segments in three flexible modes of deployment, enabling you to easily integrate it into your network and adapt to any network or security changes that you may encounter in the future. Some Sensor models contain built-in 10/100 Mbps Ethernet taps, thus making it extremely easy to switch between tap and in-line modes through software reconfiguration; no physical rewiring is required. The multi-port configuration of all Sensors empowers comprehensive network-wide IPS deployment with significantly fewer Sensors.
The latest Trellix IPS devices come with hardware acceleration for supporting encryption, decryption, and decompression. They use Intel's high-performance processors to deliver higher throughput.
VIPS - Applying policies at the interface and sub-interface levels: The VIPS feature enables you to configure multiple policies for multiple unique environments and traffic directions all monitored with a single Sensor. The goal of virtualization is scanning granularity. Virtualization allows you to apply multiple policies to traffic flowing through a single interface. In this way, a unique scanning policy can be applied to a single host or group of hosts, when their traffic will not travel through a unique Sensor port. For example, suppose port G0/1 of an NS9500 Sensor is connected to the SPAN port on a switch. Port G0/1 is configured with a specific environment detection policy. The rest of the ports on the Sensor can have policies completely different than the policy on G0/1, or they can use the same policy. In this case, each monitoring port of the Sensor is an interface. The other option is to segment each monitoring port by multiple VLAN tags or CIDR addresses, each customized with its own security policy. In this case, each monitoring port is segmented into virtual sub-interfaces.
High-availability: Sensors support high-availability deployment, using stateful Sensor failover between two hot-standby Sensors. The Sensors are interconnected, copy traffic between themselves, and maintain synchronization. If one Sensor fails, the standby Sensor automatically takes over and continues to monitor the traffic with no loss of session state or degradation of protection level. Trellix IPS also supports Manager Disaster Recovery (MDR) for its management console. If, for any reason, the primary Trellix IPS Manager goes off-line, its secondary can automatically take its place, processing alerts and managing Sensor configuration.
Scalable IPS management: A scalable web-based architecture allows customers to efficiently manage their IPS deployment while reducing operational costs. Trellix IPS's real-time signature and software update mechanism automate the process of keeping the complete system current with little or no human intervention, thus reducing on-going operating costs. Also, Virtual IPS Sensors are remarkably quick and easy to deploy. Therefore, they greatly enhance scaling up your next-generation IPS deployment without any compromise on security features.