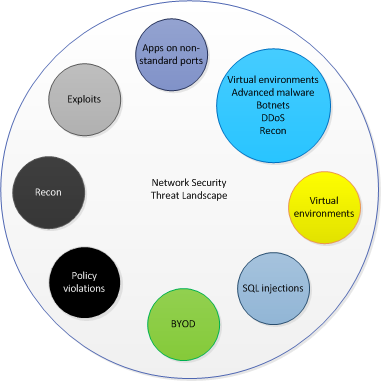
Every technological advancement provides new options to hackers. Some of the popular trends that are used to attack networks are:
Exploits: A hacker attempts to take advantage of hidden features or bugs in a system in order to gain unauthorized access. Examples include buffer overflows, directory traversal, and DNS cache poisoning.
Advanced persistent threats (APTs): APTs are unrelenting attacks against specific networks over a long period of time. APTs are purpose oriented. They target specific networks for specific goals. The attackers probe the target network for the most feasible entry point and then launch the attacks using the most appropriate technique. It could be a simple or complex technique, but they choose one that can help them achieve their goals. The attackers take care to remain undetected and persist with different methods until they succeed. The usual purpose is to gain financially or intellectually. It is very difficult to trace the source because APTs are mostly sponsored by nation states. Therefore, they are backed up by people, technology, and almost unlimited funds.
Advanced malware: Earlier users received malware as attachments in their emails. With the upsurge in Internet applications, users only need to click on a link to download files. Today, there are many other options to post such files - blogs, social networking sites, websites, chat messages, webmails, message boards, and so on. Your security system must not only be able to detect known malware but zero-day ones as well.
Bots: These are malware running on compromised systems. They are part of a larger, centrally managed network of such compromised systems. This network of compromised systems reporting to one command and control system is referred to as a botnet.
DoS and DDoS: Denial of Service (DoS) attack is a malicious attempt to render a service, system, or network unusable by its legitimate users. The previous generation DoS attacks do not require the attacker to gain access or entry into the targeted server. The primary goal of such DoS attacks is to deny legitimate users access to the service provided by that server. Distributed Denial of Service (DDoS) involves many compromised hosts across the Internet, to launch a DoS attack. Attackers typically use various tools to launch DoS and DDoS attacks.
DoS attacks have now evolved to exploit vulnerabilities in the web applications themselves. The aim is to turn off the service, thereby denying access to legitimate users. This technique produces the same result as the traditional DoS but costs less in terms of time and money.
Reconnaissance: These include host sweeps, TCP or UDP port scans, e‑mail recons, brute force password guessing, and possibly indexing of public web servers to find CGI holes or other system vulnerabilities that might later be exploited.
SQL injections: Because of their location and their functionality, web servers are usually the favorites for hackers. Mere signature-based detection cannot adequately protect your servers. You need an IPS that can quickly and intelligently detect SQL injections.
Bandwidth-consuming applications: As a security expert, you must be concerned not just about attacks but also about multimedia-rich applications bringing your network to a halt by consuming the majority of the available bandwidth. Your security system must be capable of identifying and regulating application traffic.
Virtual environments: Organizations are increasingly moving towards virtual environments. So, your security system must be capable of inspecting traffic between virtual machines residing on the same host.
Applications using non-standard ports: Current threats involve exploiting the use of non-standard ports to evade the IPS boxes. Your security system must be intelligent enough to address this issue.
Browser-based attacks: Browsers have become feature-rich and very user friendly with the support for new features, including HTML 5. However, this also offers new opportunities for hackers.
Policy violations: This denotes to all activities for which the underlying traffic content may not be malicious by itself, but are explicitly forbidden by the usage policies of your network as defined by your security policy. These can include "protocol violations" wherein packets do not conform to network protocol standards. (For example, they are incorrectly structured, have an invalid combination of flags set, or contain incorrect values.) Examples might include TCP packets with their SYN and RST flags enabled, or an IP packet whose specified length does not match its actual length. A protocol violation can be an indication of a possible attack, but can also be triggered by buggy software or hardware.