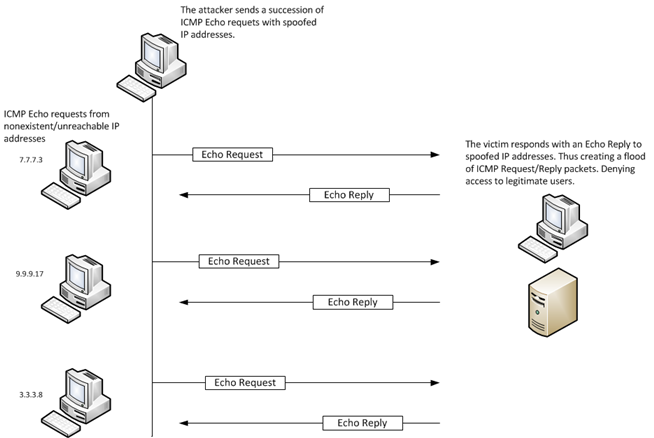
This attack involves flooding the network with ICMP echo request or reply packets. A flood of echo requests to a target system makes the system busy responding to the requests. If there is a flood of reply packets, it is very likely that the remote attacker has forged an IP address from within your network and is sending ICMP echo request packets to another network. That network replies to the address in the requests, thus starting a request/reply flood between the two networks.
In such an attack, the attackers send large numbers of IP packets with the source address forged to appear to be the address of the victim. The network's bandwidth is consumed, preventing legitimate packets from getting through to their destination.
A variation of an ICMP flood is also known as the smurf attack, named after a program capable of generating this attack. In such an attack, an ICMP echo request is sent to a broadcast network address, acting as an amplifying agent. The source address of the victim is spoofed. The result is a flood of replies from that network which takes the victim's network down.