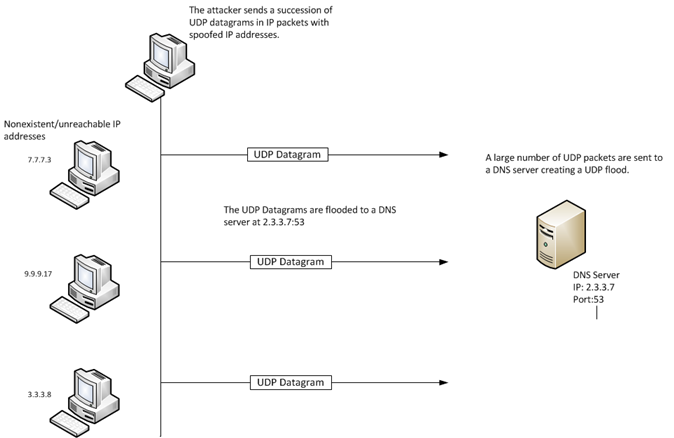
Sending a flood of UDP attacks to a targeted system constitutes a UDP flood attack. When communication is established between two UDP services, an UDP flood attack is initiated by sending a large number of UDP packets to random ports of the targeted system. The targeted system is forced into sending many Destination unreachable UDP packets, thus consuming its resources and leading to DoS. As UDP does not require any connection setup procedure to transfer data, anyone with network connectivity can launch an attack; no account access is needed.
Another example of UDP flood is connecting a host's chargen service to the echo service on the same or another machine. All affected machines might be effectively taken out of service because of the excessively high number of packets produced. In addition, if two or more hosts are so engaged, the intervening network might also become congested and deny service to all hosts whose traffic traverse that network.