In the use case presented below, it is assumed that Trellix NI is integrated with Trellix IPS, which means that the Manager and attached Sensors are able to successfully communicate with the NI appliance and send alert data, flow records and L7 metadata information to NI. It is also assumed that the Trellix NI is connected to a PX appliance which is added to the Client Group configured and associated with the IPS Manager at the domain and/or device level.
Note
Some screenshots and related web features referenced in this section may vary slightly from the latest NI Web UI.
Important
The IP addresses and ports shown in this use case have been used for representation purpose only.
The use case
The → → page in the Manager shows an alert named HTTP: MOVEit Transfer Shell Upload Activity Detected (CVE-2023-34362) which looks suspicious and you want to investigate it further by analyzing the corresponding flow record and alert entry available on the NI Web UI for the same alert.
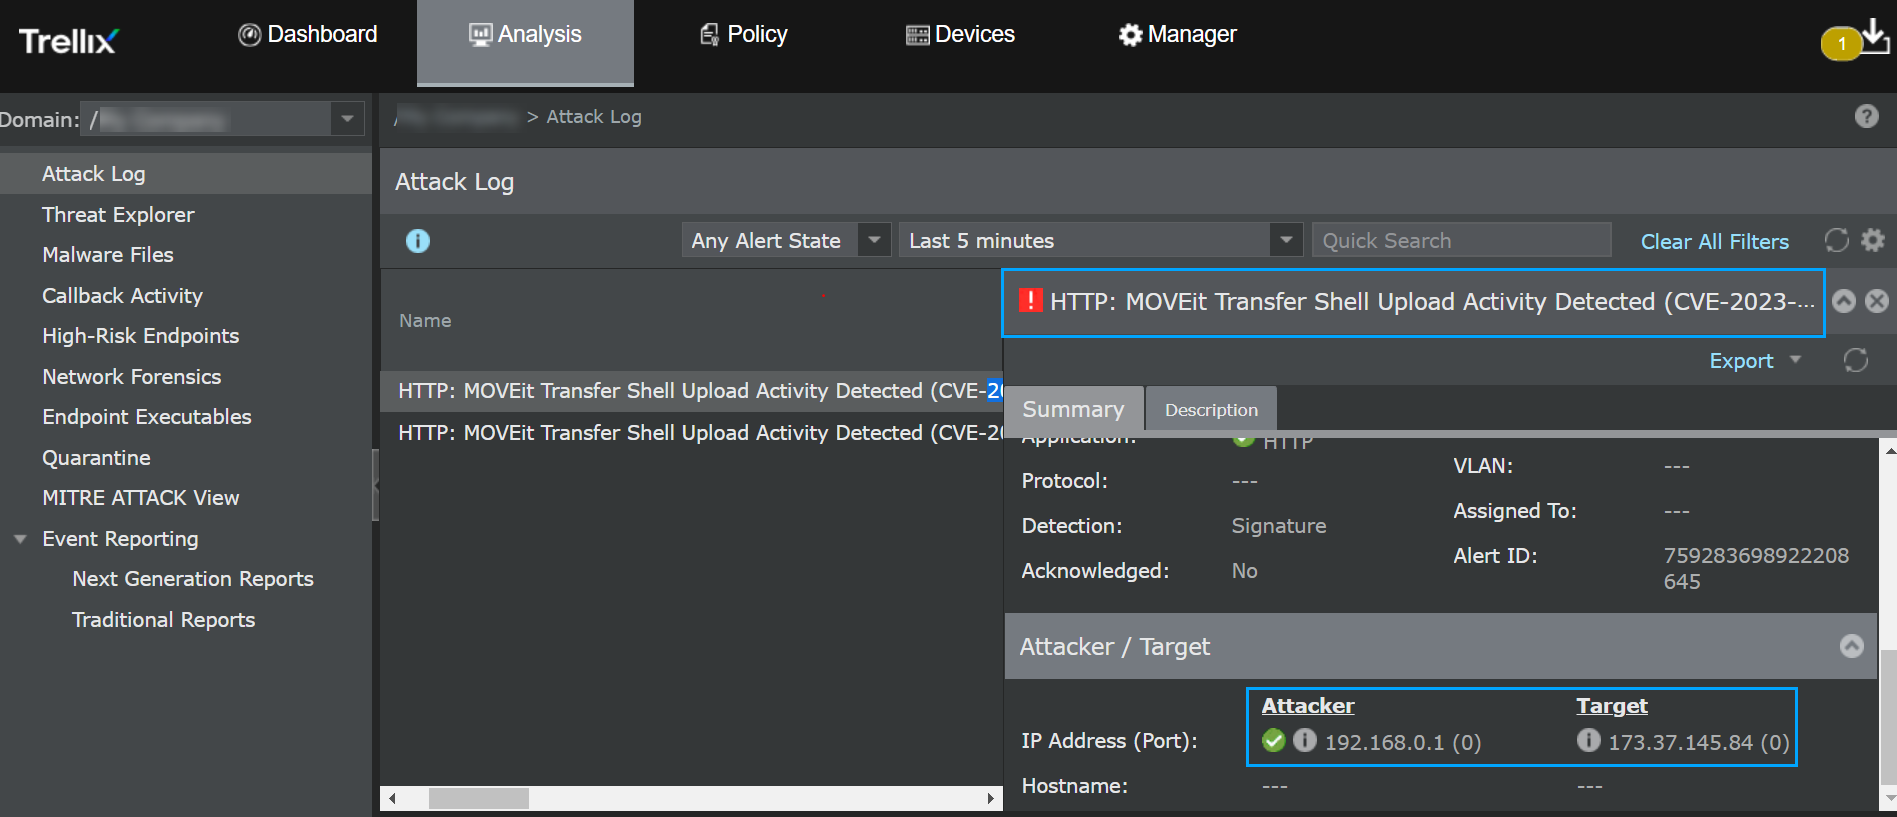
You can obtain the Attacker IP Address/port or Target IP address/port from the Summary tab of the selected alert and then look for the same alert entry in the Alerts page of the NI Web UI. The screenshot below shows the same alert entry located in the Alerts page of NI Web UI.
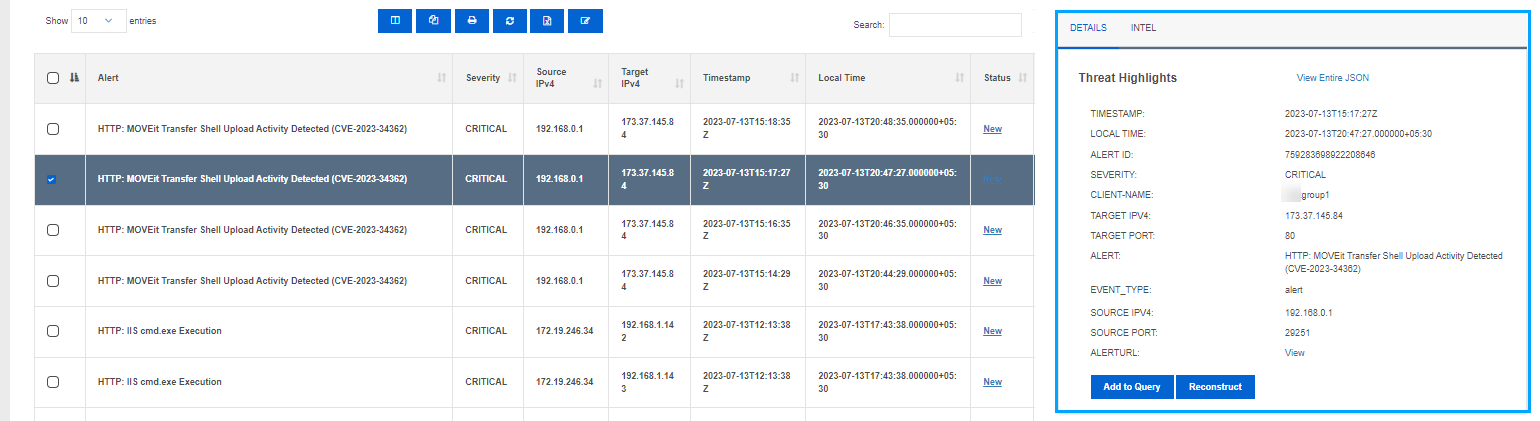
Selecting the alert provides you with detailed information about the alert in Threat Highlights section under the Details tab. To analyze the event further, click the View link beside the ALERTURL field, which redirects you to the Web UI of the associated PX appliance.
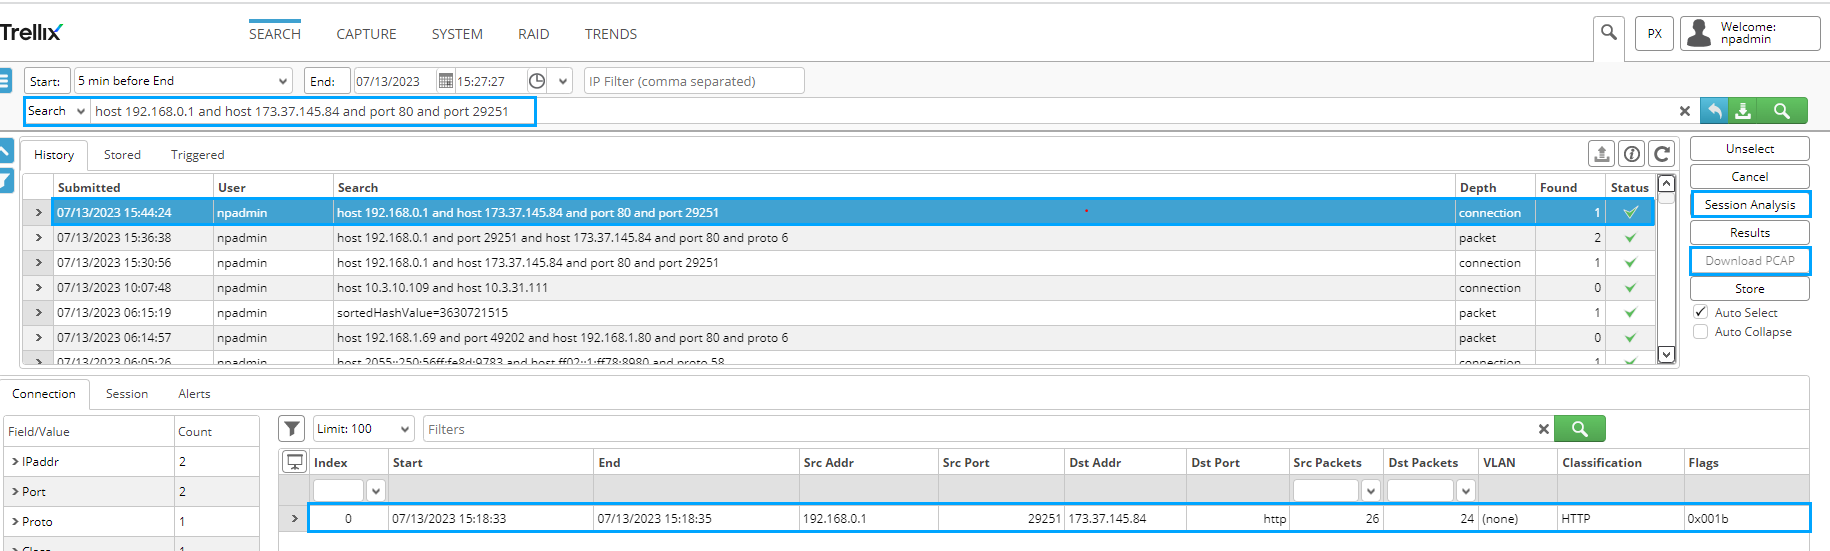
On the PX Web UI, you are redirected to the History tab of the Search page with an entry for the alert being analyzed. You can view the depth of the search (here, the alert), date and time when it was created, number of items found in the search, and its status. If you wish to download the PCAP file related to the alert event, click Session Analysis and then Download PCAP button.
Note
For more information on the PX Platform and how to use it for network investigation, refer to PX Series User Guide.
You can also correlate the alert under analysis to the corresponding netflow to drill down further into the network event. To identify the corresponding netflow, navigate to the Dashboards page of NI Web UI and construct a search query in NI Query Bar using the Attacker/Target IP address or any other data related to the alert. Searching with the query doc_values_type:flowANDsourceIPv4Address:192.168.0.1 shows the corresponding flow entry in the Event Table of the NI Dashboards page, as shown in the screenshot below:
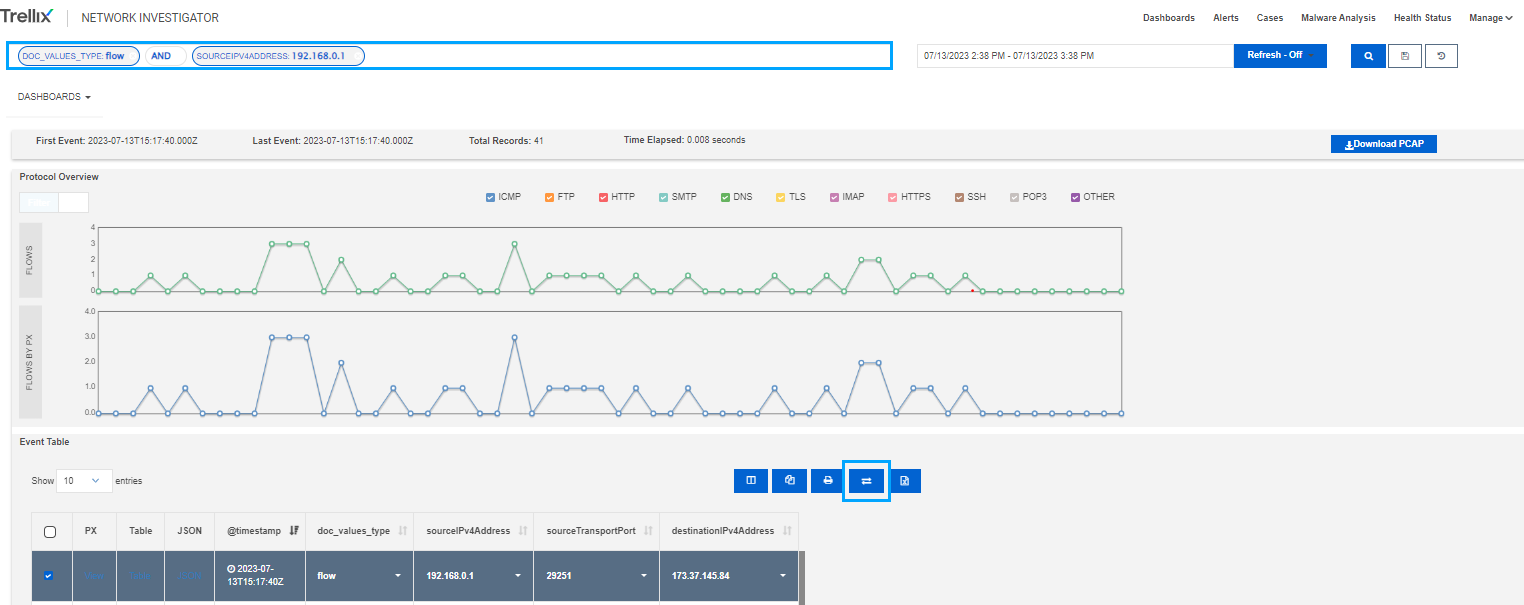
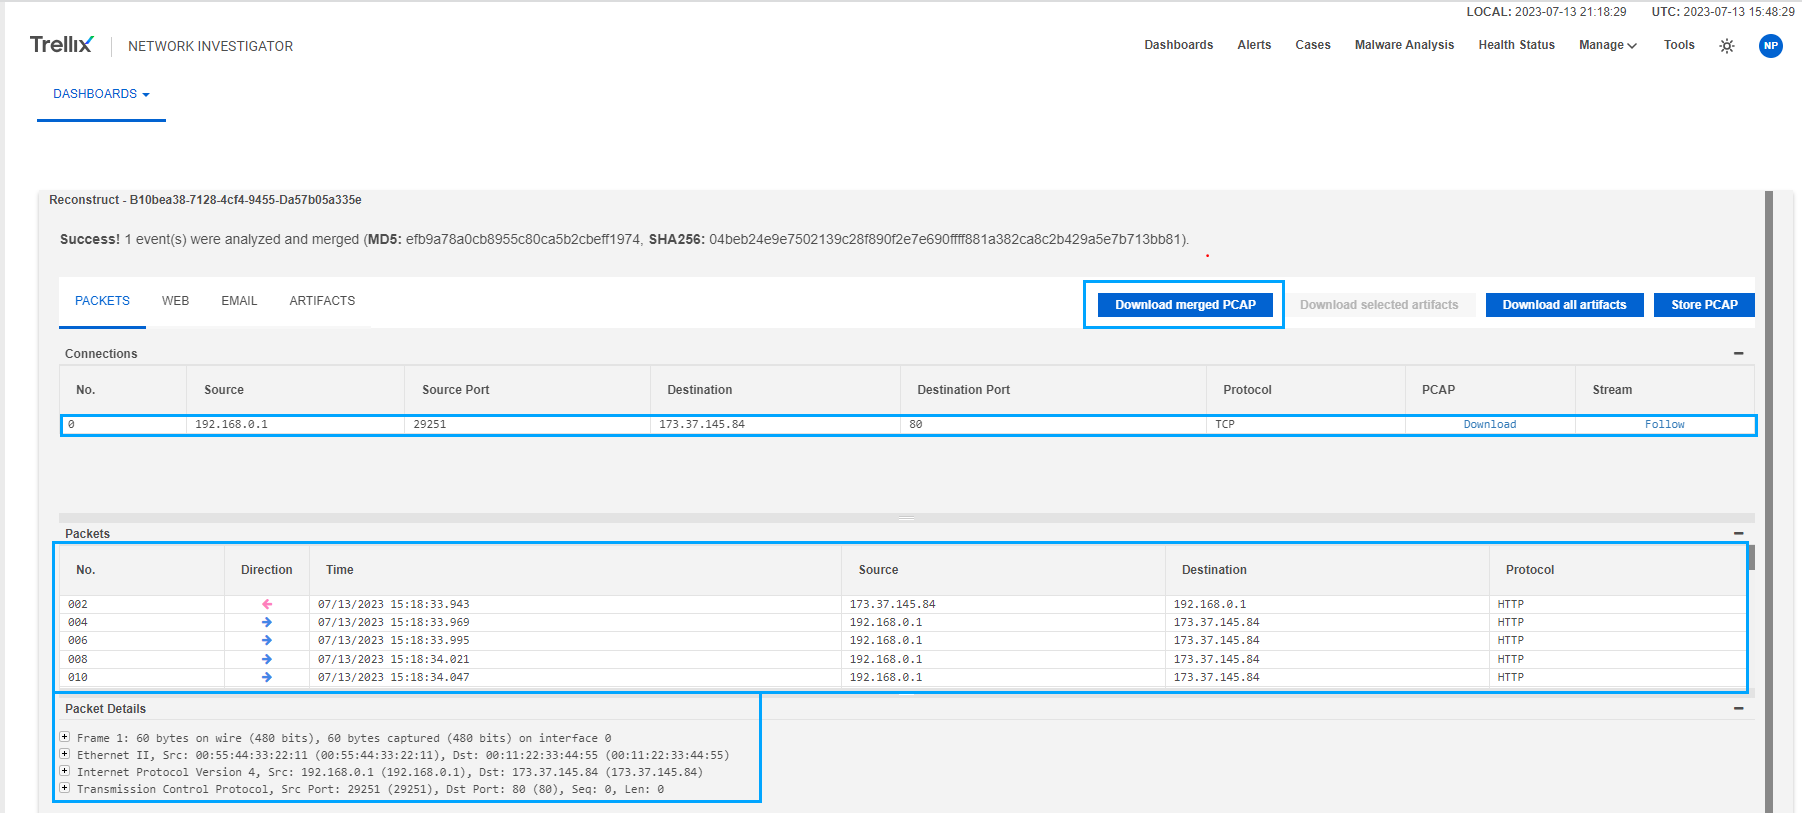
To analyze the packet(s) associated with the netflow being analyzed, select the flow entry on NI and click Reconstruct ( ) icon. It redirects you to the Packets tab within the Dashboards page where you can view the number of connections within the flow. You can also view all packets associated with the flow, packet flow direction, source and destination IPs, source and destination ports, and the packet protocol for each packet session. The Packets tab also allows you to review the hex data of any selected packets in the Hex Details section.
Post your analysis on the information available on the Packets tab, you may download and collect all packets of interest for the selected flow in the PCAP format by clicking the Download Merged PCAP button, which you can further analyze by using any third-party applications, such as WireShark.
Note
For more information on the NI platform and how to use it during the investigation of any network event, refer to Network Investigator User Guide