The  (or, mega menu) → → page of NI Web UI displays all alert data exported by the IPS Manager in a tabular format. Using this page, you can view details of any alert, sort as well as filter the entries further as per your analysis requirement.
You can see the following things when you open the Alerts page in NI:
General alert information: In this section in the top half of the page, you see a summary of all alerts ingested by NI. A chart provides a visual display, by date and risk level, that helps you determine patterns.
General alert information in Alerts page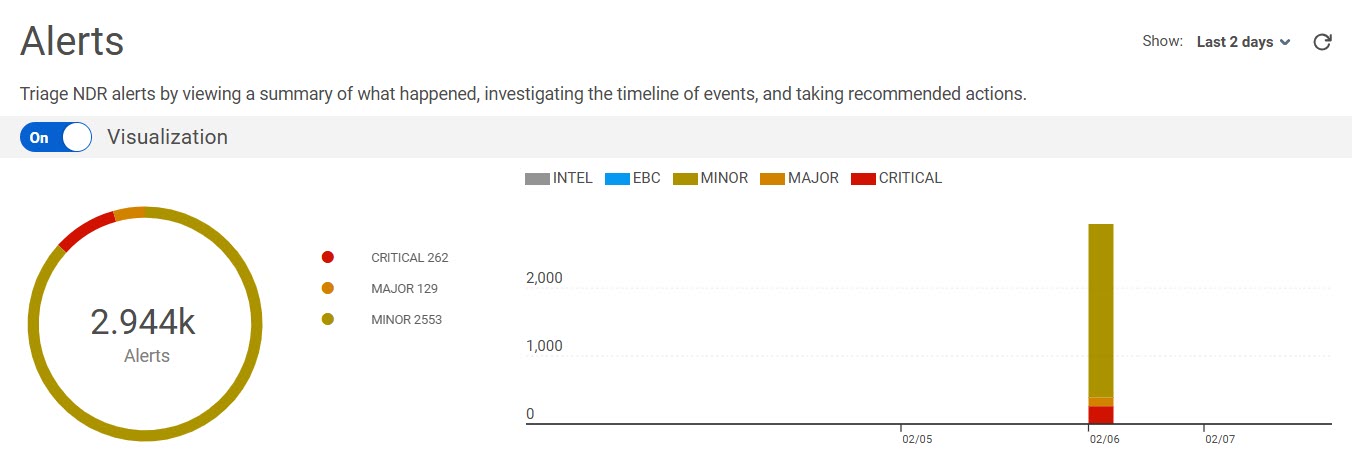
Alerts table: In the lower half of the page, you can view a table displaying all alerts. The table contains multiple columns, such as Alert Name, Severity, Source IP (address), Destination IP (address), Alert Created (time), and Status.
Alerts table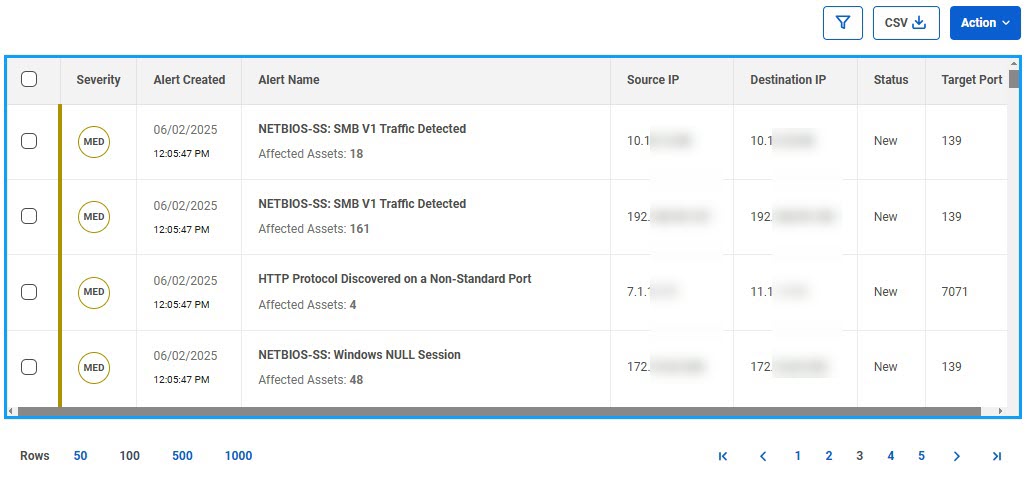
Viewing the specifications of alert data entries in NI
In the Alerts page, when you click any specific alert data entry in the Alert table, the specifications related to that alert is displayed on the right side of the page. This section provides a quick overview of the alert specifications and contains multiple fields, some of which include Severity Level, Alert Details, Asset Details, JSON, and Trellix Intelligence.
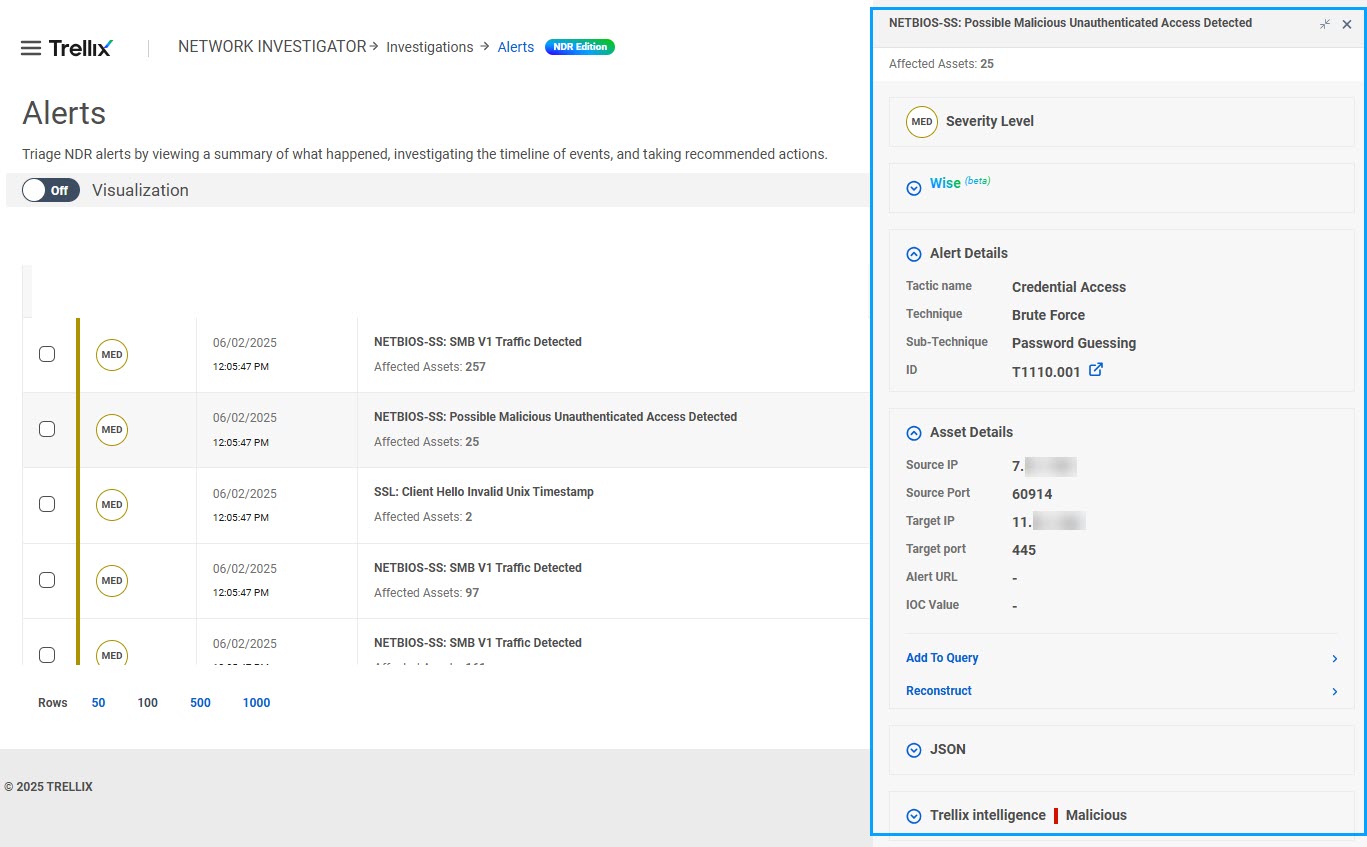 |
If you wish to see more details of an alert for your analysis, select it and then expand the the JSON drop-down. The JSON file format opens displaying more specific details of the selected alert.
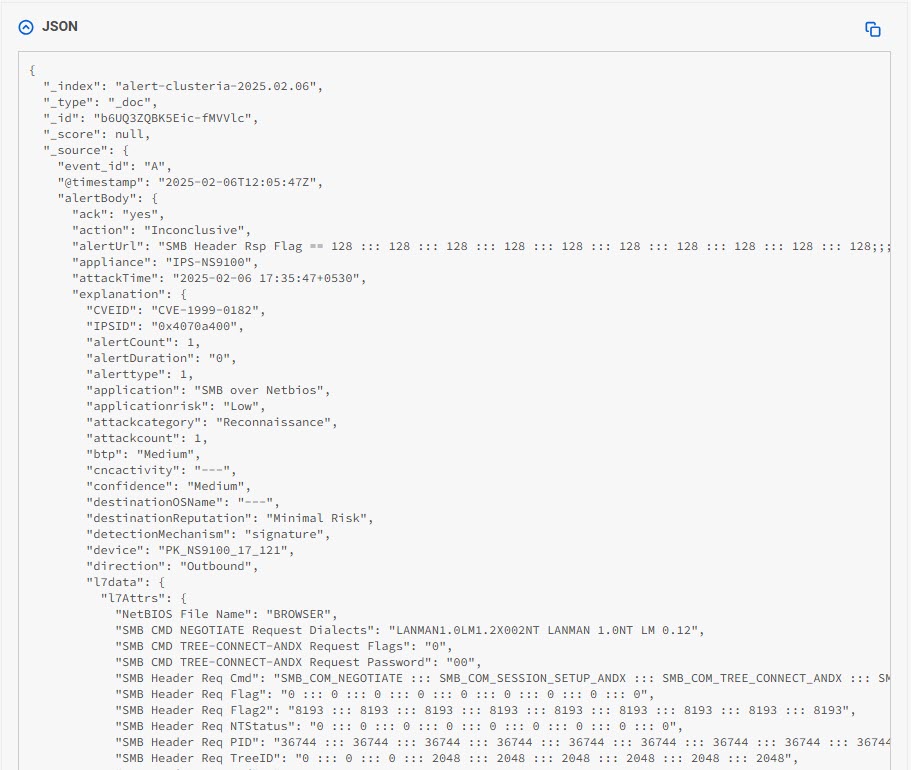 |
In case of alerts related to SmartVision attacks, the Manager sends the SmartVision alert data to Trellix NI as base events. NI consumes and utilizes these base events that enable it to perform more comprehensive and effective analysis and correlation of network activities and potential threats in customer network environments. See Harnessing SmartVision attacks for effective threat detection and response for more information.
Filtering alerts
The Alerts page offers multiple filtering options for easier analysis of the alert data entries, some of which include the following:
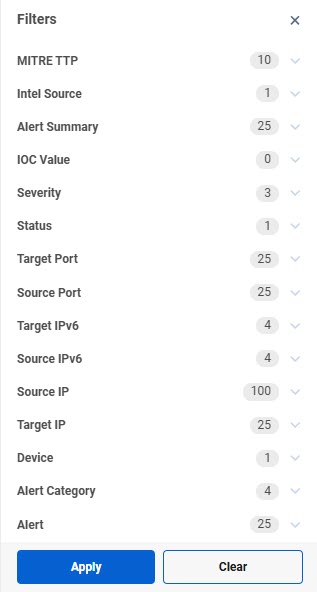
you can modify and narrow down your alert results by applying filters. To do so, click the
 icon located at the top right corner of the page and select the required filter(s). Expand the filter types to view counts for the filter values.
You can configure the number of alert data entries you want to see in the table. The configuration options are 50, 100, 500, and 1000 entries.
You can export the table content containing the alert data entries by generating a .CSV file. To do so, click the
 icon and download the file.
For more information on the NI platform and how to use it during the investigation of any network event, refer to Network Investigator User Guide.