The Adversarial Tactics, Techniques, and Common Knowledge (ATT&CK) is a well-known and publicly available knowledge base developed by MITRE Corporation that highlights the tactics, techniques, and procedures (TTPs) used by cyber adversaries in different phases of attack lifecycle. These details are presented in the form of a matrix that showcases the tactics, techniques, and associated sub-techniques employed by cyber attackers in real-world scenarios.
The Analysis → <Admin Domain Name> → MITRE ATTACK View page in the Trellix IPS Manager provides a consolidated view of all adversarial tactics, techniques and sub-techniques in the MITRE ATT&CK matrix format for attacks detected on the network. It also provides users with further drill-down capabilities, such as applying filters based on the attack severity level or IP address, and delving into any specific technique/sub-technique to view only the attacks that fall under those categories. It thus can help in identifying security gaps, analyzing existing IPS policies, and strengthening network security for future.
Note
This page is not available in Trellix IPS Central Manager.
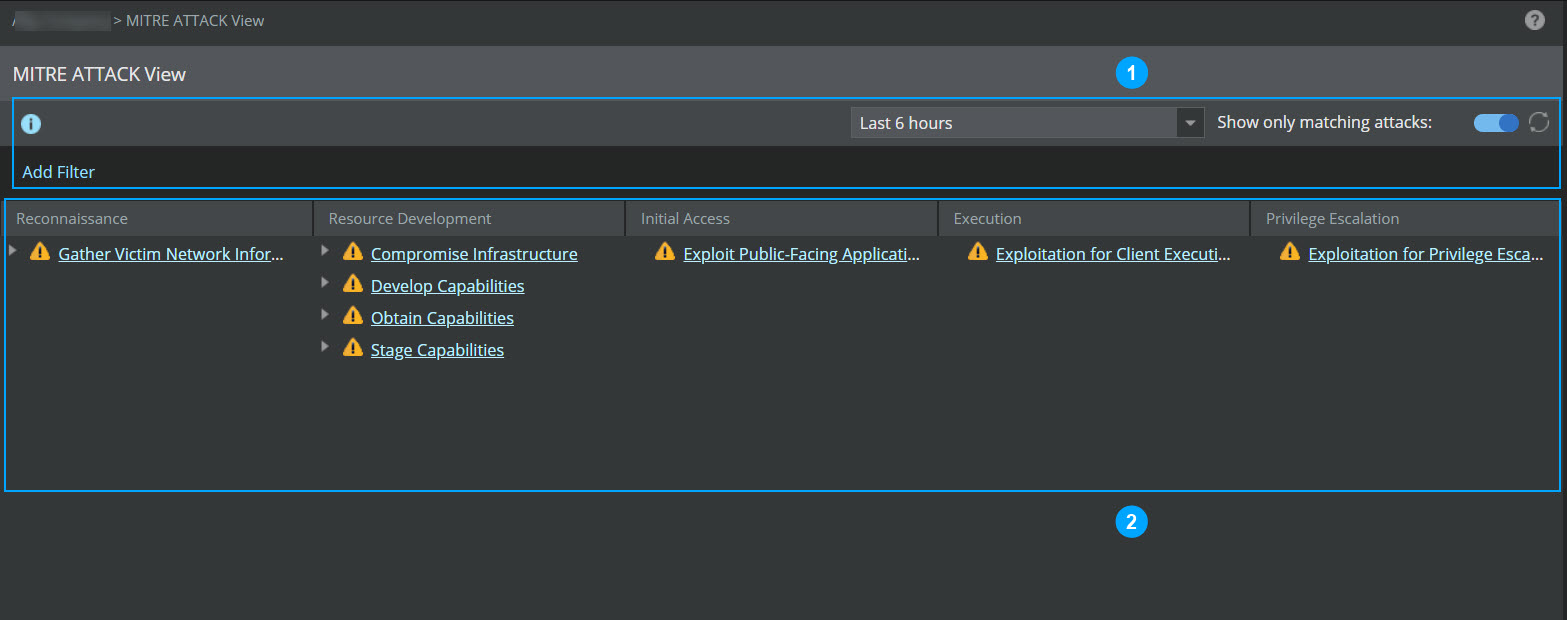
Callout | Description |
|---|---|
1 | Top menu |
2 | Grid view |
The following options are available in the MITRE ATTACK View page:
Options | Description |
|---|---|
Top menu | |
 | This provides an overview of the MITRE ATTACK View page. |
Time period | When this option is selected, it shows the tactics, techniques and/or sub-techniques associated with the attacks for the chosen time period. The minimum time is Last 5 minutes. The matrix data can be also filtered for any time period of your preference using the Custom Time Period option. |
 | Clicking this icon refreshes the page. |
Show only matching attacks | This option comes with a toggle button with the following functionality:
|
 | This option enables you to add a filter based on IP addresses and attack severity levels. |
Grid view
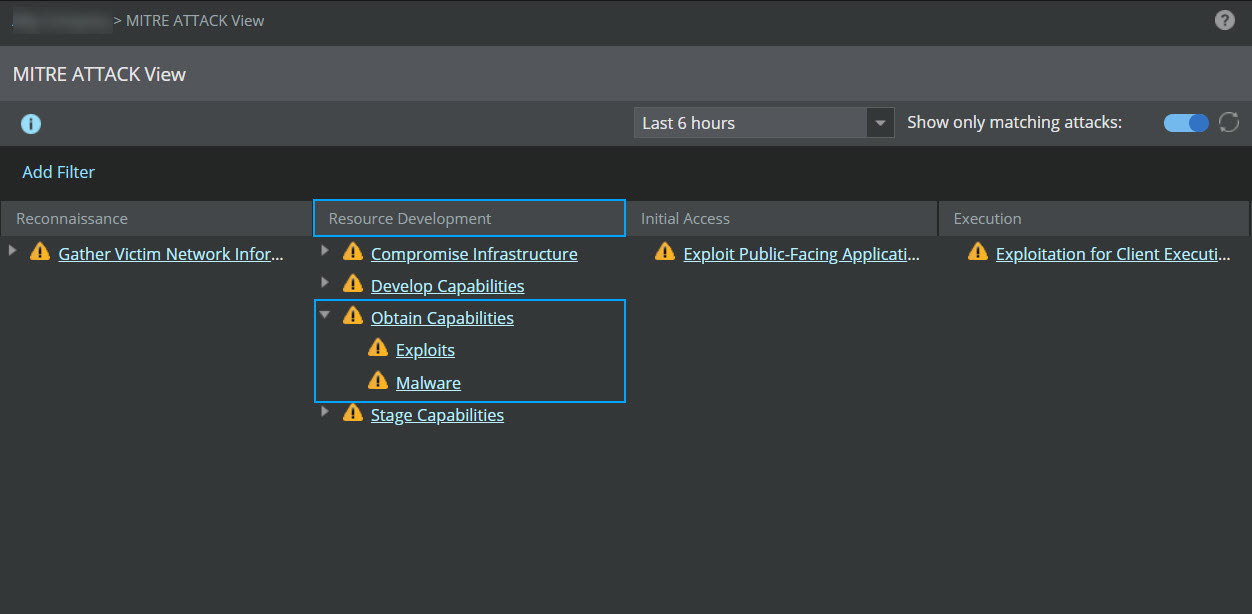
The grid view of the MITRE ATTACK View page displays the MITRE ATT&CK matrix structure in which the adversarial tactics are organized as column headings. Cells appearing under each column are the techniques employed by cyber adversaries to achieve the tactical objectives. You can expand any technique to view the corresponding sub-technique(s), if any. The tactics, techniques and sub-techniques preceded with the  icon indicate the presence of attack entries. For example, the figure below shows the Mitre matrix view for all the matching attacks where we can see Obtain Capabilities as one of the adversarial techniques under the tactic column Resource Development. Expanding the technique reveal two corresponding sub-techniques - Exploits and Malware.
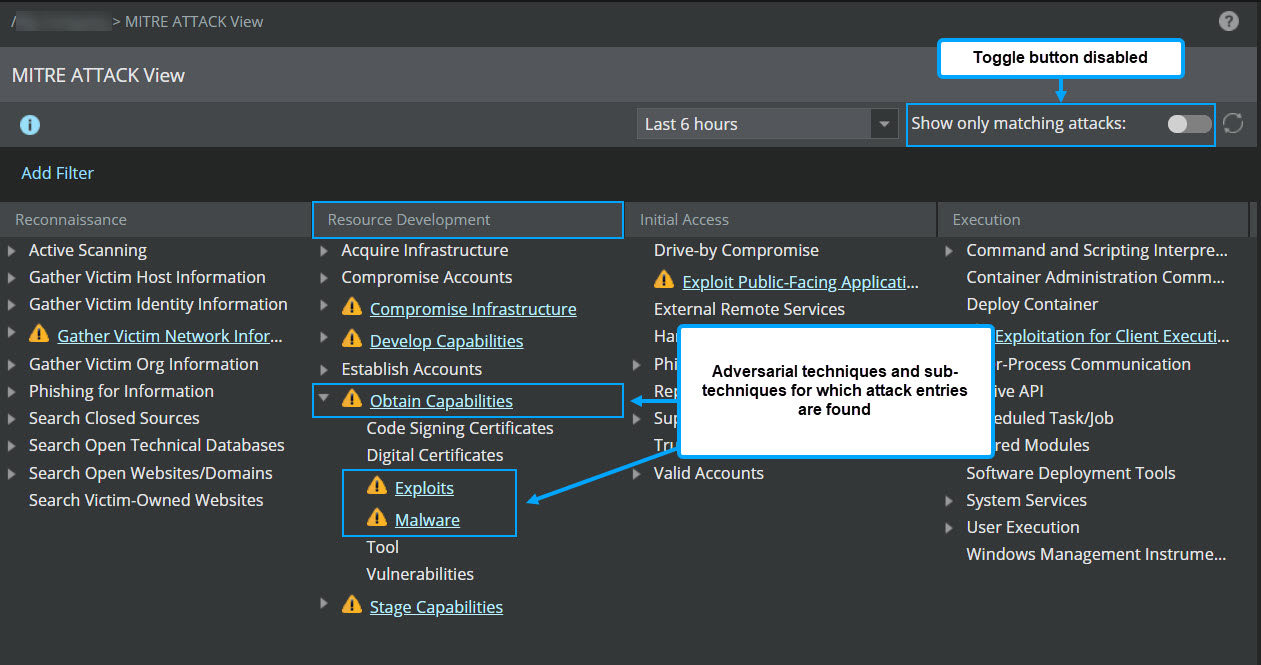
When the Show only matching attacks toggle button is off, the page shows all the adversarial tactics, techniques and sub-techniques in which the hyperlinked entries for techniques and sub-techniques starting with icon represent the matching attacks.
The MITRE ATTACK View page can be customized by different options, such as sorting and filtering, which help drilling down into the attack details based on your requirement. The following options are available:
Sort Ascending: You can sort all columns in the ascending order.
Sort Descending: You can sort all columns in the descending order.
You can also apply filters based on IP address and/or attack severity levels. For more information, refer to the section Adding filters. For information on how to drill down on attacks in the MITRE ATTACK View page, refer to the section Analyzing attack details using matching tactic, technique, or sub-technique.