FIREEYE TECHNICAL DOCUMENTATION
NX SERIES
HARDWARE ADMINISTRATION GUIDE
NX10450 (REGULATORY MODEL: FOR HARDWARE ONLY)
NX SERIES / 2017
FireEye and the FireEye logo are registered trademarks of FireEye, Inc. in the United States and other countries. All other trademarks are the property of their respective owners.
FireEye assumes no responsibility for any inaccuracies in this document. FireEye reserves the right to change, modify, transfer, or otherwise revise this publication without notice.
Copyright © 2017 FireEye, Inc. All rights reserved.
NX 10450 Hardware Administration Guide
Revision 6
FireEye Contact Information:
Website: www.fireeye.com
Support Email: support@fireeye.com
Support Website: csportal.fireeye.com
Phone:
United States: 1.877.FIREEYE (1.877.347.3393)
United Kingdom: 44.203.106.4828
Other: 1.408.321.6300
Contents
CONTENTS
CHAPTER 1: The FireEye NX 104507
The Front View .............................................................. 8
Bezel .................................................................. 8
Buttons ................................................................ 8
LEDs .................................................................... 8
Chassis ................................................................. 9
The Rear View ............................................................. 10
Power Port .............................................................. 10
I/O Ports ............................................................... 11
Management Ports ................................................... 11
Monitoring Ports ..................................................... 11
CHAPTER 2: Deployment13
Deployment Mode Overview ............................................. 13
Inline Deployment Modes .............................................. 13
Inline Deployment .................................................... 13
Prerequisites .......................................................... 14
Cabling .................................................................. 14
Inline Proxy Deployment ............................................. 14
Prerequisites .......................................................... 15
Cabling .................................................................. 15
Out-of-Band Deployment Modes ..................................... 16
Test Access Point Deployment ....................................... 16
Prerequisites .......................................................... 17
Cabling .................................................................. 17
Port Mirroring (SPAN) Deployment ................................. 17
Prerequisites .......................................................... 18
© 2017 FireEye
3
Contents
Cabling ................................................................................................18
CHAPTER 3: Installation ..............................................................19
Before You Begin ...............................................................................19
Site Requirements ................................................................................20
Installation Site Guidelines .............................................................20
Rack Precautions ................................................................................20
Server Precautions .............................................................................21
Rack-Mounting Precautions ...........................................................21
Ventilation Requirements .....................................................................21
Cabling Requirements .........................................................................21
Power Requirements ...........................................................................22
Rack Installation ..................................................................................22
Installing the Inner Rails on the Appliance ........................................22
Installing the Outer Rails on the Rack ..............................................24
Mounting the Appliance on the Rack ................................................26
Attaching Cables to your Appliance ..................................................27
Turning On the Appliance ...................................................................27
CHAPTER 4: Baseline Configuration ................................................29
Network Information Requirements ..................................................29
Configuring the Appliance via the LCD Panel ...................................30
LCD Panel Navigation Buttons ........................................................30
LCD Panel Menus ...............................................................................30
Required Ports and Protocols ............................................................33
CHAPTER 5: Replacements ............................................................35
Return Process ..................................................................................35
Replacing an Appliance Including Disk Drives ..................................37
Replacing an Appliance Excluding Disk Drives ..................................37
Backing Up and Restoring the Appliance Database .............................38
Backing Up and Restoring the Appliance Database Using Release 7.4 and Earlier 39
4
© 2017 FireEye
Contents
Backing Up the Appliance Configuration ........................................39
Backing Up the Appliance Database ..................................................39
Restoring the Appliance Configuration ...........................................40
Restoring the Appliance Database ..................................................41
Backing Up and Restoring the Appliance Database Using Release 7.5 and Later .41
Backing Up the Appliance Database ...........................................41
Restoring the Appliance Database ................................................43
Applying License Keys ..........................................................44
Identifying the Failed Disk Drive ................................................45
Removing and Replacing an NX 10450 Disk Drive ..................................45
Removing and Replacing an NX 10450 Power Supply Unit ...........................48
Appendices ..........................................................51
Appendix 1: System Specifications ............................................51
Appendix 2: Product Compliance Information ...................................52
Technical Support .....................................................55
Documentation ........................................................55
© 2017 FireEye
5
Contents
6
© 2017 FireEye
NX Series Hardware Administration Guide
CHAPTER 1: The FireEye NX 10450
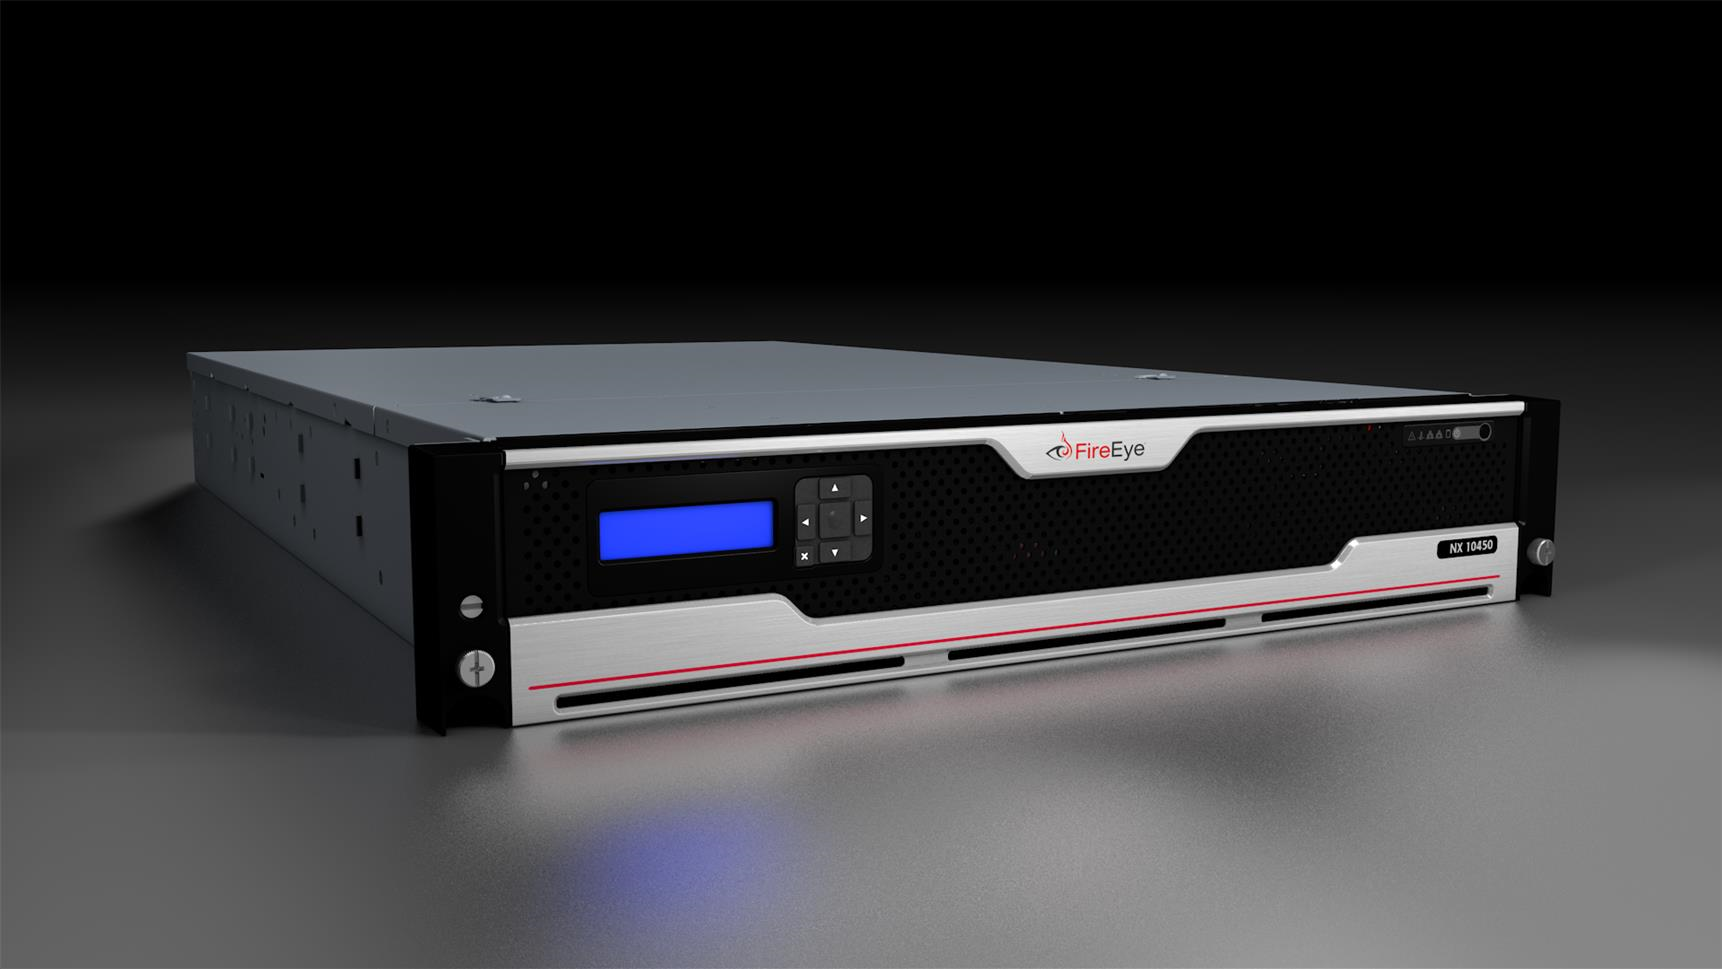
The FireEye NX 10450 stops the new generation of cyber attacks that use zero-day Web exploits and multiprotocol malware callbacks to compromise the majority of today's networks.
When used as a standard (or integrated) appliance, the NX Series appliance performs both monitoring and analysis functions. When used as a sensor within the FireEye Network Security, the NX 10450 only monitors traffic, extracting objects and URLs and sending them to an MVX cluster for analysis. This allows a flexible approach to your security solution.
 For information about using the NX Series appliance as a sensor, see the Network Security Deployment Guide for your software release.
© 2017 FireEye 7
NX Series Hardware Administration Guide
CHAPTER 1: The FireEye NX 10450
The Front View
The NX 10450 comes with a sleek removable bezel that can be removed to access the chassis.

The bezel shown has screws at each end. Your model may not have screws, but it is otherwise identical to the one shown.
Bezel
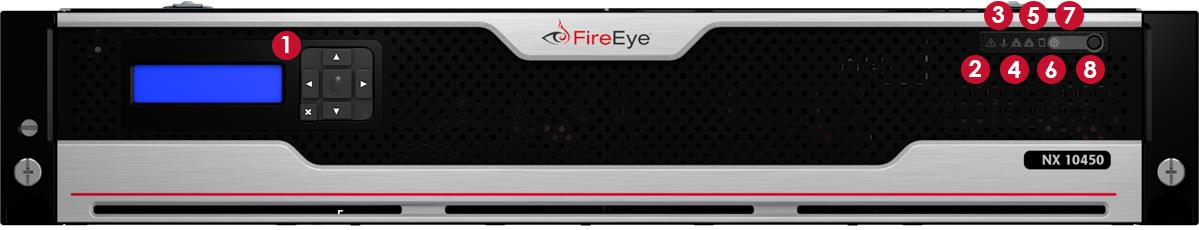
| 1) LCD Panel Navigation Buttons | 5) Management 2 LED |
| 2) Power Fail LED | 6) HDD LED |
| 3) System Health Indicator LED | 7) Power LED |
| 4) Management 1 LED | 8) Power Button |
Buttons
The bezel has seven buttons: six LCD panel navigation buttons and one power button. Use them to perform basic operations of the appliance.
- LCD Panel Navigation: Use the navigation buttons to perform basic configuration of the appliance. See Configuring the Appliance via the LCD Panel on page 30 for more information.
- Power: Use the power button to turn the appliance on or off. Turning off the power with this button removes the main power but keeps the standby power supplied to the appliance. Therefore, unplug the appliance before servicing.
LEDs
The front panel has LEDs that provide critical information about parts of the appliance. The following table describes each LED.
The Front View
| LED | Flashing | Steady | Off | Normal State |
|---|---|---|---|---|
Power Fail | N/A | Not drawing power | Drawing power | Off |
System Health Indicator | Flashing and amber indicates a fan failure |
Steady and amber indicates a power supply failure or overheat condition, which may be caused by cables obstructing the airflow in the appliance or the ambient room temperature being too high. | Operating normally | Off |
Management 1 | Activity via management 1 port | N/A | No activity | Green and flashing |
Management 2 | Activity via management 2 port | N/A | No activity | Green and flashing |
Power | N/A | Operating normally | Not drawing power | Green and steady |
HDD | Degraded SAS drive connection | N/A | Operating normally | Off |
Chassis
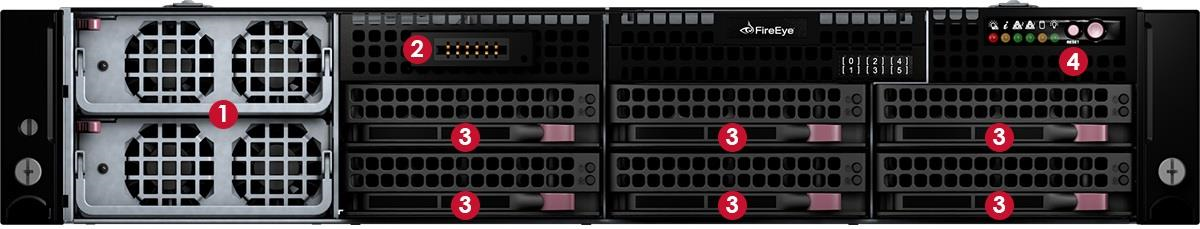
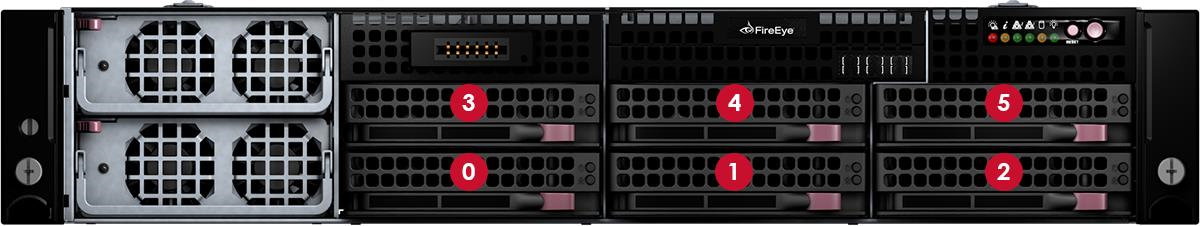
The drive map on the appliance located to the left of the LEDs may be incorrect. See Removing and Replacing an NX 10450 Disk Drive on page 45 for the correct disk slot identification.
| 1) Power Supply Units | 3) Disk Drive Carrier |
| 2) LCD Panel Port | 4) Reset Button |
© 2017 FireEye
9
- Power Supply Units: These units are redundant, hot-swappable 1400W power supplies. See Removing and Replacing an NX 10450 Power Supply Unit on page 48 for more information.
- LCD Panel Port: The LCD panel on the bezel connects to this port for power.
- Disk Drive Carrier: Each carrier can house a hot-swappable disk drive. See Removing and Replacing an NX 10450 Disk Drive on page 45 for more information.
- Reset Button: Use the reset button to reboot the system.
The Rear View
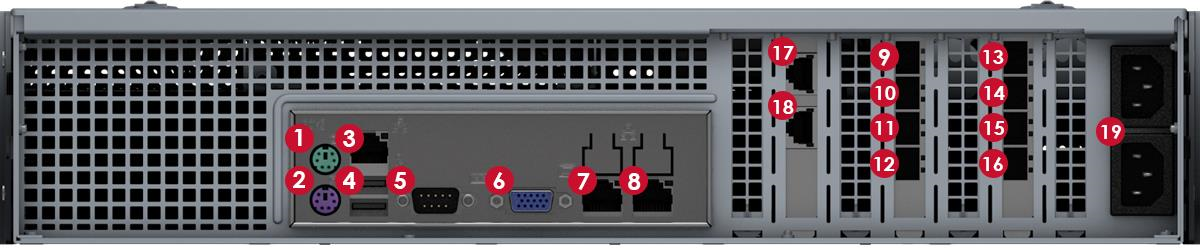
1) PS/2 Mouse Port | 11) pether5 (SFP+) Monitoring 5 Port |
2) PS/2 Keyboard Port | 12) pether6 (SFP+) Monitoring 6 Port |
3) IPMI/Serial over Ethernet Port | 13) pether7 (SFP+) Monitoring 7 Port |
4) USB Ports | 14) pether8 (SFP+) Monitoring 8 Port |
5) Serial Console Port | 15) pether9 (SFP+) Monitoring 9 Port |
6) Video Port | 16) pether10 (SFP+) Monitoring 10 Port |
7) ether1 (RJ45) Management 1 Port | 17) HA1 (RJ45) High Availability Control Port |
8) ether2 (RJ45) Management 2 Port | 18) HA2 (RJ45) High Availability Data Port |
9) pether3 (SFP+) Monitoring 3 Port | 19) Power Ports |
10) pether4 (SFP+) Monitoring 4 Port |
|
Power Port
- Power: Connect your power source to this port to provide power to the appliance. The appliance comes with one redundant power supply unit for use if the primary
© 2017 FireEye
10
The Rear View
unit fails. See Removing and Replacing an NX 10450 Power Supply Unit on page 48 for more information.
I/O Ports
- Mouse: Connect a mouse to this port to manage the appliance locally.
- Keyboard: Connect a keyboard to this port to manage the appliance locally.
- Video: Connect a monitor to this port to view the appliance's command-line interface.
- USB: The port is USB 2.0 compliant.
- Serial Console: Connect to this port to manage the appliance from your terminal.
Management Ports
- ether (RJ45): Connect your LAN to this port to enable remote access to the CLI and Web UI. The RJ45 connector is a 10/100/1000BASE-T port.
- IPMI: Connect for access to out-of-band management functions, including power control, console redirection, and appliance health status. The connector is a 100BASE-T port.
Monitoring Ports

Each interface pair is physically and logically segregated from other interface pairs, preventing communication between the different network segments.
- pether (SFP+): The SFP+ connectors accept the following modules:
- 1000BASE-SX/10GBASE-SR (LC MMF)
- 1000BASE-LX/10GBASE-LR (LC SMF)
- 1000BASE-T (RJ45)
- 10GBASE-CU (5m direct attach cable)
Pether3–10 support data rates up to 10 Gbps. Connect the switch port you want to monitor to this port.

Link partners connected to the same port pair must have the same data transmission rates (1 Gbps or 10 Gbps). The port pairs are as follows:
- pether3 and pether4
- pether5 and pether6
- pether7 and pether8
- pether9 and pether10
© 2017 FireEye 11
NX Series Hardware Administration Guide
CHAPTER 1: The FireEye NX 10450
Contact Customer Support to order the appropriate transceiver modules.
- HA (RJ45): The High Availability ports are for connecting your appliance to another NX 10450 for detection redundancy. See the NX Series High Availability Guide of your software release for more information.
12
© 2017 FireEye
NX Series Hardware Administration Guide
Deployment Mode Overview
CHAPTER 2: Deployment
This chapter describes how to deploy the NX 10450 appliance in your network.
Deployment Mode Overview
There are multiple modes that can be used to install the NX Series appliance on your network, and each method offers specific costs and benefits.
FireEye strongly recommends using an inline deployment mode. An appliance deployed inline can automatically block attacks and callbacks to Command and Control (CnC) servers. With inline deployment, recovering from a malware attack is faster and less resource-intensive.
Deployment modes include:
Inline Deployment Modes
An inline deployment provides high security by blocking all malicious traffic from reaching your network.
FireEye NX Series appliances can be deployed inline with the following network configurations:
- Inline Deployment below
- Inline Proxy Deployment on the next page
Inline Deployment
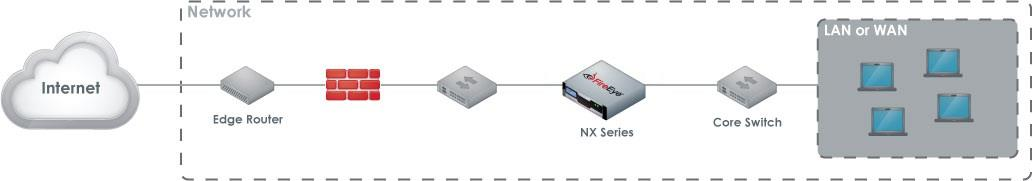
The diagram below illustrates the deployment of an NX 10450 appliance installed between the LAN and the firewall in a typical network topology.
[IMAGE PLACEHOLDER: Diagram showing an NX 10450 appliance deployed inline between the LAN and the firewall in a typical network topology.]
© 2017 FireEye
NX Series Hardware Administration Guide
CHAPTER 2: Deployment
Prerequisites
Before connecting the NX10450 to your network, ensure that your network devices that will connect to pether3—6 provide data transmissions no greater than 10 Gbps and the network devices that will connect to and pether7—10 provide output no greater than 1 Gbps. Also ensure that they provide output via one of the following:
1000BASE-SX (LC MMF)
1000BASE-LX (LC SMF)
1000BASE-T (RJ45)
10GBASE-Cu (5m direct attach cable)
Cabling
Connect the appropriate cables to the NX 10450 appliance's ports as follows:
ether1: Connect one end of the cable to the NX 10450 appliance's ether1 port, and connect the other end to your LAN-facing switch. This will enable you to access the appliance's Web UI.
pether3: Connect one end of the cable to the NX 10450 appliance's pether3 port, and connect the other end to your LAN-facing switch.
pether4: Connect one end of the cable to the NX 10450 appliance's pether4 port, and connect the other end to the Internet-facing switch.
You can monitor up to three more network segments by connecting additional Internet-facing switches and LAN-facing switches to pether5—10. Pether5 and pether6 can support up to 10 Gbps of traffic, and pether7—10 support up to 1 Gbps of traffic.
Inline Proxy Deployment
In an inline with proxy deployment, the NX 10450 appliance monitors both proxy and non-proxy traffic inline. The following diagram illustrates the inline proxy deployment in a typical network topology.
Inline Deployment Modes
If your environment contains Web proxies or other NAT devices that obscure incoming IP addresses, deploy the NX device so that it sees Web traffic from the internal (or LAN) side of the proxy. If you place the NX device on the external side of the proxy, the NX appliance reports a malicious site as being the LAN IP of the proxy.

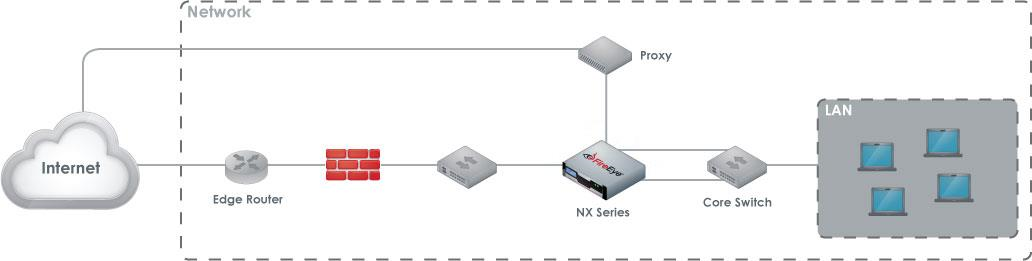
Connect your NX 10450 appliance between two routers or switches on your network, and to your proxy.
Prerequisites
Before connecting the NX 10450 to your network, ensure that your network devices that will connect to pether3—6 provide data transmissions no greater than 10 Gbps and the network devices that will connect to and pether7—10 provide output no greater than 1 Gbps. Also ensure that they provide output via one of the following:
- 1000BASE-SX (LC MMF)
- 1000BASE-LX (LC SMF)
- 1000BASE-T (RJ45)
- 10GBASE-Cu (5m direct attached cable)
Cabling
Connect the appropriate cables to the NX 10450 appliance’s ports as follows:
- ether1 cable: Connect one end of the cable to the NX 10450 appliance’s ether1 port, and connect the other end to your LAN-facing switch. This will enable you to access the appliance’s Web UI.
- pether3 cable: Connect one end of the cable to the NX 10450 appliance’s pether3 port, and connect the other end to the LAN-facing switch.
- pether4 cable: Connect one end of the cable to the NX 10450 appliance’s pether4 port, and connect the other end to the proxy server.
NX Series Hardware Administration Guide
CHAPTER 2: Deployment
- pether5 cable: Connect one end of the cable to the NX 10450 appliance’s pether5 port, and connect the other end to the LAN-facing switch.
- pether6 cable: Connect one end of the cable to the NX 10450 appliance pether6 port, and connect the other end to the Internet-facing switch.
You can monitor up to two more proxy servers by connecting additional proxies and LAN-facing switches to pether7—10. Pether7—10 support up to 1 Gbps of traffic.
Out-of-Band Deployment Modes
Out-of-band deployment modes only monitor malicious content as it enters your network; they do not block malicious content.
FireEye appliances can be deployed out of band with the following existing network configurations:
- Test Access Point Deployment below
- Port Mirroring (SPAN) Deployment on the facing page
Test Access Point Deployment
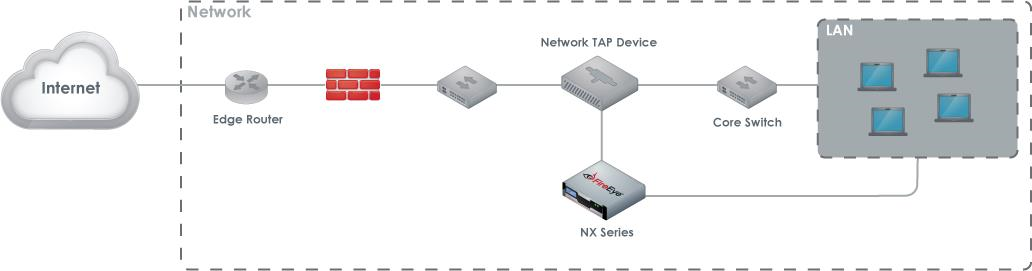
Test Access Point (TAP) uses a TAP device to provide a real-time duplicate copy of the network traffic through the network.
Test Access Points have the following limitations:
- You must purchase a separate TAP device to deliver packets to the NX Series device.
- A TAP deployment does not block malware from accessing your network.
To deploy the FireEye NX Series appliance using a TAP device, you first connect the TAP device inline to your network. You then connect the FireEye NX Series monitoring ports to the ingress and egress ports on the TAP device. The following diagram illustrates the TAP deployment in a typical network topology.
16
© 2017 FireEye
Out-of-Band Deployment Modes
Prerequisites
Before connecting the NX 10450 to your network, ensure that your network devices that will connect to pether3—6 provide data transmissions no greater than 10 Gbps and the network devices that will connect to and pether7—10 provide output no greater than 1 Gbps. Also ensure that they provide output via one of the following:
- 1000BASE-SX (LC, MMF)
- 1000BASE-LX (LC, MMF)
- 1000BASE-T (RJ45)
- 10GBASE-Cu (5m direct attach cable)
Cabling
Connect the appropriate cables to the NX 10450 appliance’s ports as follows:
- ether1: Connect one end of the cable to the NX 10450 appliance’s ether1 port, and connect the other end to your LAN-facing switch. This will enable you to access the appliance’s Web UI.
- pether3: Connect one end of the cable to the NX 10450 appliance’s pether3 port, and connect the other end to your TAP device.
Port Mirroring (SPAN) Deployment
Port mirroring deployment, also known as Switch Port Analyzer (SPAN) packet capture, is usually the least expensive option in a low-traffic network environment. To set up port mirroring, you configure a router or switch with port mirroring capability to forward a copy of incoming and outgoing traffic passing between selected ports to SPAN ports on the switch. Then connect the SPAN ports to the appliance.
Port mirroring has the following limitations:
- Heavily used networks may result in dropped packets that are not passed to the NX Series appliance.
- Port mirroring is active packet duplication. The router or switch uses its processing power to mirror the network packets and pass these packets to the NX Series device. In a heavily used network, the network quality and response times tend to degrade.
- The router or switch must be configured to provide port-mirrored data to the NX Series appliance. Maintenance costs for this configuration can be higher than other configurations.
- Detected malware cannot be prevented from accessing your network.
- SPAN port connectivity issues may cause delays in your deployment. You may need to add a few days to troubleshoot the connectivity issues.
The following diagram illustrates the port mirroring deployment in a typical network topology.
[IMAGE PLACEHOLDER: Diagram illustrating port mirroring (SPAN) deployment in a typical network topology]
© 2017 FireEye
17
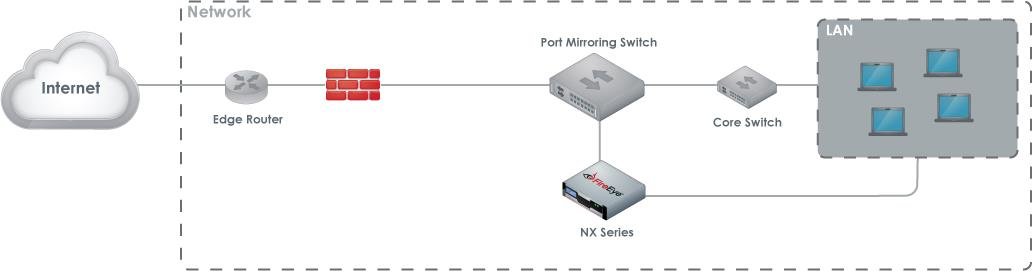

You must configure the SPAN port correctly and test it to make sure that the mirroring ports are passing all of the traffic you want to monitor. This usually requires an administrator with networking expertise who can set up the SPAN port and run TCPDump or WireShark to monitor the traffic and verify that there is bi-directional TCP port 80 (HTTP) traffic passing through the port.
Prerequisites
Before connecting the NX 10450 to your network, ensure that your network devices that will connect to pether3—6 provide data transmissions no greater than 10 Gbps and the network devices that will connect to and pether7—10 provide output no greater than 1 Gbps. Also ensure that they provide output via one of the following:
- 1000BASE-SX (LC MMF)
- 1000BASE-LX (LC SMF)
- 1000BASE-T (RJ45)
- 10GBASE-Cu (5m direct attach cable)
Cabling
Connect the appropriate cables to the NX 10450 appliance’s ports as follows:
- ether1: Connect one end of the cable to the NX 10450 appliance’s ether1 port, and connect the other end to your LAN-facing switch. This will enable you to access the appliance’s Web UI.
- pether3: Connect one end of the cable to the NX 10450 appliance’s pether3 port, and connect the other end to your SPAN device.
NX Series Hardware Administration Guide
CHAPTER 3: Installation
This chapter provides information about the site requirements of your installation location.
Before You Begin
Follow the steps in this section before you install the appliance.
Before Opening the Box
- Review the Packing Slip contained in the plastic slip attached to the top of the box. Ensure the shipment contains the correct appliance and any additional items you may have ordered, such as a subscription to the Dynamic Threat Intelligence Cloud or the correct level of customer support.
- Ensure the serial number listed on the Packing Slip matches the one specified on the sticker located on one side of the box.
- If there appears to be damage to the box, file a damage claim with the carrier who delivered it.
Unpacking the Appliance
Carefully remove the appliance from the box in an area away from heat, electrical noise, and electromagnetic fields.
Ensure your box contains:
- The correct appliance model
- One set of rails
- An accessory kit
The accessory kit contains:
- (8) 10-32 cage nuts
- (8) 10-32 Phillips screws
- 8 washers
© 2017 FireEye
19
NX Series Hardware Administration GuideCHAPTER 3: Installation
- Safety Guide
- Online Documents Portal Referral
- The cables listed in Cabling Requirements on the facing page.
Tools You'll Need
- Phillips crosshead screwdriver
- ESD wrist strap
Site Requirements
This section contains guidelines for the appropriate location of your rack unit and appliance and precautions.
Installation Site Guidelines
Follow these guidelines when you select an installation site:
- Leave enough clearance in front of the rack for its door to open completely without obstruction.
- Avoid environments that produce heat, electrical noise, and electromagnetic fields.
- Only install the appliance in a Restricted Access Location such as a service closet or dedicated equipment room.
- Make sure the location is properly ventilated.
- Make sure there is sufficient space for air flow.
Rack Precautions
FireEye recommends that you mount the appliance in a standard 19-inch rack. The vertical hole spacing on the rack rails must meet standard ANSI/EIA-310-C requirements, which call for a one-inch (2.54-cm) spacing.
Consider the following before installing your appliance in the rack:
- Ensure the leveling jacks on the bottom of the rack are fully extended to the floor with the full weight of the rack resting on them.
- In a single-rack installation, stabilizers should be attached to the rack.
- In a multiple-rack installation, the racks should be coupled together to increase their stability.
- Always make sure the rack is stable before extending a component from the rack.
- Only extend one component from the rack at a time--extending two or more simultaneously may cause the rack to become unstable.
- Ensure your rack meets the safety requirements of UL 60950-1.
20 © 2017 FireEye
Site Requirements
Server Precautions
FireEye recommends reviewing the electrical and general safety precautions that came with each component you intend to install in the rack.
Review the following before installing the appliance in the rack:
Determine the placement of each component in the rack.
Ensure there is a minimum clearance of six inches behind the chassis to allow for easy cable management.
Install the heaviest component at the bottom of the rack first, then move up.
Allow hot-swappable power supply units and disk drives to cool before handling them.
Use a regulating uninterruptible power supply to protect your components from voltage spikes, power surges, and failure during a power outage.
Keep all of the rack's doors and panels closed when you are not servicing the components.
Rack-Mounting Precautions
Consider the following safety precautions when you install the appliance in the rack:
Make sure the appliance is grounded at all times to prevent damage from electrostatic discharge.
Use an electrostatic wrist guard when handling the appliance.
At least two technicians should be involved to install the appliance safely.
FireEye recommends only individuals with rack-mounting experience should install the appliance.
Install the appliance in an environment compatible with the manufacturer's maximum rated ambient temperature (Tmra) for each component in your rack.
Ventilation Requirements
Ventilation and optimal location are essential to the proper operation of the NX Series appliance. Give the unit at least six inches of space around ventilation openings so that adequate ventilation is possible.
The NX Series appliance draws air through the front and expels it out the back. Note the direction of the air intake and exhaust of the other components in the rack to ensure safe ventilation of all components involved.
Cabling Requirements
The NX 10450 ships with the following cables:
© 2017 FireEye
21
NX Series Hardware Administration GuideCHAPTER 3: Installation
- (2) 6 ft AC power cord, SVT, 60ºC, 3x18AWG (0.824mm²)
- (1) 6 ft null modem DB9 female serial cable
The SFP+ connectors on the NX 10450 are 850nm multimode ports that support a 10Gbps transmission rate. The connecting cables must not exceed 100 meters.
You must provide any additional cables required to connect your system to the network and other devices. Do not exceed the maximum run length of the additional cables you provide.
Power Requirements
The NX 10450 uses a power supply unit with two different output ranges that depend upon the input range. The two output ranges are as follows:
- 1200 W, 100-140 VAC (±10%), 14.7-10.5 A at 50-60 Hz
- 1400 W, 180-240 VAC (±10%), 9.5-7.2 A at 50-60 Hz
Ensure your power source has sufficient electrical overload protection. In North America, connect the rack to a power source with over-current protection that complies with UL 489. In Europe, the over-current protection must comply with IEC standards.
Rack Installation
This section explains how to install your appliance in a standard 19-inch wide rack with the equipment provided. Because various rack units are available, the assembly procedure may differ slightly from the following instructions. Refer to the installation instructions that came with your rack.
Installing the Inner Rails on the Appliance
-
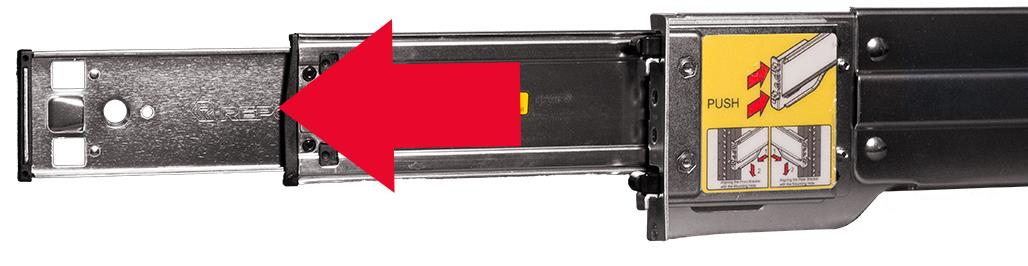
Pull the right inner rail from the outer rail until it is fully extended.
-
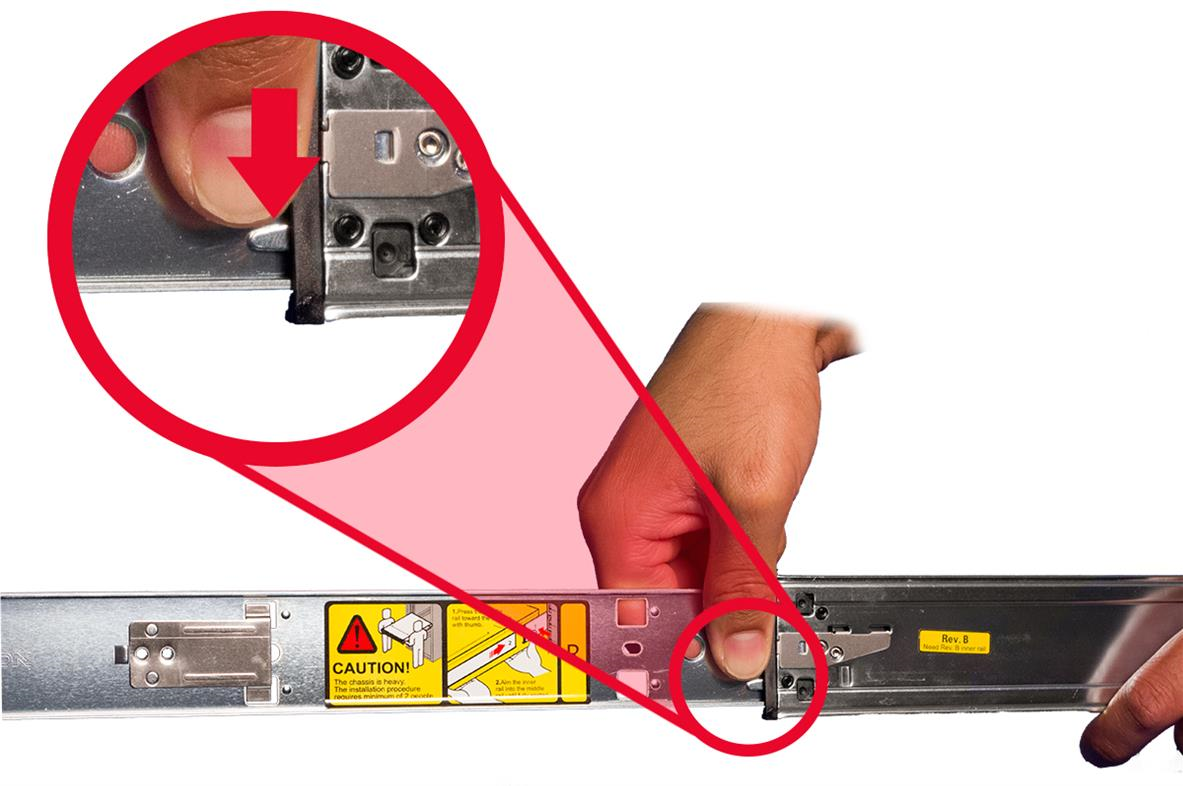
Press the rail-release lever (located between the middle and inner rails) downward and slide the inner rail out until it is separated from the other two rail segments.
22© 2017 FireEye
Rack Installation
3. Align the notches of the inner rail with the tabs on the right side of the appliance.
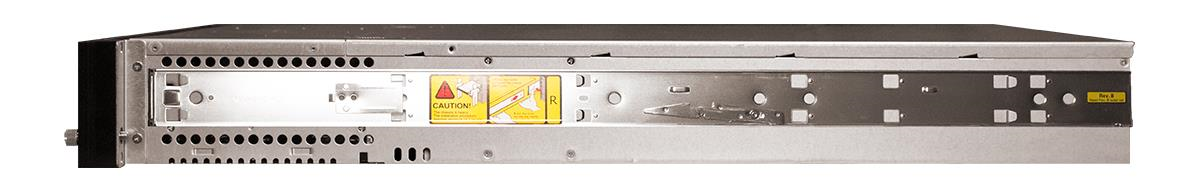
4. While firmly pressing the inner rail against the appliance, slide it in the direction of the tabs until you hear a click.
© 2017 FireEye 23
NX Series Hardware Administration Guide
CHAPTER 3: Installation
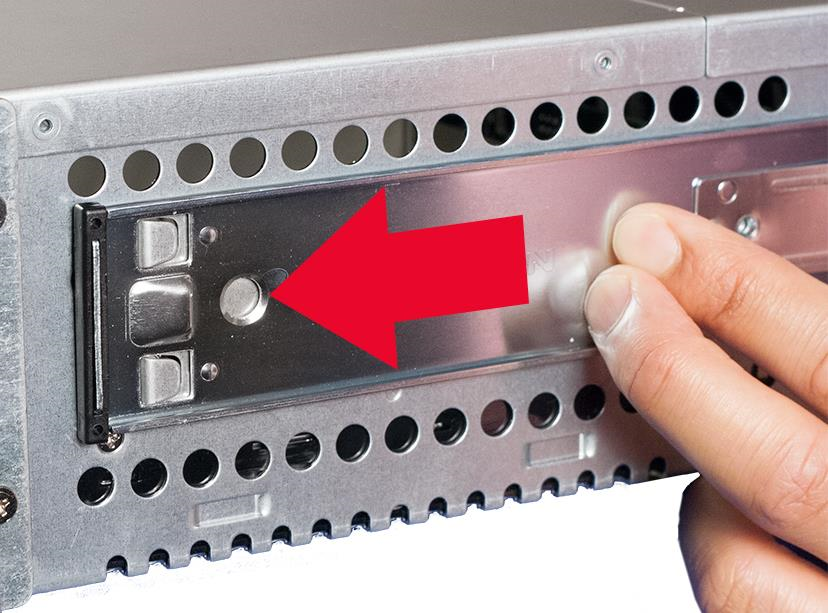
5. Repeat steps 1-4 for the left inner rail.
6. (Optional) Further secure the inner rails to the appliance with the screws provided (one for each rail).
Installing the Outer Rails on the Rack
- Press the black tabs of the right outer rail against the front rack column and insert the hooks at the desired height.
24
© 2017 FireEye
Rack Installation
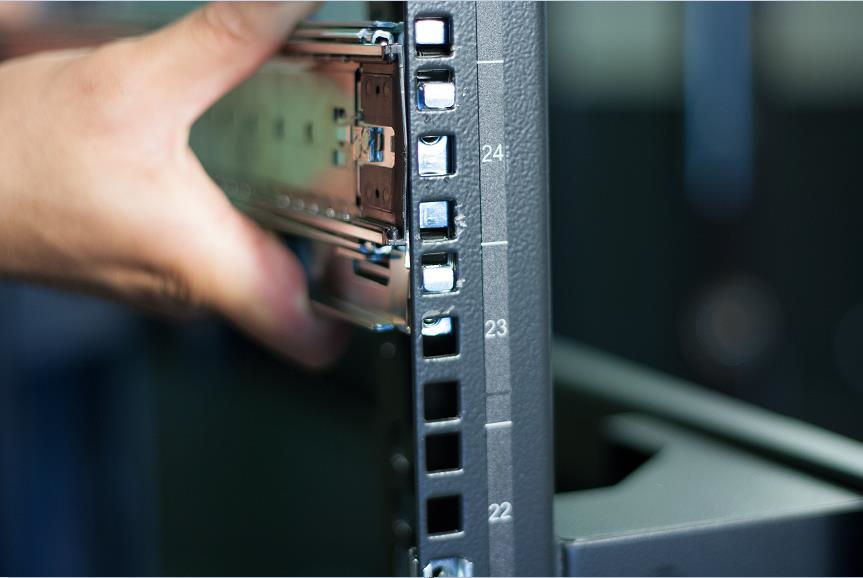
-
Firmly press the rail down to lock it in place.
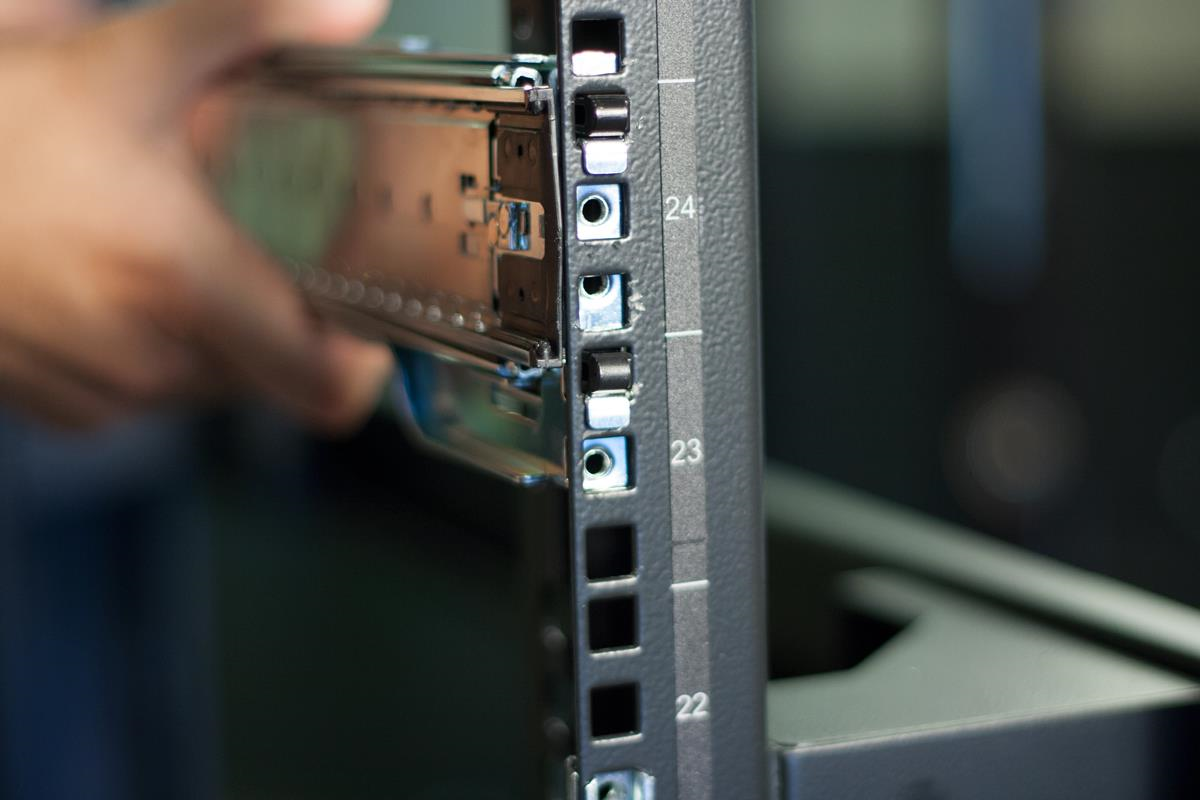
-
Extend the rail until it reaches the rear rack column.
-
Insert the hooks and firmly press it onto the rack.
-
Repeat steps 1-4 to install the left outer rail.
-
Insert and tighten the screws at the rear of the rails to further secure the rails to the rack.
© 2017 FireEye 25
NX Series Hardware Administration Guide
CHAPTER 3: Installation
Mounting the Appliance on the Rack
-
Align the appliance's inner rails with the rack's outer rails.
-
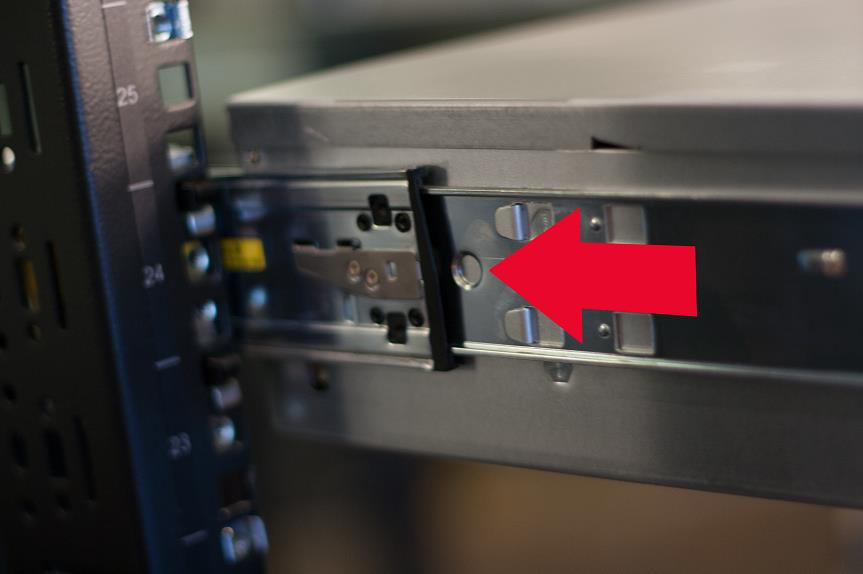
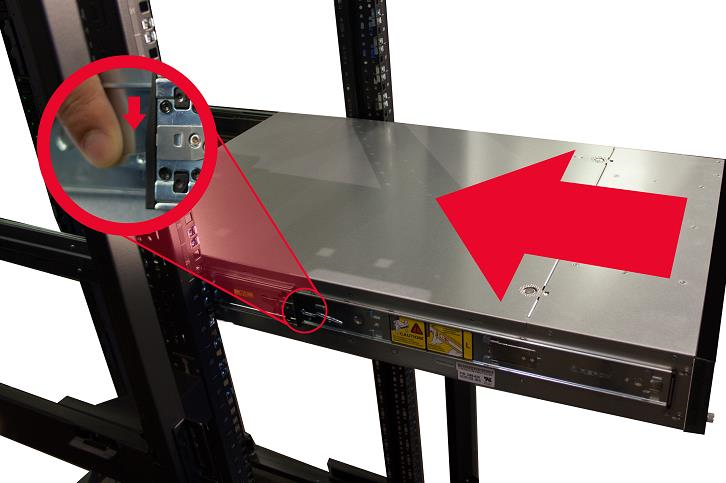
Slide the appliance halfway into the rack.
-
Press the rail-release notches down on both rails and slide the appliance fully into the rack. When the appliance has been pushed completely into the rack, you should hear the locking tabs click.
26
© 2017 FireEye
Rack Installation
Attaching Cables to your Appliance
-
Connect the NX 10450 to one or more network devices using the appropriate cables specific to the deployment of your choice. See Deployment on page 13 for more information.
-
Connect the power cables to the power ports on the back of the appliance.
Turning On the Appliance
Power on the appliance by pressing the power button on the bezel.
|
NX Series Hardware Administration Guide |
CHAPTER 3: Installation |
28 | © 2017 FireEye |
NX Series Hardware Administration GuideNetwork Information Requirements
CHAPTER 4: Baseline Configuration
This chapter contains information and instructions for performing the basic configuration of your appliance.
Network Information Requirements
Before you configure the appliance, collect the information about your network outlined in the following table.
|
Network Item |
Information Needed |
|---|---|
|
FireEye Appliance |
|
|
Domain Name Service (DNS) |
IP address of one or more DNS servers |
|
Network Time Protocol (NTP) Service (Optional) |
IP address of one or more NTP servers |
|
Remote Management (Optional) |
If you want to access the appliance's CLI remotely, the remote system must have an SSH client. |
|
CMS (Central Management System) (Optional) |
|
© 2017 FireEye29
Configuring the Appliance via the LCD Panel
You can perform basic configuration of the appliance using the LCD panel navigation buttons on the bezel.

FireEye recommends using the CLI to configure the appliance, if possible. For information about configuring the appliance via the CLI, see "Initial Configuration" in the System Administration Guide or Administration Guide specific to your FireEye Series appliance and software release.
LCD Panel Navigation Buttons
The table below describes the functions of each navigation button.
|
Navigation Button |
Description |
|---|---|
|
|
Press this button to enter a menu, change a prompt, or accept a change. |
|
|
Press this button to increment a numeric value, change an alphabetical or special character, or change between "yes" and "no." |
|
|
Press this button to decrement a numeric value, change an alphabetical or special character, or change between "yes" and "no." |
|
|
Press this button to move backward between menus, setting prompts, or characters in a sequence. |
|
|
Press this button to move forward between menus, setting prompts, or characters in a sequence. |
|
|
Press this button to exit from a menu or setting prompt. |


LCD Panel Menus
The LCD panel has four menus: Network, Config Options, LCD, and Restart Options. When the LCD panel is idle, press the center button to display the menu options. Use the arrows to cycle through the options and the center button to make a selection.
The following table provides information about the Network menu.
Configuring the Appliance via the LCD Panel

Additional prompts may be available depending on your software release.
Prompt | Description |
|---|---|
Hostname | Hostname for the appliance. |
DHCP enabled | Enter "yes" to use DHCP on the Ethernet 1 (management) port. Enter "no" to manually configure your IP address and network settings. |
IPv6 enabled | Enter "yes" to enable the IPv6 protocol and to change the management network IP routing from IPv4 to IPv6. |
SLAAC enabled | The prompt is available if IPv6 is enabled. Enter "yes" to enable IPv6 autoconfig on the Ethernet 1 (management) port. |
Static IP address | This prompt is available if DHCP is disabled. Enter the IP address for the Ethernet 1 (management) port. |
Netmask | This prompt is available if DHCP is disabled. Enter the network mask. |
Default gateway | This prompt is available if DHCP is disabled. Enter the gateway IP address for the management interface. |
Primary DNS | This prompt is available if DHCP is disabled. Enter the Primary DNS server IP address. |
Domain name | This prompt is available if DHCP is disabled. Enter the domain name for the management interface, for example, yourdomain.com. |
Admin net login | Enter "yes" to enable the administrator to log in to the appliance remotely. Enter "no" to disable remote access. |
IP net filter |
Enter "yes" to enable IP net filtering. This is automatically enabled when MGD Defense is enabled. The IP net filter cannot be disabled while MGD Defense is enabled. This prompt is only available in FireEye AX, CM, EX, FX, and NX releases 7.5 and later, and FireEye HX release 2.0 and later. |
IPv6 net filter |
Enter "yes" to enable IPv6 net filtering. This is automatically enabled when MGD Defense is enabled. The IPv6 net filter cannot be disabled while MGD Defense is enabled. This prompt is only available in FireEye AX, CM, EX, FX, and NX releases 7.5 and later; and FireEye HX release 2.0 and later. |
Enter “yes” to enable MGD Defense VPN, allowing the Managed Defense service to integrate. Enabling this feature also automatically enables IP and IPv6 net filters. Disabling this feature afterward does not affect your IP and IPv6 net filter configurations.
This prompt is only available in FireEye AX, CM, EX, FX, and NX releases 7.5 and later, and FireEye HX release 2.0 and later.
|
Prompt |
Description |
|---|---|
|
MGD Defense VPN |
Enter “yes” to enable MGD Defense VPN, allowing the Managed Defense service to integrate. Enabling this feature also automatically enables IP and IPv6 net filters. Disabling this feature afterward does not affect your IP and IPv6 net filter configurations. This prompt is only available in FireEye AX, CM, EX, FX, and NX releases 7.5 and later, and FireEye HX release 2.0 and later. |
The following table provides information about the Config Options menu.
|
Prompt |
Description |
|---|---|
|
Save settings |
Saves changes made during this session so they will persist after a reboot. |
|
Revert to factory defaults |
Reverts the appliance to its factory default settings, which include username, password, and network configuration information. |
|
Reset admin password |
Resets the admin password for accessing the appliance itself. This does not set the password for accessing the LCD panel. |
The following table provides information about the LCD menu.
|
Prompt |
Description |
|---|---|
|
Password |
Sets a password for LCD-panel access. This does not set the password for accessing the appliance. |
|
Brightness |
Sets the LCD panel's level of brightness from 0 to 9, with 9 being the brightest. |
|
Contrast |
Sets the LCD panel's level of contrast between the background and text from 0 to 9, with 9 being the greatest contrast. |
The following table provides information about the Restart Options menu.
|
Prompt |
Description |
|---|---|
|
Reboot System |
Restarts the system. |
|
Halt System |
Puts the system in sleep mode. |
|
Next boot loc |
Specifies disk partition (1 or 2) to boot from during the next reboot. |
Required Ports and Protocols
The table below outlines the main connections for the NX 10450 appliance’s communications. Open the ports listed below on your firewall to permit these connections.
|
Source |
Destination |
Destination Port |
User Configurable |
Notes |
|---|---|---|---|---|
NX 10450: Ether1* | cloud.fireeye.com | TCP 443 | Yes | Dynamic Threat Intelligence (DTI) Cloud Update Service |
Administrator Workstation | NX 10450: Ether1 | TCP 22 | No | CLI Management |
Administrator Workstation | NX 10450: Ether1 | TCP 443 | No | Web UI Management |
NX 10450: Ether1 | SMTP Relay | TCP 25 | No | SMTP Alerts |
NX 10450: Ether1 | Internal DNS Servers | TCP/UDP 53 | No | DNS Queries |
NX 10450: Ether1 | NTP Servers | UDP 123 | No | NTP |
NX 10450: Ether1 | SIEM/Syslog Server | UDP 514 | No | Syslog |
NX 10450: Ether1 | SNMP Server | UDP 162 | No | SNMP |
CM-Managed NX 10450: Ether1** | CM Ether1 | TCP 22 | No | CM Management Connection |
Remote Console | NX 10450 IPMI | TCP 5900/5901 | No | Remote Console Redirection |
Sensor*** | Broker |
22 (for on-premise solution) 443 (for Cloud MVX solution) | No | Job submission communication |
NX Series Hardware Administration Guide
CHAPTER 4: Baseline Configuration
| Source | Destination | Destination Port | User Configurable | Notes |
|---|---|---|---|---|
|
* This is the default destination and port for stand-alone appliances and the CM Series platform. For a CM Series platform or standalone NX Series appliance running Release 7.5.0 or later, or a standalone EX Series appliance running Release 7.6.0 or later, the DTI source server can be either cloud.fireeye.com or staticcloud.fireeye.com. For a managed NX Series or EX Series appliance running these releases, the default DTI source server is the CM Series platform, but it can be either of the two servers mentioned above instead. ** For a managed appliance running Release 7.6.0 or later that uses the CM Series platform as its DTI source server, single-port communication is the default behavior. This means CM Ether1 port (TCP 22) is used for both DTI traffic and management traffic, unless otherwise configured. For details, see the CM Series Administration Guide or the System Administration Guide for your appliance. ***In a FireEye Network Security configuration. | ||||

For information about CM Series High Availability (HA) ports, see the CM Series High Availability (HA) Deployment Guide.
NX Series Hardware Administration GuideReturn Process
CHAPTER 5: Replacements
This chapter contains instructions for replacing your appliance, with or without disk drives, and removing and replacing individual failed disk drives and power supplies. The disk drives and power supplies are hot-swappable, meaning they can be removed and replaced without unracking the appliance or powering it off.
Return Process
If you believe you have a defective part, you must first contact FireEye Technical Support, who will validate whether or not the part is defective. If the part is defective, Technical Support will initiate a Return Materials Authorization (RMA). No part can be returned without a FireEye-issued RMA number.
After receiving the replacement part from FireEye, please package and return the defective part within five (5) days, at FireEye's cost (provided that you utilize FireEye's designated courier service). If you fail to return the defective part within ten (10) business days after receiving the replacement, FireEye may invoice you as detailed in our Support Terms and Conditions, described here: http://www.fireeye.com/support/terms-and-conditions.html.
In the case of a defective disk drive or a defective system with disk drives, you may retain the disk drive(s) if you have purchased the Non-Returnable Disk Drive support option. Follow these instructions:
To return a defective part or system:
-
Pack the defective part or the entire appliance in the packaging that the replacement part was received in, or in its original packaging material (or equivalent).
-
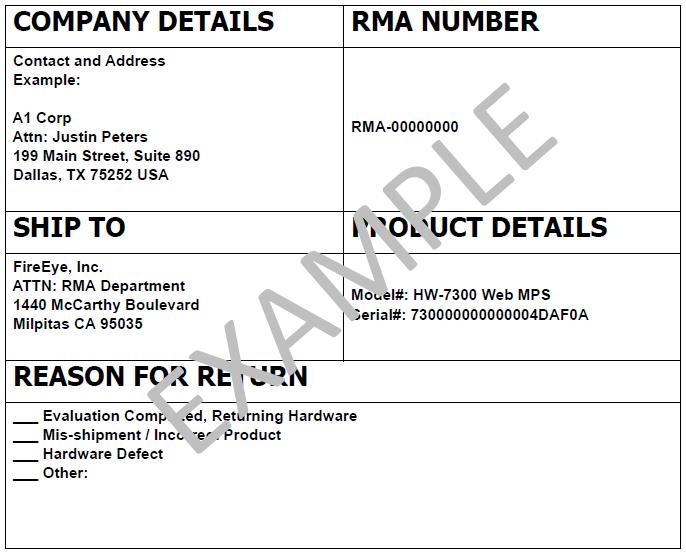
Place a copy of the associated RMA Form (example shown below) inside the package. If you have more than one package, place a copy inside each package.
-
Write the associated RMA number on the outside of each return package and in the reference field on each waybill. Returns cannot be processed without referencing the associated RMA number.
NX Series Hardware Administration Guide
CHAPTER 5: Replacements
Do not insure the shipment. FireEye is self-insured. Please declare “$0” in the “value for carrier” section.
Send an email to RMA_Ops@fireeye.com listing the RMA number(s), the carrier name, and the carrier tracking number(s) for the return package.
If you do not have a return shipping label, contact FireEye operations at RMA_Ops@fireeye.com and they will provide one for your return.
All international shipments require three copies of a commercial invoice (CI). FireEye provides a partially completed CI. Please either use this CI, after completing the remaining required information, or create your own if you prefer. Please contact your distribution partner who can assist you. If you require additional assistance, please contact RMA_Ops@fireeye.com.
Send the package directly to the location specified in the "SHIP TO" section on the RMA Form (example shown below) provided in the replacement part package.
For questions regarding an RMA return or status, please email: RMA_Ops@fireeye.com or call +1-408-321-7798.
Enclosed with your replacement part, you will receive a FireEye RMA Form similar to the following:
Replacing an Appliance Including Disk Drives
Before replacing your NX 10450, take a backup of the current system, if possible. FireEye recommends that regular, full system backups are taken. For more information, see Backing Up and Restoring the Appliance Database on the next page. If you cannot back up the appliance, make sure your latest system backup is available. Contact FireEye Technical Support if you have questions on backing up your appliance.
To replace an appliance including the disk drives:
-
Perform an orderly shutdown of the defective appliance.
-
Unplug the appliance.
 Keep the power cord and cables for your replacement appliance.
-
Unrack the defective appliance and rack-mount and re-cable the replacement appliance.
-
Power on the replacement appliance.
-
Configure the appliance as described in "Initial Configuration" of the System Administration Guide specific to your FireEye Series appliance and software release.
-
Using a console connection, restore the appliance's configuration and database as described in Backing Up and Restoring the Appliance Database on the next page.
-
Install replacement licenses as described in Applying License Keys on page 44.
-
Set the DTI credentials as described in "Configuring DTI Credentials" in the System Administration Guide or Administration Guide specific to your FireEye Series appliance and software release.
© 2017 FireEye
37

Be sure to keep the power cord and cables for your replacement appliance.
-
Unrack the defective appliance.
-
Rack-mount the replacement appliance as described in Rack Installation on page 22.
-
Cable the appliance as described in Attaching Cables to your Appliance on page 27.
-
Plug in a VGA monitor and USB keyboard.
-
Power on the replacement appliance and watch the boot up process on the connected monitor.
-
Press Ctrl-C to enter the SAS Configuration Utility when prompted.
-
Enter the RAID Properties menu.
-
Select View Existing Volume > Manage Volume > Activate Volume then press Y to activate the volume.
-
Wait for the volume to activate. This takes about one minute.
-
Configure the appliance via the LCD panel or console as described in Configuring the Appliance via the LCD Panel on page 30 or "Initial Configuration" in the System Administration Guide specific to your FireEye Series appliance and software release.
-
Install replacement licenses as described in Applying License Keys on page 44.
-
Set the DTI Credentials as described in “Configuring DTI Credentials” in the System Administration Guide or Administration Guide specific to your FireEye Series appliance and software release.
Backing Up and Restoring the Appliance Database
Before replacing your NX 10450 appliance, take a backup of the current system so you can later restore it on the replacement.
If the appliance runs FireEye OS Release 7.4 or earlier, you back up the configuration file and the database separately. Refer to the following topics:
- Backing Up the Appliance Configuration on the facing page
- Backing Up the Appliance Database on the facing page
- Restoring the Appliance Configuration on page 40
- Restoring the Appliance Database on page 41
If the appliance runs FireEye OS Release 7.5 or later, you back up the configuration file and database in one operation. Refer to the following topics:
Backing Up the Appliance Database on page 41
Restoring the Appliance Database on page 43
Backing Up and Restoring the Appliance Database Using Release 7.4 and Earlier
Backing Up the Appliance Configuration
To back up an appliance configuration file:
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal
-
Save the appliance configuration to a file:
NX10450 (config) # configuration write to filename
-
Upload the saved configuration file to a file server:
NX10450 (config) # configuration upload filename-url
-
Verify that the configuration file is on the file server.
NX10450 (config) # show configuration files
The following example backs up the configuration file to a file named config_backup.
NX10450 (config) # configuration write to config_backup NX10450 (config) # show configuration files config_backup (active) initial initial.bak
Active configuration: config_backup
Unsaved changes: no
NX10450 (config) # configuration upload config_backup ?
<FTP/TFTP URL or scp://username[:password]@hostname/path/filename> ftp, tftp, scp and sftp are supported. e.g. scp://username[:password]@hostname/path/filename
NX10450 (config) # configuration upload config_backup scp://username@backuphost/path/config_backup Password (if required): ********
Backing Up the Appliance Database
Follow these steps to back up the appliance database using the CLI.
To back up the appliance’s database using the CLI:

Be sure to back up in binary format, not ASCII, for FTP restores.
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal
© 2017 FireEye
39
NX Series Hardware Administration GuideCHAPTER 5: Replacements
-
Save a backup of the appliance database to a file.
NX 10450 (config) # fedb backup to-file filename
-
Upload the database backup file to a file server.
NX 10450 (config) # fedb backup upload filename-url
-
Verify that the backup file is on the file server.
NX 10450 (config) # show fedb backups
Videos, binaries, and PCAPS are not backed up during this process. Contact FireEye Technical Support for more information.

The following example backs up the database file to a file named db_backup.
NX 10450 (config) # fedb backup to-file db_backup Dumping database to backup file Encrypting backup file Created database backup file db_backup NX 10450 (config) # show fedb backups Created At Size Backup File 2014/04/15 03:00:00 50.0M db_backup 1 backup file available! NX 10450 (config) # fedb backup upload db_backup scp://username@backuphost/path/db_backup Password (if required): ********
Restoring the Appliance Configuration
Be sure to make a copy of the current configuration before restoring an older configuration.
To restore a configuration file:
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal
-
Fetch the saved configuration file from the file server.
NX 10450 (config) # configuration fetch url filename
-
Activate the saved configuration file.
NX 10450 (config) # configuration switch-to filename
The following example restores the configuration file named config_backup.
NX 10450 (config) # configuration fetch ? <download URL> http, https, ftp, tftp, scp and sftp are supported. e.g. scp://username[:password]@hostname/path/filename NX 10450 (config) # configuration fetch scp://username@backuphost/path/config_backup Password (if required): ******** NX 10450 (config) # show configuration files config_backup initial (active) initial.bak Active configuration: initial Unsaved changes: yes NX 10450 (config) # configuration switch-to config_backup
40© 2017 FireEye
Restoring the Appliance Database
Follow these steps to restore the appliance database using the CLI.
To restore the database using the CLI:
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal
-
Fetch the database backup file from the file server.
NX 10450(config) # fedb backup fetch filename
-
Restore the database backup.
NX 10450 (config) # fedb restore from-file filename
-
Reload the appliance.
NX 10450 (config) # reload
The following example restores the database file named db_backup.
NX 10450 (config) # fedb backup fetch ? <HTTP/FTP/TFTP URL or scp://username:password@hostname/path/filename> NX 10450 (config) # fedb fetch scp://username@backuphost/path/db_backup Password (if required): ******** NX 10450 (config) # show fedb backups Created At Size Backup File 2014/04/01 03:00:00 50.0m db_backup 1 backup files available! NX 10450 (config) # fedb restore from-file db_backup Decrypting backup file Restore backup file into database Backup is from supported database version 9.1 Restored database backup file db_backup Restarting Database clients ... done! Appliance reload is recommended to ensure best results after a database restore. NX 10450 (config) # reload Configuration has been modified; save first? [yes] Configuration changes saved. Rebooting...
Backing Up and Restoring the Appliance Database Using Release 7.5 and Later
Backing Up the Appliance Database
Follow these steps to back up the appliance database using the CLI.
To back up the appliance database:
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal
-
Specify the type of profile.
-
To set the profile for the configuration database, enter:
NX 10450 (config) # backup profile config
-
© 2017 FireEye
-
-
To set the profile for the FireEye appliance database, enter:
NX 10450 (config) # backup profile fedb -
To set the profile for both the configuration database and the FireEye appliance database, enter:
NX 10450 (config) # backup profile config+fedb -
To set the profile for the configuration database, FireEye appliance database, and detected data (malware, alerts, reports, and so on), enter:
NX 10450 (config) # backup profile full
-
-
Specify the location for the backup file.
-
To save the backup file to a local destination on the appliance, enter:
NX 10450 (config) # backup profile <profile> to local -
To save the backup file on a remote server, enter:
NX 10450 (config) # backup profile <profile> to <url>where
urlis the specified remote location using the following format:scp://username:password@hostname/remote_path -
To save the backup file to a USB drive on your local machine, enter:
NX 10450 (config) # backup profile <profile> to usb
-
-
Specify the prefix for the backup file name.
NX 10450 (config) # backup profile <profile> to <backup_location> prefix <prefix>You can use the customized prefix to sort the list of the backup files.
-
(Optional) Monitor the progress of the backup operation.
-
To disable progress tracking for the backup operation, enter:
NX 10450 (config) # backup profile <profile> to <backup_location> progress no-track -
To enable progress tracking for the backup operation, enter:
NX 10450 (config) # backup profile <profile> to <backup_location> progress track
By default, progress tracking is enabled.
You can cancel progress tracking by using
Ctrl+C. The backup operation still happens in the background. Use theshow backup statuscommand to find the status of the backup operation. -
-
(Optional) Disable public and private key encryption for the backup operation.
NX 10450 (config) # backup profile <profile> to <backup_location> no-encryptionEach backup file is signed by default using the public and private key pairs. By default, encryption is always included in the backup.
Encryption delays the backup operation. Backups are encrypted only using static keys.
Backing Up and Restoring the Appliance Database

To cancel a backup that is in progress, enter the backup cancel command. When you cancel the backup operation that is in progress, the system finishes the current step before canceling the entire operation.
The following example backs up the configuration database, detected data, and artifacts to a local destination on the appliance:
NX 10450 (config) # backup profile full to local
Step 1 of 4: Backing up config db
100.0% [#############################################]
Step 2 of 4: Backing up fedb
100.0% [#############################################]
Step 3 of 4: Backing up Artifacts
100.0% [#############################################]
Step 4 of 4: Generating Backup package
100.0% [#############################################]Restoring the Appliance Database
Follow these steps to restore the appliance database from a backup file using the CLI.
To restore the appliance database from a backup file:
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal -
Locate the backup FEBKP file you want to restore.
-
To display a list of the backup files on the USB drive, enter:
NX 10450 (config) # show backup available on-usb -
To display a list of the backup files on the appliance, enter:
NX 10450 (config) # show backup available local
-
-
Specify a backup profile.
-
To set the profile for the configuration database, enter:
NX 10450 (config) # restore profile config -
To set the profile for the FireEye appliance database, enter:
NX 10450 (config) # restore profile fedb -
To set the profile for both the configuration database and the FireEye appliance database, enter:
NX 10450 (config) # restore profile config+fedb -
To set the profile for the configuration database, FireEye appliance database, and detected data (malware, alerts, reports, and so on), enter:
NX 10450 (config) # restore profile full
-
4. Specify the location of the backup file.
-
To restore the backup from the local destination on the appliance, enter:
NX 10450 (config) # restore profile profile from local
-
To restore the backup from a remote server, enter:
NX 10450 (config) # restore profile profile from url
where url is the specified remote location using the following format:
https or scp://username:password@hostname/remote path
-
To restore the backup from a USB drive on your local machine, enter:
NX 10450 (config) # restore profile profile from usb
5. Enter the name of the backup file.
NX 10450 (config) # restore profile profile from backup location backup name
6. (Optional) Restore the network settings from the relevant backup.
NX 10450 (config) # restore profile profile from backup location backup name include-network-config
By default, the network settings are not included in the restore operation.
Do not restore the current network settings while the appliance is performing a restore operation from a remote server.

7. (Optional) Monitor the progress of the restore operation.
-
To disable progress tracking for the restore operation, enter:
NX 10450 (config) # restore profile profile from backup location backup name progress no-track
-
To enable progress tracking for the restore operation, enter:
NX 10450 (config) # restore profile profile from backup location backup name progress track
By default, progress tracking is enabled.
You can cancel progress tracking by using Ctrl+C. The restore operation still happens in the background. Use the show restore status command to find the status of the restore operation.
The following example shows how to restore a configuration database backup from your local appliance:
NX 10450 (config) # restore profile config from local backup wMPS-Config-7.5.0-sulabh-wmps-20141118-133123.febkp Step 1 of 3: Performing Sanity checks 100.0% [########################################] Step 2 of 3: Extracting backup package 100.0% [########################################] Step 3 of 3: Restoring config db 100.0% [########################################]
Applying License Keys
After you replace an appliance, you must apply replacement license keys.
To apply a license key from the CLI:
-
Enable the CLI configuration mode.
NX 10450 > enable NX 10450 # configure terminal -
Enter the license key.
NX 10450 (config) # license install <license-key> -
Repeat step 2 for each additional license key you need to apply.
Identifying the Failed Disk Drive
Before removing and replacing the failed disk drive from your appliance, you must first identify the slot in which it resides.
To identify the slot of failed disk drive for appliances running a release prior to the NX Series 7.2 release, contact Customer Support.

To identify the slot number of a failed drive from the CLI:
-
Enable configuration mode.
NX 10450 > enable NX 10450 # configure terminal -
Enter the show media disk command.
-
Note the slot number of the failed drive. View the sample output below for reference.
Enclosure Device ID: 12 Slot Number: 16 Drive's position: DiskGroup: 0, Span: 0, Arm: 0Enclosure position: 1 . . . Physical Sector Size: 0 Firmware state: Failed Commissioned Spare : No . . . -
Proceed to the following section for instructions on removing and replacing the disk drive within the specified slot number.
Removing and Replacing an NX 10450 Disk Drive
Perform the following steps to remove and replace an NX 10450 disk drive:
NX Series Hardware Administration Guide
CHAPTER 5: Replacements
-
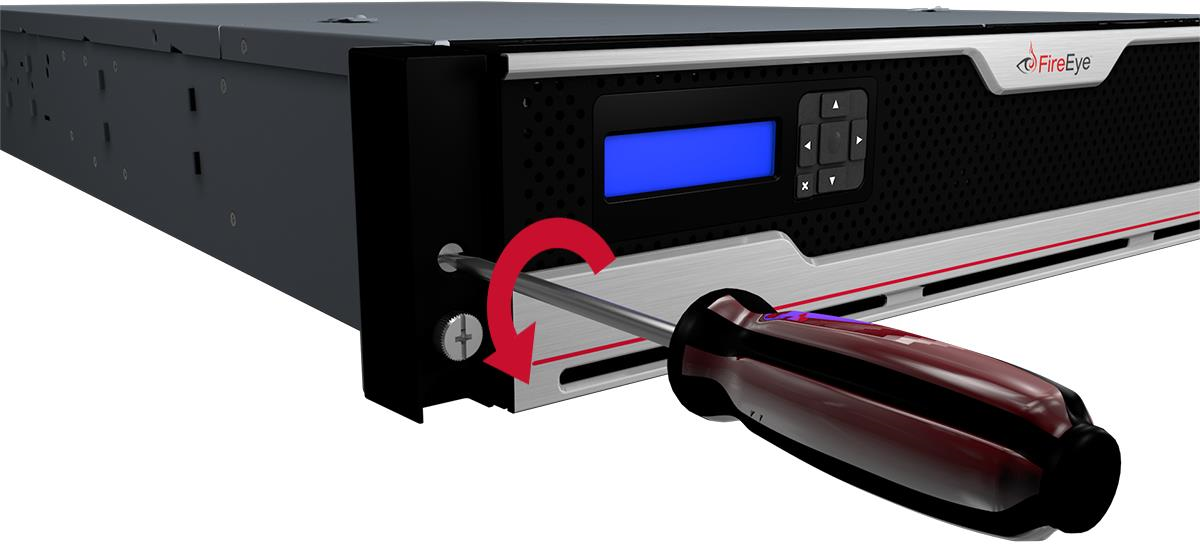
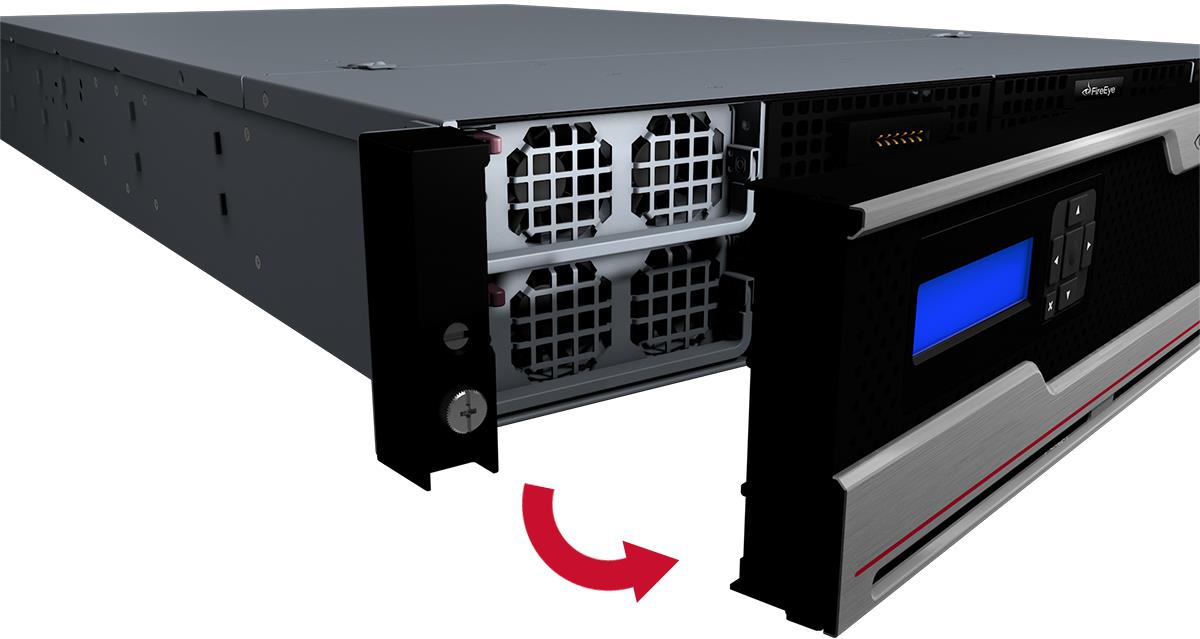
Turn the screw located to the left of the bezel counterclockwise to unlatch it from the appliance.
-
Gently remove the bezel from the appliance to reveal the disk drives.
-
Locate the disk drive carrier that contains the failed disk drive.
46
© 2017 FireEye
Removing and Replacing an NX 10450 Disk Drive
-
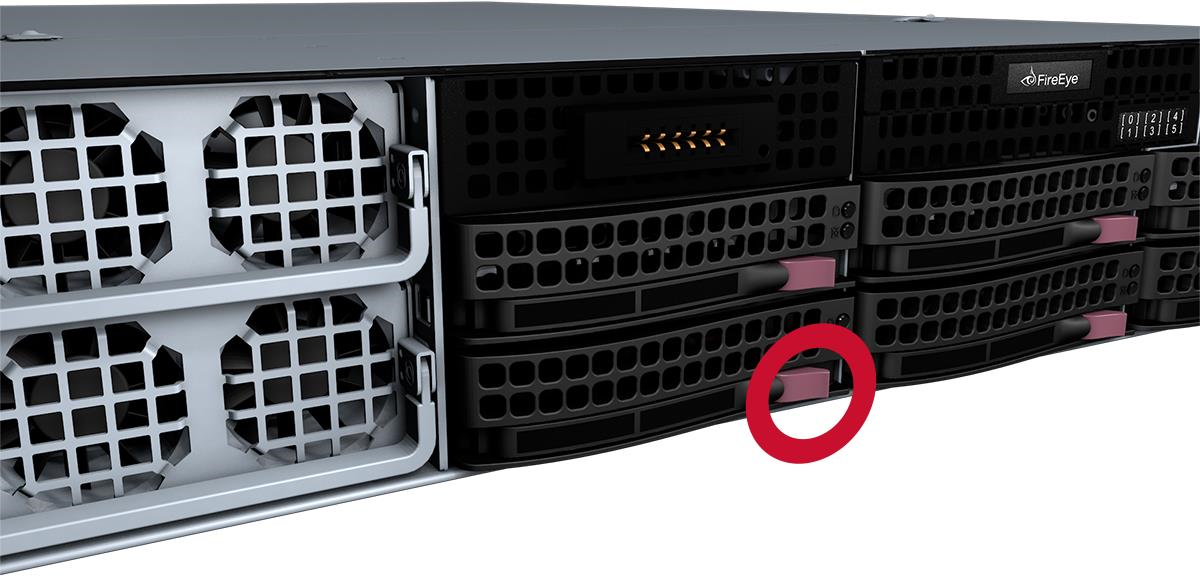
Push the maroon button to release the latch handle.
-
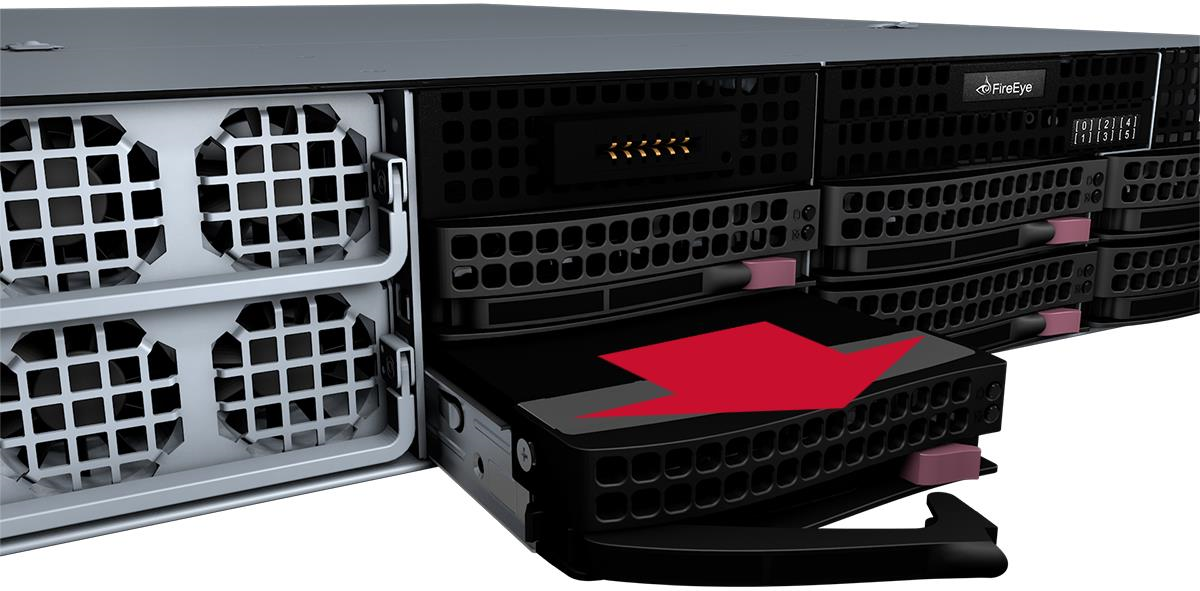
Carefully pull the latch handle forward.
-
Pull the handle to slide the disk drive from its slot.
© 2017 FireEye
47
NX Series Hardware Administration GuideCHAPTER 5: Replacements
-
Use the latch handle on the new drive carrier to slide the new drive into the empty slot. When the drive is fully inserted into the slot, push the latch handle in until it clicks.
To verify the RAID functionality of the replacement drive:
-
Enable configuration mode.
NX 10450 > enable NX 10450 # configure terminal -
Enter the show system hardware status raid command.
-
Verify that the disk status of the replaced drive is “Online.”
For appliances running a release prior to NX Series 7.2, see the About > Hardware section of the appliance’s Web UI to verify the RAID functionality of the replacement drive.
Removing and Replacing an NX 10450 Power Supply Unit
Perform the following steps to remove and replace an NX 10450 power supply unit (PSU):
-
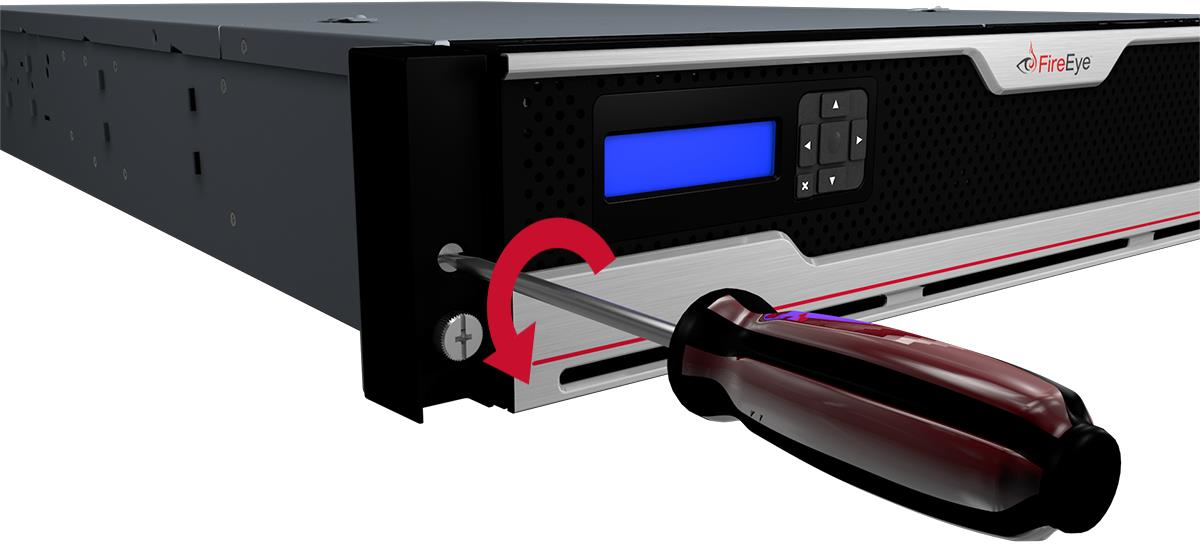
At the rear of the appliance, remove the power cable from the failed PSU.
-
Turn the screw located to the left of the bezel counterclockwise to unlatch it from the appliance.
48© 2017 FireEye
Removing and Replacing an NX 10450 Power Supply Unit
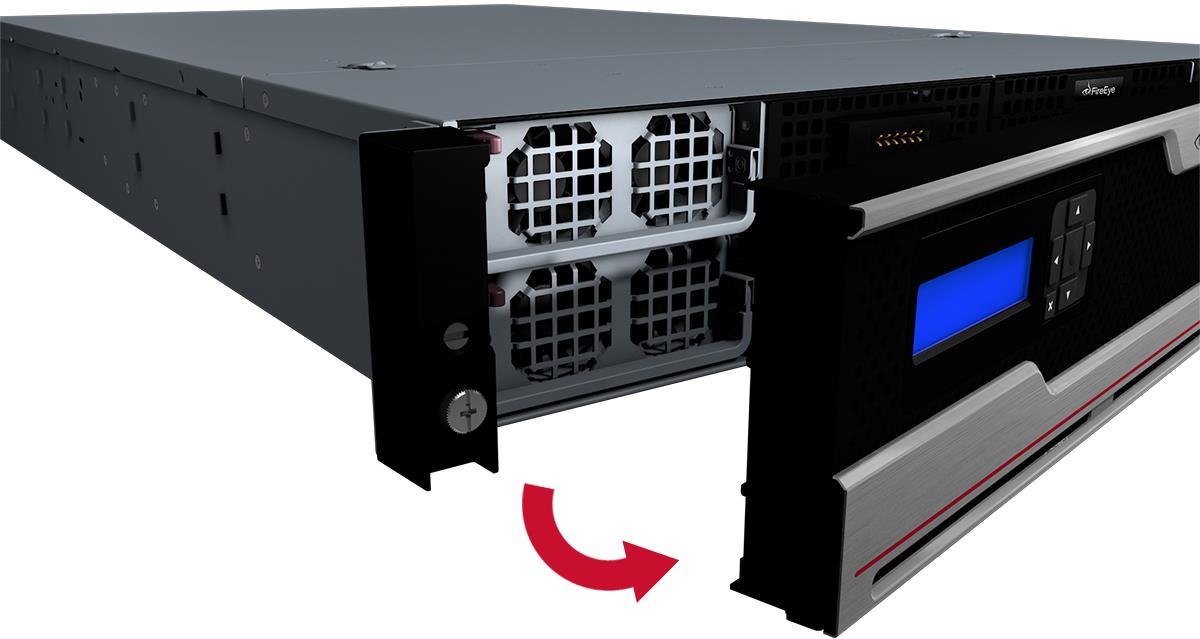
3. Gently remove the bezel from the appliance to reveal the failed PSU.
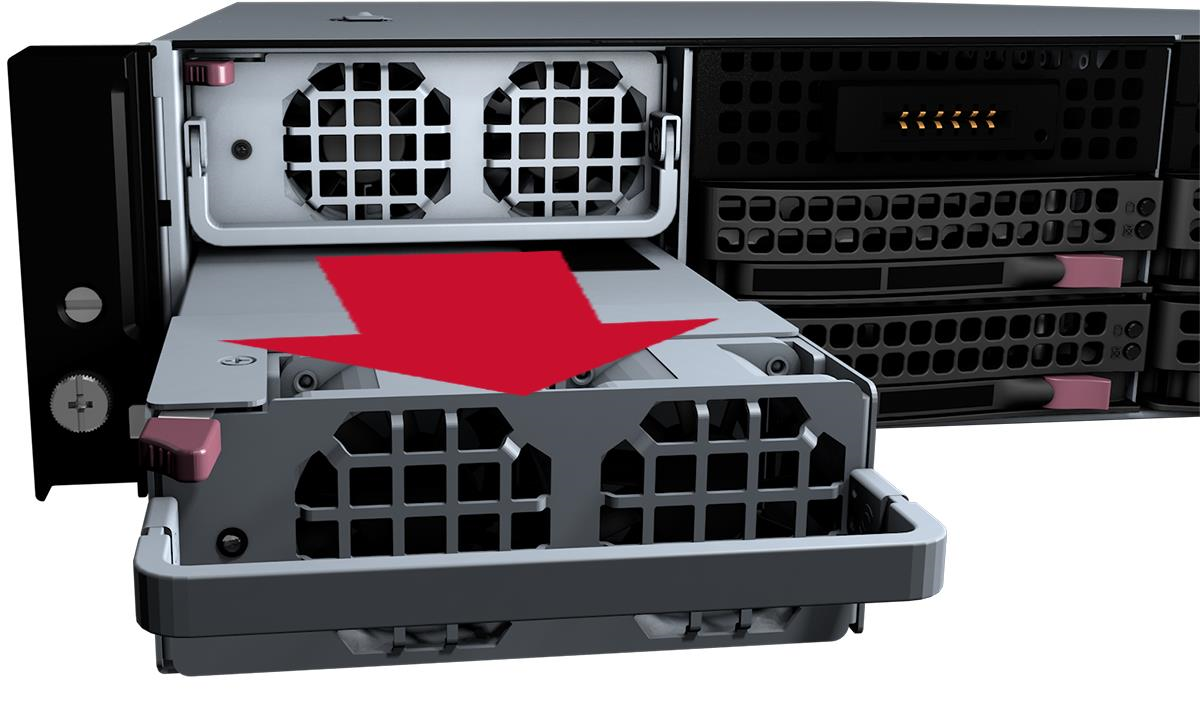
4. Press the PSU's red button rightward while pulling its handle to slide the unit out of the slot.
NX Series Hardware Administration Guide CHAPTER 5: Replacements
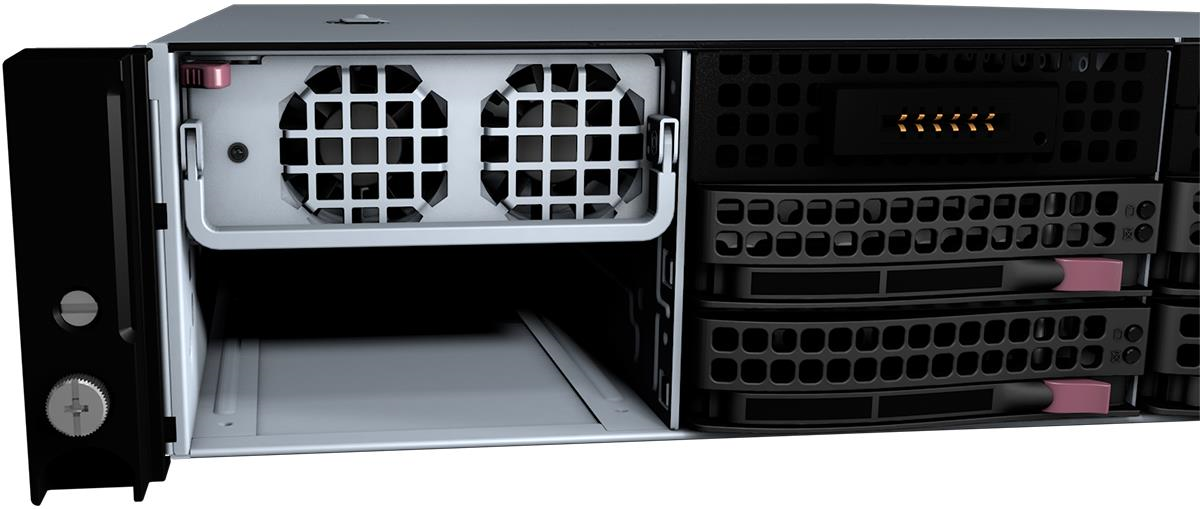
5. Insert the replacement PSU in the slot guides and slide it back until the latch clicks.
50
© 2017 FireEye
NX Series Hardware Administration GuideAppendix 1: System Specifications
Appendices
Appendix 1: System Specifications
The table below provides the technical specifications of the FireEyeNX 10450.
| Component | NX 10450 Specifications |
|---|---|
| Form Factor | 2U Rack-Mount |
| Dimensions (W x D x H) | 17.2 x 27.9 x 3.5 inches
(437 x 709 x 89 mm) |
| Enclosure | 2 RU, Fits 19-inch rack |
| Management Interfaces | (2) 10/100/1000BASE-T Ports |
| Monitoring Interfaces | (4) SFP+ Ports (4) SFP Ports |
| Drive Capacity | (4) 800 GB SSD, RAID 10, 2.5", FRU |
| AC Power Supply | Redundant (1 + 1)
1200 W @ 100-140 VAC 14.7-10.5 A, 50/60 Hz or 1400 W @ 180-240 VAC 9.5-7.2 A, 50/60 Hz IEC60320-C14 inlet |
| Maximum Power Consumption | 850 W |
| Operating Temperature | 10° to 35° C |
| Maximum Thermal Dissipation | 2908 BTU/hour |
© 2017 FireEye51
NX Series Hardware Administration Guide
Appendices
Appendix 2: Product Compliance Information
The following table lists the electromagnetic compatibility (EMC), low voltage directive (LVD), safety, and other regulatory standards met by the FireEye NX Series appliance.
|
NX Model |
EMC (2004/108/EC) |
LVD/Safety (2006/95/EC) |
Other |
|
900 9450 10450 |
EN 55022: 2010 EN 55024: 2010 IEC/EN 61000-3-2: 2006 IEC/EN 61000-3-3: 2008 |
IEC 60950-1:2005 (2nd Edition) + A1: 2009 EN 60950-1: 2006 + A11: 2009 UL 60950-1 (2nd Edition) CSA/CAN‑C22.2 No 60950-1 + A1: 2011 |
FCC Part 15 ICES-003 AS/NZ CISPR 22 VCCI V-3 RoHS REACH WEEE IEC60320-C14 inlet |
Index
INDEX
© 2017 FireEye, Inc.
53
Index
|
54 |
© 2017 FireEye, Inc. |
Release ADD Software Release
Technical Support
For technical support, contact FireEye in the following ways:
- Visit the FireEye Customer Support Portal (login required): https://csportal.fireeye.com
- Call us at 1-877-FIREEYE (USA); +44 203 106 4828 (UK); +1 408.321.6300 (Outside the USA)
- Email us at support@fireeye.com
Documentation
Documentation for all FireEye products is available on the FireEye Documentation Portal (login required):
FireEye, Inc. | 1440 McCarthy Blvd. | Milpitas, CA | 1.408.321.6300 | 1.877.FIREEYE
support@fireeye.com | www.fireeye.com
© 2017 FireEye, Inc. All rights reserved. FireEye is a registered trademark of FireEye, Inc. All other brands, products, or service names are or may be trademarks or service marks of their respective owners.