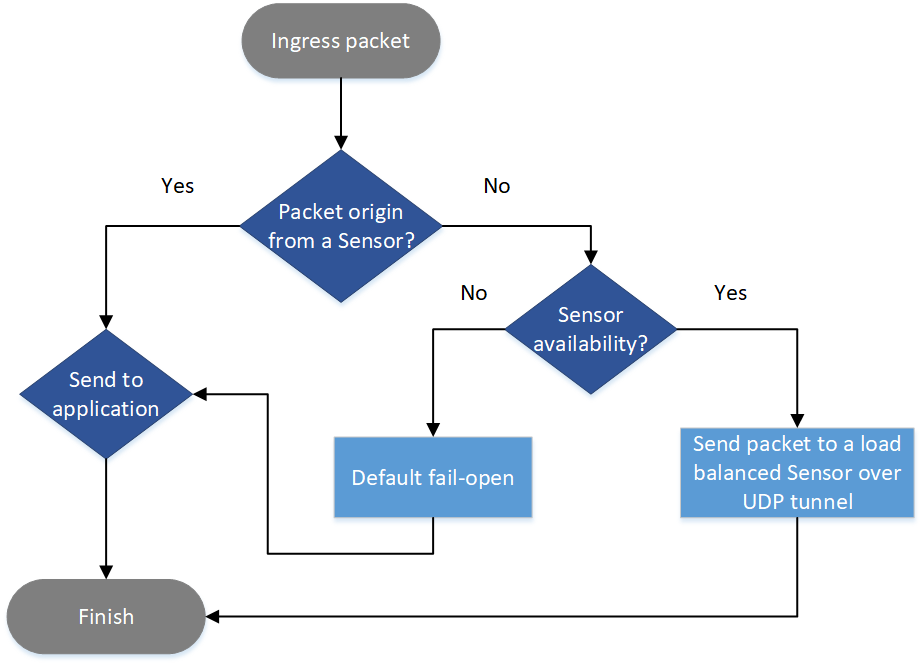
Ingress packet
When a packet arrives at the interface, it is first checked to see if the packet is directed from a Sensor tunnel after inspection or to an application. If it is from a Sensor tunnel, the packet is already inspected, and subsequently, directed to the application. If the packet is directed to an application, it needs to be inspected. So, the Probe checks for any Sensor to which it can redirect the traffic for inspection through the UDP tunnel. The Sensor inspects the traffic as per the configuration. The packet after inspection is forwarded to the Sensor tunnel to be directed back to the application. If there is no Sensor available, a fail-open state is established where the packet is forwarded to the application without inspection.
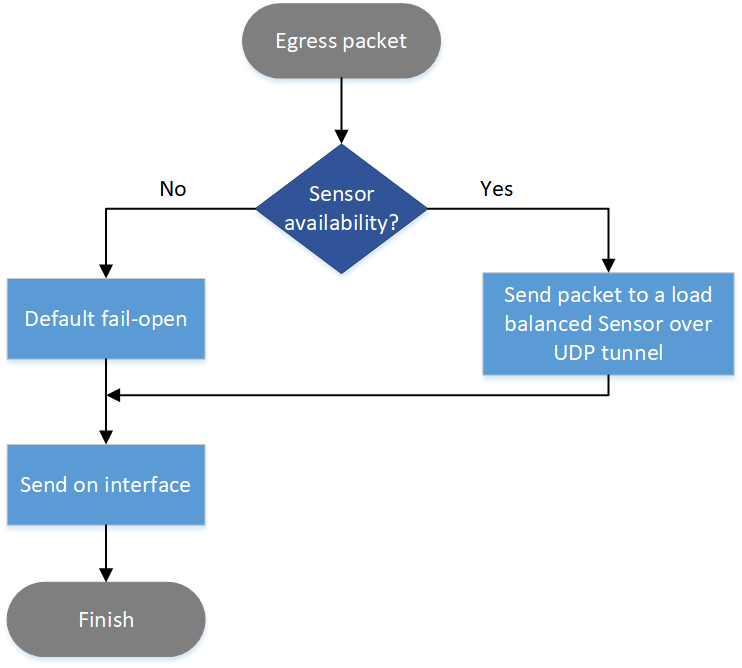
Egress packet
When an application sends a packet, it is intercepted and sent to the Probe. The Probe sends the packet to the Sensor over UDP tunnel for inspection. After inspection, the Sensor sends the packet back to the Probe over UDP tunnel, which is sent out on the interface. If there are no Sensors, a fail-open state is established and the packet is sent out on an interface without inspection.
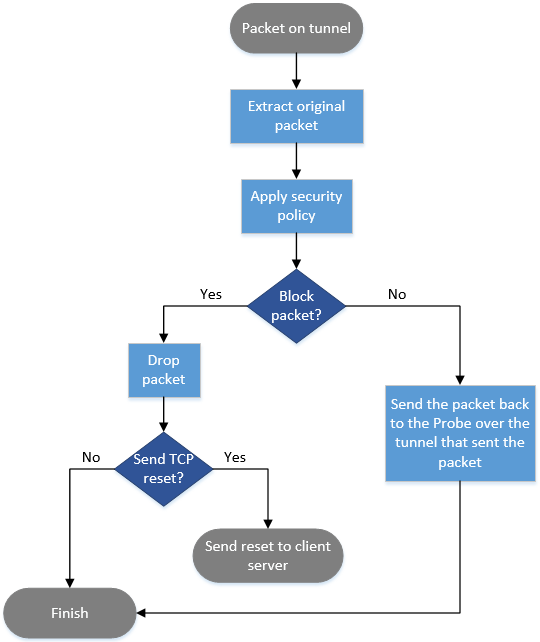
Packet flow in Sensor
A packet is received by the Sensor over the tunnel interface. The original packet is extracted by the Sensor and used for inspection. Based on the attack action configured in the Sensor, the packet is either blocked or directed to the Probe to be forwarded. The connection is blocked by dropping the packet and sending a TCP reset from the Sensor that resets the connection.