You can perform the Network Forensics for either the source endpoint or the destination endpoint. This analyzes and provides information about the endpoints.
Note
Network Forensics is not applicable for the Central Manager.
Task
- Navigate to Analysis → <Admin Domain Name> → Attack Log.
- Select the alert whose IP to which you want to perform forensics.
-
Click
Other Actions, and select
Perform Network Forensics. Click the endpoint IP for which you want to perform forensics.
The Network Forensics page opens. The IP address is populated based on the endpoint selected to perform forensics.
Network Forensics 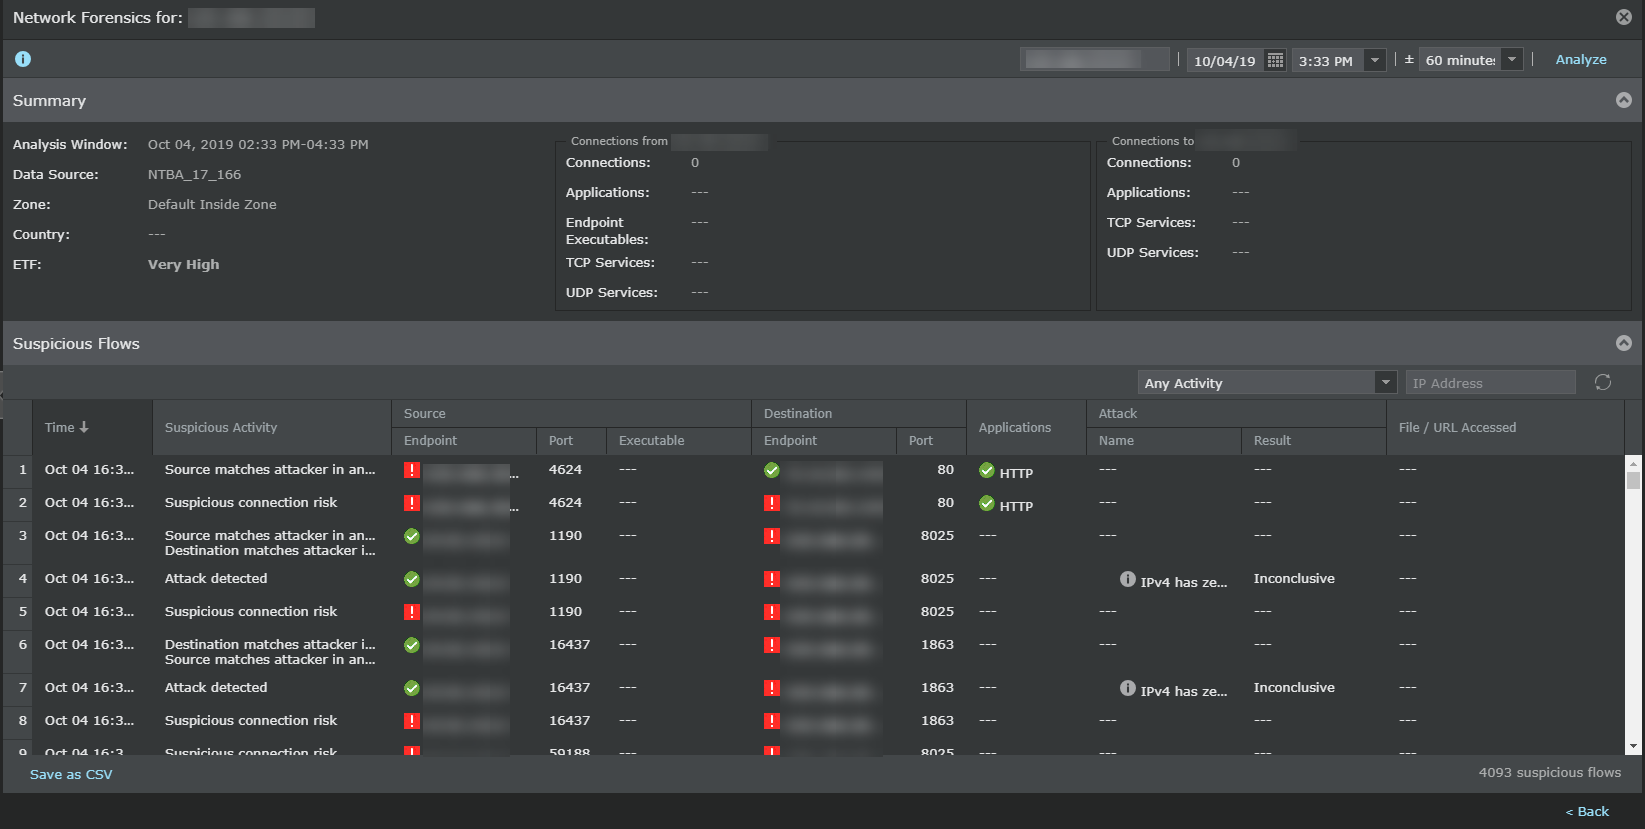
-
Select the date and time. Use the
 time to view endpoint behavior before and after an attack.
-
Click
Analyze.
Detailed information about the endpoint is displayed.
Click the
 icon to close the network forensics page.
For more information on network forensics, see the Network Threat Behavior Analysis Product Guide.