You can enter an IP address and track its network behavior for a specified time period.
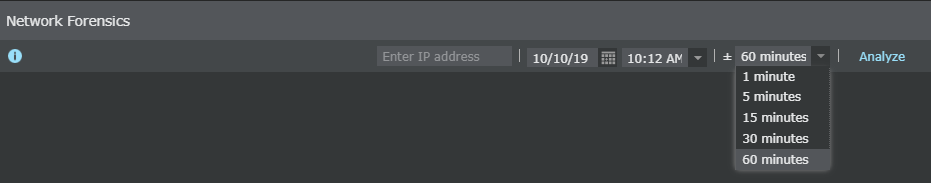
Go to Analysis → Network Forensics to analyze the recent behavior of the specific endpoint in the network, including conversations and events in the specified time period.Filter your view by choosing the time and date of your choice. Use the ± option to view data before and after an attack. This enables to analyze context-aware data and see network behavior of an endpoint in the network.
| Item | Description |
|---|---|
| Filter Criteria Panel | |
| Enter IP address | Enter the IP address of the endpoint whose network activities you wish to analyze. |
| Date | Select the date when the event occurred. |
| Event occurrence time | Select the time at which the event occurred. The event can be an attack, alert, or policy violation. |
| Analysis window | Select the time period in which you wish to track an endpoint's activities in the network. This includes activities performed by an endpoint before and after a security event. |
| Analyze | Retrieves suspicious flows, activities, and indicators for an event in the specified time period. |
Task
- In the Enter IP address field, enter an IP address for which you wish to view the suspicious flows and activity. Example: 1.1.1.9.
- Select the date and time. Use the ± time to view endpoint behavior before and after an attack.
- Click Analyze.
-
In the top panel, view
Summary for endpoint details and connections made to and from an endpoint.
Summary Panel 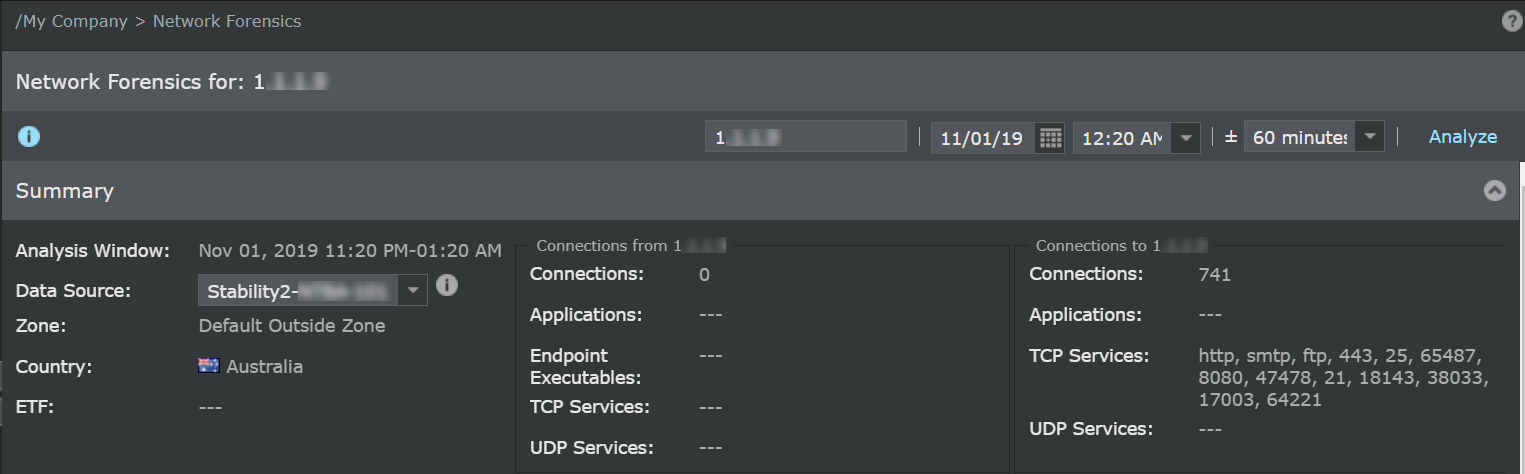
Item Description Summary Panel Endpoint Summary - Analysis Window — The period of analysis.
- Data Source — The NTBA device that is mapped to an endpoint IP address.
Note
If one or more NTBAs have an endpoint IP address within the same time range, you can view these NTBA devices from this drop-down list.
- Zone — The zone to which this endpoint belongs to.
- Country — The country of the endpoint.
- ETF — The ETF value assigned by NTBA to an endpoint.
Connections from endpoint Specifies the client connections from an endpoint that include the TCP and UDP services and ports. - Connections — The number of connections made from an endpoint.
- Applications — The applications accessed from an endpoint.
- Endpoint Executables — The executables accessed.
- TCP Services — The tcp services used by an endpoint.
- UDP Services — The UDP services accessed by an endpoint.
Connections to endpoint - Connections — The number of connections made to an endpoint.
- Applications — The applications used on an endpoint.
- TCP Services — The TCP services used on an endpoint.
- UDP Services — The UDP services accessed on an endpoint.
-
In the lower panel, view
Suspicious Flows for details like suspicious activity, applications, attack name, and files and URLs accessed.
- From the flows, select the indicator to view specific activity-based flows. Example: Blocked executable.
- View suspicious flows that have blocked executables involved in the attack.
Suspicious activity indicator filter 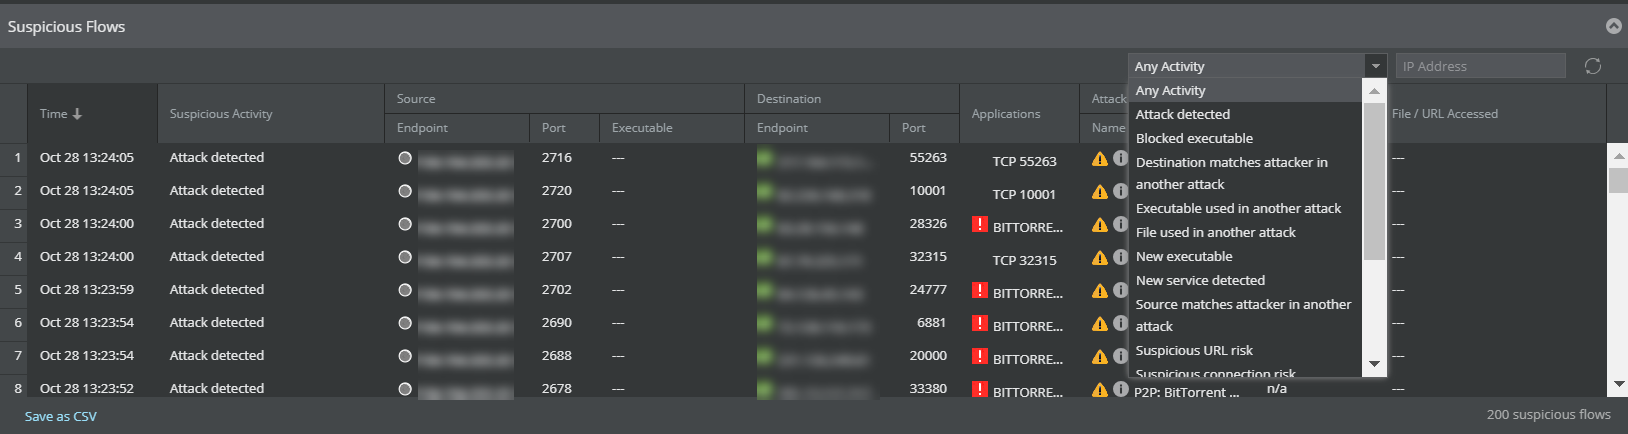
Item Description Suspicious Flows Panel Suspicious activity indicators View indicators that map to an event like an alert or attack. - Destination matches attacker in another attack
- Source matches attacker in another attack
- Suspicious endpoint risk
- Unverified endpoint risk
- Executable used in another attack
- Suspicious executable malware confidence
- Blocked executable
- New executable
- URL used in another attack
- Suspicious URL risk
- Unverified URL risk
- File used in another attack
- Suspicious file malware confidence
- Unverified file malware confidence
- Attack detected
- New service detected
IP Address Specify an IP address and use Search to view flows for this address. Time Displays the date and time when the suspicious flow for an event occurred. Tip
You can sort the flows view based on time.
Suspicious Activity Displays the indicator that specifies the suspicious activity performed like an URL accessed that was involved in another attack, blocked executable accessed and others. Source Specifies the source from which the flow was initiated for an endpoint. Details include endpoint and ports used. Destination Specifies the destination details like endpoint involved and port. Applications Displays the applications accessed from the endpoint. Attack Attacks for a specific endpoint that includes attack name and result. File/URL Accessed Specifies file or URL access details for a specific endpoint. - Click Save as CSV to export suspicious flows for analysis.