When network forensics is enabled, the Manager takes advantage of the NTBA Appliance to provide network activity for a given endpoint over a given time span. You can collect network forensic data for a time period for analysis.
Task
-
At the Global level, select
Devices → Global → NTBA Device Settings → Device Settings → Setup → Collection Settings.
Tip
At a device level, you can navigate to Devices → Devices → <NTBA Appliance> → Setup → Collection Settings. If you want to inherit the global level collection settings, select Use Global Settings.
- Enter the listening port and select Discard Duplicate Flow Records if you do not wish duplicate records. By default, the UDP port is set to 9996.
-
In the
Network Forensics area, specify the following:
Item Description Collect Network Forensics Data Select this checkbox to collect network forensics data. By default, this checkbox is selected. Applicable Attacks Select Any, IPS Attacks Only or NTBA Attacks Only. By default, this is set to Any. Collect Data Before the Attack For Select the time for which you wish to collect data before a security event. By default, this is set to 10 minutes. The time range is 1-60 minutes. Collect Data After the Attack For Select the time for which you wish to collect data after a security event. By default, this is set to 10 minutes. The time range is 1-60 minutes. Executable is 'New' if Not Seen in Previous Collect executable details if the executable is new in the network. By default, this is set to 30 days. The day range is 3-90 days. Service is 'New' if Not Seen in Previous Collect service details if the service is new in the network. By default, this is set to 30 days. The day range is 3-90 days. Forensic data collection 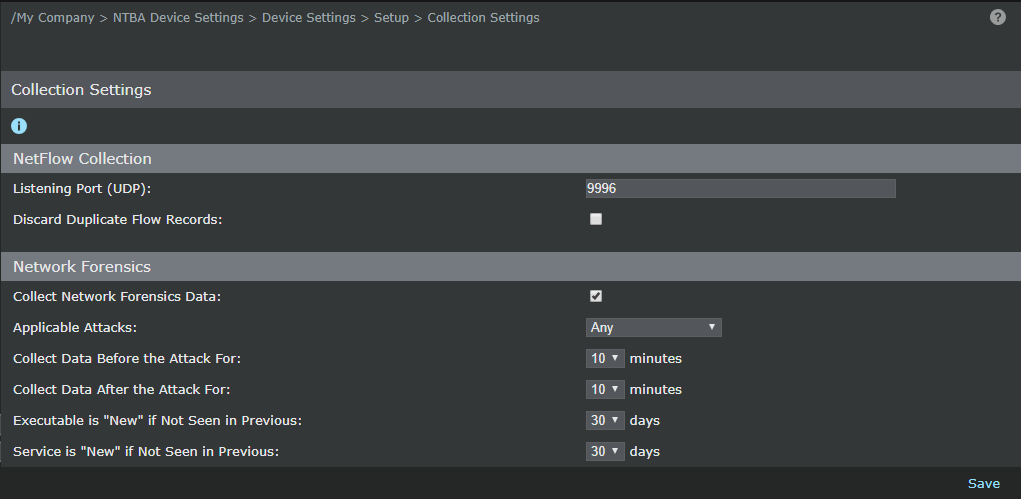
-
Click
Save.
Tip
If no forensic data is displayed, execute the show forensic-db details command to check if the network forensics feature is enabled or not. By default, this feature is enabled. You can use the set dbdisksize and show l7dcapstats commands to set the percentage of disk size for the forensic data and view layer 7 captured data details.