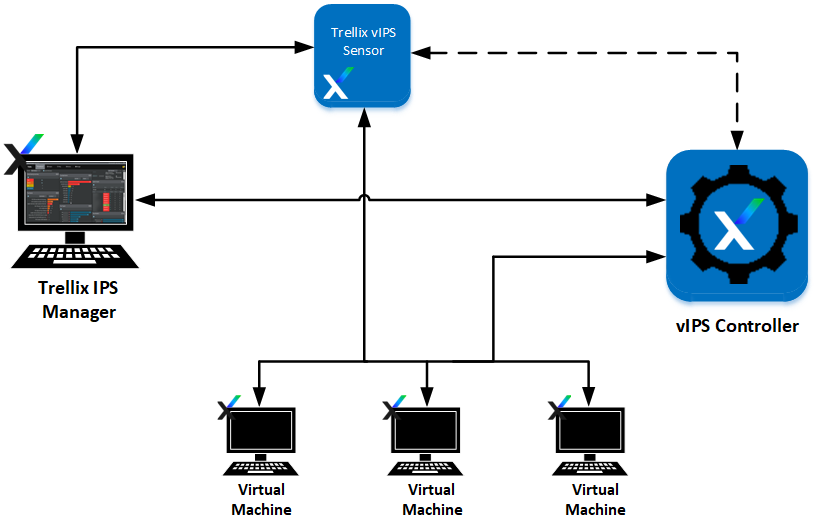
To protect your virtual machines in the public cloud environment, the following components of Trellix vIPS are deployed:
- Trellix IPS Manager
- Controller (Local and External)
Note
You can either configure the Local Controller, or deploy a public cloud instance for External Controller.
- Virtual IPS Sensor
- Virtual IPS Probe
When traffic flows to a virtual machine, the Virtual Probe installed in the virtual machine intercepts traffic and forwards it to the Virtual IPS Sensor for inspection in IPS mode. The Sensor then scans the traffic for any malicious activity. If there is no threat, the traffic is returned to the virtual machine. If a threat is found, depending on the response action configured, the Sensor will either black hole the traffic or return the traffic after generating an alert in the Manager. In IDS mode of deployment, the Virtual Probes intercept the traffic in the same way as in IPS mode, but instead of forwarding traffic to the Sensors and receiving it back, only a copy of the traffic is forwarded to the Sensors. The original traffic continues to be processed by the virtual machine.
The documentation is based on the assumption that you have created the subnets and resource groups in line with your company’s requirement.
Important
For a successful vIPS deployment, make sure the CIDR for subnet configuration is within the following reserved private IPv4 ranges:
- 10.0.0.0 - 10.255.255.255
- 172.16.0.0 - 172.31.255.255
- 192.168.0.0 - 192.168.255.255