Users are now moving to a more secure cipher suite like the DHE (Diffie-Hellman), ECDHE (Elliptic Curve Diffie-Hellman) ciphers. The RSA cipher suites have vulnerabilities and hence, there is a requirement to use stronger ciphers for secure connections. The stronger ciphers use the Perfect Forward Secrecy (PFS) method where the keys are generated dynamically for each session. The main advantage of this method is that if an attacker obtains a session key, the previous encrypted sessions cannot be decrypted.
In case of inbound SSL decryption for DHE/ECDHE cipher suites, an agent is installed in the web servers to be protected. The Agent passes the keys to the Sensor every time a connection is established with the web server. The session key must be passed to the Sensor as the keys are generated dynamically for every session. The key transfer is through TLS encrypted channel.
In the Agent based approach for inbound SSL decryption, the Trellix IPS's IPS Sensor is placed between the client and server. When the client sends a request to the web server, the Sensor intercepts the connection. The Sensor then initiates a connection with the server. This way the Sensor retrieves information about the keys used at both ends.
The Agent and the Sensor communicates over the management port for session key exchange. You can specify the number of concurrent connections between the Sensor and Agent in the Manager. This avoids unnecessary consumption of the management port bandwidth. The IP address of the web server should be added in the Manager which allows the server to communicate with the Sensor for inbound decryption.
You can download the Trellix SSL Agent from the Trellix Download Server. The link is available in the SSL Decryption page in the Manager. You can log into the Download Server using your Grant Number. The SSL Agent download file is available under Utilities & Connectors in the Download Server. The web server to be protected should have the Agent installed on it. In case of DHE/ECDHE ciphers suites since the public keys are dynamically generated, the Agent passes the keys to the Sensor every time a new connection is established. When the traffic flows through the Sensor, the keys are already available in the Sensor which helps in inspecting the traffic. When an attack is detected, the Sensor generates an alert in the Manager.
Note
The Trellix SSL Agent can be installed on Linux based web servers only across multiple distributions like RHEL, Ubentu, Fedora, etc.
Once the inbound SSL decryption feature is disabled, the Agent is disconnected from the Sensor. The keys shared with the Sensor is purged once the Agent is disconnected. You can view the number of active Agent connections using the CLI command show sslagentaccesscontrol status.
Inbound SSL decryption is supported in Inline, TAP, and SPAN modes.
Note
The Agent based method is supported only on NS9600 standalone and stack, NS9500 standalone and stack, NS9x00, NS7600, NS7500, NS7x50, NS7x00, NS5x00, and NS3600 series Sensors.
Note
Agent based method is not supported for AWS, Azure and GCP cloud platforms.
Below is the working of the Agent based inbound decryption method:
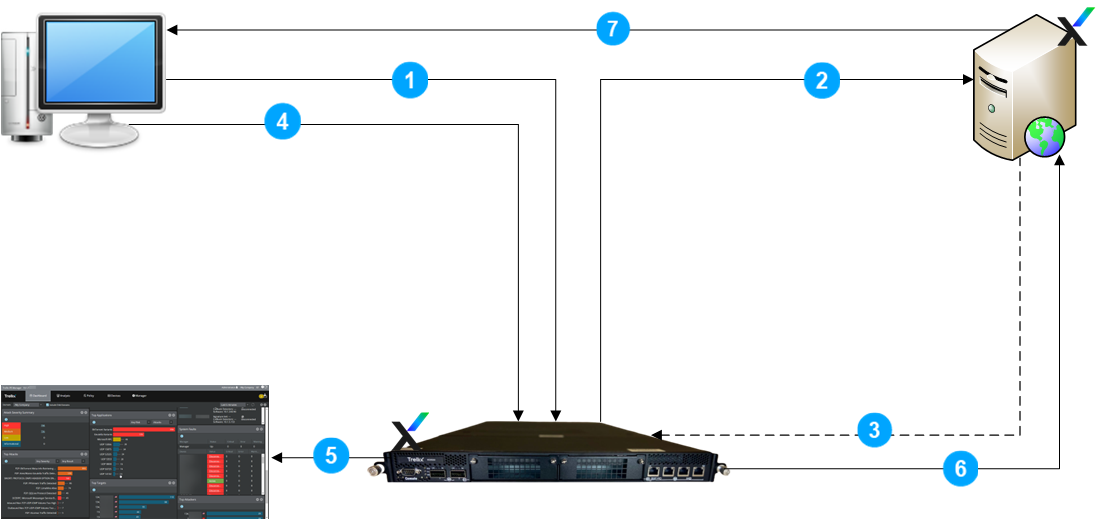
Steps:
The Sensor intercepts the initial request from the client. (Steps 1, 2, and 3 constitute the handshake process)
The Sensor forwards the request to the web server.
The Agent in the web server sends the SSL keys to the Sensor through an encrypted channel.
Using the SSL keys received from the Agent, the Sensor decrypts and inspects the subsequent requests from the client.
If an attack is detected, the Sensor generates an alert in the Manager.
If there are no attacks, the Sensor forwards the request to the web server.
The web server responds to the client's request.
Factors to be considered:
Port 8501 should be opened for communication between the Agent and the Sensor.
A restart of the web server is required once you install the Agent.
One Agent must be installed per web server to be protected. Any number of Agents can be installed across different web servers.
When you disable an enabled inbound SSL decryption feature, you must uninstall the Agent manually from the web servers.
In case of failure in the Sensor, the Agent is configured to have a fail-open policy where the traffic is allowed to flow. In such cases the traffic will not be inspected.
In case of a HA pair, IP addresses of both the primary and secondary Sensors must be available in the Agent.