Trellix IPS SSL functionality allows a Sensor to maintain a copy of a server's private key, thereby allowing the Sensor to properly determine the session key for SSL sessions terminating on that server. The Manager provides a passthru interface for importing a set of public/private keys of the servers to the Sensor. You import the SSL keys separately for each Sensor.
After you import the required SSL keys into the Manager, you must deploy changes to the corresponding Sensors. Then the Manager pushes the encrypted SSL keys to the corresponding Sensors. The Sensors keep the SSL keys in their volatile memory when they receive the SSL keys from the Manager. If a Sensor reboots, the SSL keys are lost. When the Sensor starts, it requests all of the SSL keys that the Manager has for that Sensor.
In case of inbound SSL traffic, the Manager stores an escrow of the imported keys it its database for Sensor recovery purpose. However, the Manager does not interpret the escrowed keys, nor does it attempt to recover the keys themselves in case a Sensor has lost its encryption key. In order to protect the imported keys both in transit and in escrow, the Manager uses the public key of the corresponding public/private key pair of the Sensor. Only the corresponding Sensor can decrypt the SSL keys.
Note
The Known key method is supported only on NS9600 standalone and stack, NS9500 standalone and stack, NS9x00, NS7600, NS7500, NS7x50, NS7x00, NS5x00, NS3600, IPS-VM600, and IPS-VM5000 Sensors.
Trellix IPS supports the PKCS12 format — file suffixes like ".pkcs12", ".p12", or ".pfx" — with an RSA private key no longer than 4096 bits. The keys work across all of a Sensor's Virtual IPS (VIPS) instances. The private key must be a part of the PKCS12 file.
Note
The Sensor decrypts inbound SSL traffic only on TCP port 443. To decrypt SSL on a non-standard port, make sure you have defined the non-standard port for HTTP with SSL enabled. To do this, select the device and go to Setup → Advanced → Non-Standard Ports.
Note
From 11.1 Update 8 release, jumbo frame traffic with SSL encryption is supported in NS9600 (standalone and stack), NS9500 (standalone), NS7600, NS7500, NS3600, IPS-VM600-SSL, IPS-VM600-VSS-SSL, and IPS-VM5000-SSL Sensors.
Note
For Virtual IPS Sensors, OpenSSL version 1.1.1 and above SSL decryption is not supported.
The steps to decrypt inbound SSL traffic by the Sensor are given below:
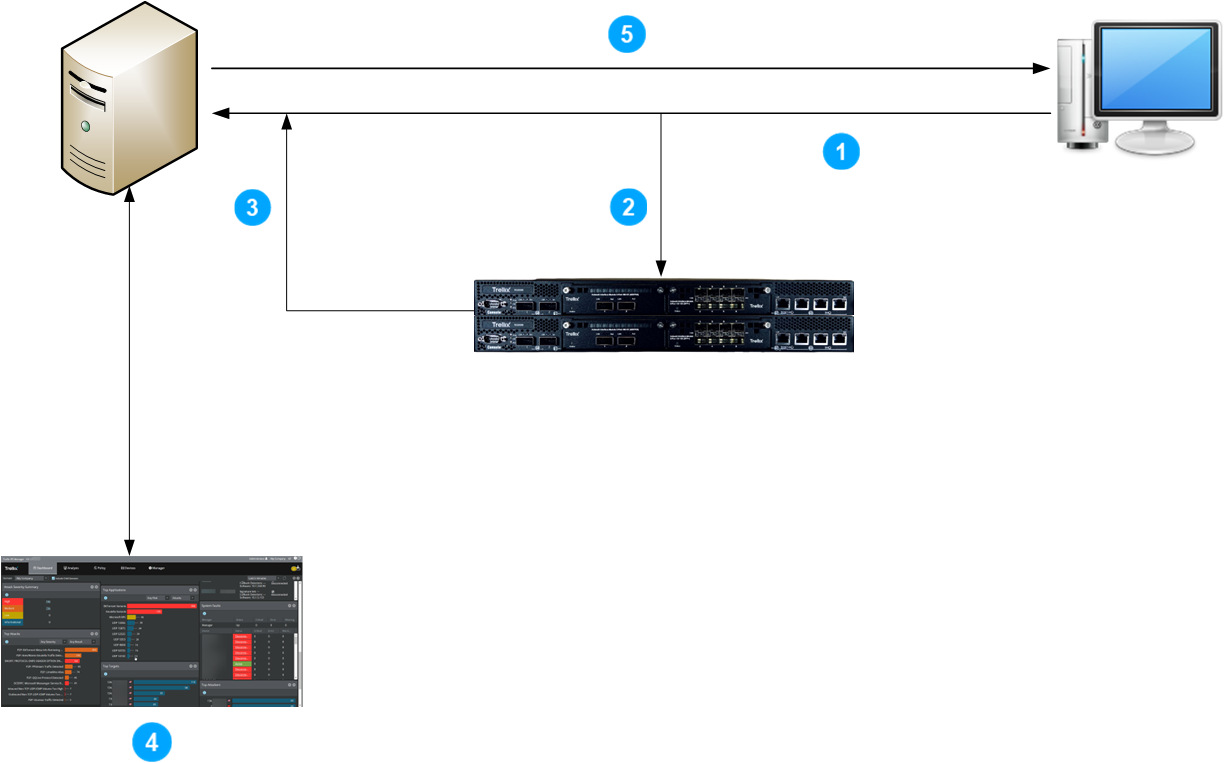
The client sends the secure request to the web server.
The Sensor intercepts the request, validates the certificates, and scans the packets.
If any malicious activity is found, the Sensor blocks the packets. If no malicious activity is found, the Sensor lets the request reach the server.
The Sensor raises an alert on the Attack Log.
The web server sends encrypted packets to the client.
Factors to be considered:
There is a performance impact when using the SSL decryption feature. See the section SSL best practices at the end of this chapter for Sensor throughput information when you enable SSL decryption.
Note
There is a performance impact when using the SSL decryption feature. If there is a lot of outbound SSL traffic from the client to the internet as well, it consumes SSL flows. Therefore, to enable the Sensor to effectively utilize the SSL decryption feature, it is recommended to bypass these outbound SSL traffic using ACL Ignore rules.
Inbound SSL Decryption is not supported by NS3500, NS3200, and NS3100 Sensors.
NS-series Sensors can support up to 1024 SSL certificates.
Sensors which are capable of SSL traffic inspection support both SSL session IDs and TLS session tickets to resume SSL session.
SSL session ID — The web server attaches the session ID when the web server sends the handshake to the client. The client can use the session ID to resume the SSL session with the web server.
TLS session ticket — The web server sends its secret state to the client, encrypted with a key only known to it as a session ticket. The client will store its secret information for a TLS session along with the ticket received from the web server. The client sends the session ticket along with its information to the Web server to resume the SSL session.