Below are some use case scenarios for inbound SSL decryption using the Agent method:
Scenario 1: Web server without load balancer
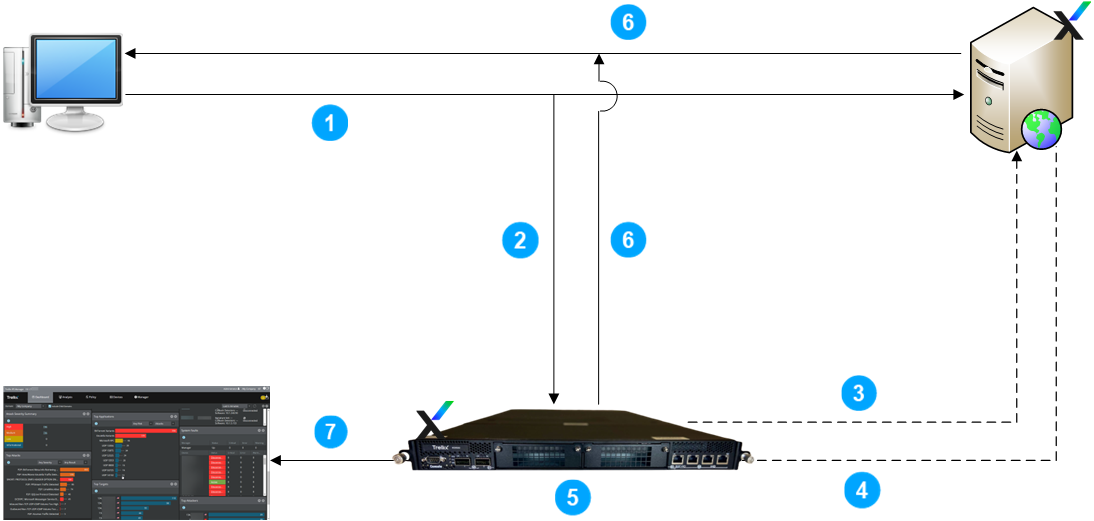
When you enable SSL decryption in the inbound direction, the web servers to which the clients send requests needs protection against malicious requests. This is possible by installing the Agent on the web server to be protected. When a client sends a request to the web server, the Sensor intercepts the traffic. The Agent on the web server exchanges the session key with the Sensor. The Sensor uses these keys to decrypt and inspect the traffic. If the traffic is clean, the web server sends a response to the request. In case of malicious requests an alert is generated in the Manager.
Steps:
The client sends a request to the web server.
The Sensor intercepts the connection.
The Sensor re-establishes the connection with the server through the Agent installed on the server.
The Agent sends the SSL keys to the Sensor through an encrypted channel.
The Sensor inspects the decrypted traffic.
If there are no attacks in the traffic the server responds to the client’s request.
If an attack is detected, the Sensor generates an alert in the Manager.
Scenario 2: Web server with load balancer
The load balancer usually directs the traffic from the client to the required web server. In such cases, the request from the client is directed to the load balancer first. The load balancer then directs the traffic to the required web server. As the request from the client can be malicious, the load balancer needs to be protected. The Agent shares the session keys with the Sensor for decryption must be installed on the load balancer.
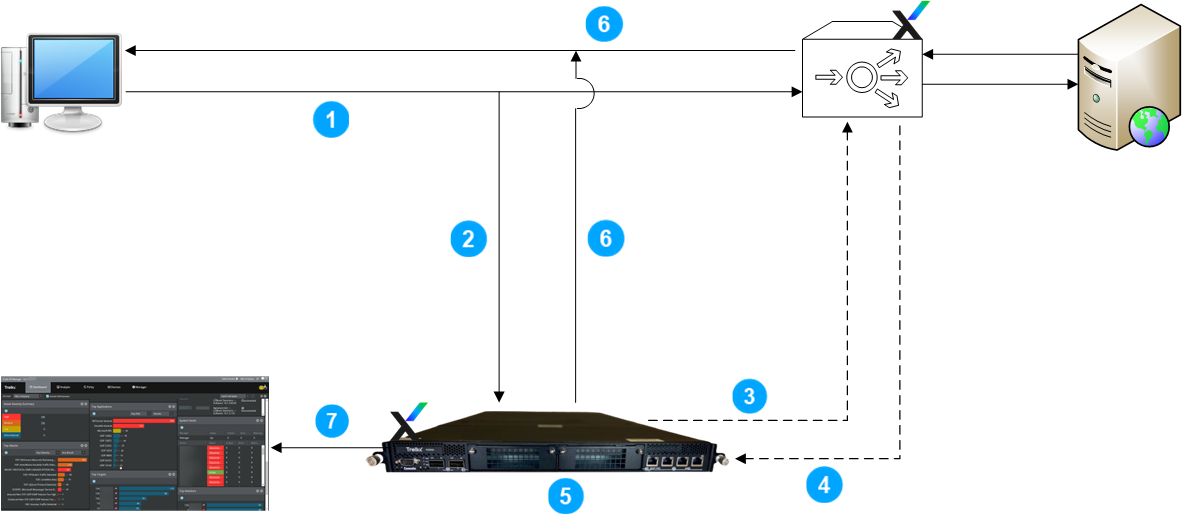
When the client sends a request to the web server, the traffic is first directed to the load balancer. The Sensor intercepts the traffic. The Agent on the load balancer exchanges the session key with the Sensor which the Sensor uses to decrypt and inspect the traffic. If the traffic is clean, the load balancer directs the traffic to the web server which then responds to the client’s request. In case of malicious requests an alert is generated in the Manager.
Steps:
The client sends a request which is directed to the web server through the load balancer.
The Sensor intercepts the connection.
The Sensor re-establishes the connection with the load balancer through the Agent installed on it.
The Agent sends the SSL keys to the Sensor through an encrypted channel.
The Sensor inspects the decrypted traffic.
If there are no attacks in the traffic the server responds to the client’s request.
If an attack is detected, the Sensor generates an alert in the Manager.