As a security administrator, you may want to analyze the root cause of a specific security event a few hours or days after an event has occurred. You may also want any supporting contextual data for an endpoint during that time interval.
NTBA performs context-aware network forensics to capture connections and layer 7 activity before and after a security event. This helps forensic analysis to be performed on the contextual data, against a set of predefined suspicious activity indicators.
NTBA collects forensic data for a target or attacker that is internal or external to the network. NTBA collects context-aware data as profile and forensic data. Profile data includes details like executables and services launched by an endpoint. Forensic data presents contextual data captured for specific minutes before and after a security event occurs like policy violation or an attack. By default, forensic data is collected for 10 minutes before and after an event.
The network forensics data collected by NTBA provides details such as connections made to a target and attacker, port information, network application, executables, URLs, and files. Metadata information like malware confidence, executable classification, reputation, and location are also shown if available. If a connection is suspicious, a Suspicious Activity indicator briefs the type of suspicious activity performed in the network.
How NTBA collects and stores context-aware data
When a security event like an attack occurs, NTBA performs the following high-level steps to collect context-aware data:
- Consolidates conversations with attack information like 5-tuple, URLs, files, and programs involved in the connection for a target or attacker.
- Collects the accessed URLs, files, executables, and connections for the specified time interval based on suspicious activity indicators. By default, these details are collected 60 minutes before and after an event occurred.
- Checks if the endpoint is an attacker or target.
- Collects data based on conditions that match the suspicious activity indicators.
Once the context-aware data is collected, NTBA stores this in the database for the configured period. By default, forensic data is stored for 30 days. You can configure the collection settings from Devices → Devices → <NTBA device> → Setup → Collection Settings.
The Manager enables you to configure the forensics collection settings, and retrieves the context-aware data from NTBA when you want to perform forensic analysis on a specific endpoint or attack.
The forensic data is stored as part of the virtual disk of NTBA. By default, the netflow data uses 60% and forensic data uses 40% of the disk space. By enabling export of Layer 7, the entire payload is not exported. Only fields related to HTTP, netbios, FTP, SMTP, file hash, and attack ID are exported. In HTTP application, specific fields of HTTP (like URI and host) are exported. Netflow monitoring is not made in real time as the statistics of the particular flow is sent every minute. If you upgrade from version prior to 9.1 to version 10.1, these default settings get applied during migration. You can modify these limits using the command set dbdisksize.
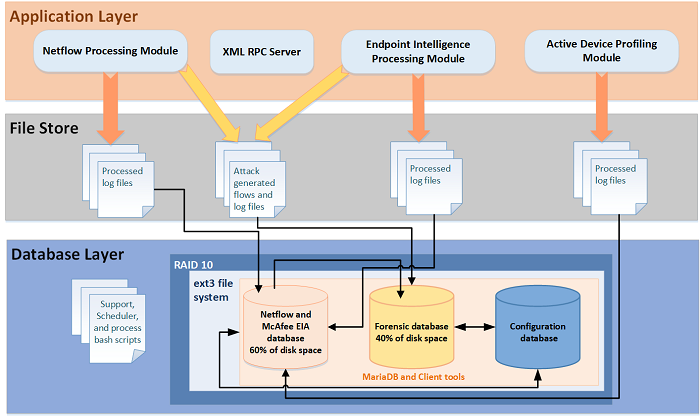
The RAID 10 layer is the first layer, followed by ext3 file system, and database layer is the container for the netflow, forensic, and configuration databases.
You can modify the forensic database pruning settings from the Devices → Devices → <NTBA Device> → Maintenance → Database Pruning page. For more details, see Maintenance of system data and files in Trellix Intrusion Prevention System Product Guide.
When you analyze an endpoint on the Network Forensics page, the Manager queries all the NTBAs and displays data from the NTBA that is mapped to the endpoint. On the Analysis → Network Forensics page, the displayed network forensic data is only from a single NTBA.
Note
If an IP address is mapped to more than one NTBA, the Network Forensics page has Data Source drop-down list to view network forensics data for NTBA mapped to an endpoint. The drop-down can be used to query the other NTBAs for forensic information.
Note
By default, if you directly navigate to the Network Forensics page to analyze an endpoint, the current date and time and analysis window of ± 60 minutes is displayed. If you perform forensics from other Manager UI paths for an endpoint, by default, the time of event occurrence and analysis window of ± 10 minutes is displayed.
Suspicious activity indicators
NTBA uses a set of predefined indicators to collect the forensic data. The indicators are triggered only when an attacker or target endpoint, flow, or executable makes a network connection in the configured analysis time window.
For example, on the Network Forensics page, you select an IP 1.1.1.6 that is involved in a policy violation. You select an analysis time of ±30 minutes to analyze the collected flows before and after the policy violation happened, and click Analyze. The suspicious flows and activity indicators are displayed based on connections made in the network in this defined time window of one hour.
NTBA collects forensic data based on the following rules:
| Suspicious activity indicator | Description |
|---|---|
| Destination matches attacker in another attack | A target endpoint was involved in another attack or traffic from/to this endpoint. |
| Source matches attacker in another attack | An attacker endpoint was involved in another attack or traffic from/to this endpoint. |
| Suspicious endpoint risk | Endpoint made a connection to another endpoint with GTI risk level of Medium Risk or High Risk. |
| Unverified endpoint risk | Endpoint made a connection to another endpoint with GTI risk level of Unverified. |
| Executable used in another attack | Executable, for example, chrome.exe was involved in another attack or traffic from/to this endpoint. |
| Suspicious executable malware confidence | Endpoint accessed an executable that has malware confidence level above Medium. |
| Blocked executable | Endpoint accessed a blocked executable. |
| New executable | Endpoint accessed a new executable that has not been previously seen in the last x* days.
*x refers to the number of days defined on the Devices | NTBA Device Settings | Device Settings | Setup | Collection Settings page. |
| URL used in another attack | Endpoint accessed a URL that was involved in another attack or traffic from/to this endpoint. |
| Suspicious URL risk | Endpoint accessed a URL with GTI risk level of Medium Risk or High Risk. |
| Unverified URL risk | Endpoint accessed a URL with GTI risk level of Unverified Risk. |
| File used in another attack | Endpoint accessed a file that is involved in another attack or traffic from/to this endpoint. |
| Suspicious file malware confidence | Endpoint accessed a file with suspicious malware confidence of Medium or High. |
| Unverified file malware confidence | Endpoint accessed a file with suspicious malware confidence of Unknown. |
| Attack detected | Specific suspicious flow generated an attack in the network. |
| New service detected | A new service was installed on an endpoint that has not been previously seen in the last x* days.
*x refers to the number of days defined on the Devices → NTBA Device Settings → Device Settings → Setup → Collection Settings page. |
On the Analysis → Network Forensics page, these are displayed in the Suspicious Activity column. You can also use these indicators as filters from the Any Activity drop-down list to view specific suspicious activity-based flows in the network.
Note
If McAfee EIA is disabled, executable-related indicators like executable used in another attack are not available. Similarly, if Trellix GTI is disabled, reputation-based indicators are not functional.