Once the integration with the Trellix NI is enabled, you can view the flow data, L7 metadata, and alert data using the NI web UI. When you log into the NI web UI, NI Dashboard is displayed. The predefined dashboard displays a collection of widgets available for the appliance. These widgets provide high-level views of the threat intelligence gathered by the appliance.
Navigate to  (or, mega menu) → → . The Search page is displayed. NI allows you to configure multiple dashboards as per your investigation requirement and customize each of them with the help of multiple widgets.
Note
Some screenshots and related web features referenced in this section may vary slightly from the latest NI Web UI.
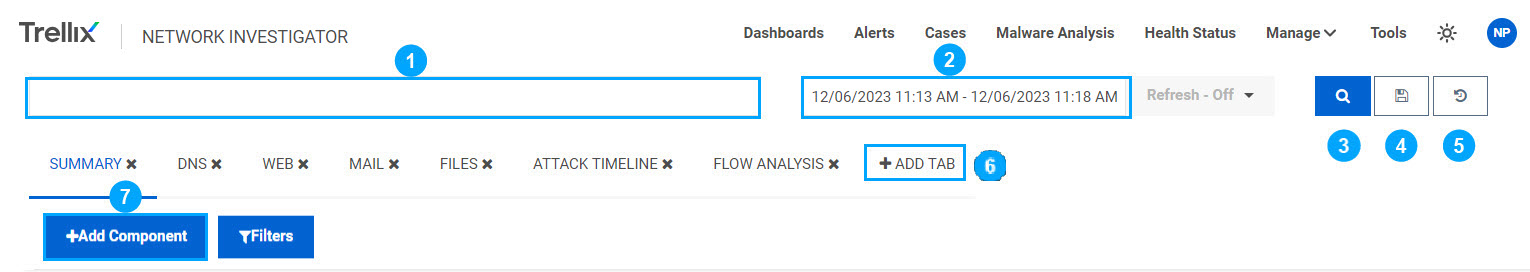
The Search page on NI web UI comes with the following options:
Callout | Components | Description |
|---|---|---|
1 | Query Bar | You can enter a single term or phrase query into the Query Bar and look for indexed metadata in the flow data, L7 metadata, and alert data displayed on the NI. You can use automatic queries or manually construct queries in the Query Bar to view and analyze specific information. |
2 | Time picker | It allows you to select a specific time duration while viewing and analyzing flow data, L7 metadata, and alert data on the NI. The configurable time interval options provided are 5 Minutes, 15 Minutes, 1 Hour, 6 Hours, 12 Hours, 24 Hours, 2 Days, and 7 Days. You can also select a custom time period. You can choose time interval in UTC or Local Time format. |
3 |  or Search Icon | Clicking this Search Icon helps you run a query. |
4 |  or Save Query button | The Save Query button helps to save a specific query in the NI for future use. |
5 |  or Reload Saved Query button | The Reload Saved Query button provides access to all saved queries (private as well as saved) and helps run a specific query quickly. |
6 |  | This button allows you create additional tabs within the Dashboards in which you can customize widgets available to further refine the display of flow data, L7 metadata, and alert data exported to NI from Trellix IPS |
7 |  | This button enables you to add one or more widgets within a tab of NI Dashboards, some of which include Alert Summary, Bar Chart, Donut Chart, Event Table, Protocol Summary, File Info, and Group Table. |
Searching and viewing search results on Event Table
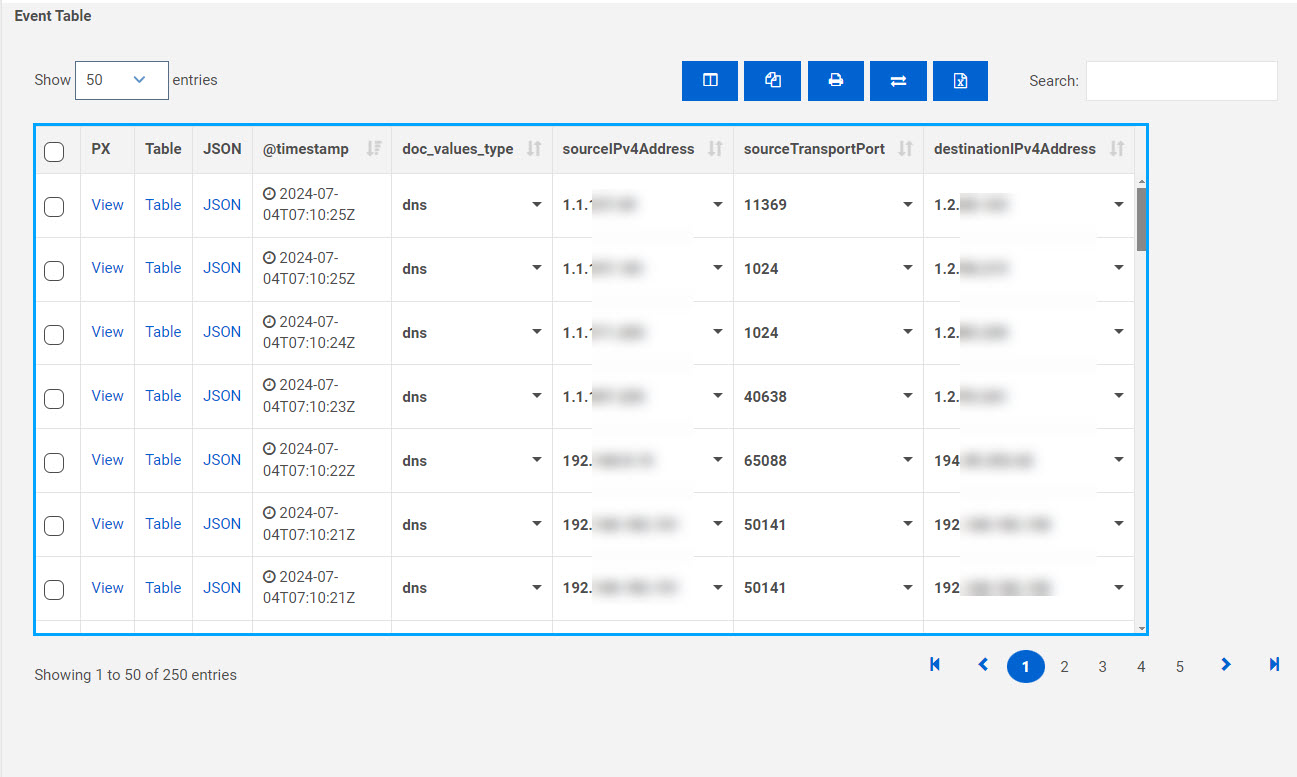
The Event Table widget under the Summary tab of NI Search page displays all the flow and alert data in a tabular format. It shows the alert and flow details in JSON format, and provides a table view displaying the event timestamp, the nature of the event displayed, source and destination IPv4 address, and source and destination transport port. It also shows the search result for any search query run on NI Query bar.
Note
If you are unable to see or want to add an Event Table in a selected Dashboard, you can do so by clicking button, and selecting Event Table option under the Select Widget drop-down. You can then configure the time interval to view specific data.
 |
To order to perform a search, you need to enter single terms or phrases in the Query Bar. You can combine multiple terms and phrases along with boolean operators and special characters to form a search query and look through indexed metadata fields, and then use filters to further refine your search results. You can use the automatic completion feature in the Query Bar to perform basic and advanced field searches.
For example, if you want to view only flow data entries in the Event Table, do the following:
Click inside the Query Bar to display a list of field names and then scroll down to select
doc_values_type:field.Type
flowwithin the box following the colon. Remove spaces, if any, between the field name and term and press Enter.Note
Spaces between the fieldname: and the term or value will return the message
No Data Availableor incorrect query resultsNote
You must press Enter to apply query syntax or exceptions to the search query.
Specify a start and end time of the search on the Time Picker.
Now, click the
icon to run the search.The figure below shows only flow data entries as search results on the Event Table after running
doc_values_type:flowas search query.Event Table showing only flow data as per the search query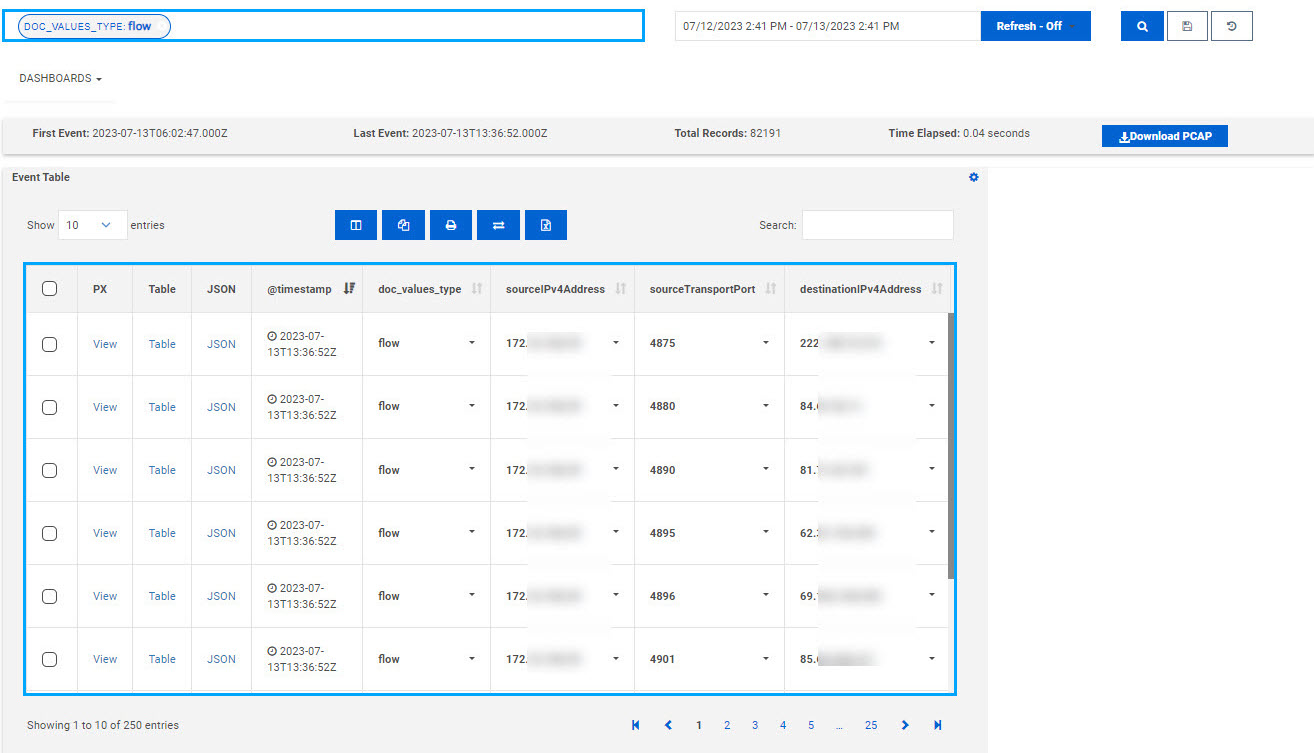
You can also combine multiple terms and phrases with boolean operators and/or special characters to form complex and advanced queries. For example, if you wish to see the alert and flow data for specific source IPv4 address and destination IPv4 address, do the following:
Click inside the Query Bar to display a list of field names. Scroll down and select
sourceIPv4Address:and press Enter.Type the source IP address that you want to track after the colon within the box and press Enter.
Begin typing
operatorin the Query Bar to see the list of operators and selectANDfrom the drop-down. Press Enter.Click inside the Query Bar, select
destinationIPv4Address:and press Enter.Type the destination IP address that you want to track after the colon within the box and press Enter.
Specify a start and end time of the search on the Time Picker.
Now, click the
icon to run the search.The figure below shows refined data entries as search results on the Event Table after running
sourceIPv4Address:1.1.1.107ANDdestinationIPv4Address:1.1.1.57as search query.Event Table showing flow and alert data specific to source and destination IP address provided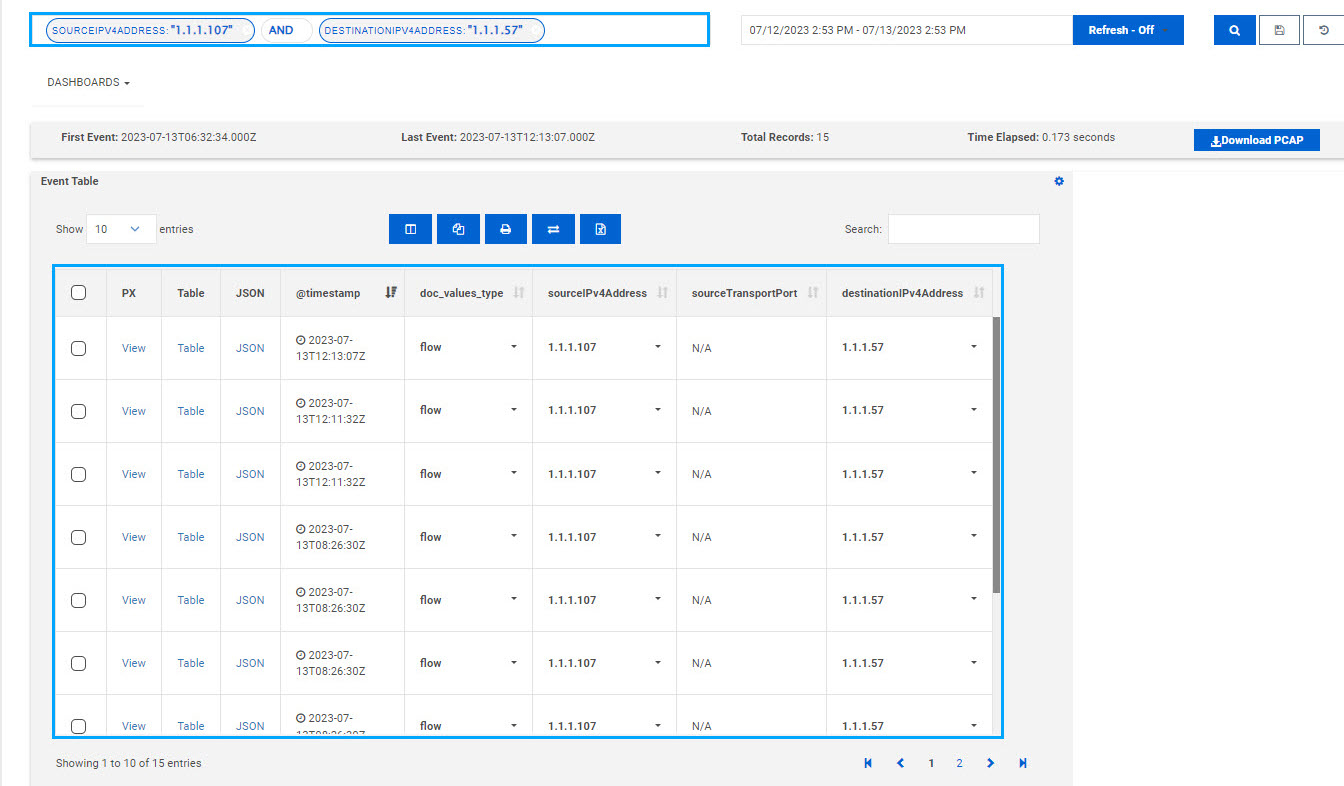
Analyzing flow data and alert data entries displayed on NI in JSON format
You can view and analyze flow data, L7 metadata, and alert data entries in the JSON format by clicking the JSON link in the document row of the Event Table. For an alert data entry, the JSON format contains many important fields, some of which include appliance name, IPS ID, attack category, BTP, attack severity (as listed in the confidence field), and detection mechanism. For a flow data entry, some of the notable fields include the client name, device ID, device IP, and device type.
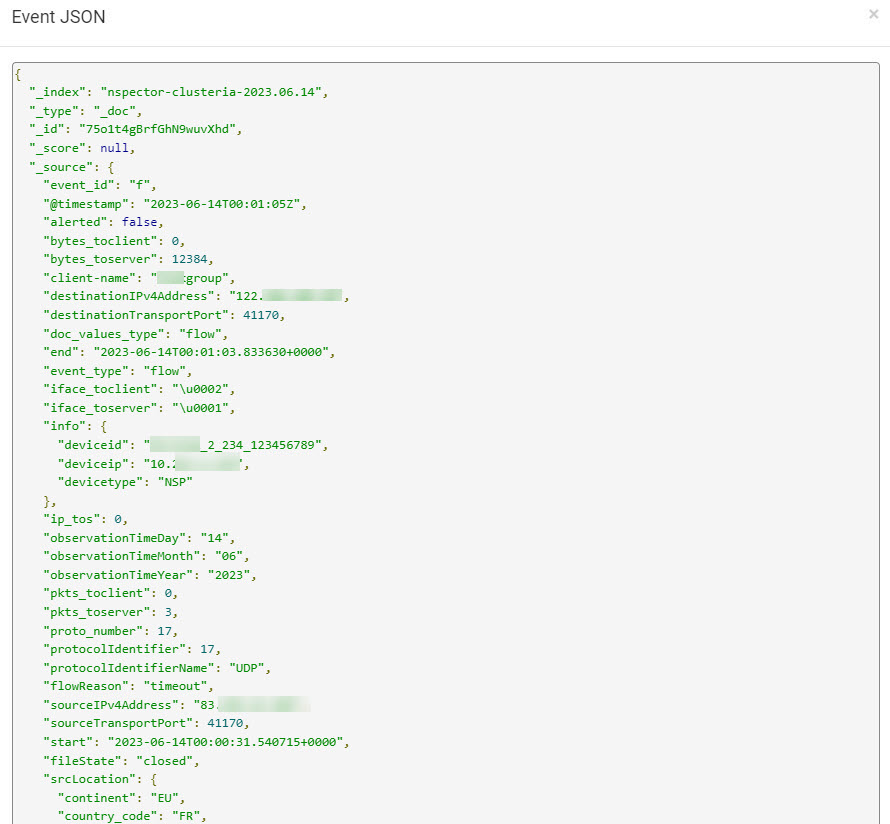
Sorting and Filtering options in Event Table
The Event Table comes with many sorting, filtering, and configuration options for viewing the flow and alert data and analyzing them via search query. Some of these options include the following:
You can view all the important details for the specific flow or alert entry by clicking the Table link in the document row.
you can modify the default view of the table by clicking the
 icon in the Event Table panel to add or remove any field column as per your requirement.
You can click any field column to see the flow and alert data entries in an ascending or descending order for that specific field.
You can configure the number of flow or alert data entries you want to see within the Event Table. The configuration options are 10, 25, 50, 100, and 250 entries.
You can export the table content containing the flow and alert entries displayed on the Event Table by generating a .CSV file. To do so, click the
 icon and download the file.
Analyzing the packet View of the flow data and alert data entries on the Packets tab
You can perform a deep dive into the flow or alert data entries of your interest by viewing the associated packet data at a connection, packet, and payload level. To do so, click the checkbox(es) next to the flow/alert data entries you want to reconstruct in the Event Table and click the Reconstruct icon. NI processes the entries (or events) selected and displays the results on the Packets tab under the Dashboards page. Some of the activities that you can perform on the Packets tab include the following:
View all packets for a connection associated with any flow/ alert data entry, which include the packet flow direction, source and destination IPs, source and destination ports, and the packet protocol for each packet session.
Analyze the information available for a selected packet in tree view in the Packet Details section.
Analyze the hex data for a selected packet in the Hex Details section.
Follow the stream for a selected connection by clicking the Follow link at the top of the Connections list.
Download and collect all packets associated with selected events by clicking the Download Merged PCAP button.
Important
To access the Packets tab on NI Dashboards, the NI appliance integrated with the Trellix IPS must be connected to a PX Series appliance and its Host IP must be added in the Client Group that is configured and associated with the Manager at the domain and/or device level.
For more information on the NI platform and how to use it during the investigation of any network event, refer to Network Investigator User Guide.