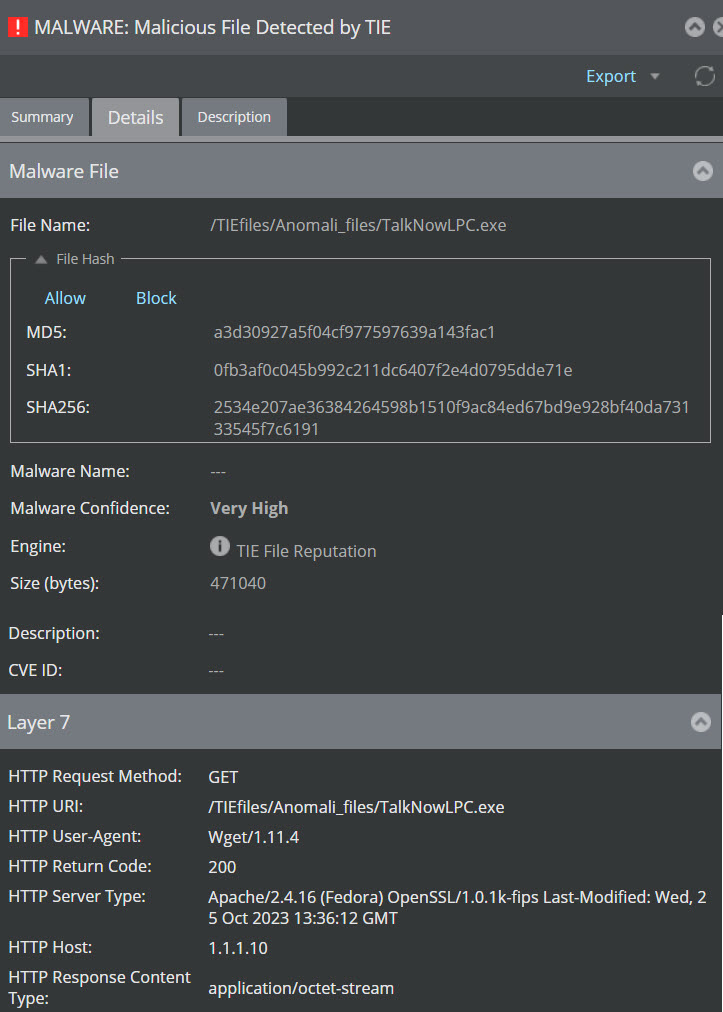
After you have enabled Threat Intelligence Exchange for the Sensor, if you have configured this engine in your advanced malware policy, you will be able to view malware files by this engine in the Manager.
Consider a scenario in which a file is detected by the Sensor. The following sequence illustrates how the Sensor queries Threat Intelligence Exchangeand provides the results to be displayed in the Manager. However, this is only one of the ways of viewing the results. For more options, see the Trellix Intrusion Prevention System Product Guide.
When a file appears on the network, the Sensor computes a file hash and checks the allow list and block list in the Manager. When this file hash is not found in these lists, it queries Threat Intelligence Exchange through DXL.
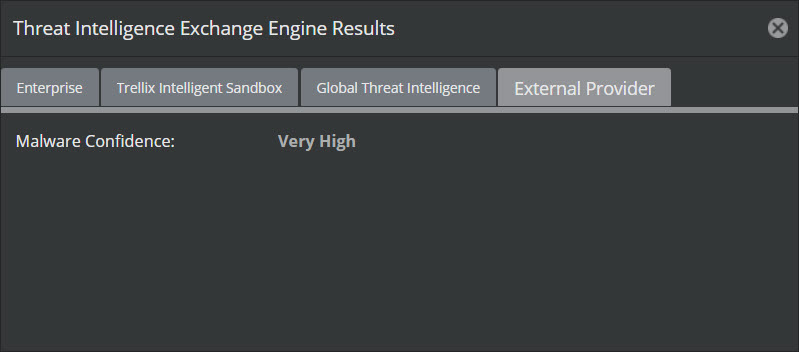
Threat Intelligence Exchange receives the malware confidence for this file hash from Enterprise, Intelligent Sandbox, Global Threat Intelligence, and External Provider and returns the various parameters to the Sensor.
The Sensor finds that the malware confidence for the file hash is reported as Very High by the External Provider and, as a result, gives the file an overall malware confidence of Very High too.
You see the malware confidence in the Malware Files page under the TIE / GTI File Reputation column.
The Sensor also raises a MALWARE: Malicious File Detected by TIE Engine alert.
Malware Files page in the Manager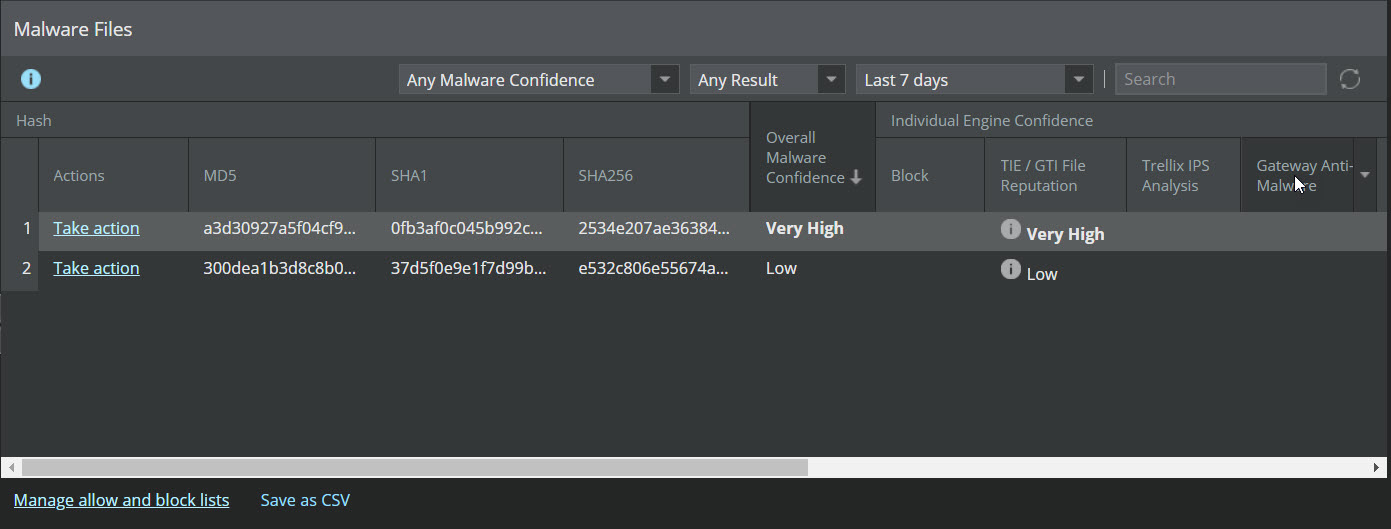
Click the
 icon to view file reputation from each of the three sources.Threat Intelligence Exchange Engine results
Or, you can click the MALWARE: Malicious File Detected by TIE Engine hyperlink to be directed to the Threat Explorer with a filter on the alert.
Threat Explorer page with a filter on that alert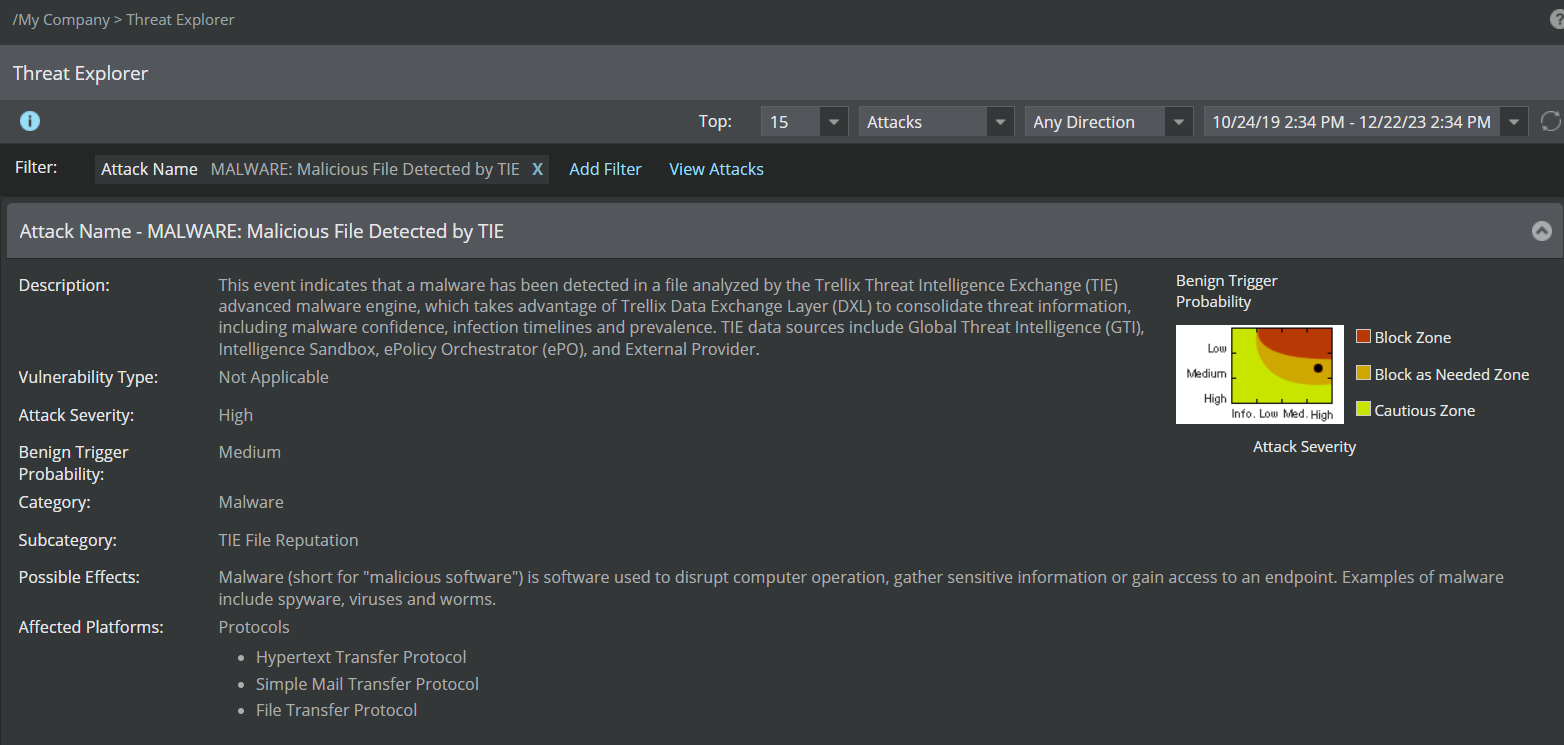
Clicking the View Attacks button opens the Attack Log page that shows all alerts for this file hash.
Double-clicking on one of these alerts opens the alert details panel.
You can view the malware details on the Details tab where you see the details of the file hash from each of the providers. On this panel, you notice the correlation, if applicable to that file hash, between the provider and the overall malware confidence.
Malware Details panel, Alert Details window