Smart Vision attacks are sent by the Manager to NI as base events. NI consumes and utilizes these base events as part of its SmartVision correlation feature. For more information, refer to Trellix Network Investigator documentation.
Below are some important points to keep in mind when you start working with SmartVision attacks:
Manager and Sensor running on 11.1 Update 7 versions or later, along with a compatible signature set (11.10.23.3 and above) that includes SmartVision attack signatures.
If you want to enable the detection and export of SmartVision attacks related L7 metadata and alerts related to SMB and DCERPC protocols, you need to use Manager and Sensor running on 11.1 Update 8 and later, along with a compatible signature set (11.10.28.4 and above) that includes SMB and DCERPC related attack signatures.
For effective detection and correlation SmartVision attacks/incidents on NI, there should be successful integration between Trellix IPS and Trellix NI.
SmartVision attacks are automatically included in the in default IPS policies (that are Default Prevention, Default Testing, Default Detection, and Default Exclude Informational) with the severity level set to Low (2) and higher.
Note
SmartVision attack signatures are not included in Default DoS and Reconnaissance Only policy.
You can configure and update the settings of SmartVision attacks in the Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS page, with a few exceptions as stated below:
The Block and Quarantine actions are disabled by signature set and not available for configuration for the attack IDs related to SmartVision attacks in the Manager. For related information, See Configure attack details and Customize attacks across policies.
SmartVision attack details configuration in Manager
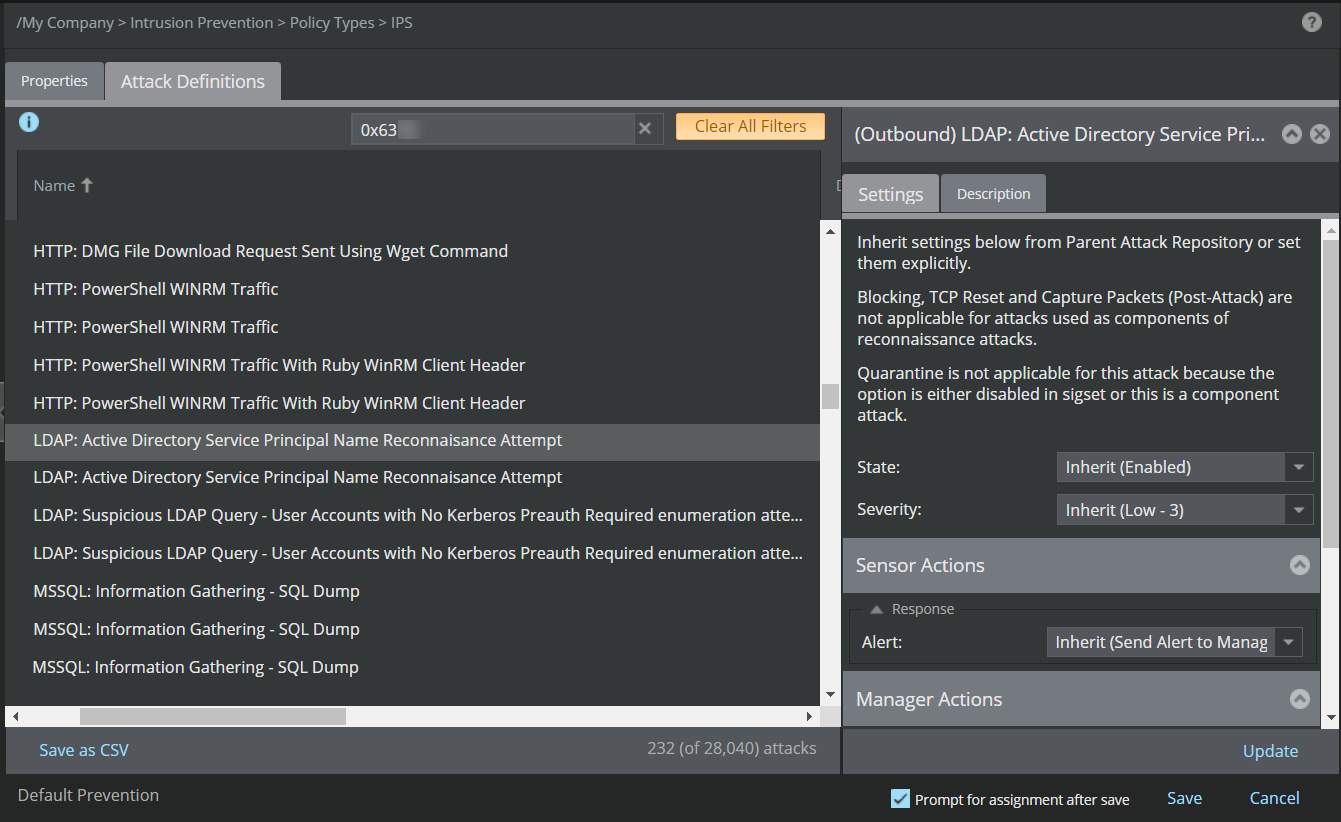
The packet logging option is disabled in signature set for SmartVision attacks. As a result, the Capture Packets section (for both Attack and Pre-Attack and Post-Attack) are not available for configuration for SmartVision attacks in the Manager. For related information, For related information, See Configure attack details and Customize attacks across policies.
Note
If you are using a Manager running on version older than 11.1 Update 7 release and using a signature set that includes SmartVision attack rules, the Capture Packets section will still be visible during attack details configuration for the related attack IDs.
The Manager performs conditional/dynamic signature set compilation and sends SmartVision attack signatures to only Sensors that are running on 11.1 Update 7 software version or later, and have integration with Trellix NI enabled at the domain or device level.
After changing NI integration configuration in selected Sensors over the Client Group Association tab (at both domain and device levels), you must deploy configuration changes to the Sensor to ensure the new signature set updates have been deployed to the required Sensors. For more information, see Enable NI integration in the Manager.