ePO - On-prem uses a self-signed certificate to secure HTTPS communication with web browsers. There are two types of self-signed certificate:
Default self-signed certificate — Generated by ePO - On-prem. You can renew it from the ePO console when needed.
Custom self-signed certificate — A certificate you create yourself, for example with OpenSSL, and import to replace the default certificate.
To do this | See |
|---|---|
Renew the default self-signed certificate | |
Create a custom self-signed certificate and use it in place of the default certificate |
Note:
To have a third party, for example Verisign or Microsoft Windows Enterprise Certificate Authority, create a signed certificate for ePO - On-prem, see How to use OpenSSL to generate a custom TLS certificate for the ePO browser console connection.
Renew the default ePO self-signed certificate
The default ePO (Tomcat) self-signed certificate can be renewed if needed by regenerating it in the ePO console, and then restarting the ePO services.
Note:
This task applies to the default self-signed certificate. To create a custom certificate, see Create and import a custom SSL certificate with OpenSSL.
Select Menu → Configuration → Server Settings.
From the Setting Categories list, select Server Certificate, and click Edit at the bottom right corner.
Under New certificate, select Regenerate a self-signed certificate and private key, and click Save.
After the changes are saved, restart the ePO services:
Press Windows+R.
Type
services.mscinto the field and press Enter.Right-click each of the following services, and select Restart:
Trellix ePolicy Orchestrator 5.10.0 Application Server
Trellix ePolicy Orchestrator 5.10.0 Event Parser Service
Trellix ePolicy Orchestrator 5.10.0 Server
After you restart the ePO services, the ePO (Tomcat) self-signed certificate is in use.
Create and import a custom SSL certificate with OpenSSL
You can use the OpenSSL toolkit to create a custom self-signed certificate and import it into ePO to replace the default certificate.
Sometimes you might not be able to, or want to, wait for a certification authority to authenticate a certificate. During initial testing or for systems used on internal networks, a custom self-signed certificate can provide the basic security and functionality needed.
There are many tools you can use to create and self-sign a certificate. This task describes the process using OpenSSL for Windows software. To have a third party, for example Verisign or Microsoft Windows Enterprise Certificate Authority, create a signed certificate for ePO - On-prem, see How to generate a custom SSL certificate for use with ePO using the OpenSSL toolkit.
Before you begin
Install the OpenSSL for Windows software. OpenSSL is available from:
http://www.slproweb.com/products/Win32OpenSSL.html
The file structure used in the following task is:
C:\ssl\— Installation folder for OpenSSL.C:\ssl\certs\— Used to store the certificates created.C:\ssl\keys\— Used to store the keys created.C:\ssl\requests\— Used to store the certification requests created.
OpenSSL does not create these folders by default. They are used in these examples and can be created to help you find your output files.
Note:
We recommend that you use certificates with RSA public key lengths of 2048 bits or greater.
To generate the initial certificate key, type the following command at the command line:
C:\ssl\bin>openssl genrsa -des3 -out C:/ssl/keys/ca.key 2048The following screen appears.
Loading 'screen' into random state - done
Generating RSA private key, 2048 bit long modulus
........................++++++
.++++++
unable to write 'random state'
e is 65537 (ox10001)
Enter pass phrase for keys/ca.key:
Verifying - Enter pass phrase for keys/ca.key:
C:\ss\bin>
Enter a passphrase at the initial command prompt and verify the pass phase at the second command prompt.
Note
Make a note of the passphrase you enter. You need it later in the process.
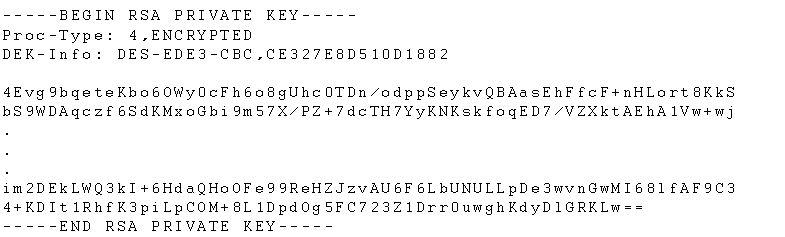
The file name
ca.keyis generated and stored in the pathC:\ssl\keys\.The key looks similar to the following example.
To self-sign the certificate key you created, type the following command at the command line:
openssl req -new -x509 -days 365 -key C:/ssl/keys/ca.key -out C:/ssl/certs/ca.cerNote:
Some web browsers no longer accept certificates signed with the SHA-1 hash algorithm. Make sure your custom certificate and its certificate chain are signed with SHA-256. For details, see ERR_SSL_VERSION_OR_CIPHER_MISMATCH (when you access the ePO on-premises console on a web browser).
The following screen appears.
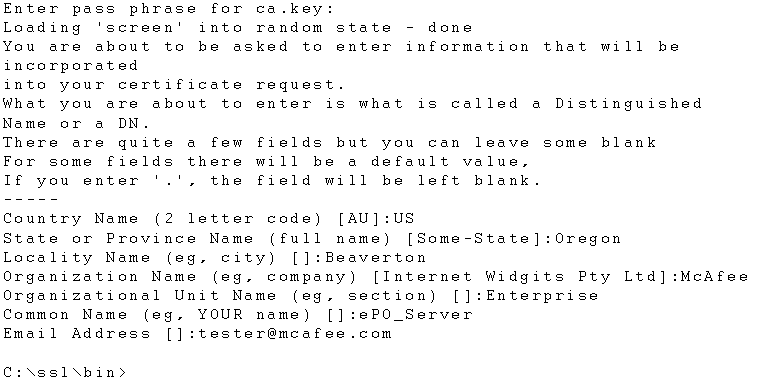
Type the information needed after the following command prompts:
Country Name (two letter code) [AU]:State or Province Name (full name) [Some-State]:Locality Name (for example, city) []:Organization Name (for example, company) [Internet Widgits Pty Ltd]:Organizational Unit Name (for example, section) []:Common Name (for example, YOUR name) []:Note
At this command prompt, type the name of your server, for example your ePO - On-prem server name.
Email Address []:
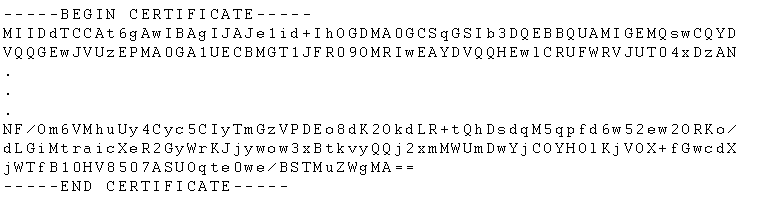
The file named
ca.ceris generated and stored in the pathC:\ssl\certs\.The self-signed certificate looks similar to the following example.
To upload the self-signed certificate, open the Edit Server Certificate page.
Select Menu → Configuration → Server Settings.
From the Setting Categories list, select Server Certificate, and click Edit.
Browse to the server certificate file, then click Open.
In this example, browse to
C:\ssl\certs\and selectca.cer.If needed, type the PKCS12 certificate password.
If needed, type the certificate alias name.
Browse to the private key file, then click Open.
In this example, browse to
C:\ssl\keys\and selectca.key.If needed, type the private key password, then click Save.
Restart ePO - On-prem for the change to take effect.