The third essential step in Vulnerability Manager configuration is configuring the Vulnerability Manager Server settings. The Manager needs to connect to the Vulnerability Manager Server to access the Scan engine. Scan engine is the component of Vulnerability Manager system that scans the hosts in your network for vulnerabilities.
Trellix IPS-Vulnerability Manager integration supports three versions of Vulnerability Manager engine: 6.8, 7.0, and 7.5. In the Manager, configuration settings for the scan engine include the engine version and logon credentials to the scan engine server.
Tip
Before configuring Vulnerability Manager Server Settings, you should enable Vulnerability Manager integration and configure Vulnerability Manager database settings.
Below are the high level steps for successfully configuring the server settings:
Before saving the server settings, make sure to provide full access rights to the user account used to run the Manager service. In case the required permissions are not provided, the Failed to save settings error appears.
Start the FCM Agent Service before retrieving the MVM certificate.
When changing the server settings, restart the FCM Agent Service even if the service is already running.
To configure the Vulnerability Manager server settings, do the following:
Task
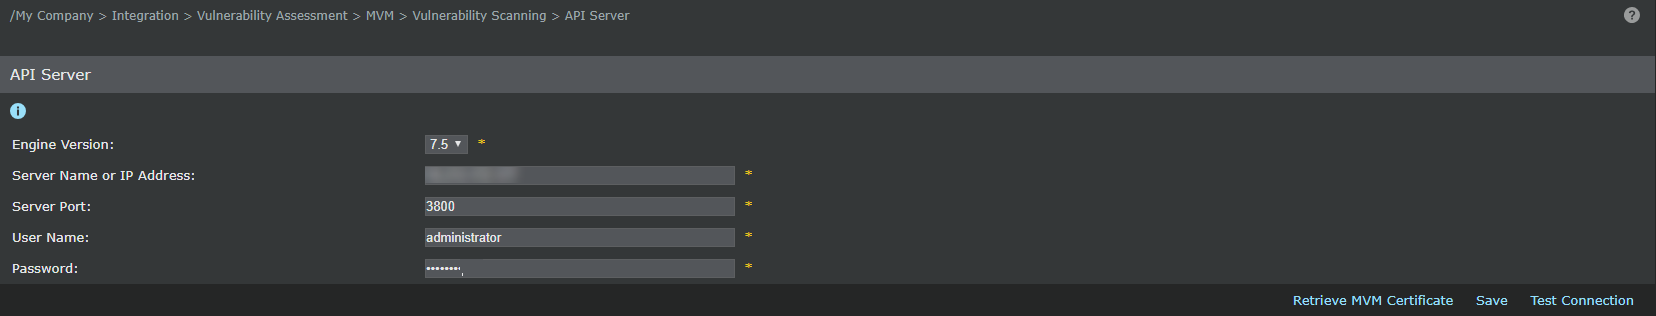
Select Manager → <Admin Domain Name> → Integration → Vulnerability Assessment → MVM → Vulnerability Scanning → API Server.
The Vulnerability Manager Server Settings page appears.
Select Engine Version as 6.8, 7.0, or 7.5.
Enter the Server Name or IP Address.
Enter the Server Port, User Name and Password for the Vulnerability Manager server.
Vulnerability Manager Server Settings area
Note
Username and password entered here should have full access rights in the Vulnerability Manager server. This is essential for successfully initiating Vulnerability Manager on-demand scans from Threat Explorer.
Click Save.
Start the FCM Agent service. Click Retrieve MVM Certificate to retrieve the MVM certificate.
Note
7.0 and 7.5 scan engines support only custom certificates.
Click Test Connection to check the availability of Vulnerability Manager server connection.